
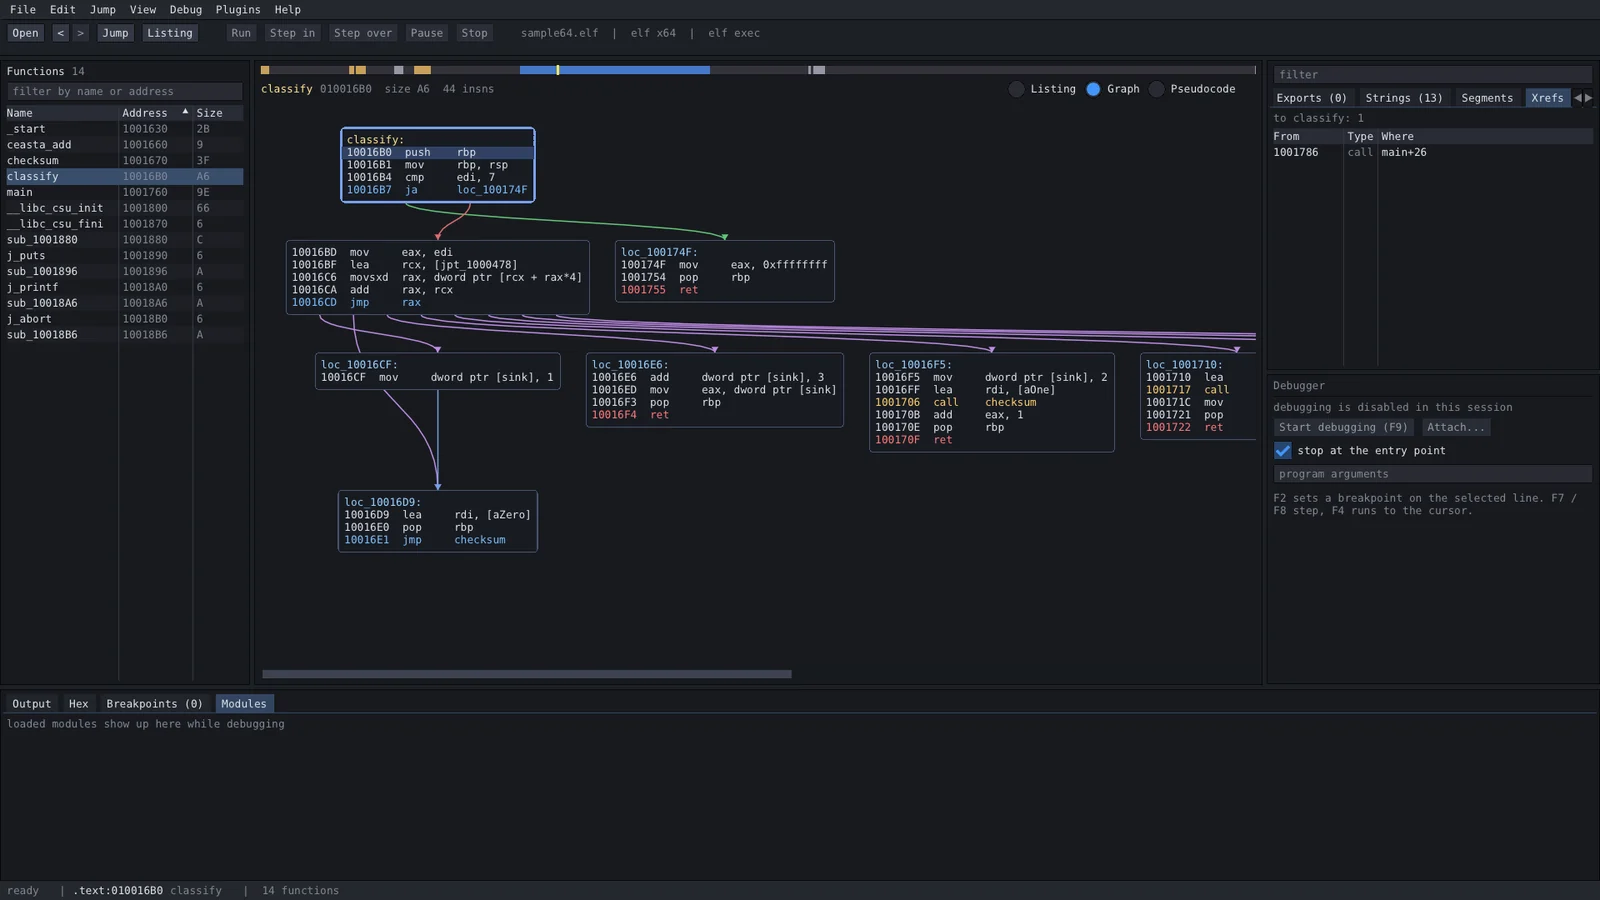
ceasta
 ngwg/ceasta
reverse engineering tool with a built-in MCP server: an AI can debug your binary, not just read it — breakpoints, stepping, memory, calling…
ai-assisted-reversingbinary-analysisbinary-exploitation+6
25
ngwg/ceastareverse engineering tool with a built-in MCP server: an AI can debug your binary, not just read it — breakpoints, stepping, memory, calling…
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 xteardx/diaphora-mcp
MCP server for automated binary diffing.
 dryxio/auto-re-agent
Reconstruct and validate C/C++ code from compiled programs with AI.
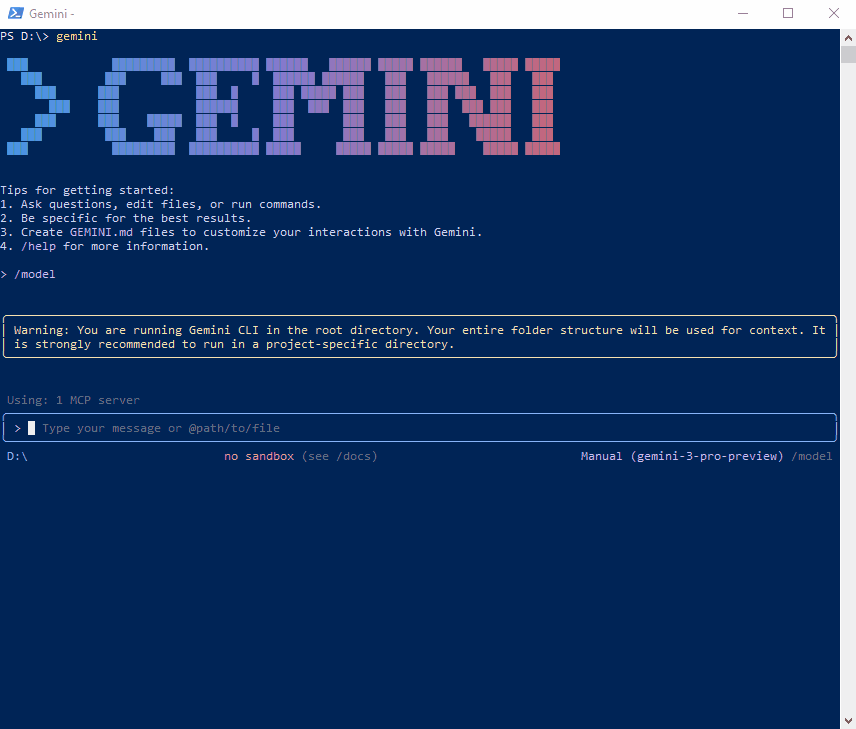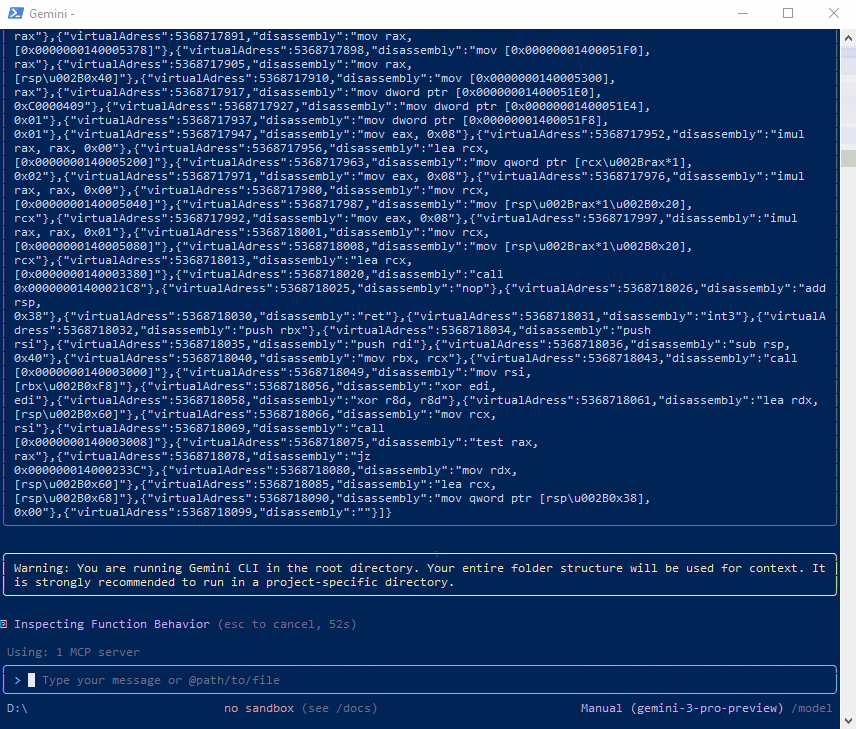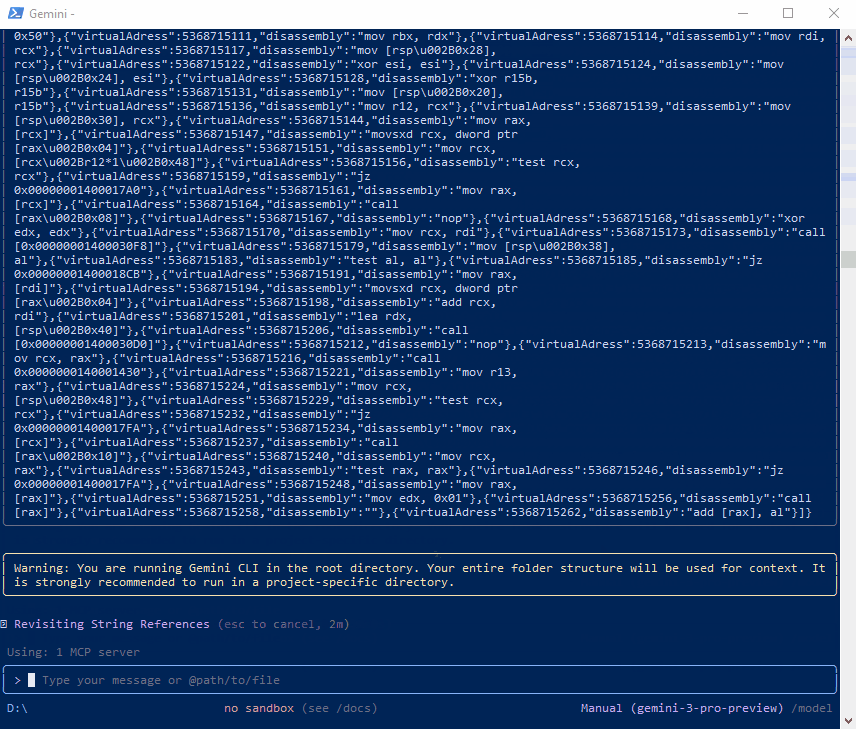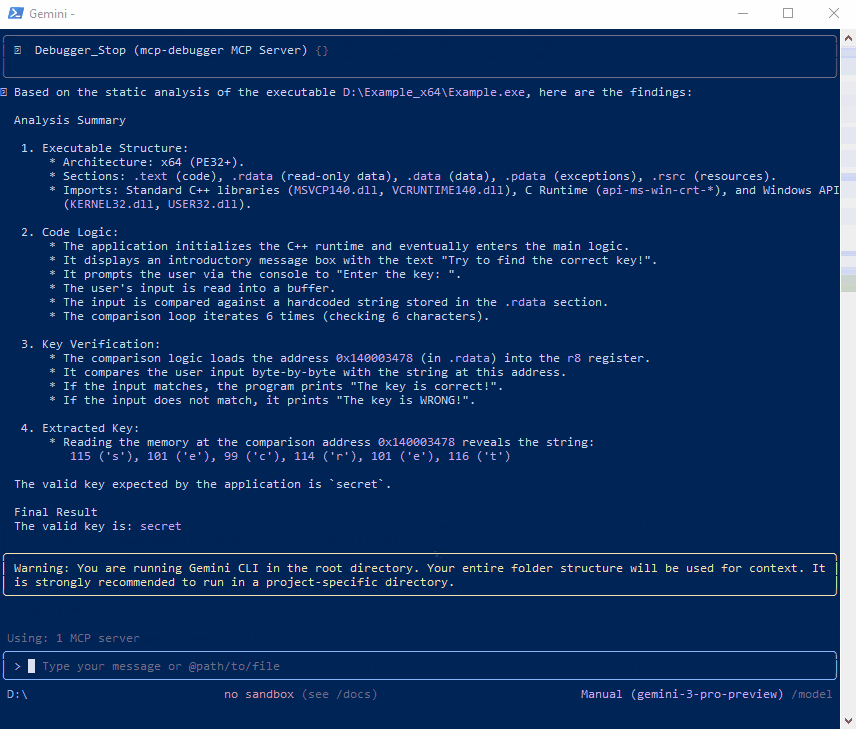 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
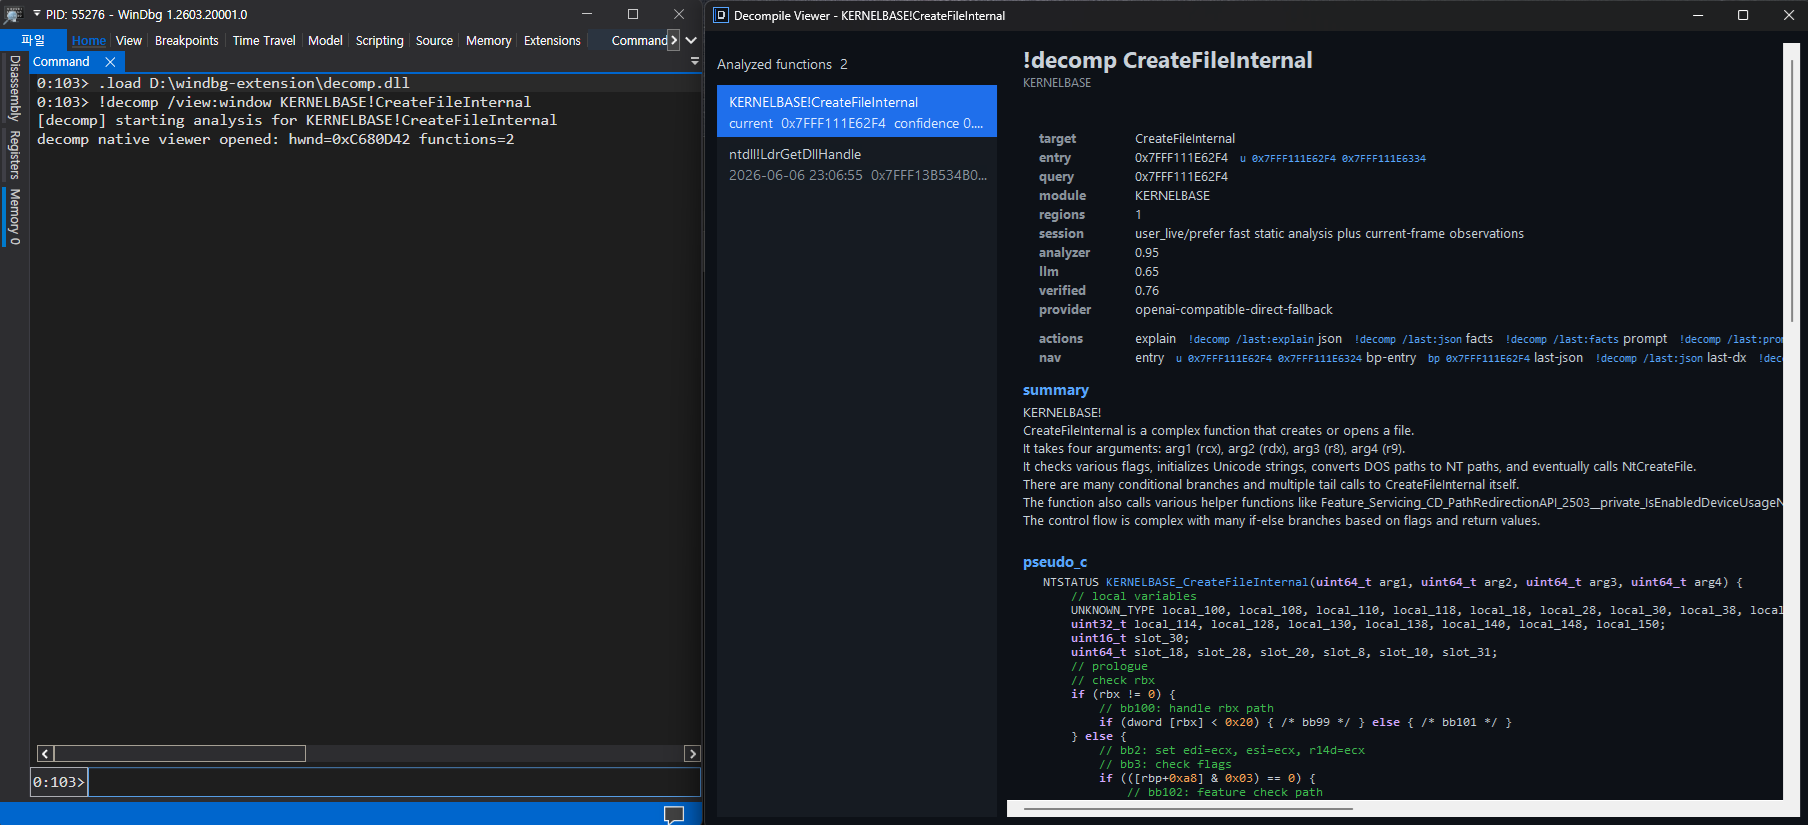 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
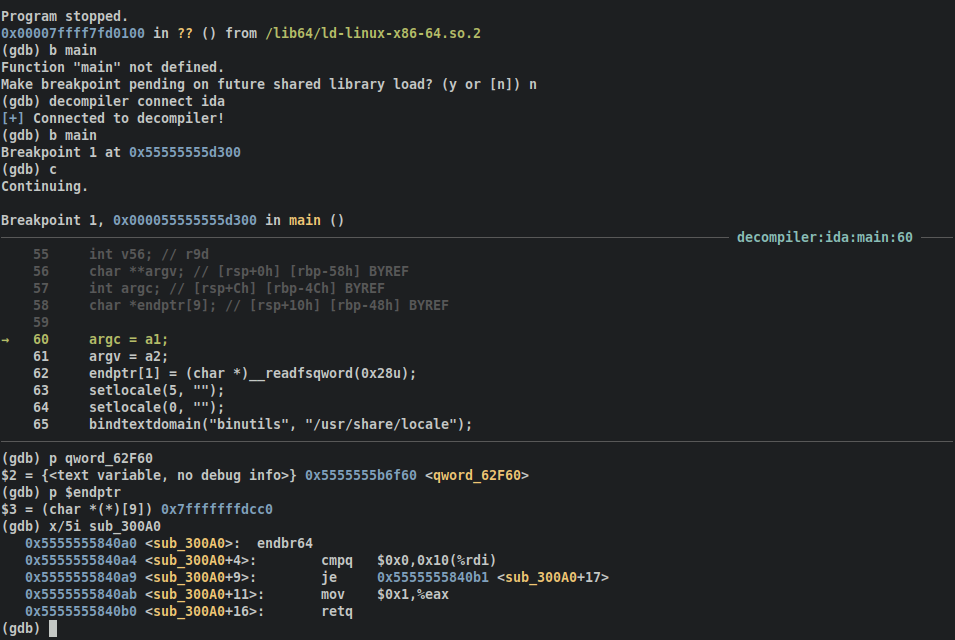 mahaloz/decomp2dbg
A plugin to introduce interactive symbols into your debugger from your decompiler
 kkaanozturk/hyperos-directory-traversal-analysis
Xiaomi HyperOS AVCodec Medya Framework'ündeki Use-After-Free (CVE-2025-21082) Zafiyetinin Derinlemesine Analizi, Rust Simülasyonu ve İnteraktif Web…
 satheesh575555/external_v8_aosp10_r33_cve-2021-0396
Repository containing V8 JavaScript engine source code with a specific commit for CVE-2021-0396, likely for vulnerability research and exploitation.
 nac-l/mergen
Deobfuscation via optimization with usage of LLVM IR and parsing assembly.
 kevinbackhouse/djvulibre-poc-cve-2025-53367
Proof-of-concept exploit for CVE-2025-53367, a vulnerability in the DjVuLibre library. Demonstrates exploitation of a memory corruption bug in DjVu…
 angr/angr
A powerful and user-friendly binary analysis platform!
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy