BinAbsInspector
 keensecuritylab/binabsinspector
Static binary vulnerability scanner using abstract interpretation on Ghidra Pcode. Detects CWE classes like buffer overflows, use-after-free, and…
binary-analysisfuzzingreverse-engineering+2
1.7k
keensecuritylab/binabsinspectorStatic binary vulnerability scanner using abstract interpretation on Ghidra Pcode. Detects CWE classes like buffer overflows, use-after-free, and…
 pq-code-package/mlkem-native
Secure, fast, and portable C90 implementation of ML-KEM / FIPS 203
 mucoze/umay
IoT Malware Similarity Analysis Platform
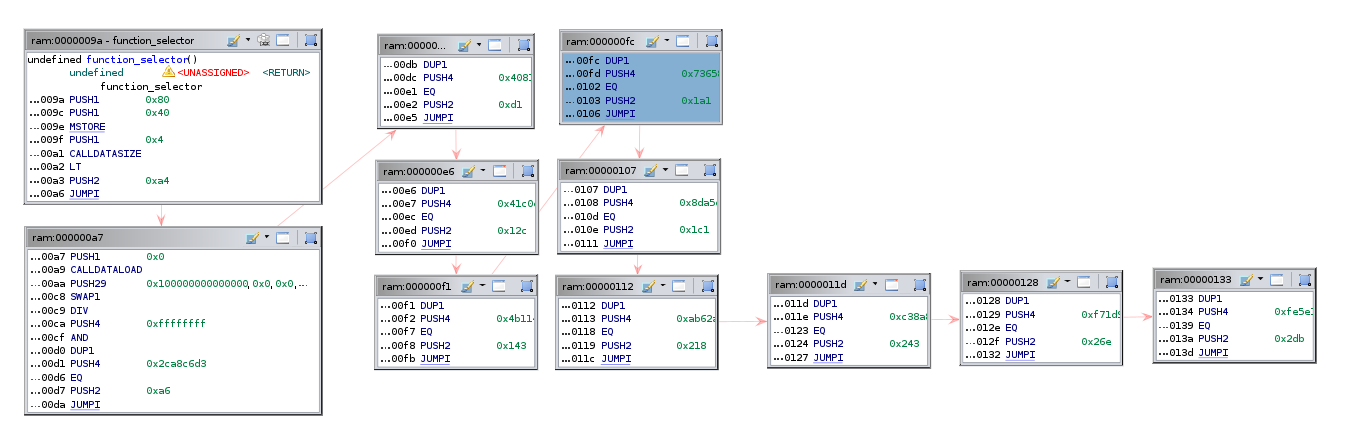 adelapie/ghidra-evm
Ghidra module for disassembling, decompiling, and analyzing Ethereum smart contract bytecode. Detects insecure instructions, extracts hidden methods,…
 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
 xoreaxeaxeax/hexcymatix
Visualizes repeated byte sequences in binary files to reveal hidden structure, supporting reverse engineering and pattern discovery without…
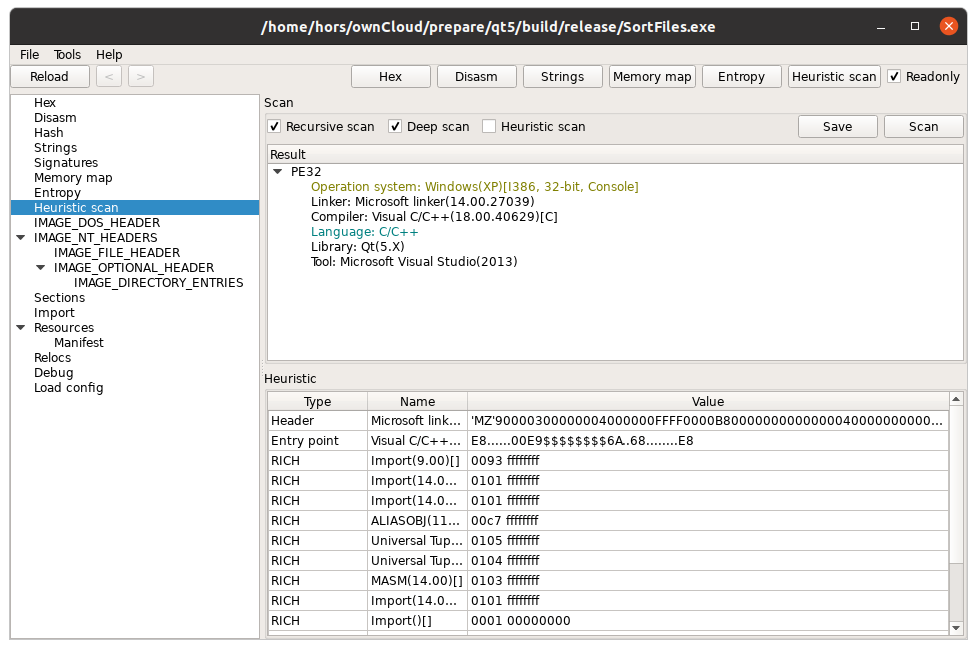 horsicq/xpeviewer
PE file viewer/editor for Windows, Linux and MacOS.
 wolfssl/wolfcose
A fast, portable, and lightweight COSE + CBOR implementation for embedded systems. Supports PQC, FIPS 140-3, DO-178, and MISRA C. Powered by wolfSSL.
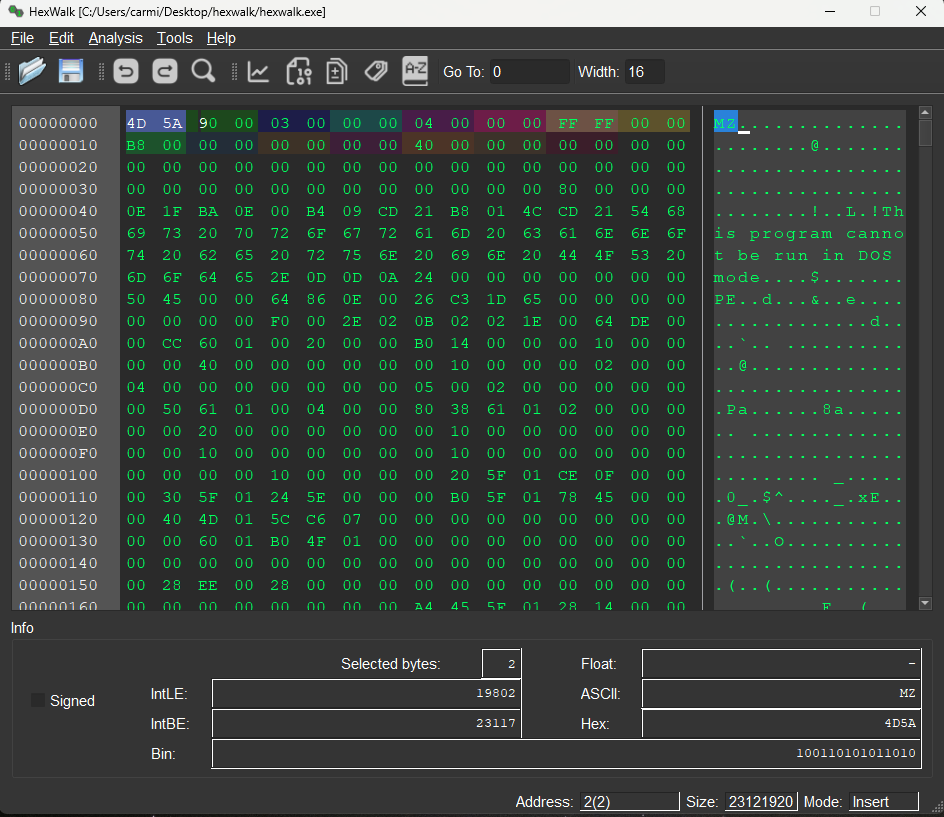 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
 checkpointsw/karta
IDA Python plugin for fast, location-driven matching of open-source library symbols in binaries, enabling efficient reverse engineering and…
 beardypig/ghidra-emotionengine
Ghidra Processor for the Play Station 2's Emotion Engine MIPS based CPU
 rehints/efixplorer
IDA plugin and loader for UEFI firmware analysis and reverse engineering automation
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
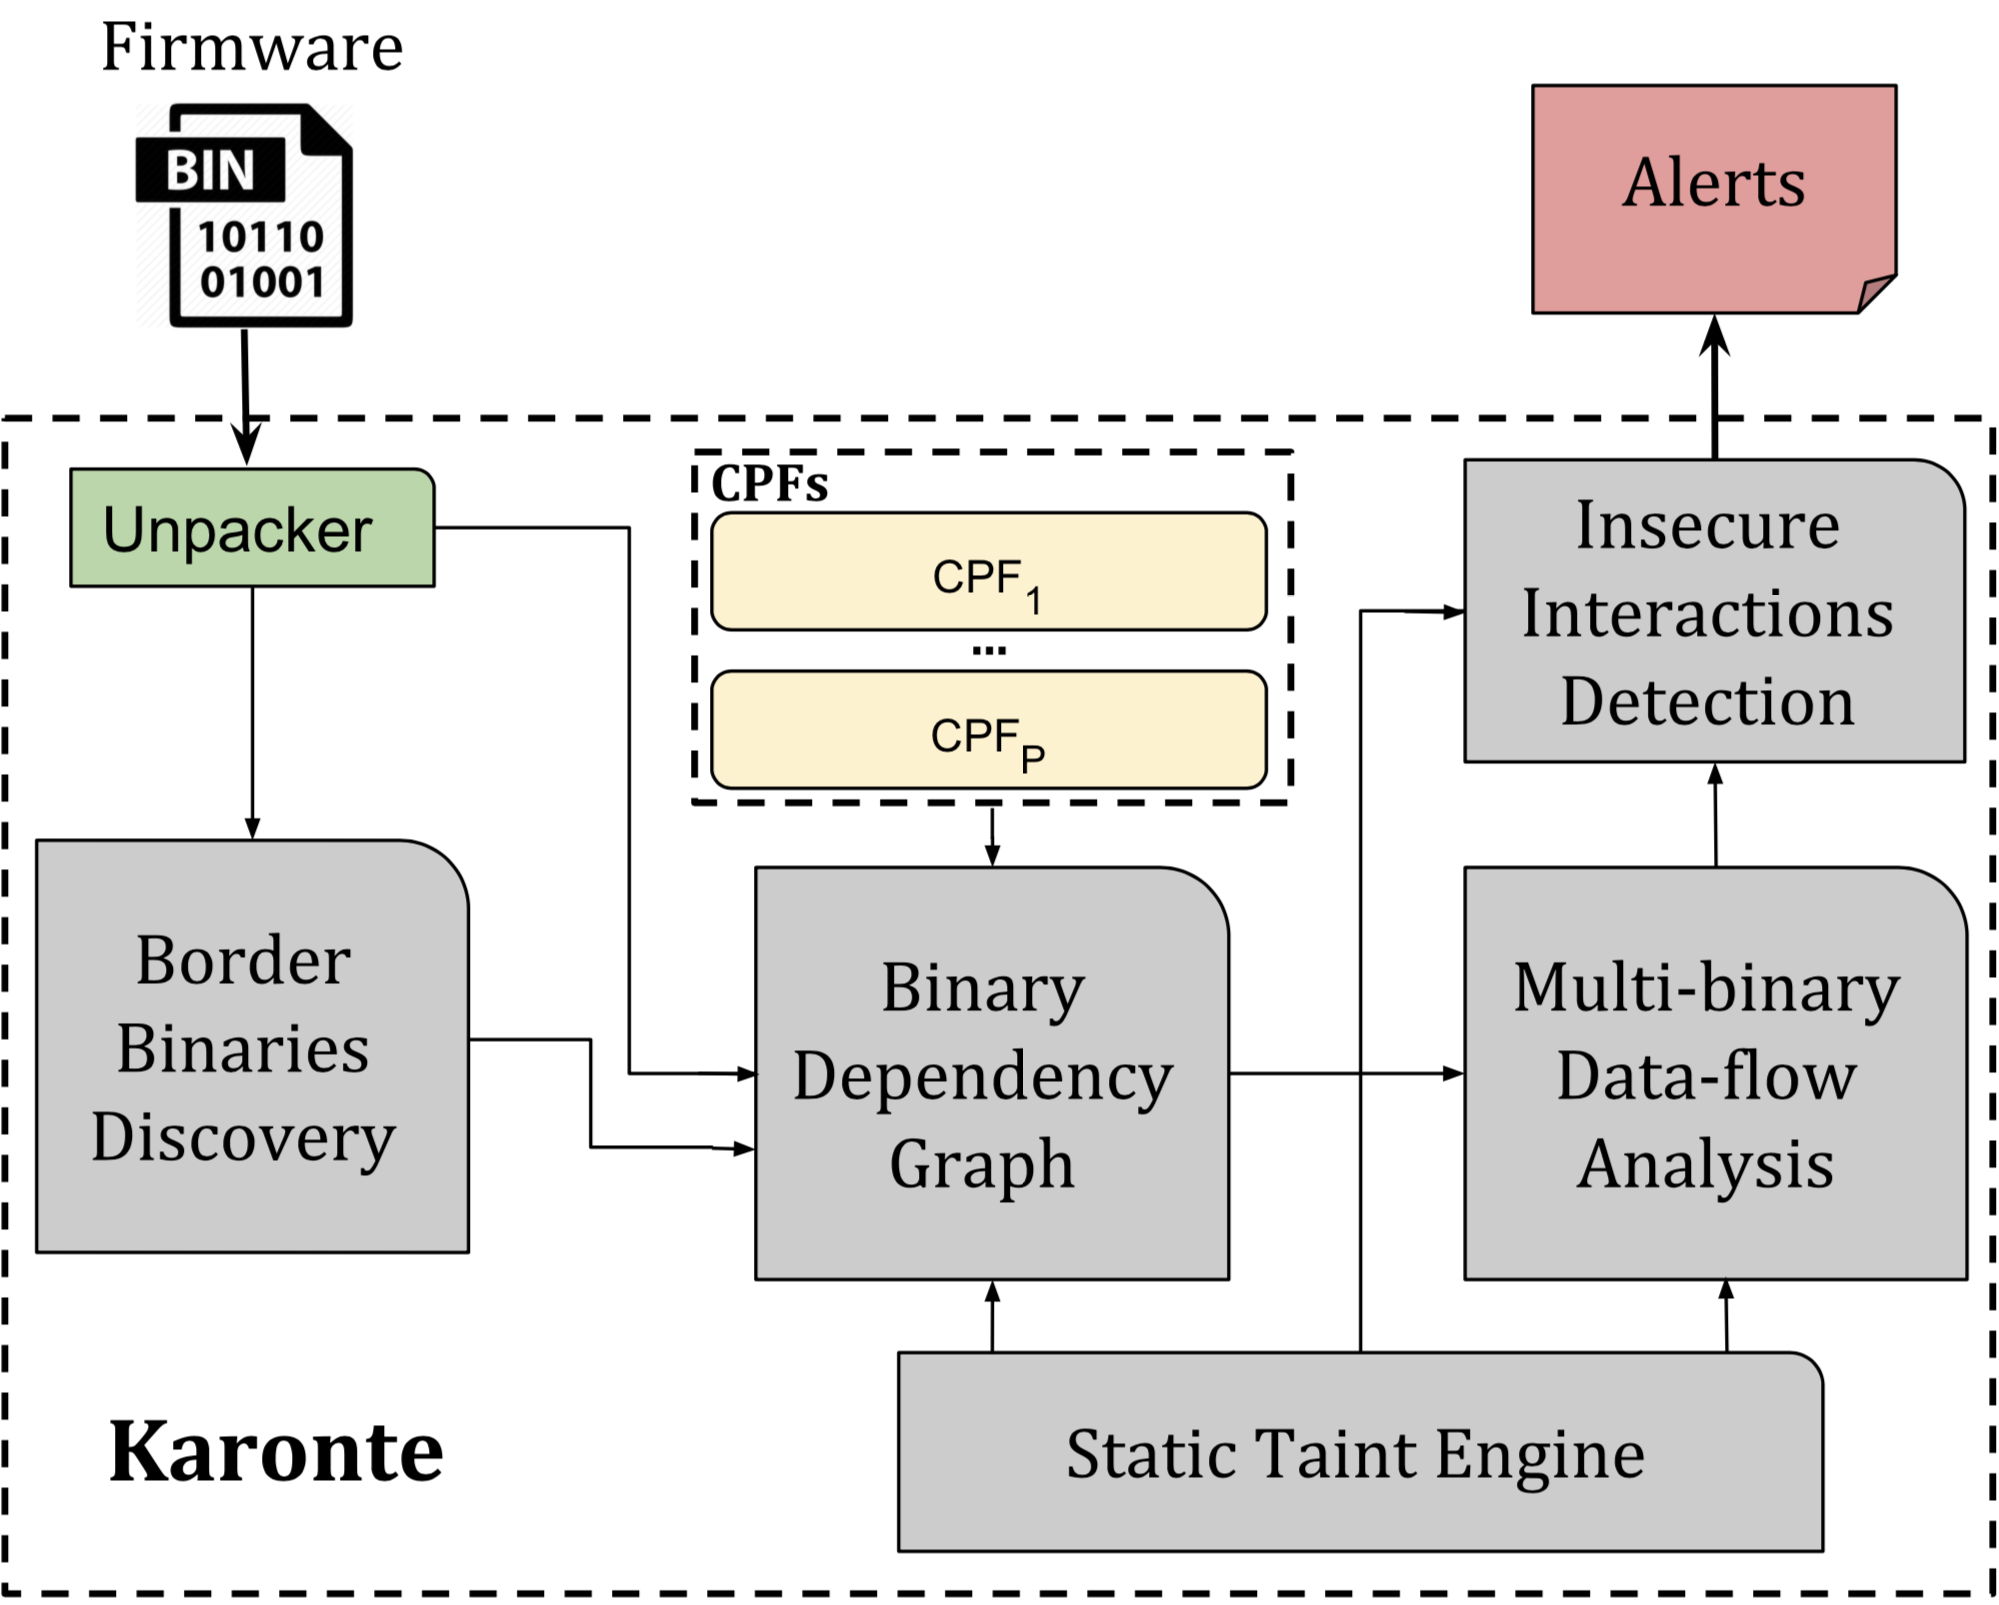 ucsb-seclab/karonte
Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware
 ex0dus-0x/fuzzable
Static analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…