

checkov
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
cloud-infrastructure-securitycloud-securitycode-analysis+12
9.0k
bridgecrewio/checkovStatic analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 pq-code-package/mlkem-native
Secure, fast, and portable C90 implementation of ML-KEM / FIPS 203
 open-policy-agent/conftest
Write tests against structured configuration data using the Open Policy Agent Rego query language
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 wadingporque/apkprobe
APK decompiler & secrets scanner for Android security research! Extract leaked API keys, hardcoded credentials, endpoints from APK files. apk2url,…
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
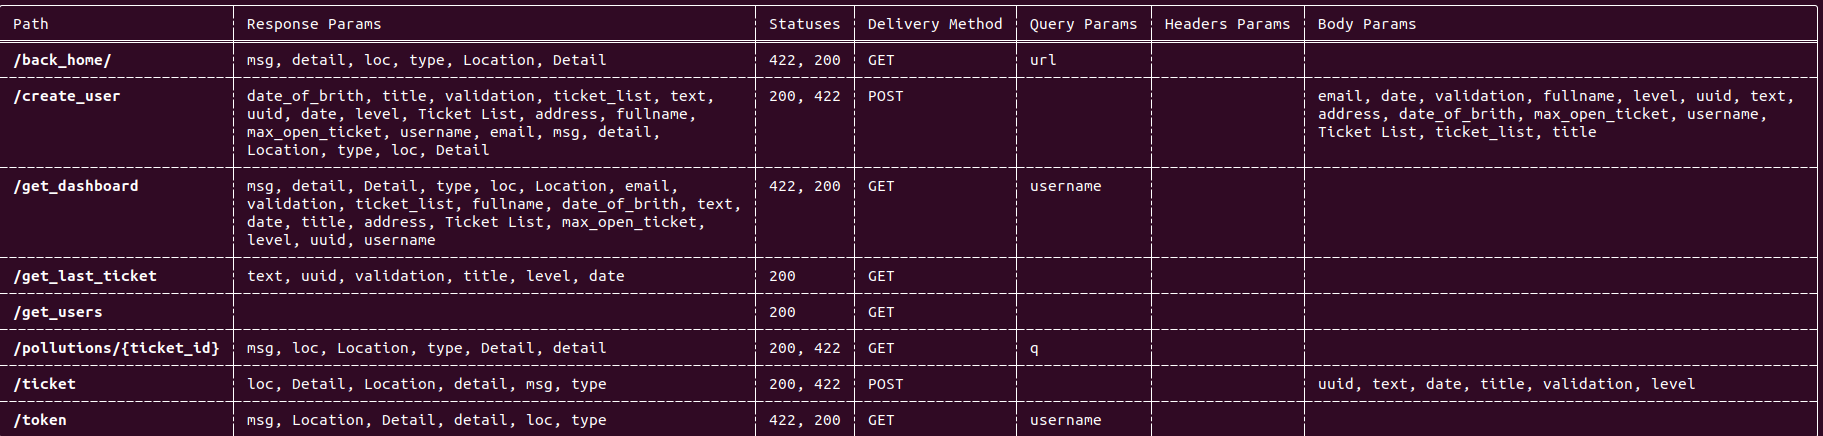 blst-security/cherrybomb
CLI tool that audits OpenAPI specifications, validates them against best practices, and runs automated security tests to detect vulnerabilities and…
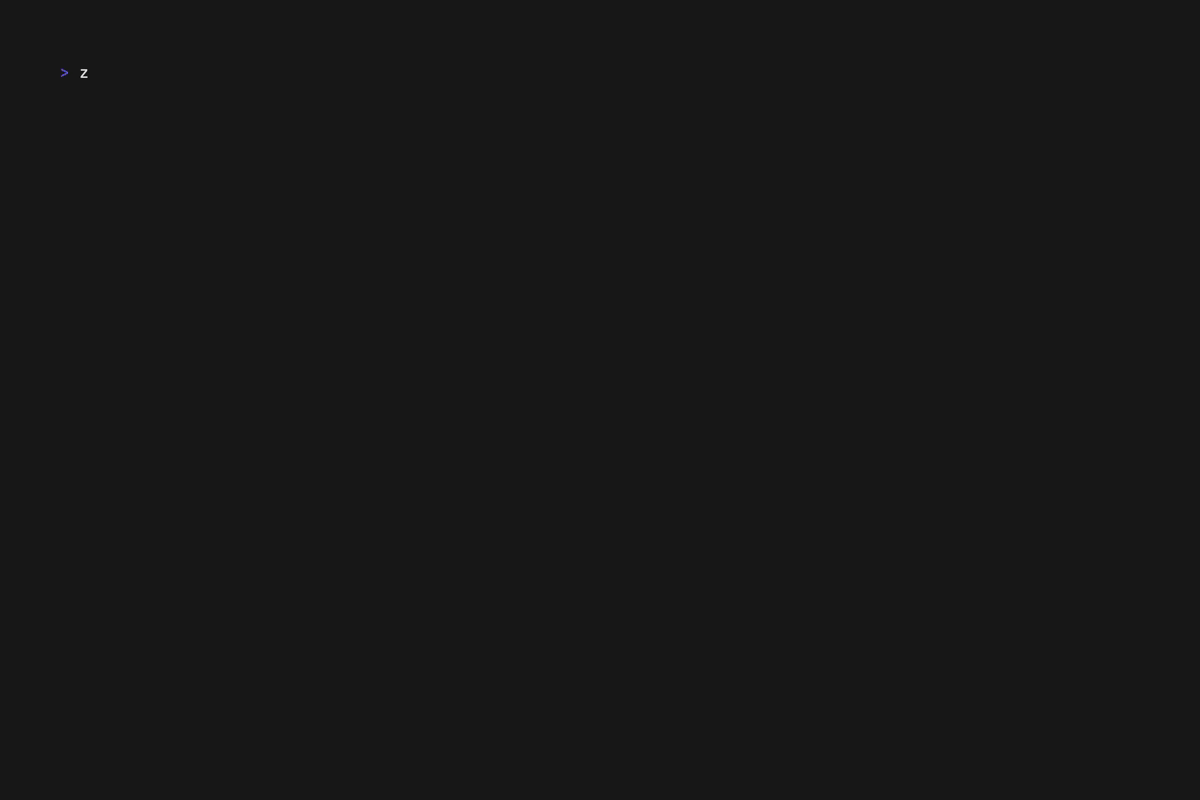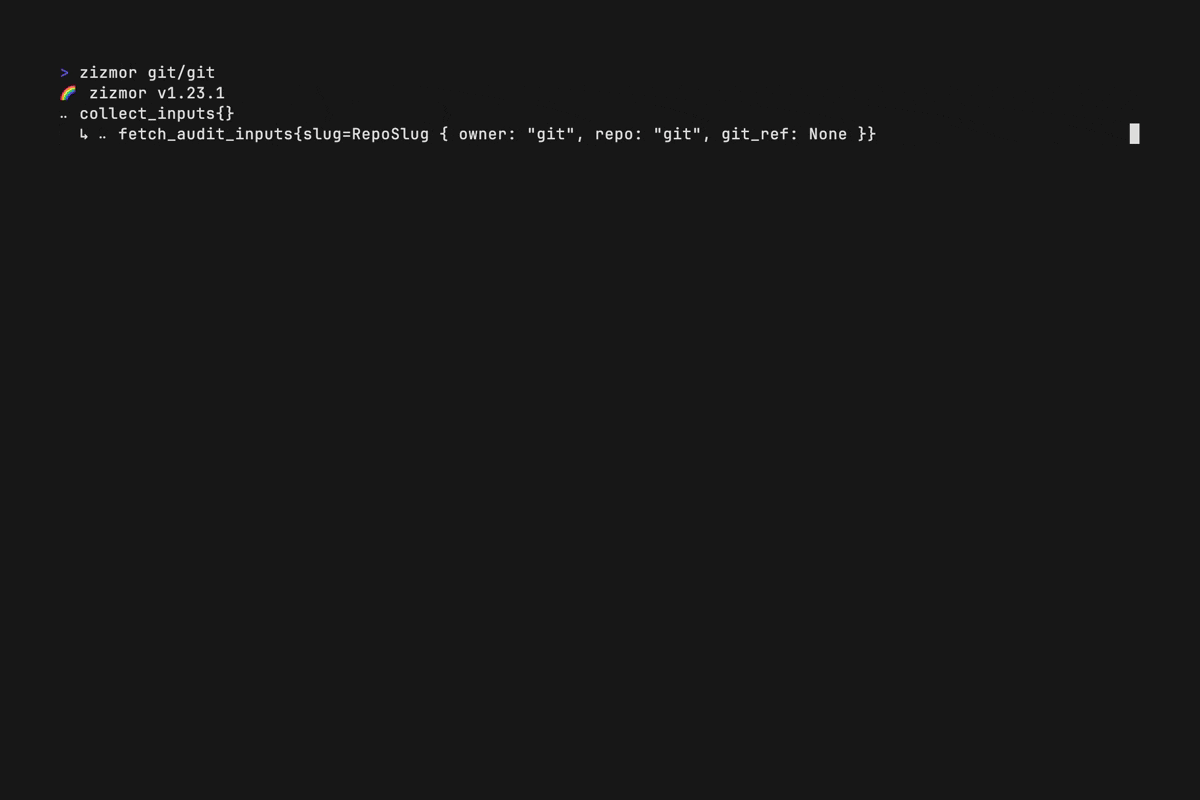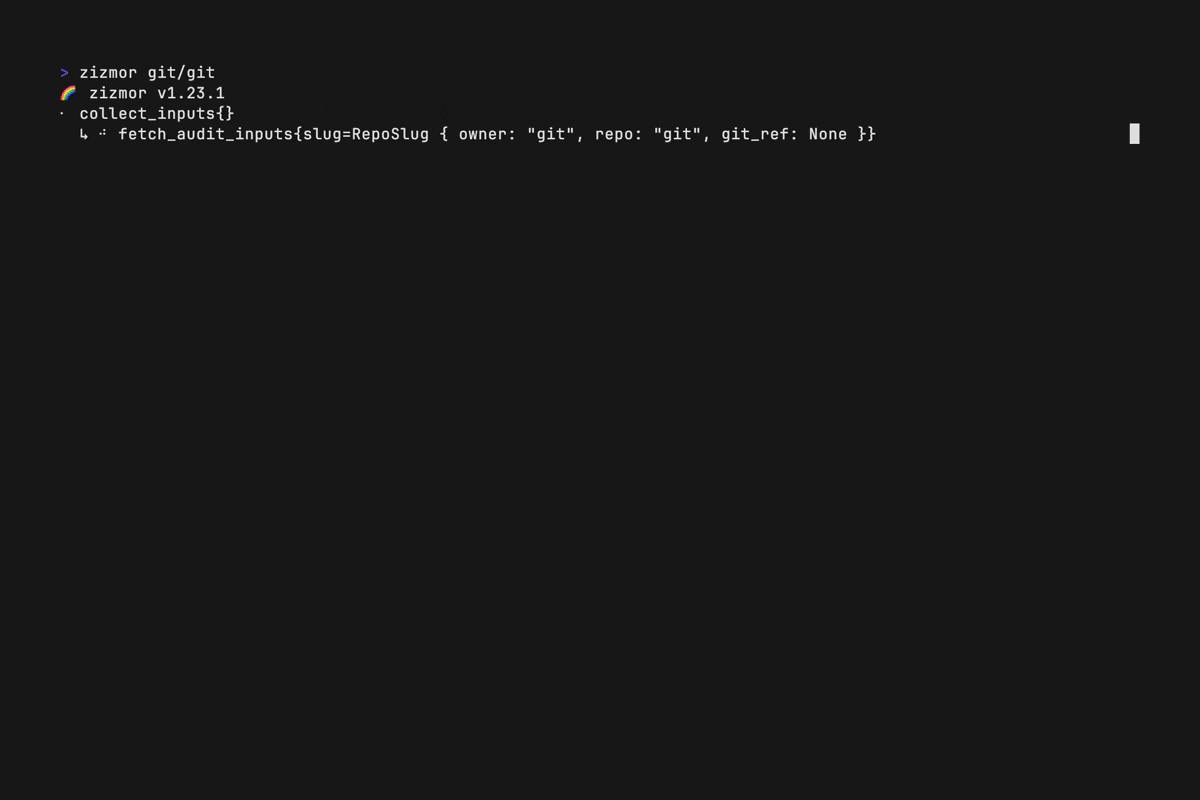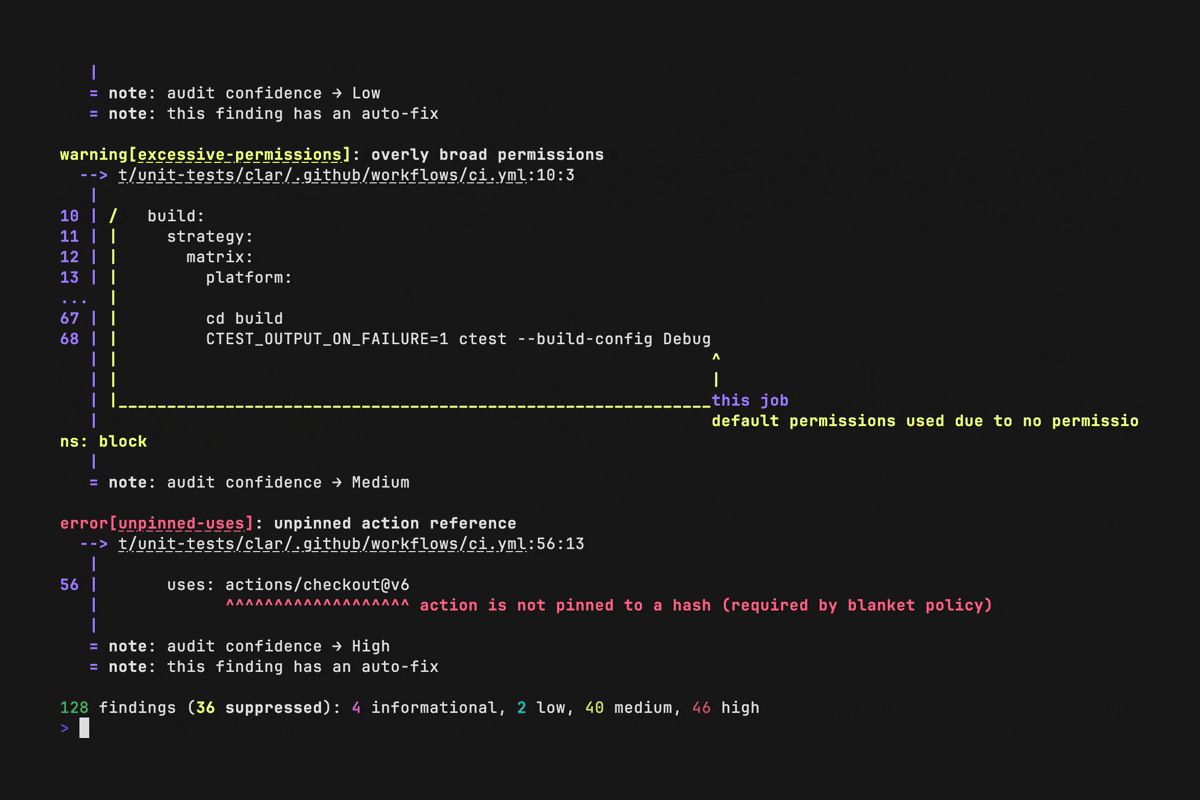 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 globocom/huskyci
Performing security tests inside your CI
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
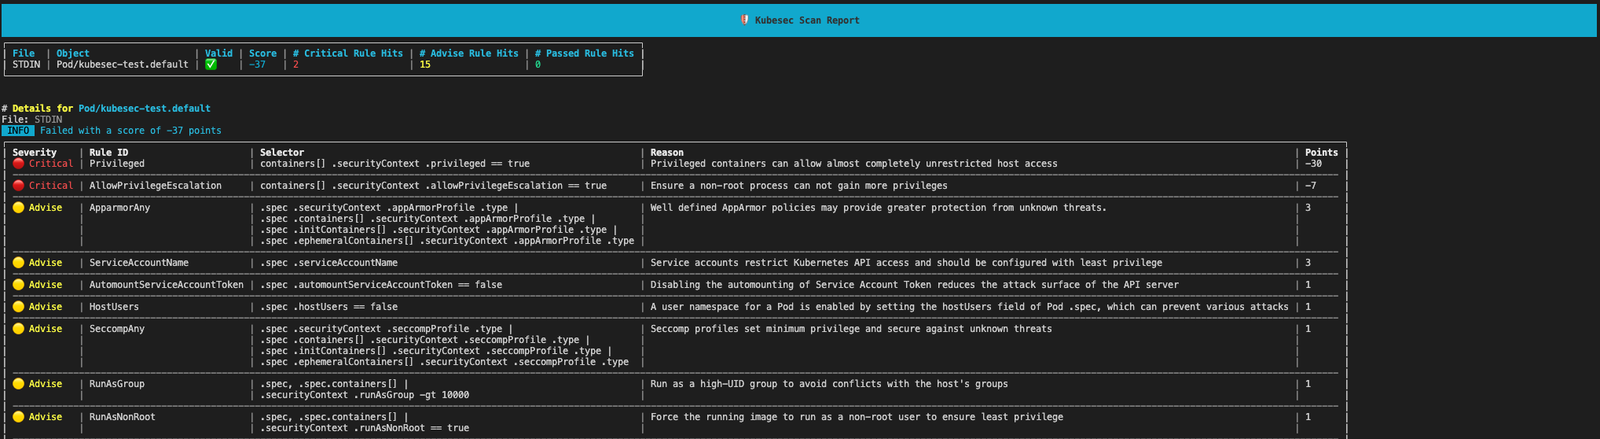 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 megamansec/gixy-next
Gixy-Next: NGINX Configuration Security Scanner & Performance Checker
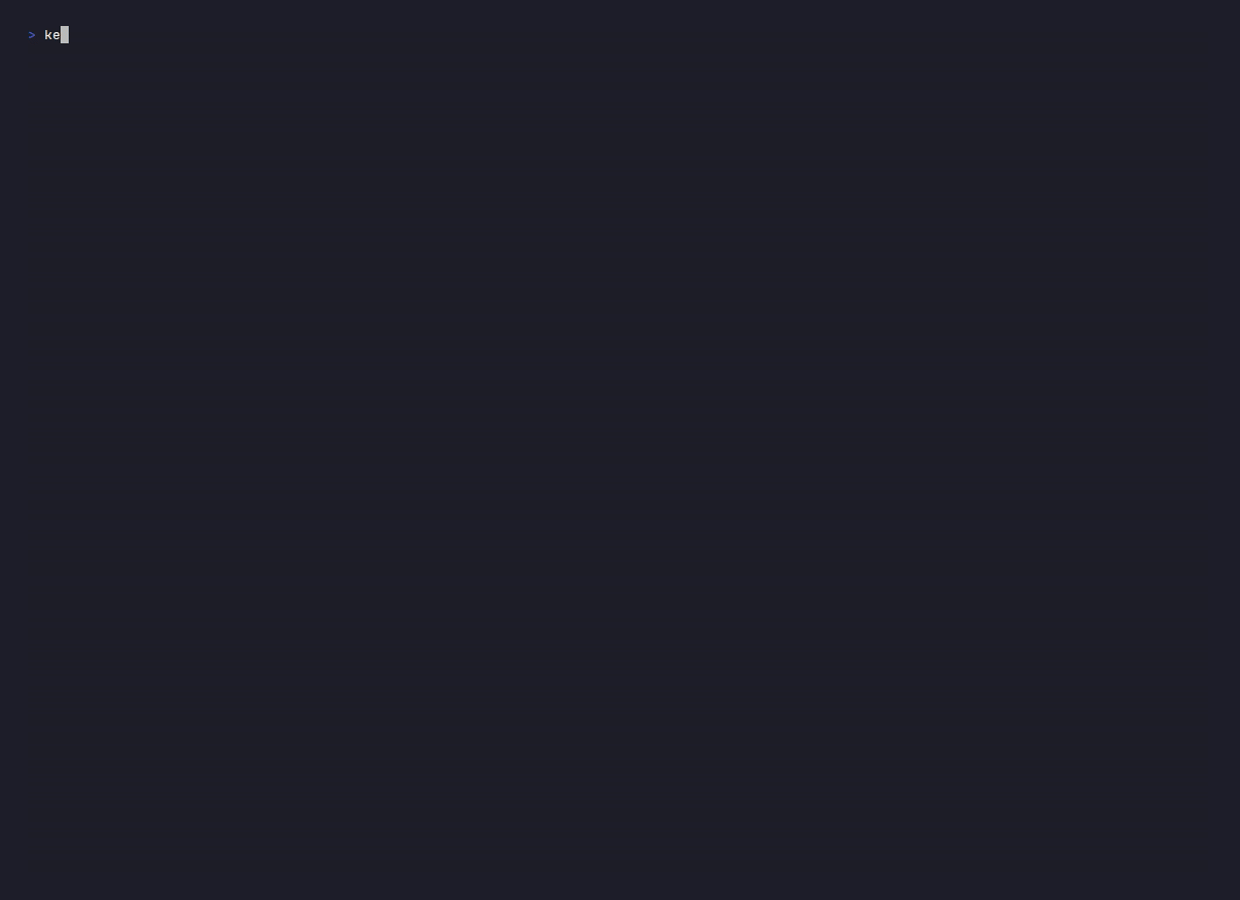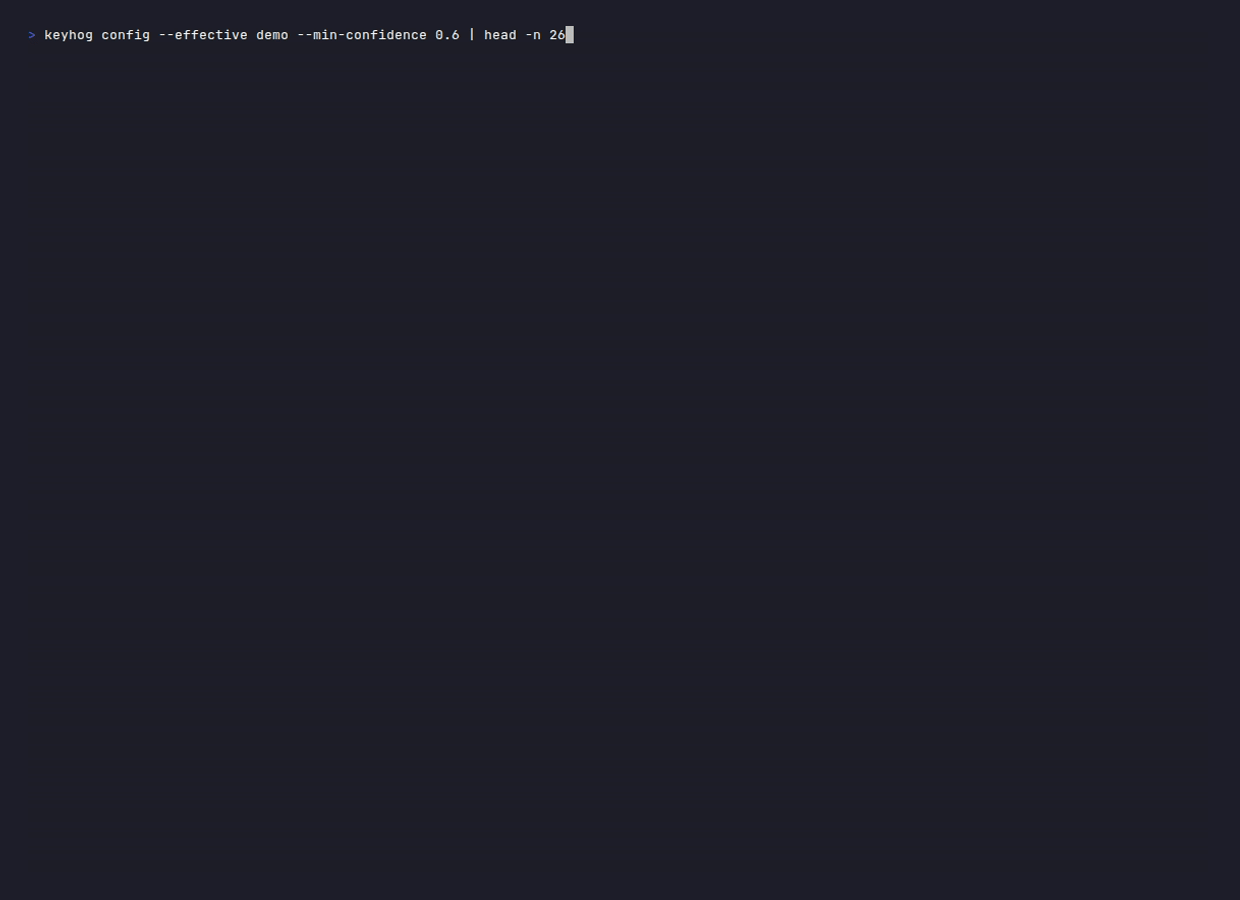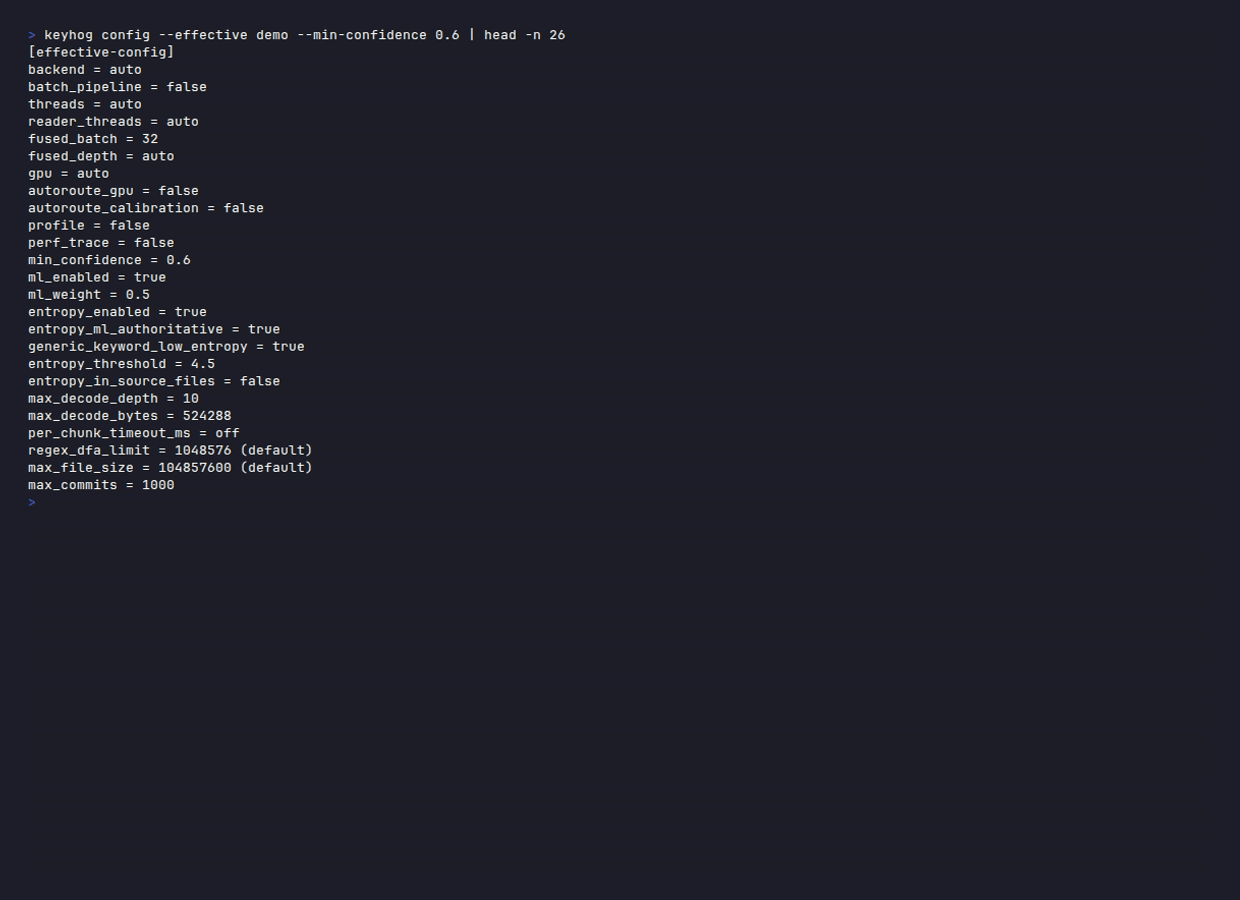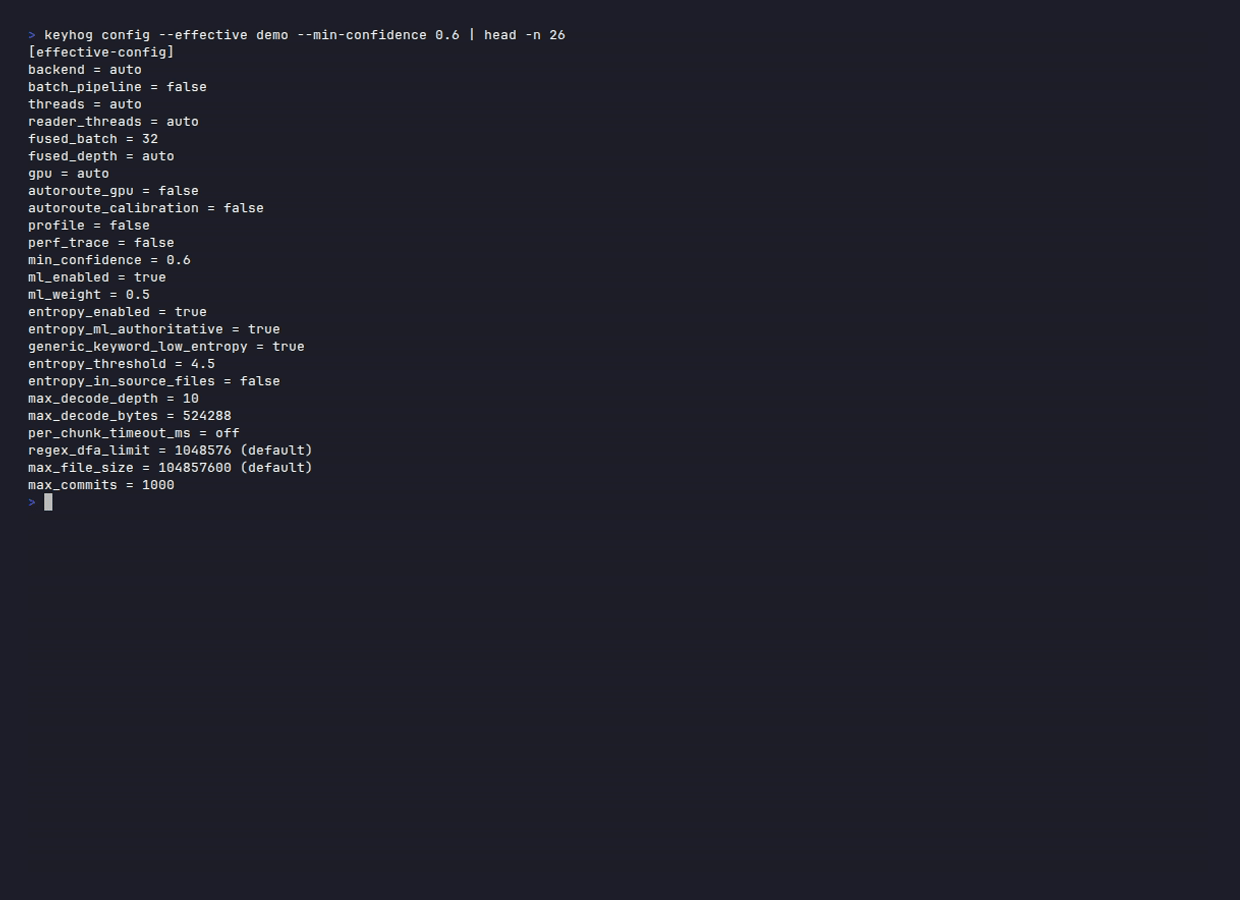 santhreal/keyhog
Open-source secret scanner in Rust
 cisco-ai-defense/defenseclaw
Security Governance for Agentic AI
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.