
PoC-CVE-2026-20841
 elenichristopoulou/poc-cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…
exploitationphishingsocial-engineering+1
elenichristopoulou/poc-cve-2026-20841Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…
 abdurahmon3236/cve-2024-6529
Proof-of-concept scripts demonstrating reflected XSS in the Ultimate Classified Listings WordPress plugin and admin cookie theft via crafted payloads…
 leocottret/cve-2024-30956
(DOM-based XSS) HTML Injection vulnerability in TOWeb v.12.05 and before allows an attacker to inject HTML/JS code via the _message.html component.
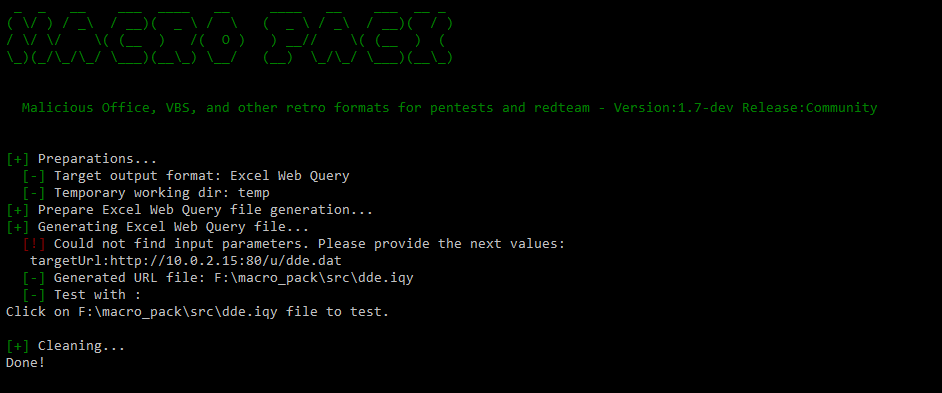 sevagas/macro_pack
macro_pack is a tool by @EmericNasi used to automatize obfuscation and generation of Office documents, VB scripts, shortcuts, and other formats for…
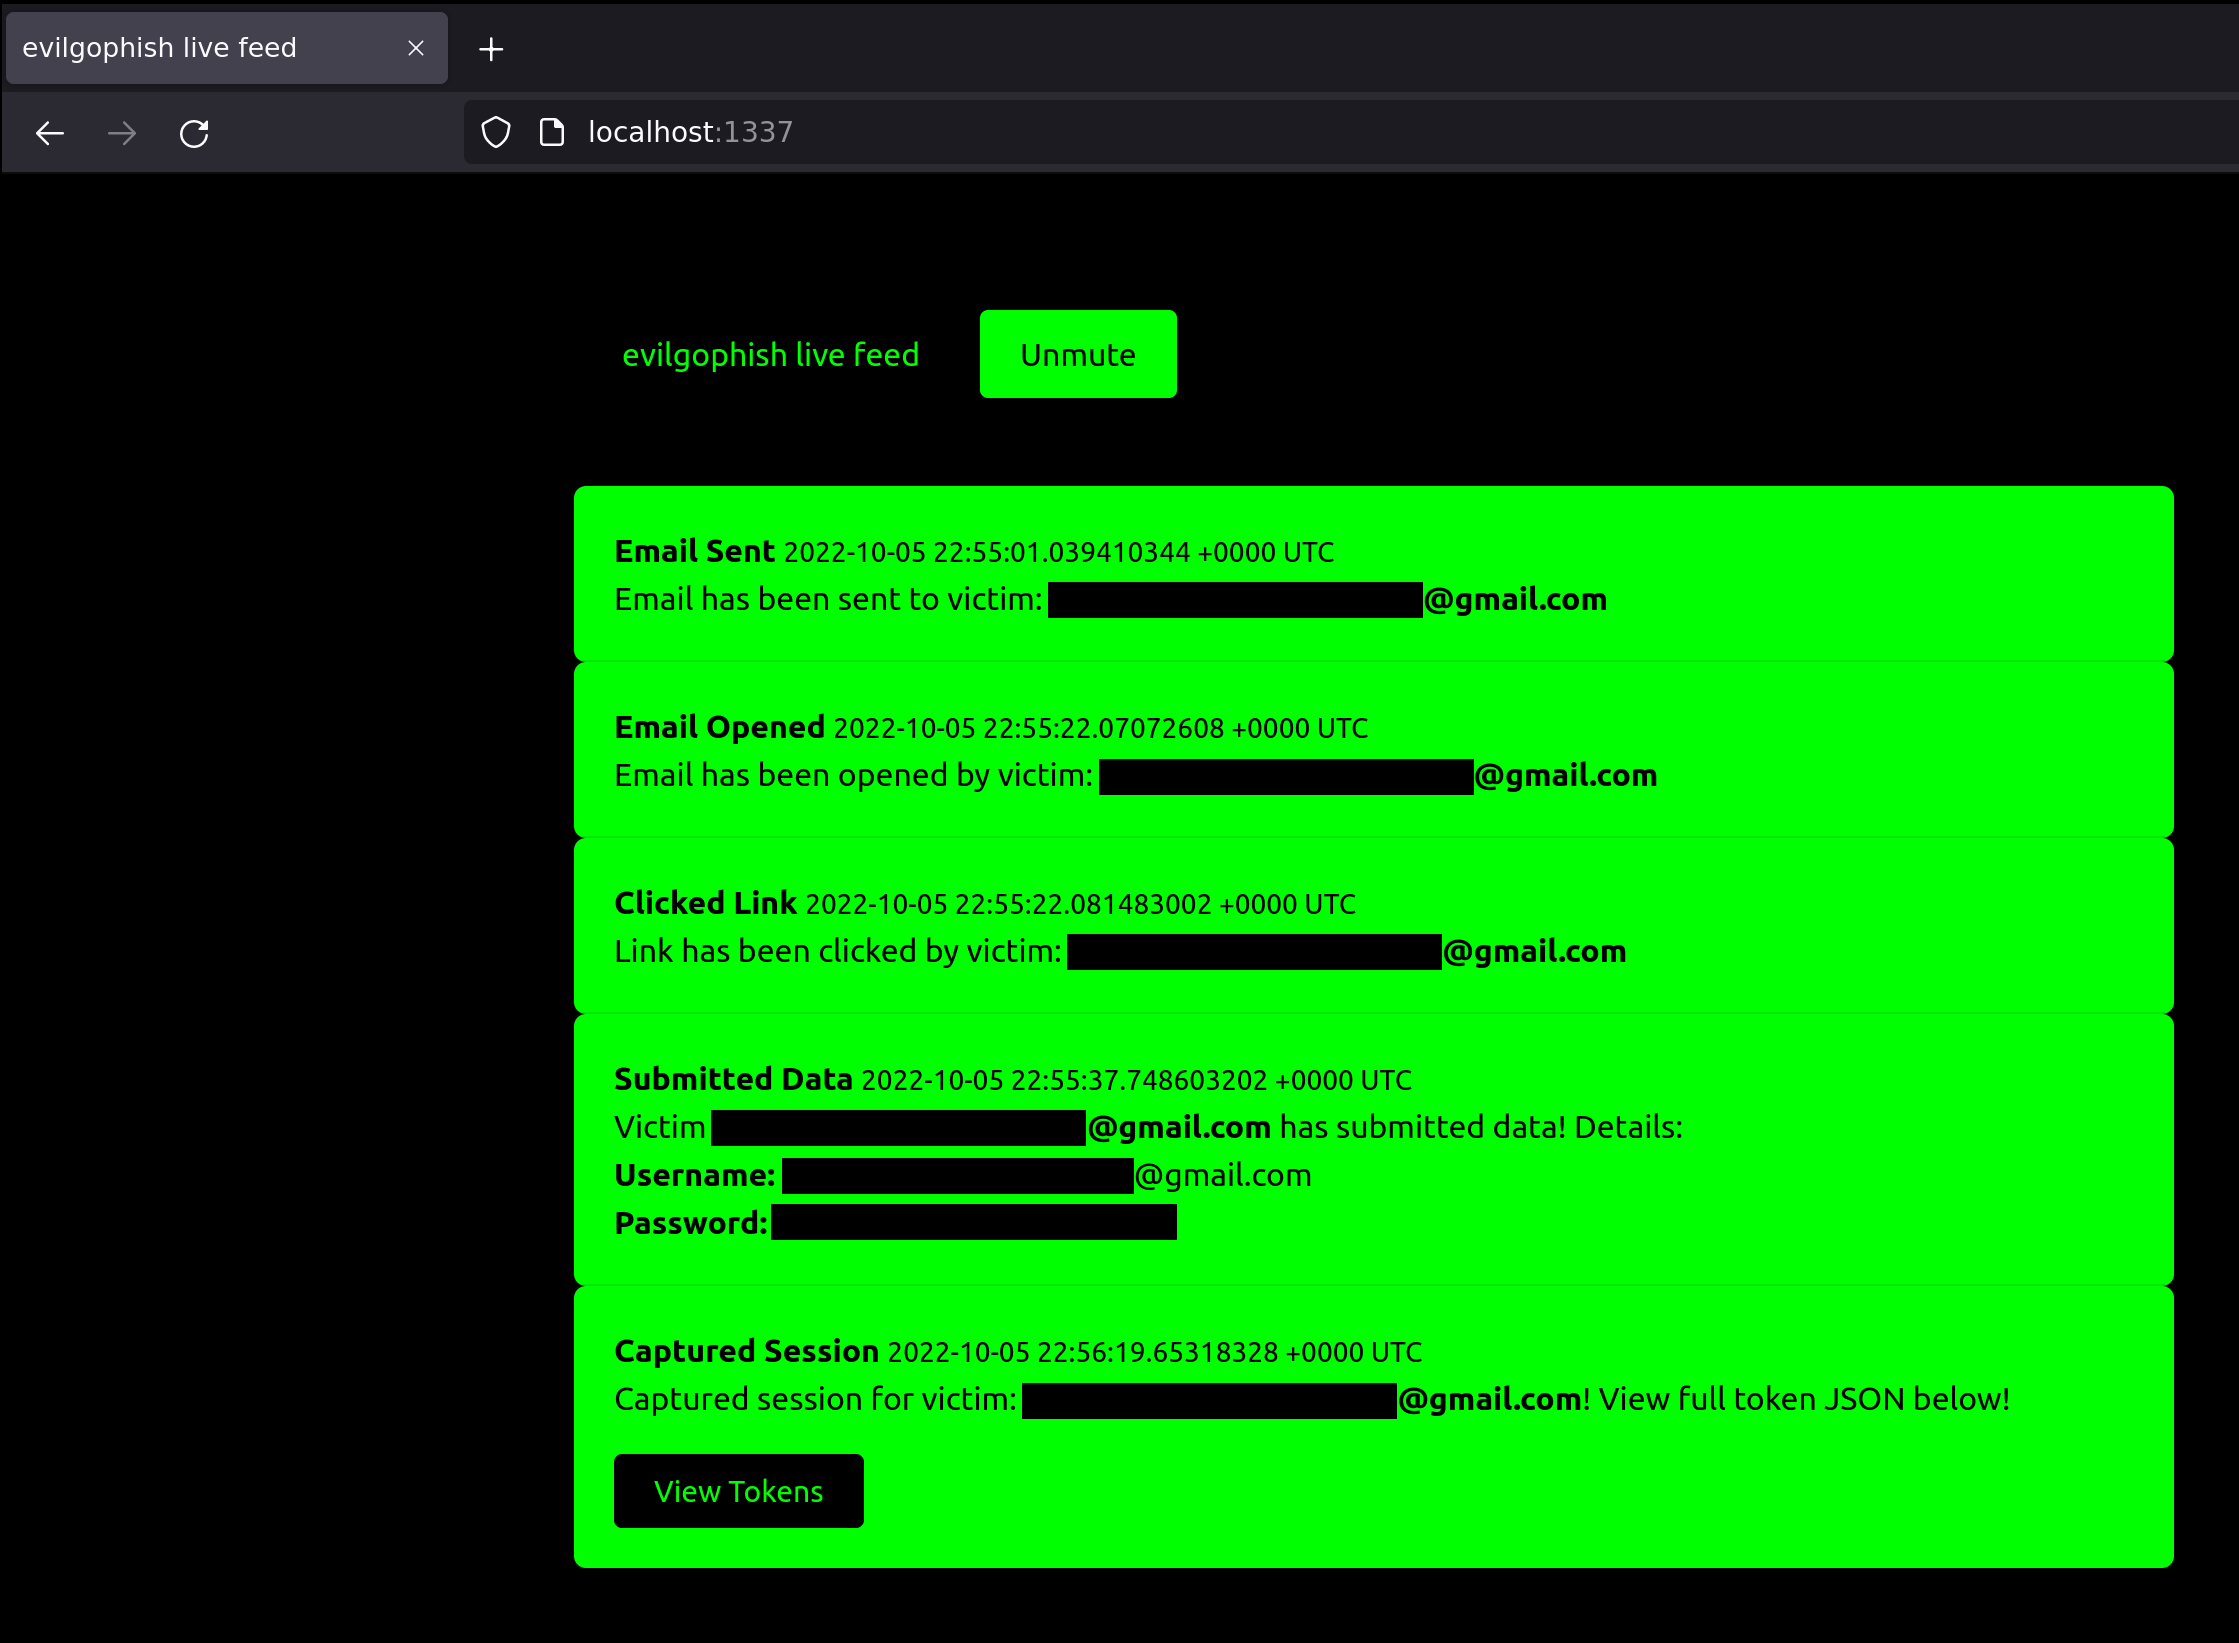 fin3ss3g0d/evilgophish
evilginx3 + gophish
 kgretzky/evilginx
PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2
 d4vinci/pastejacker
Hacking systems with the automation of PasteJacking attacks.
 absholi7ly/poc-for-cve-2024-7014-exploit
Proof of Concept (PoC) for CVE-2024-7014 (EvilVideo) Exploit
 furqankhan1/cve-2019-13498
CVE-2019-13498

 shndnth/cve-2022-30190
Educational Proof-of-Concept for the CVE-2022-30190 (Follina) vulnerability.
 asepsaepdin/cve-2010-1240
Educational proof-of-concept demonstrating how to embed a Meterpreter backdoor into a PDF file exploiting CVE-2010-1240, with step-by-step Metasploit…
 s1lkys/cve-2021-24884
If an authenticated user who is able to edit Wordpress PHP code in any kind, clicks a malicious link, PHP code can be edited through XSS in…
 openxp-research/cve-2022-47132
Academy LMS <= 5.10 CSRF
 kgretzky/evilginx2
Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…
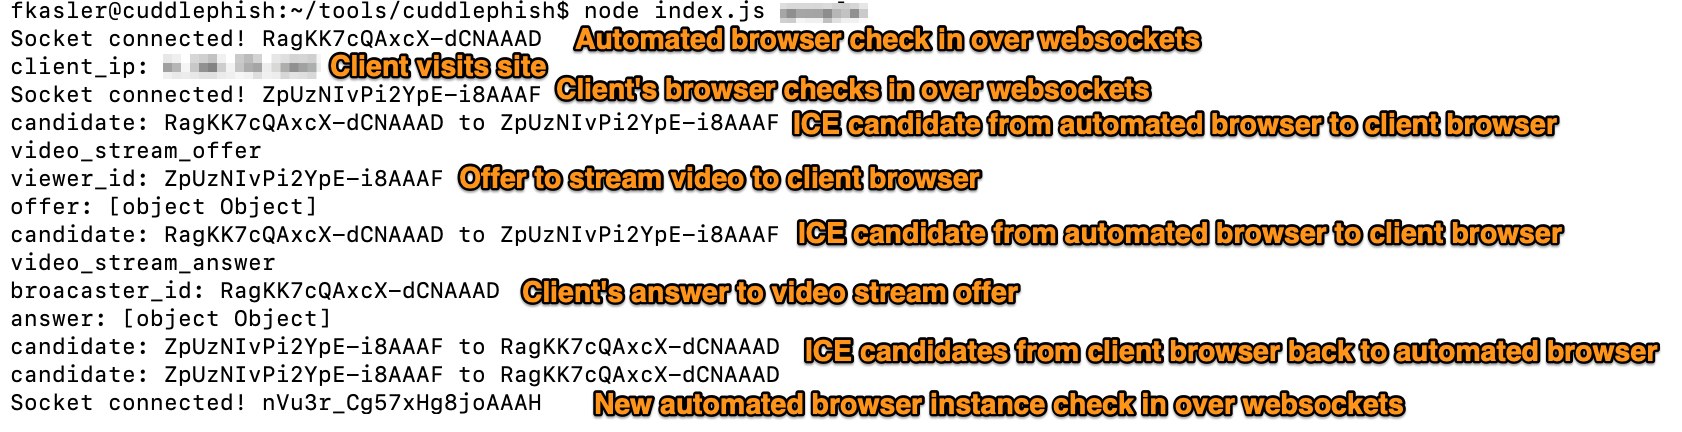 fkasler/cuddlephish
Weaponized Browser-in-the-Middle (BitM) for Penetration Testers
 praetorian-inc/chromealone
A tool to transform Chromium browsers into a C2 Implant
 kgretzky/evilqr
Proof-of-concept to demonstrate dynamic QR swap phishing attacks in practice.