

Empire
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k
bc-security/empireEmpire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 tokyoneon/chimera
Chimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.
 cryptolok/morphaes
IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 bishopfox/sliver
Adversary Emulation Framework
 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 lepotekil/msfmania
Python AV Evasion Tools
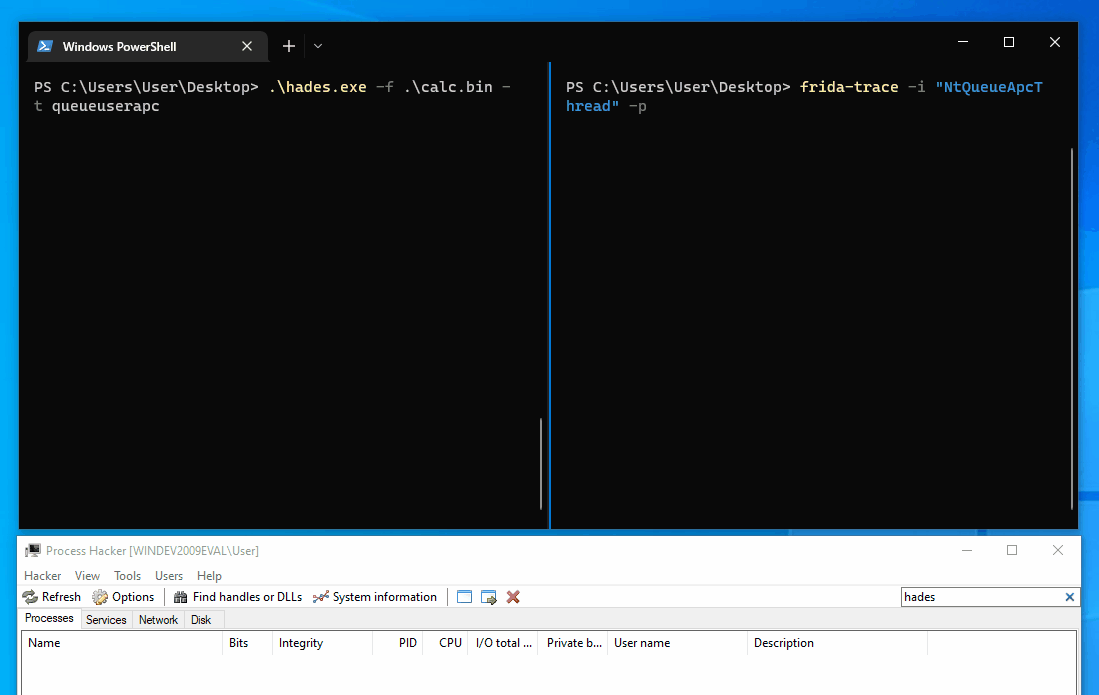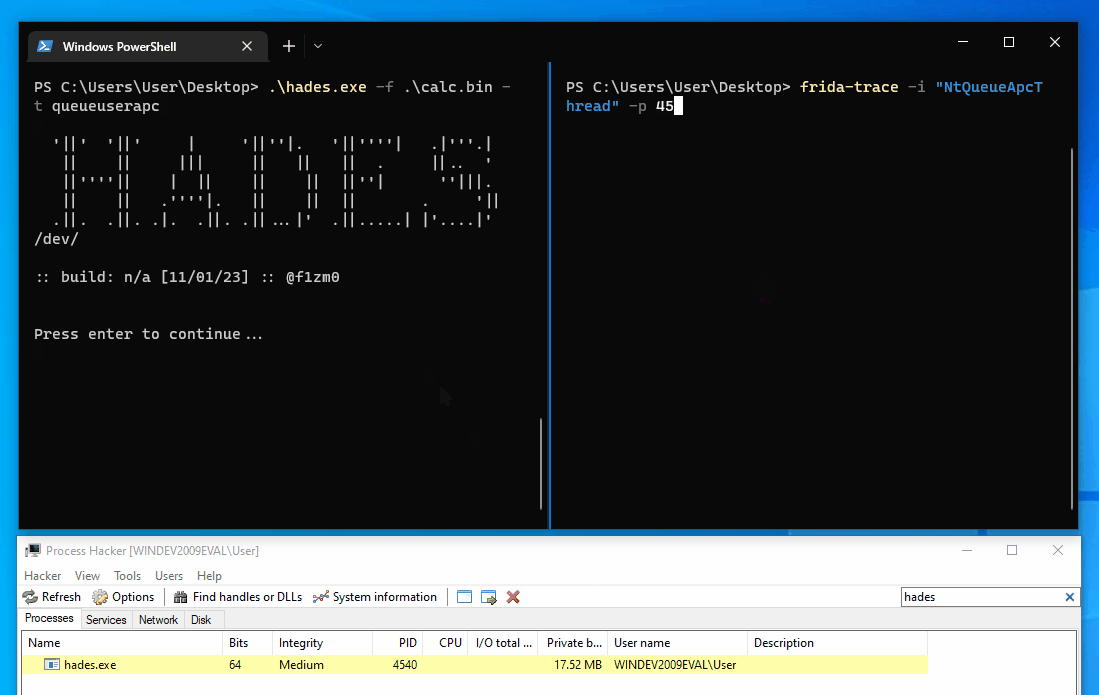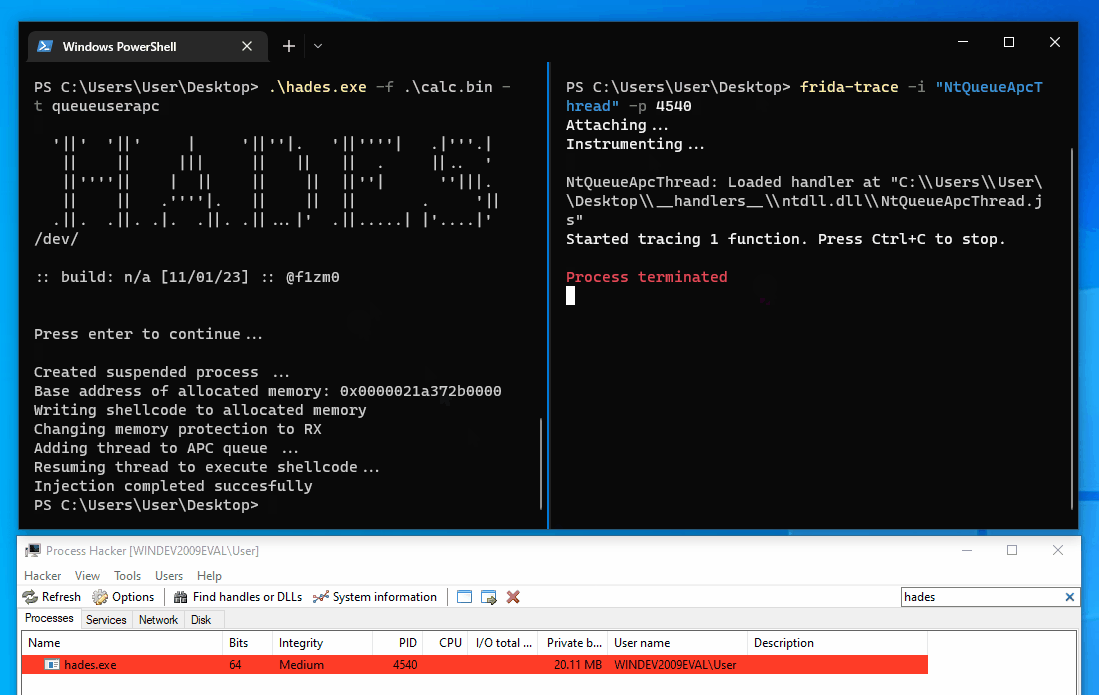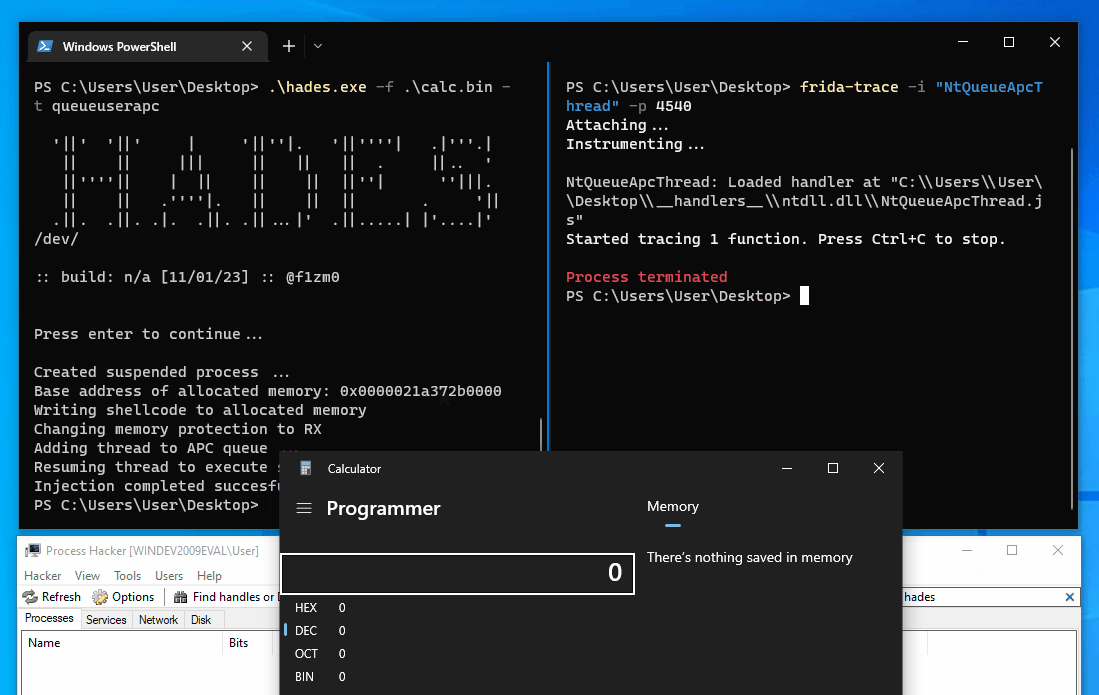 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 n00py/hwacha
Deploy payloads to *Nix systems en masse
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 saerxcit/libtp_gadget
Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.