CVE-2021-40444_CAB_archives

Custom CAB template generator for CVE-2021-40444, crafting malicious cabinet archives to exploit Windows MSHTML remote code execution via crafted…

Custom CAB template generator for CVE-2021-40444, crafting malicious cabinet archives to exploit Windows MSHTML remote code execution via crafted…

Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…

This repository contains a python script that will handle the majority of the dompdf cached font exploit (CVE-2022-28368), all you need to do is…

Bash exploit script for CVE-2020-7384, a remote code execution vulnerability in Apache NiFi, with improved usability and quality-of-life enhancements.

Bassmaster Plugin NodeJS RCE

The Havoc Framework

Python antivirus evasion tool

Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods

EGESPLOIT is a golang library for malware development

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs

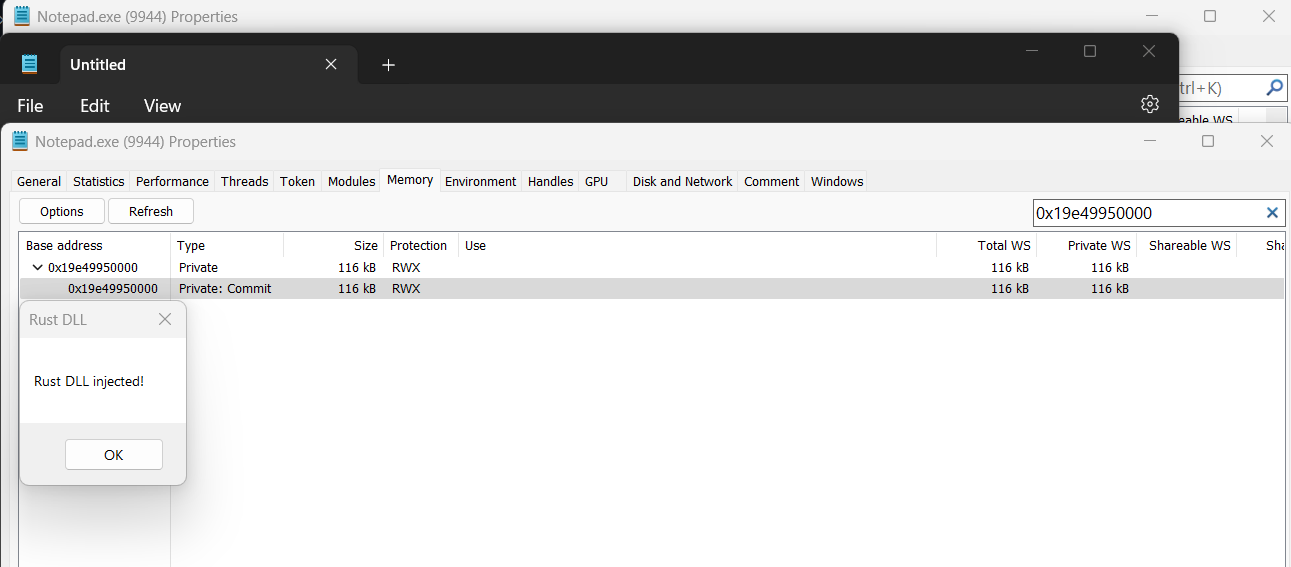
Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)

Shellcode injection technique. Given as C++ header, standalone Rust program or library.

A tool for generating reverse shell payloads on the fly.

HERCULES is a special payload generator that can bypass antivirus softwares.

Stealthily inject shellcode into an executable