
joro
 bishopfox/joro
A collaborative web exploitation framework.
command-and-controlexploit-frameworksfuzzing+5
bishopfox/joroA collaborative web exploitation framework.
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader

 mracumen/cve-2021-40444
Microsoft-Office-Word-MSHTML-Remote-Code-Execution-Exploit
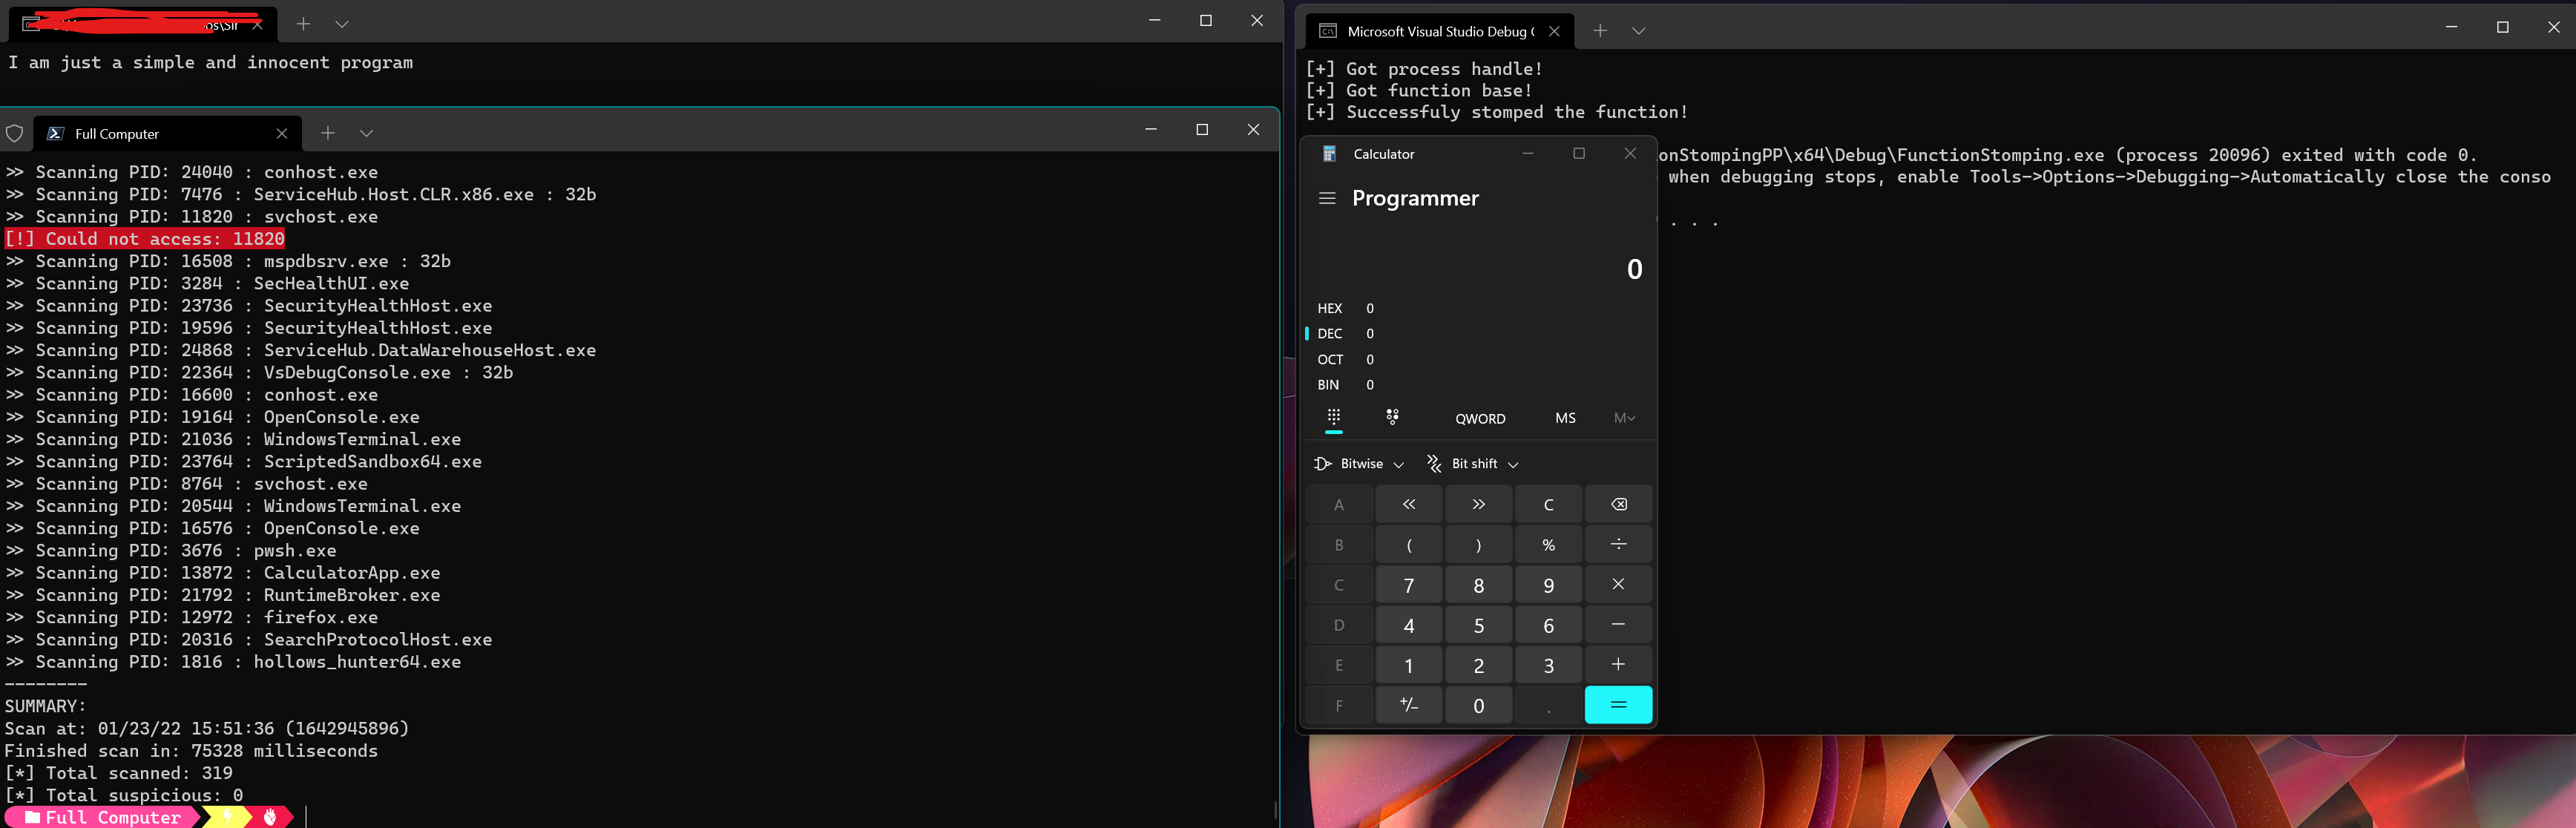 idov31/functionstomping
Shellcode injection technique. Given as C++ header, standalone Rust program or library.
 gmh5225/packer-kitsupe
Some PE hackery I'm working on (shellcode loader, packer, all WIP)
 m4sc3r4n0/astroid
ASTROID v 1.2 bypass most A.V softwares
 0xsha/cve-2026-6307
Google Chrome CVE-2026-6307 PoC
 darthton/blackbone
Windows memory hacking library
 x0rz/eqgrp
Decrypted content of eqgrp-auction-file.tar.xz
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 nccgroup/winpayloads
Undetectable Windows Payload Generation
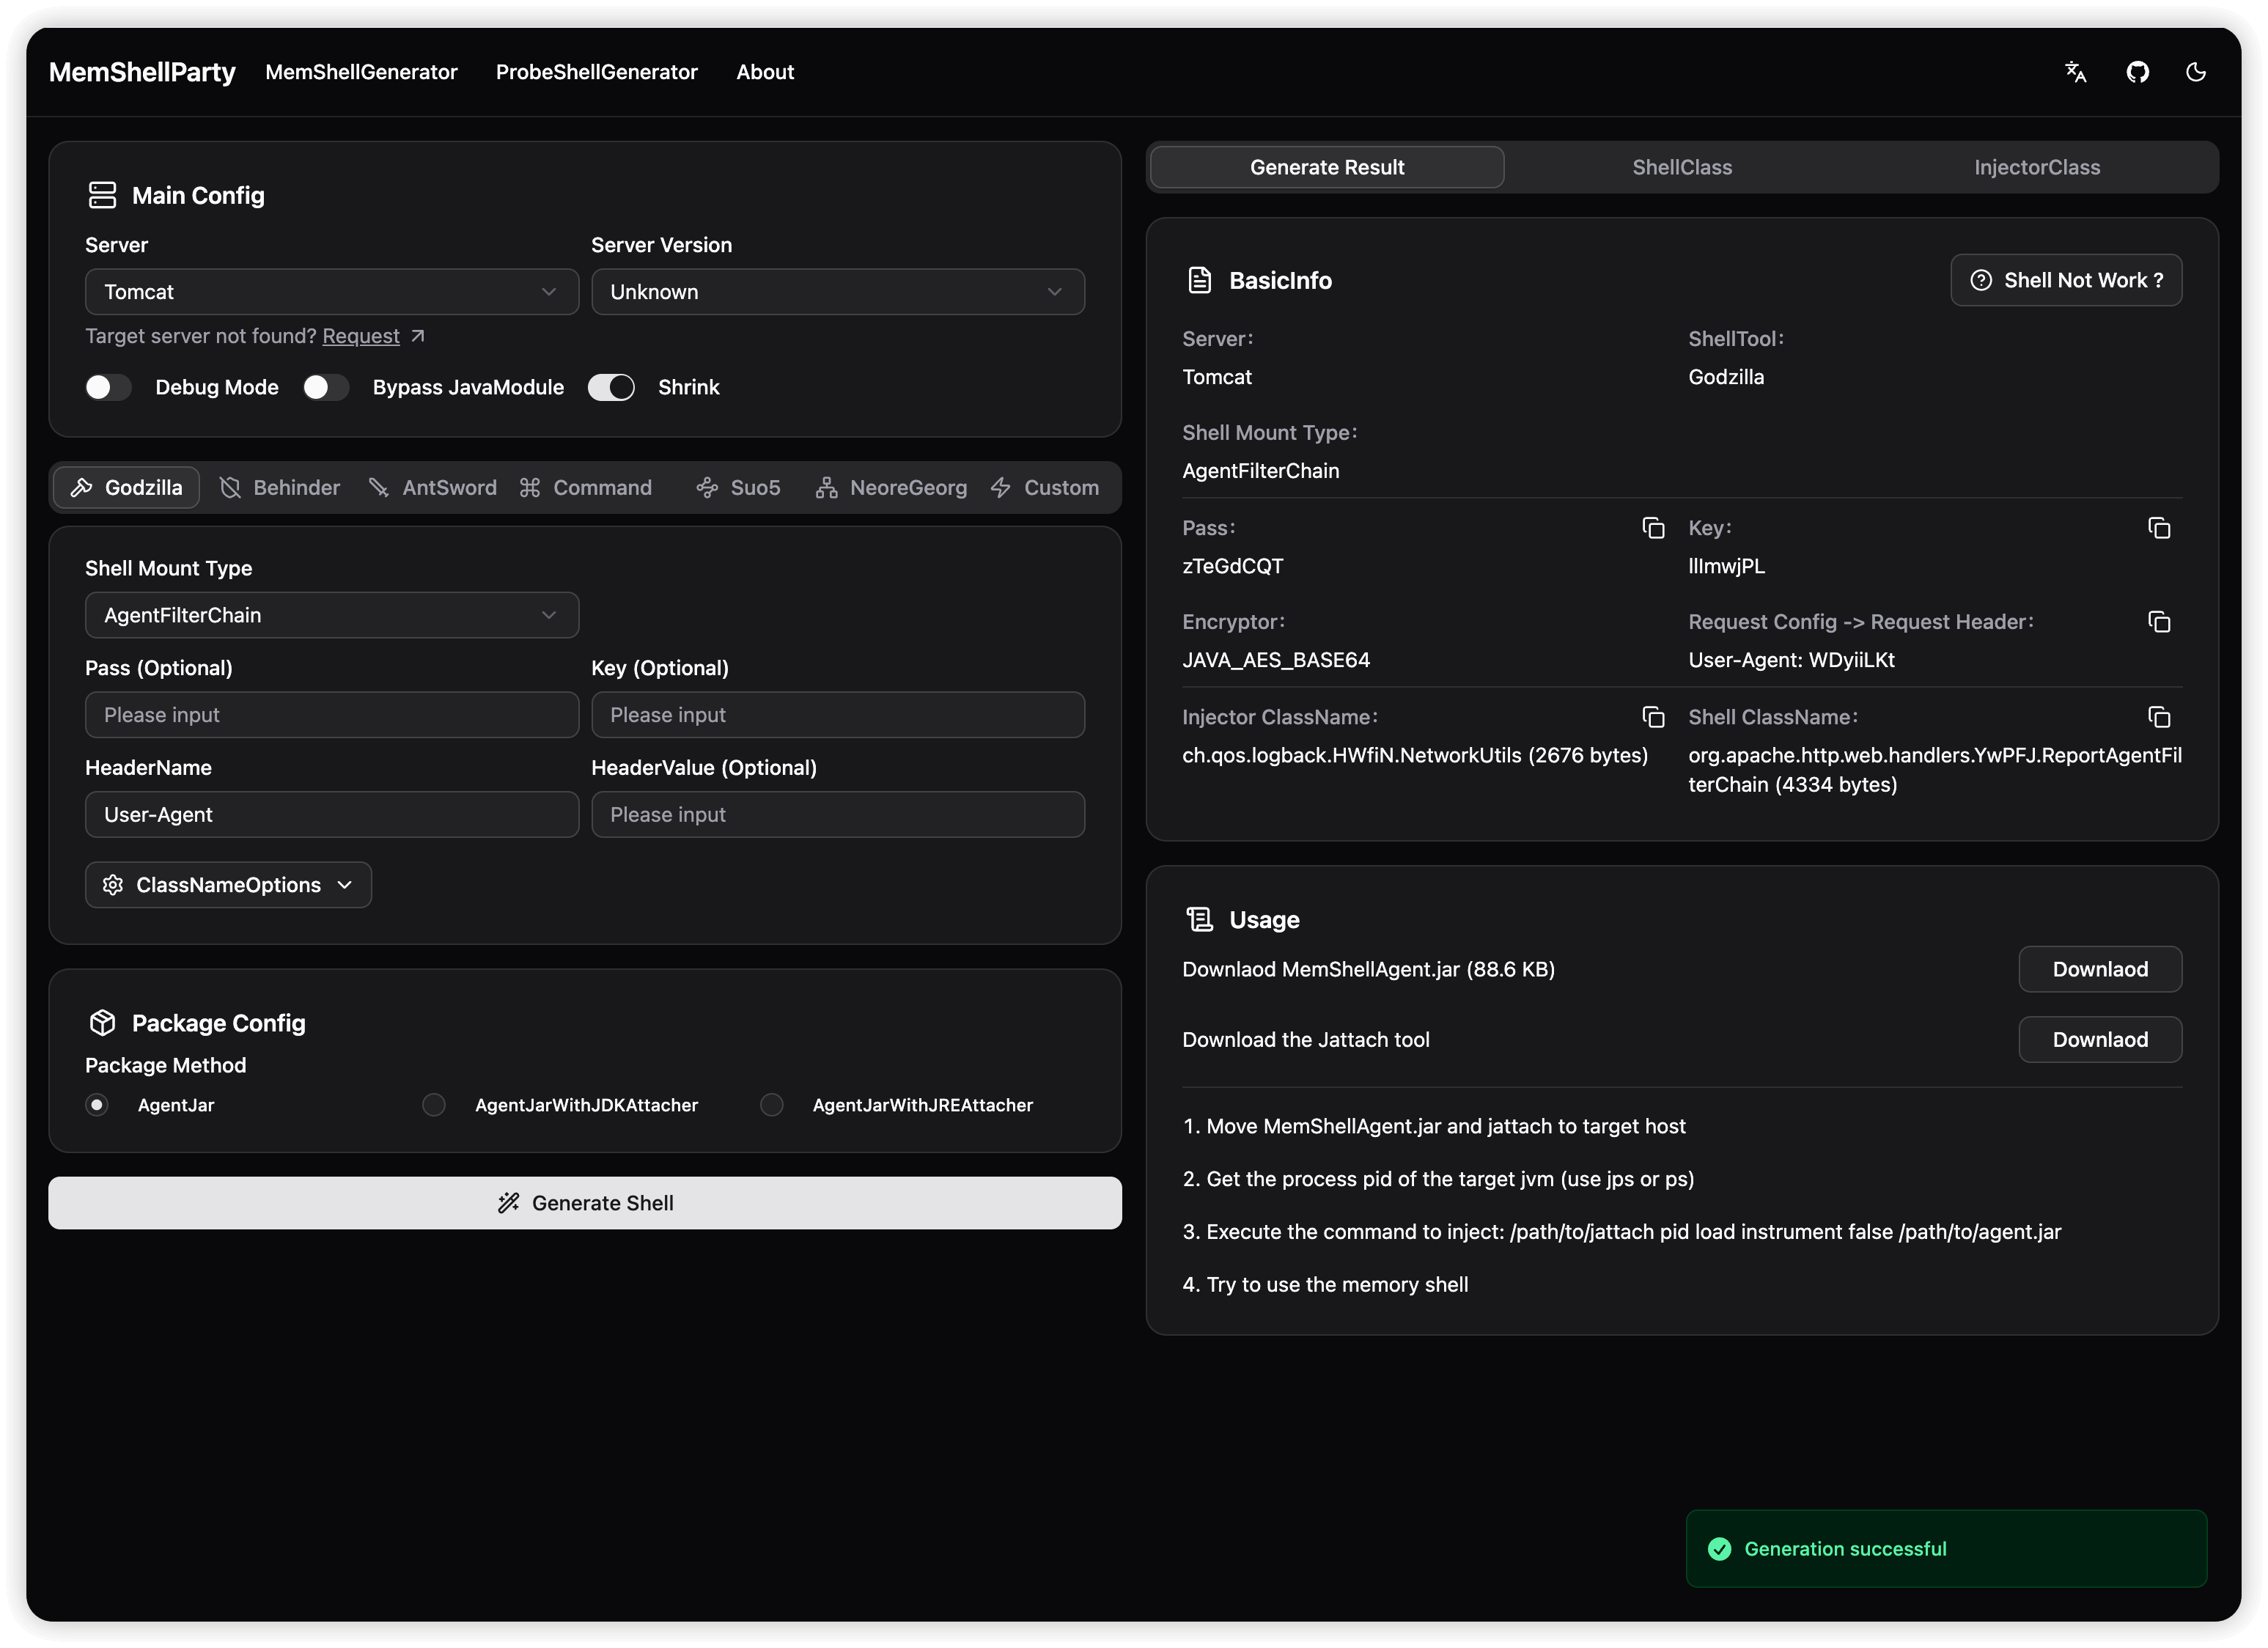 reajason/memshellparty
一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
 tokyoneon/chimera
Chimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.