
SILVERPICK
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
exploitationpayload-developmentred-teaming+2
160
winterknife/silverpickWindows User-Mode Shellcode Development Framework (WUMSDF)
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
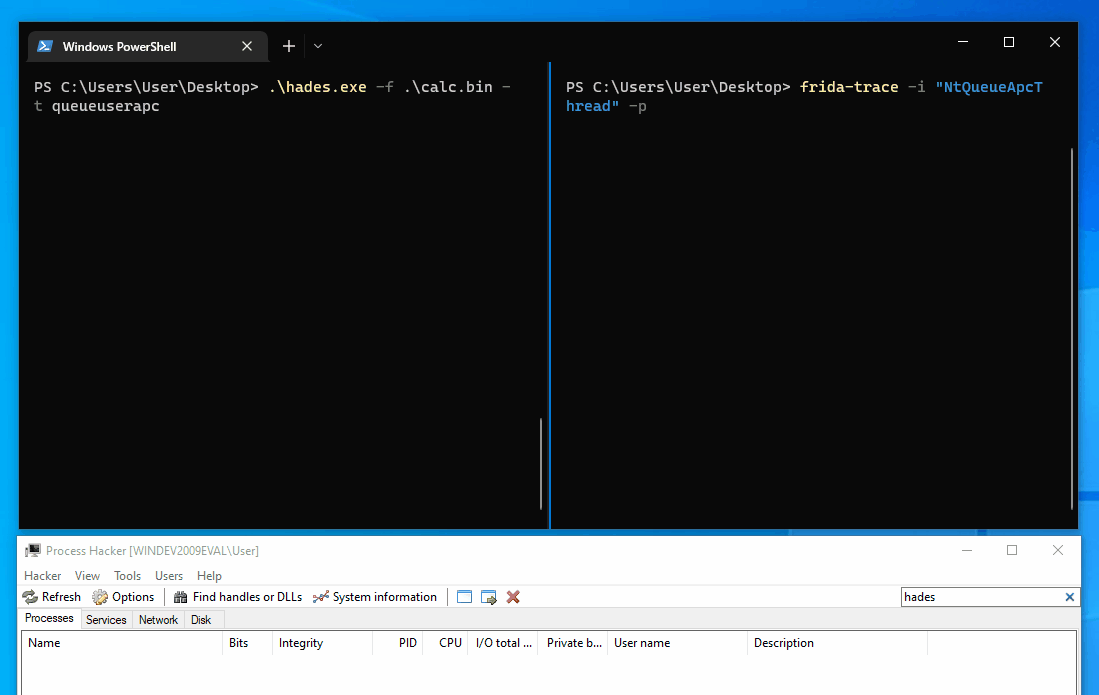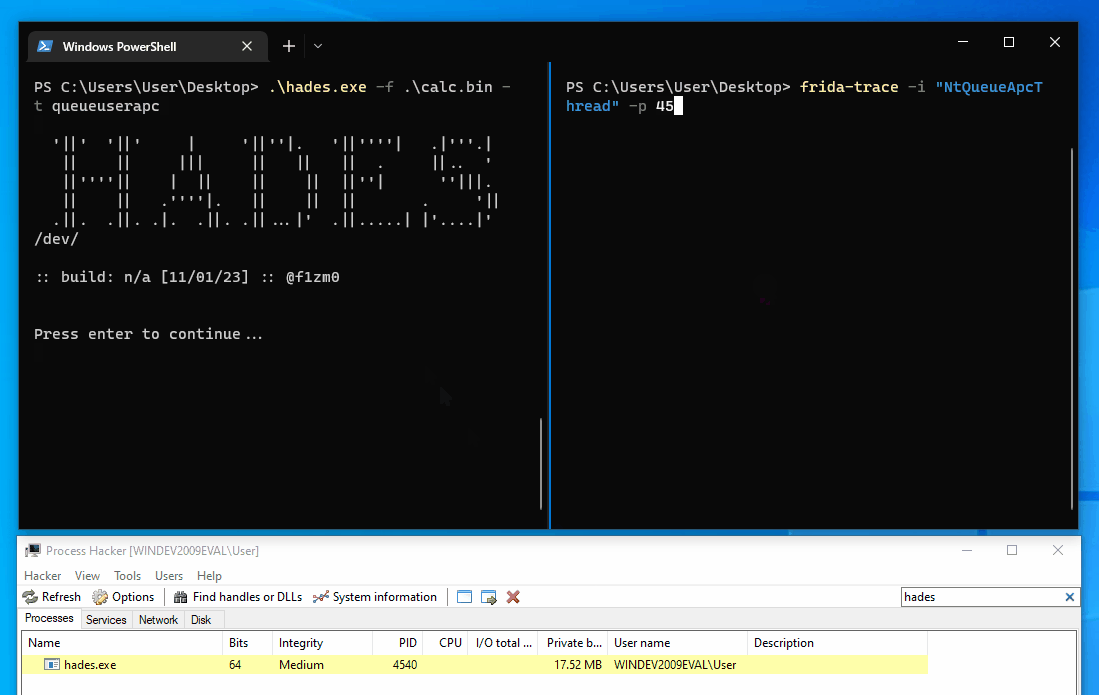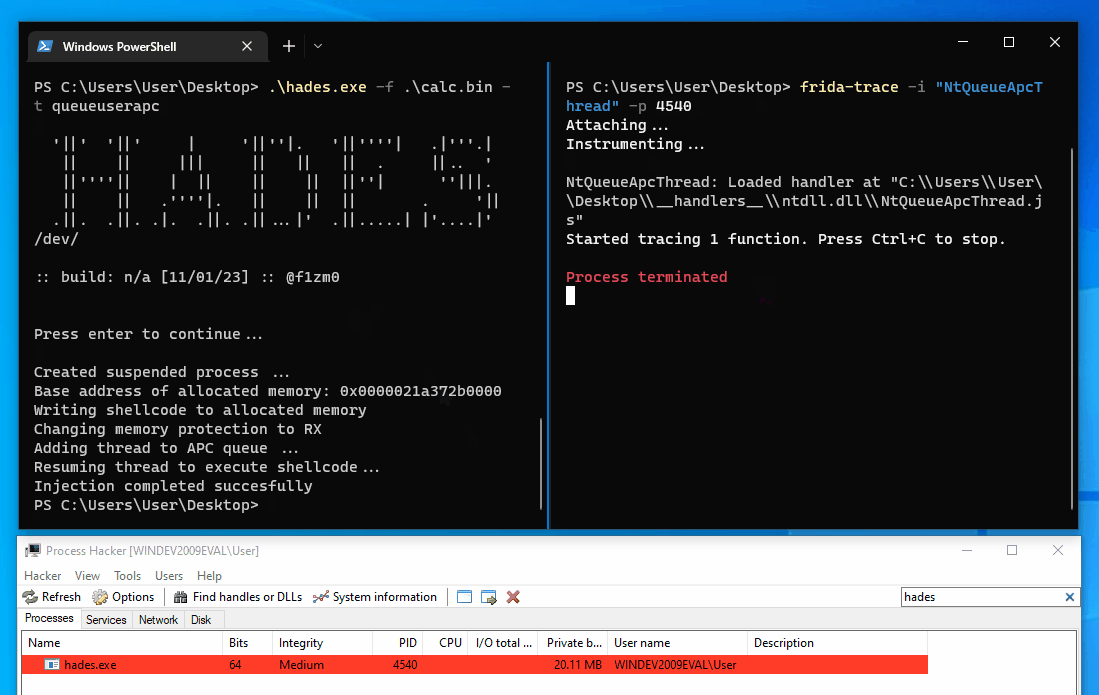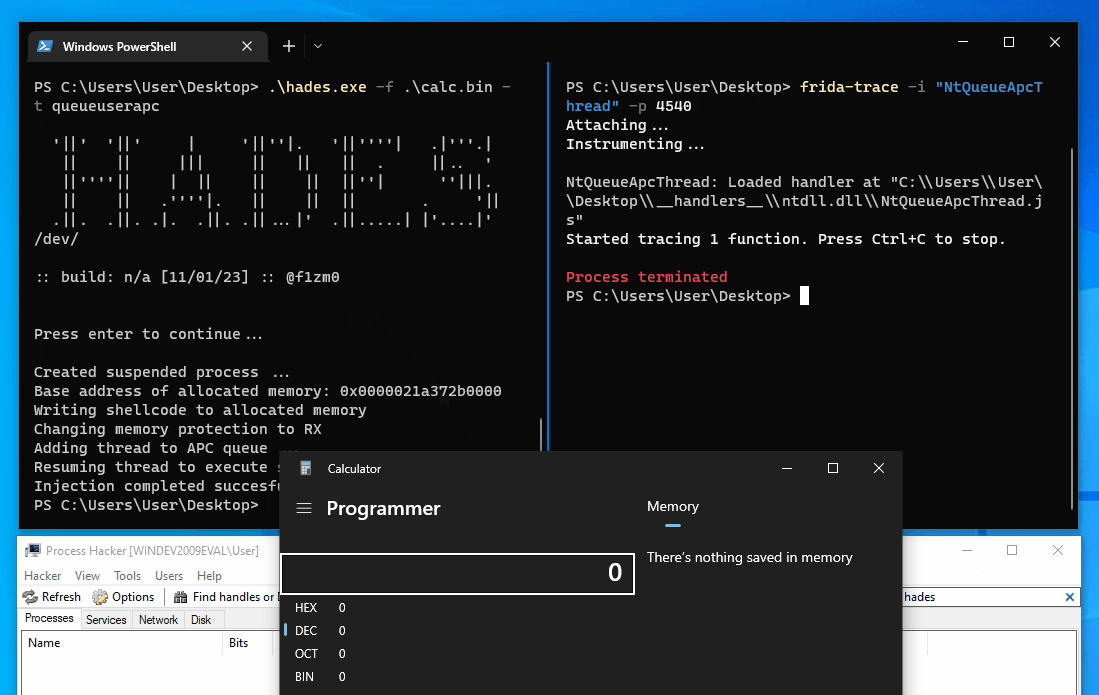 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
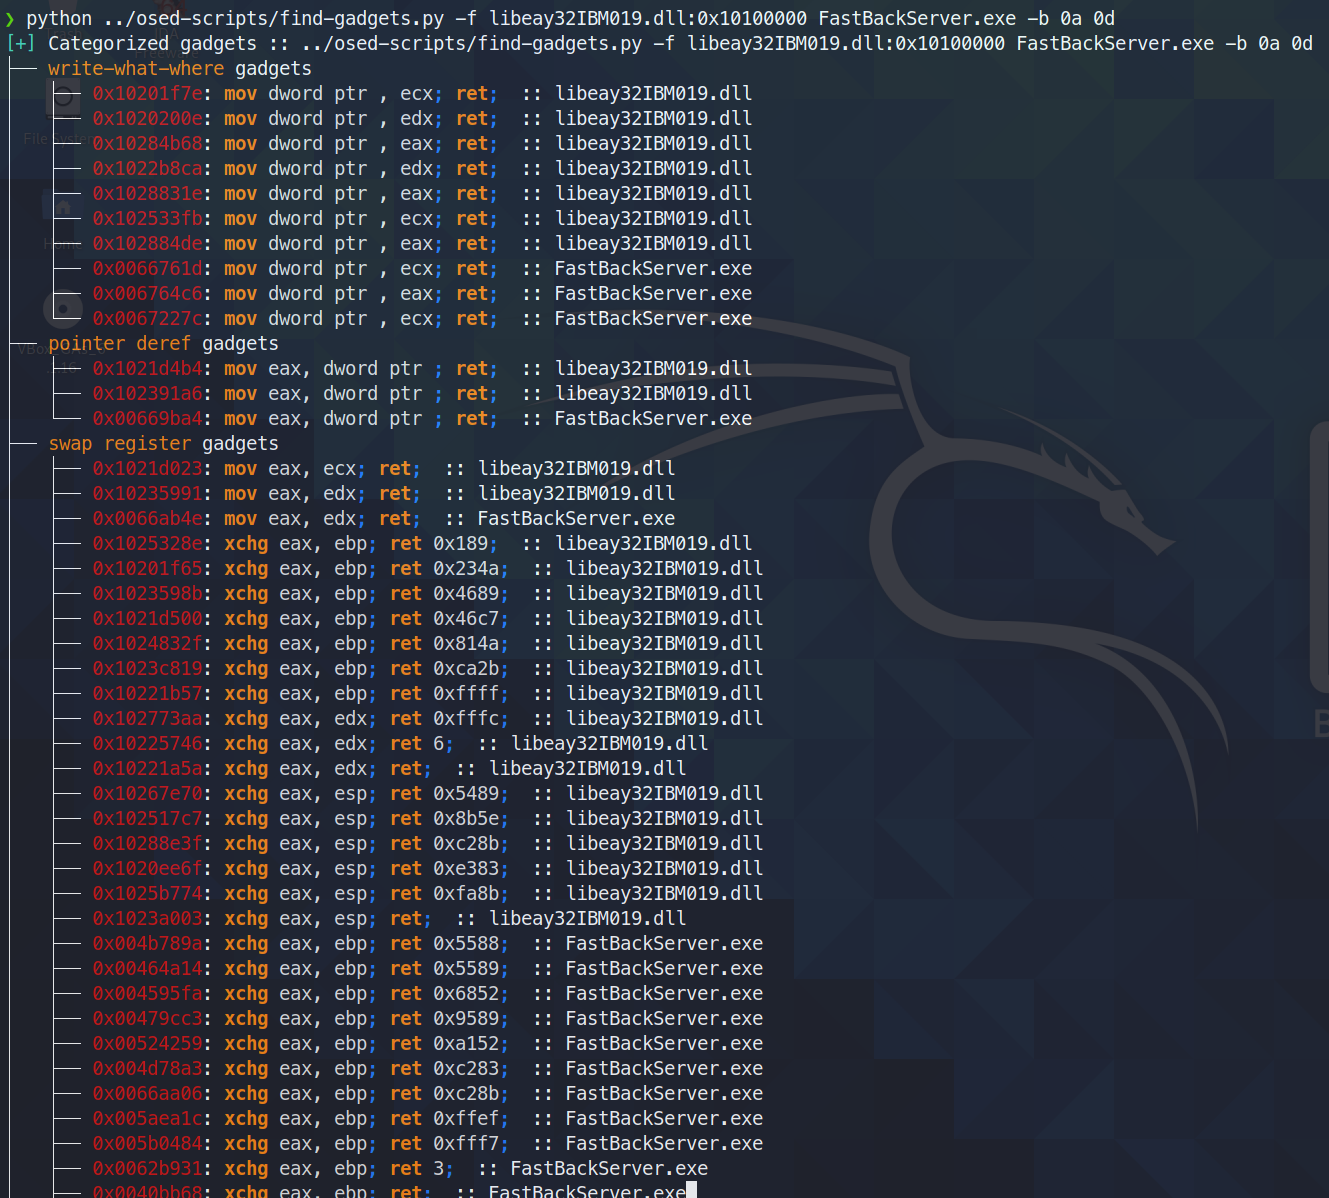 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 mracumen/cve-2021-40444
Microsoft-Office-Word-MSHTML-Remote-Code-Execution-Exploit
 tiagob0b/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 damariion/cve-2015-8522.rce
Exploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…
 pwn1sher/frostbyte
Combines AppDomain Manager injection with shellcode embedding in signed binaries to evade EDR/AV detection for red team payloads.
 cryptolok/morphaes
IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 souhardya/zerodoor
A script written lazily for generating cross-platform backdoors on the go :)
 vlad902/hacking-team-windows-kernel-lpe
Previously-0day exploit from the Hacking Team leak, written by Eugene Ching/Qavar.
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection