

Winpayloads
 nccgroup/winpayloads
Undetectable Windows Payload Generation
command-and-controlexploit-frameworkslateral-movement+9
1.6k
nccgroup/winpayloadsUndetectable Windows Payload Generation
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 0x00-0x00/shellpop
Pop shells like a master.
 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 aetsu/offensivepipeline
OfensivePipeline allows you to download and build C# tools, applying certain modifications in order to improve their evasion for Red Team exercises.
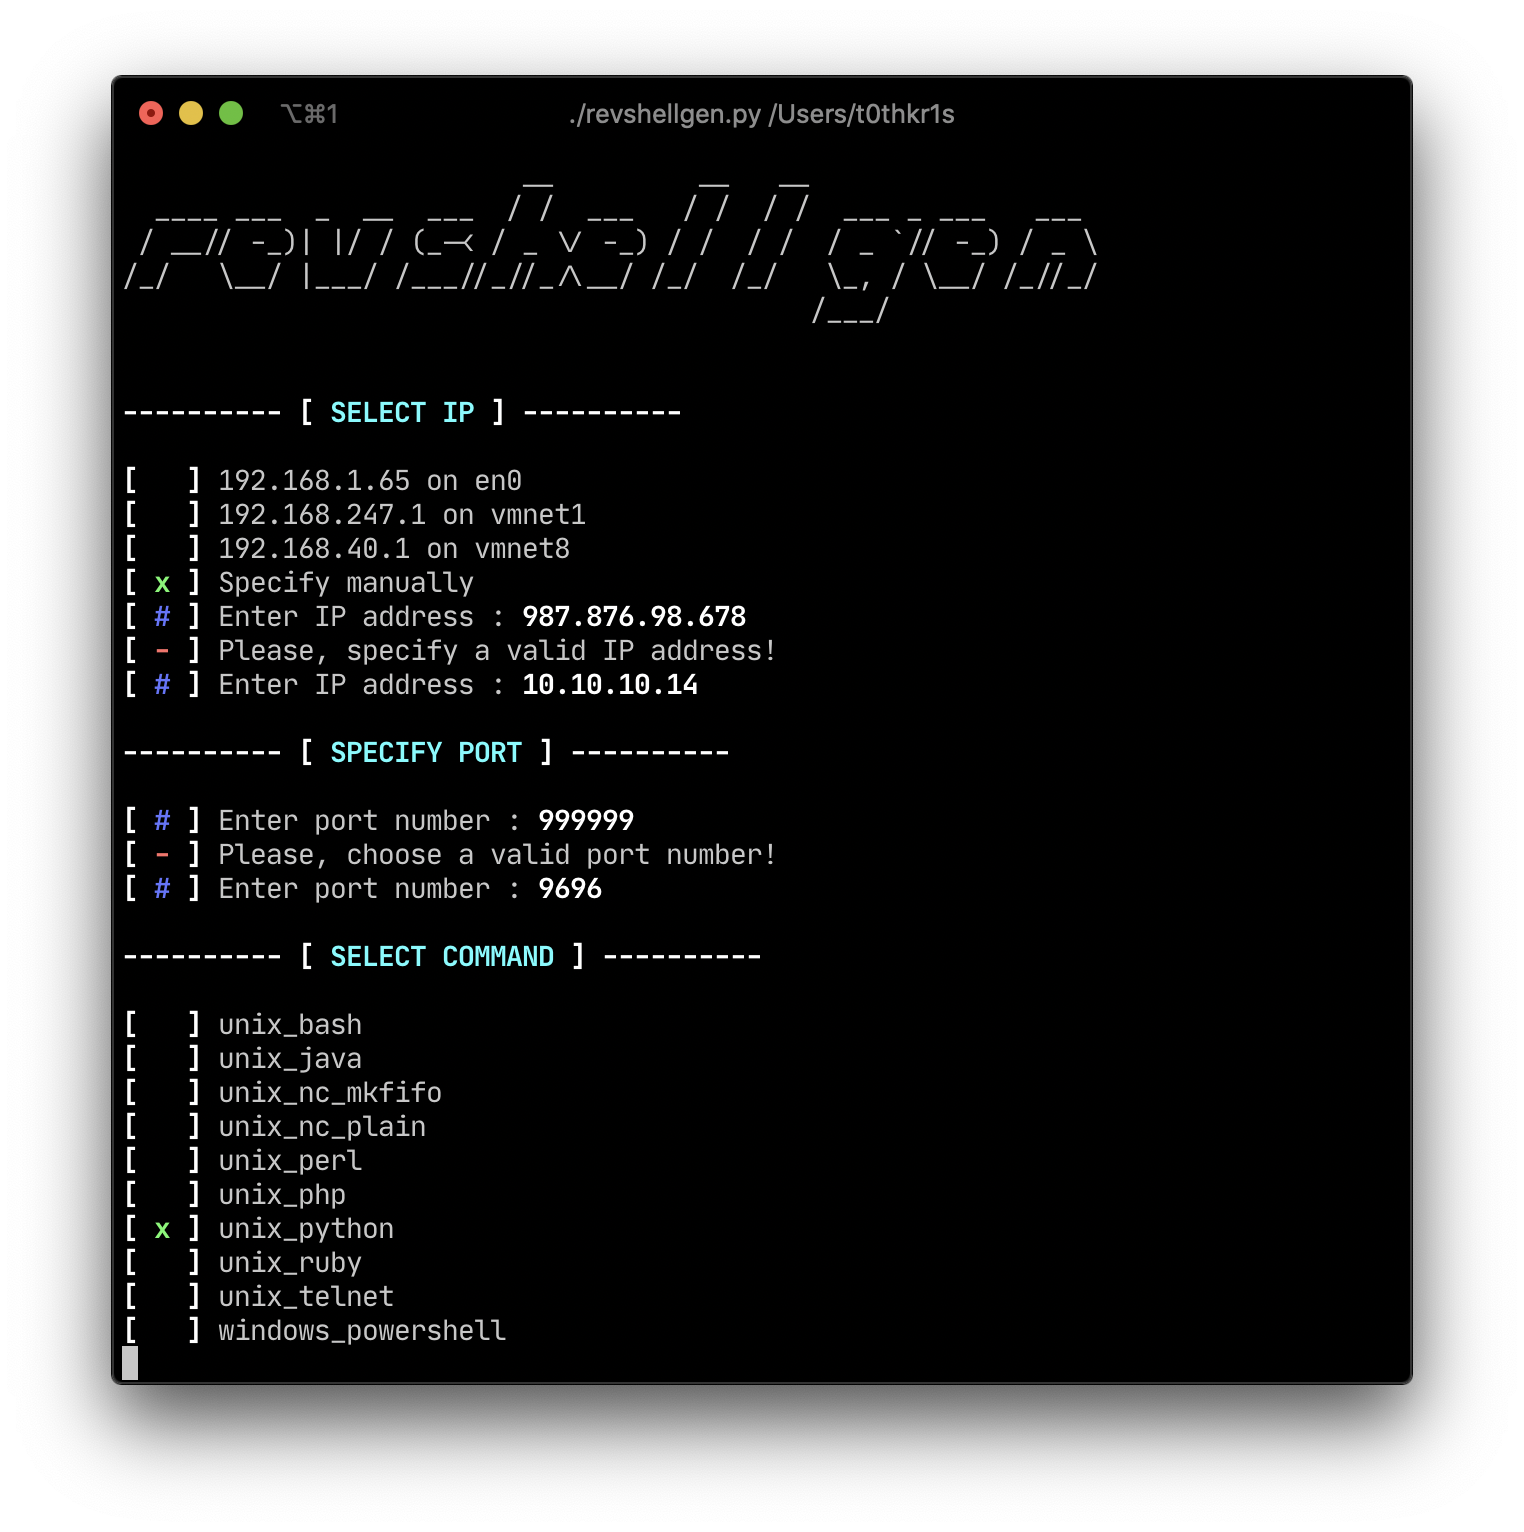 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.

 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
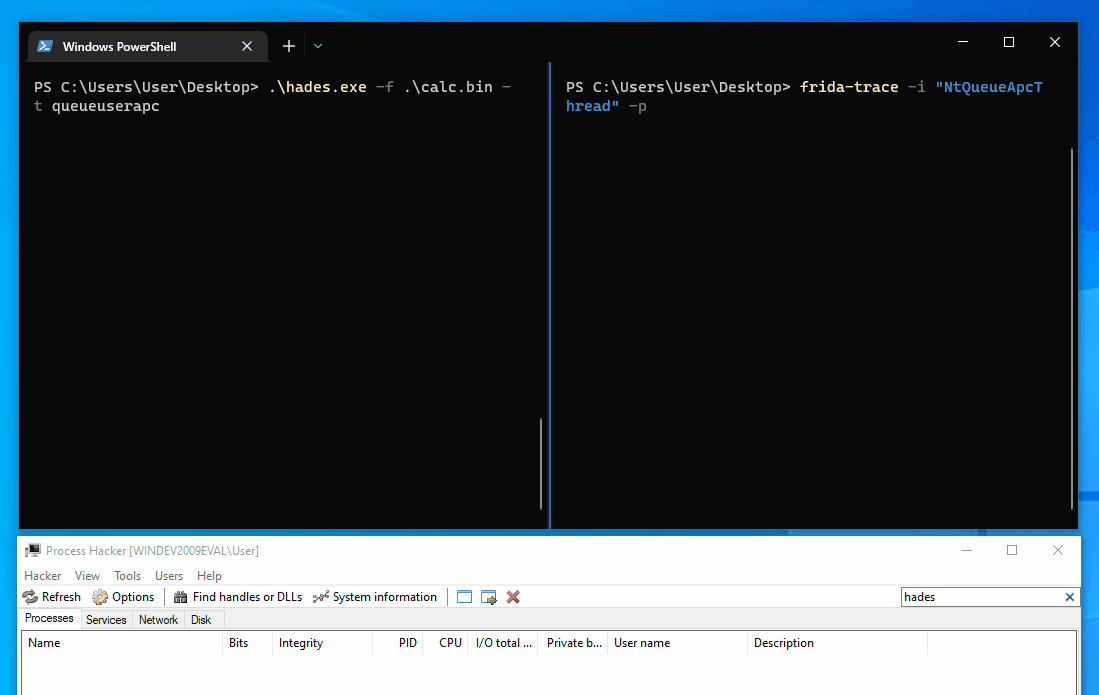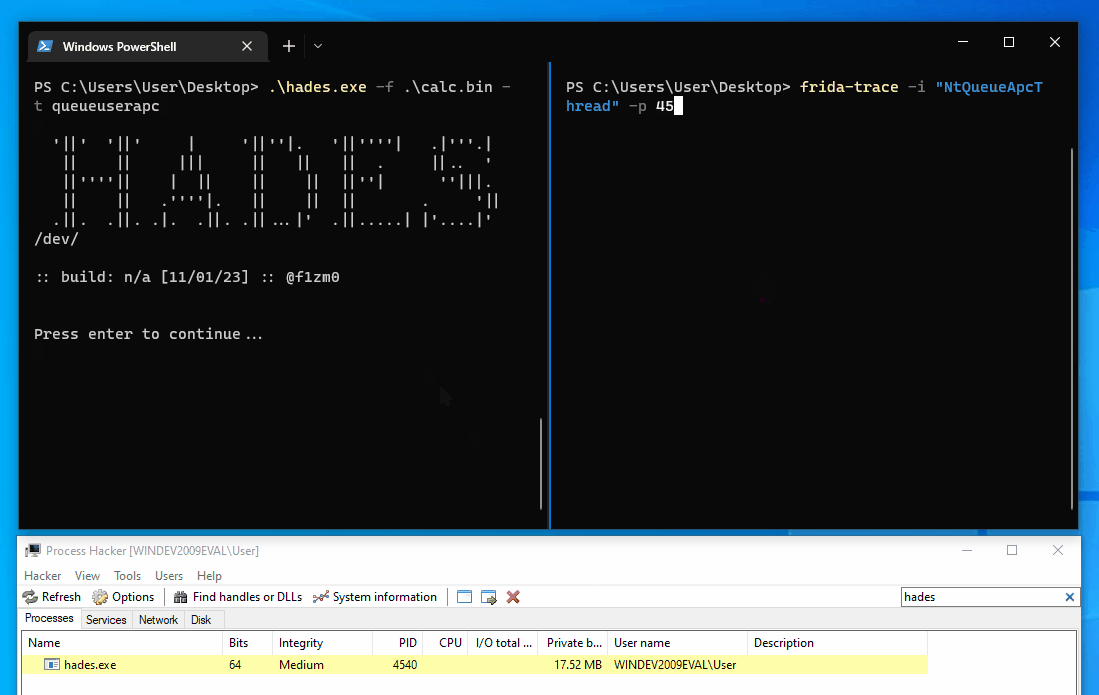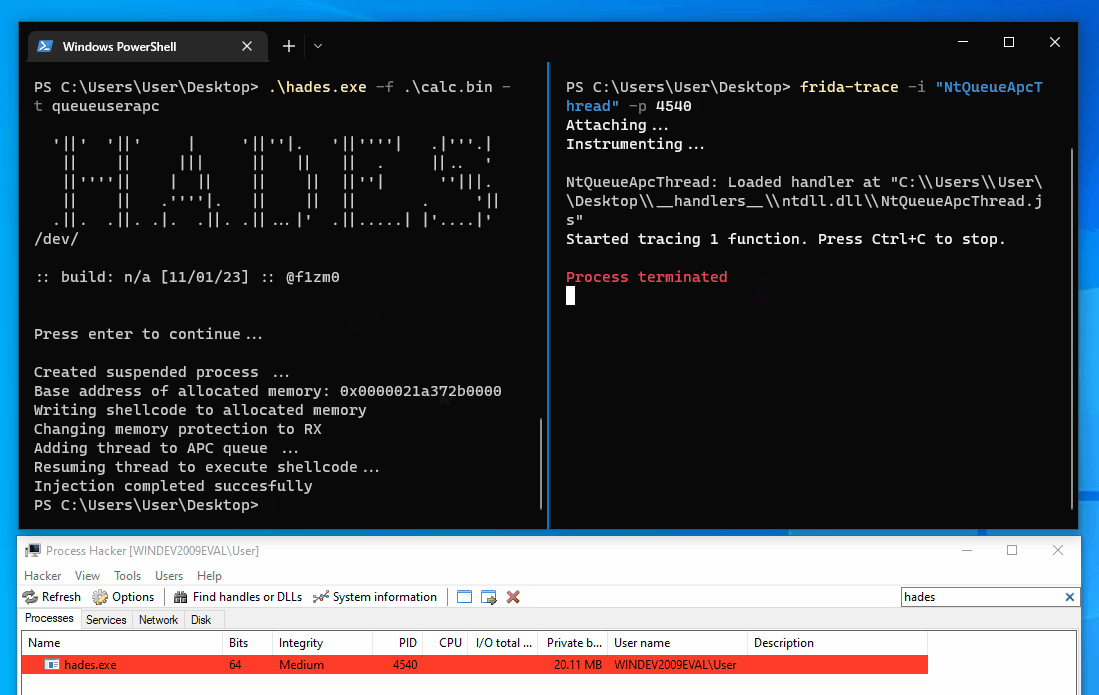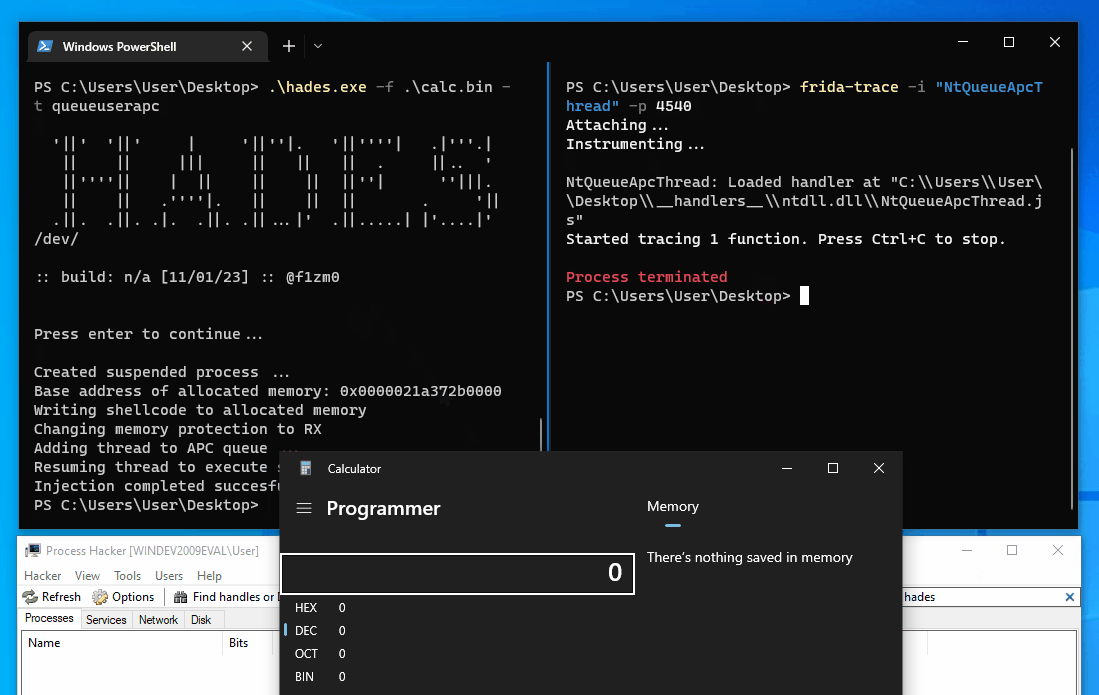 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 n00py/hwacha
Deploy payloads to *Nix systems en masse
 tremwil/ds3-nrssr-rce
Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
 saerxcit/libtp_gadget
Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
 hvictor/shellcode-x64
Shellcodes for Windows >= 11 x64
 oddcod3/phantom-evasion
Python antivirus evasion tool
