CVE-2017-14980
 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
binary-exploitationdebuggerseducation+5
1
godoy-sec/cve-2017-14980Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
 saerxcit/libtp_gadget
Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 bishopfox/sliver
Adversary Emulation Framework
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
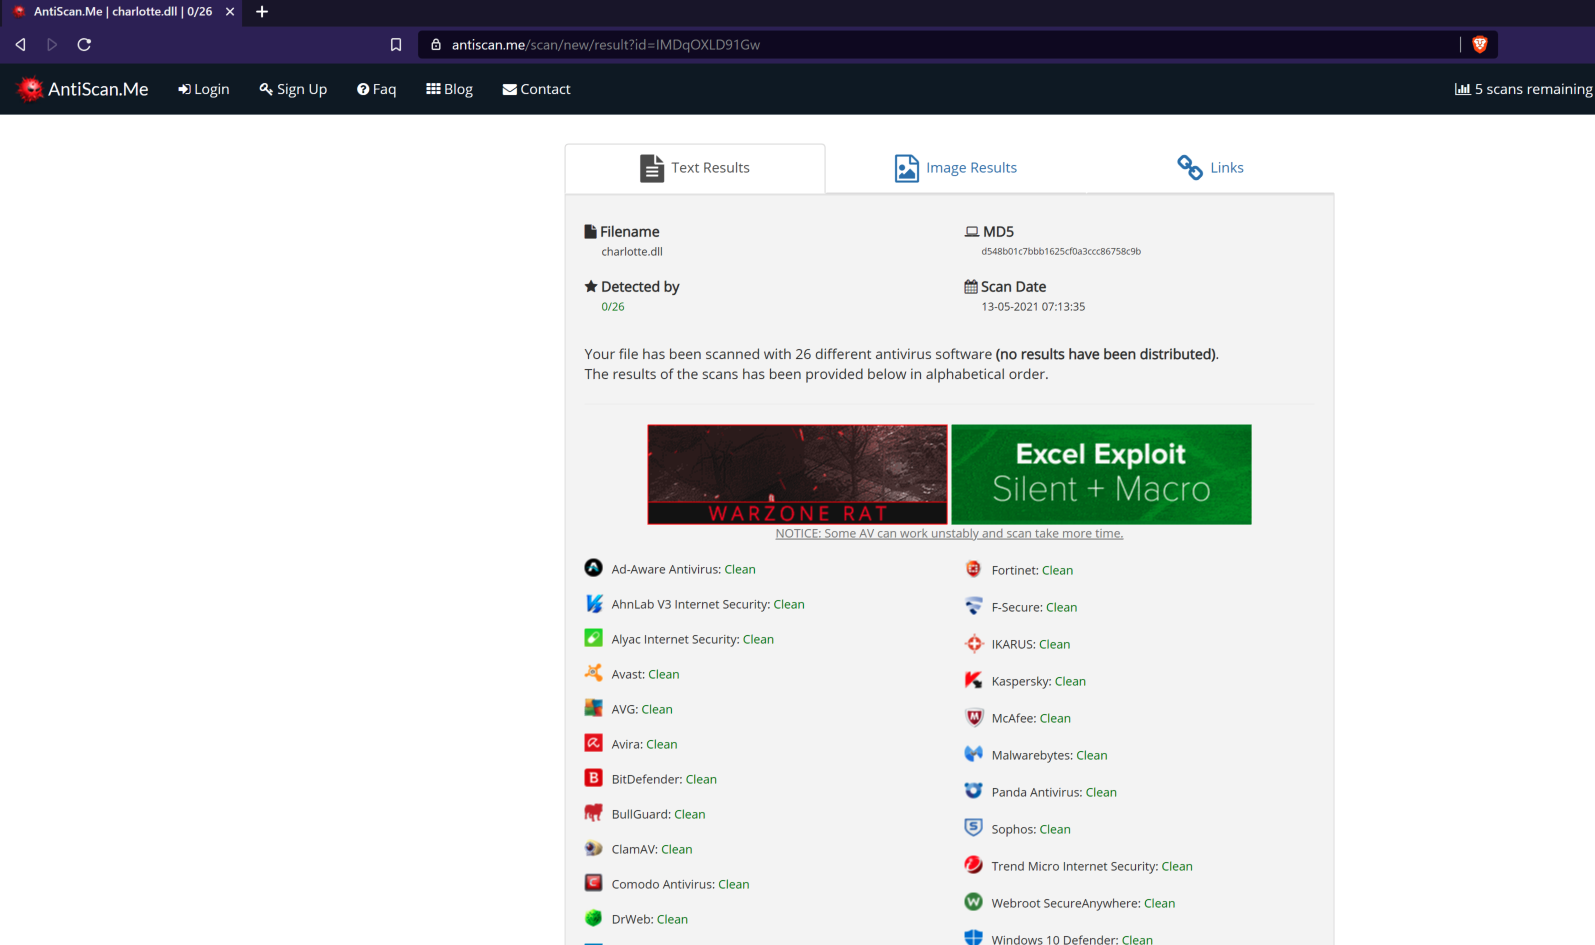 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
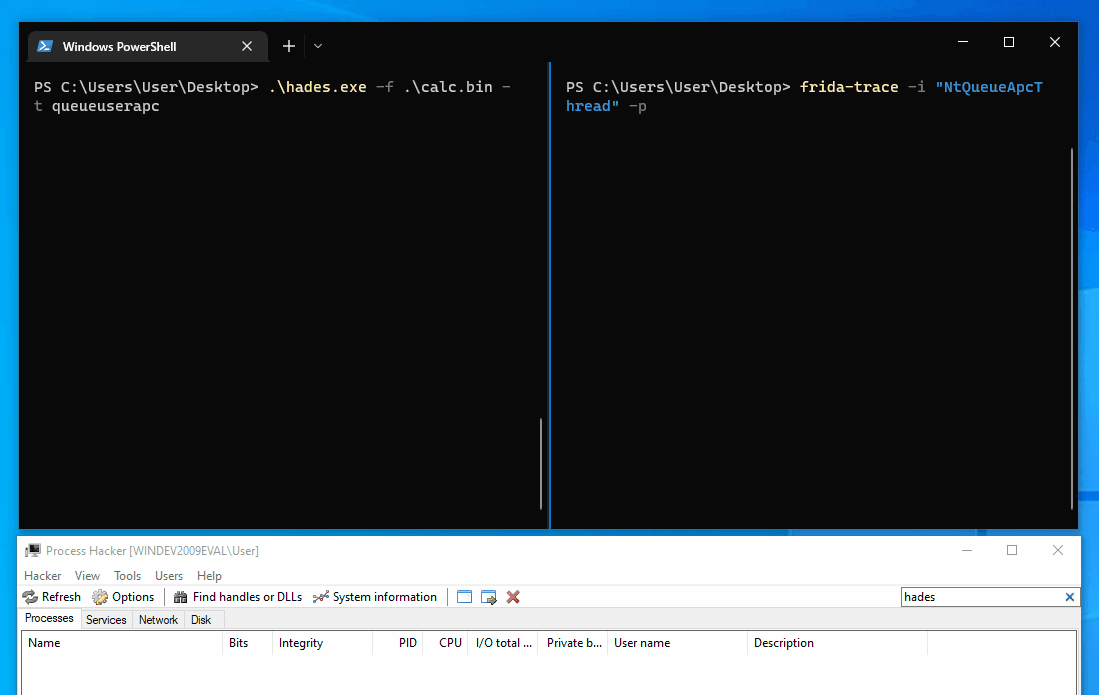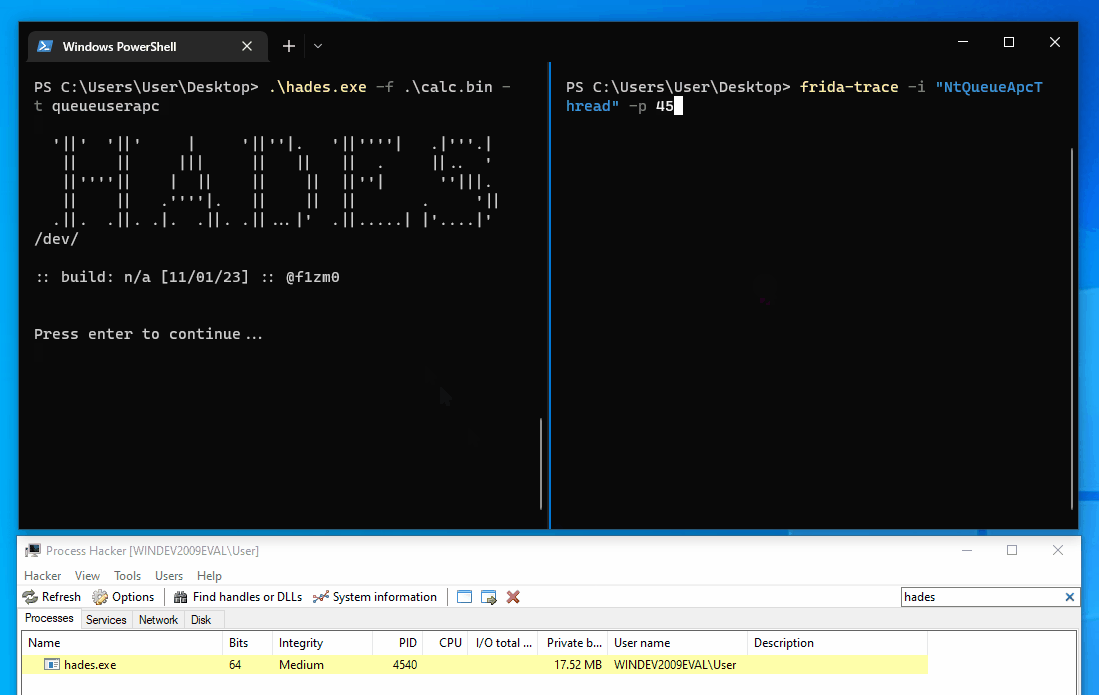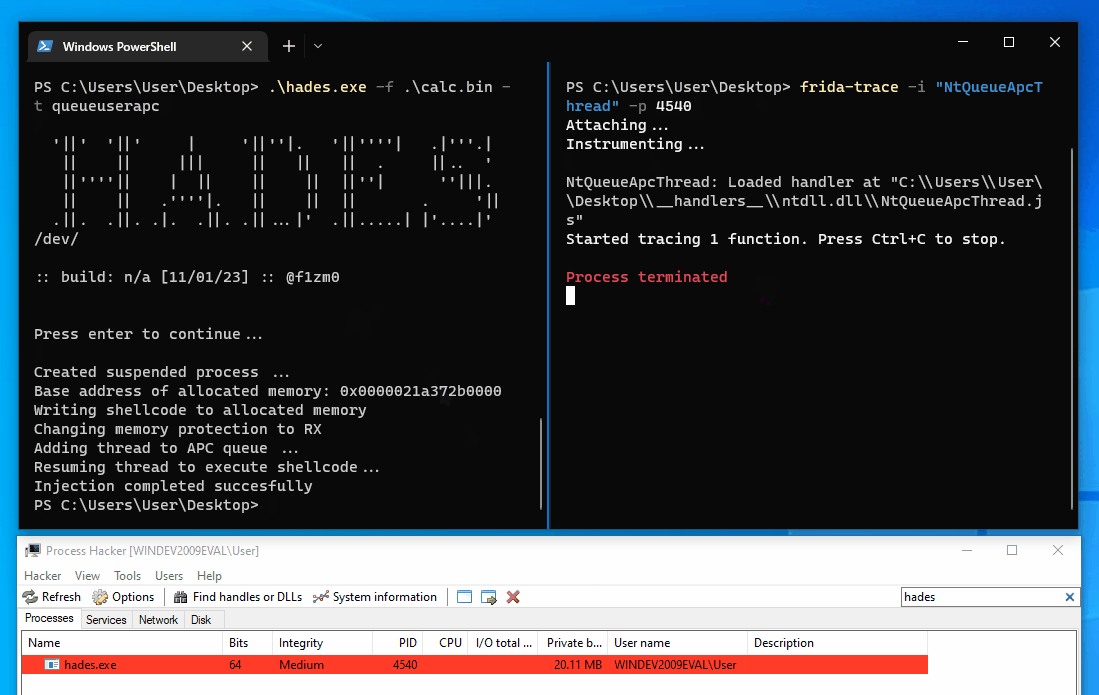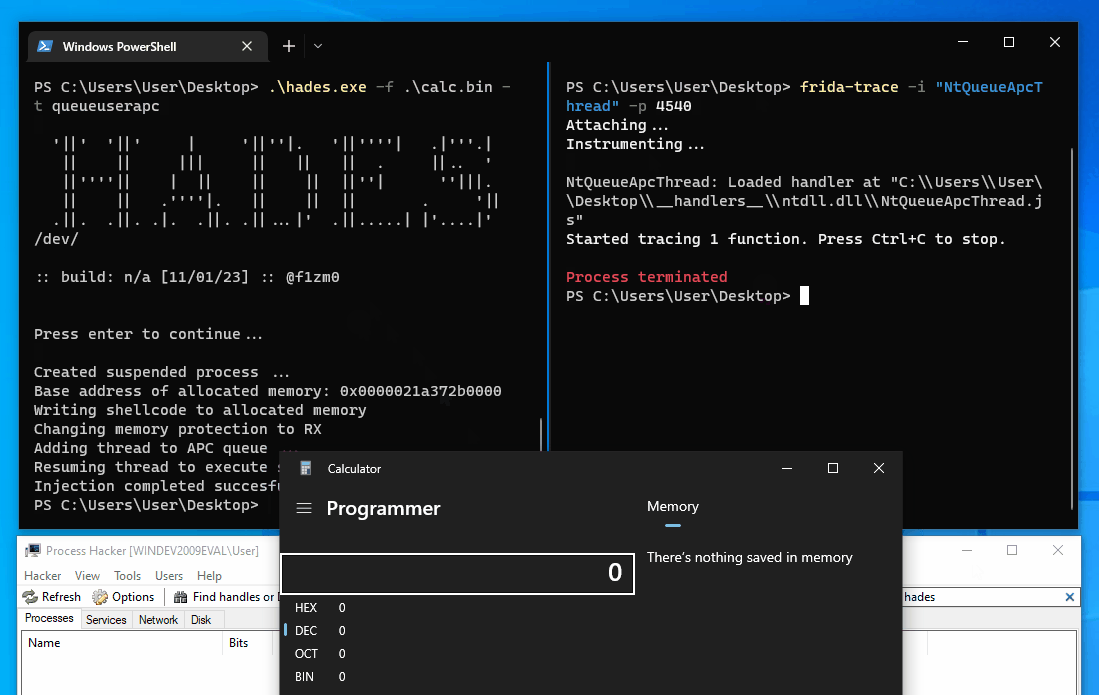 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.