

CVE-2025-3969-Exploit
 stuub/cve-2025-3969-exploit
CVE-2025-3969: Exploit PoC (OS CMD injection, Web Shell, Interactive Shell)
command-and-controlexploitationpayload-generation+3
2
stuub/cve-2025-3969-exploitCVE-2025-3969: Exploit PoC (OS CMD injection, Web Shell, Interactive Shell)
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
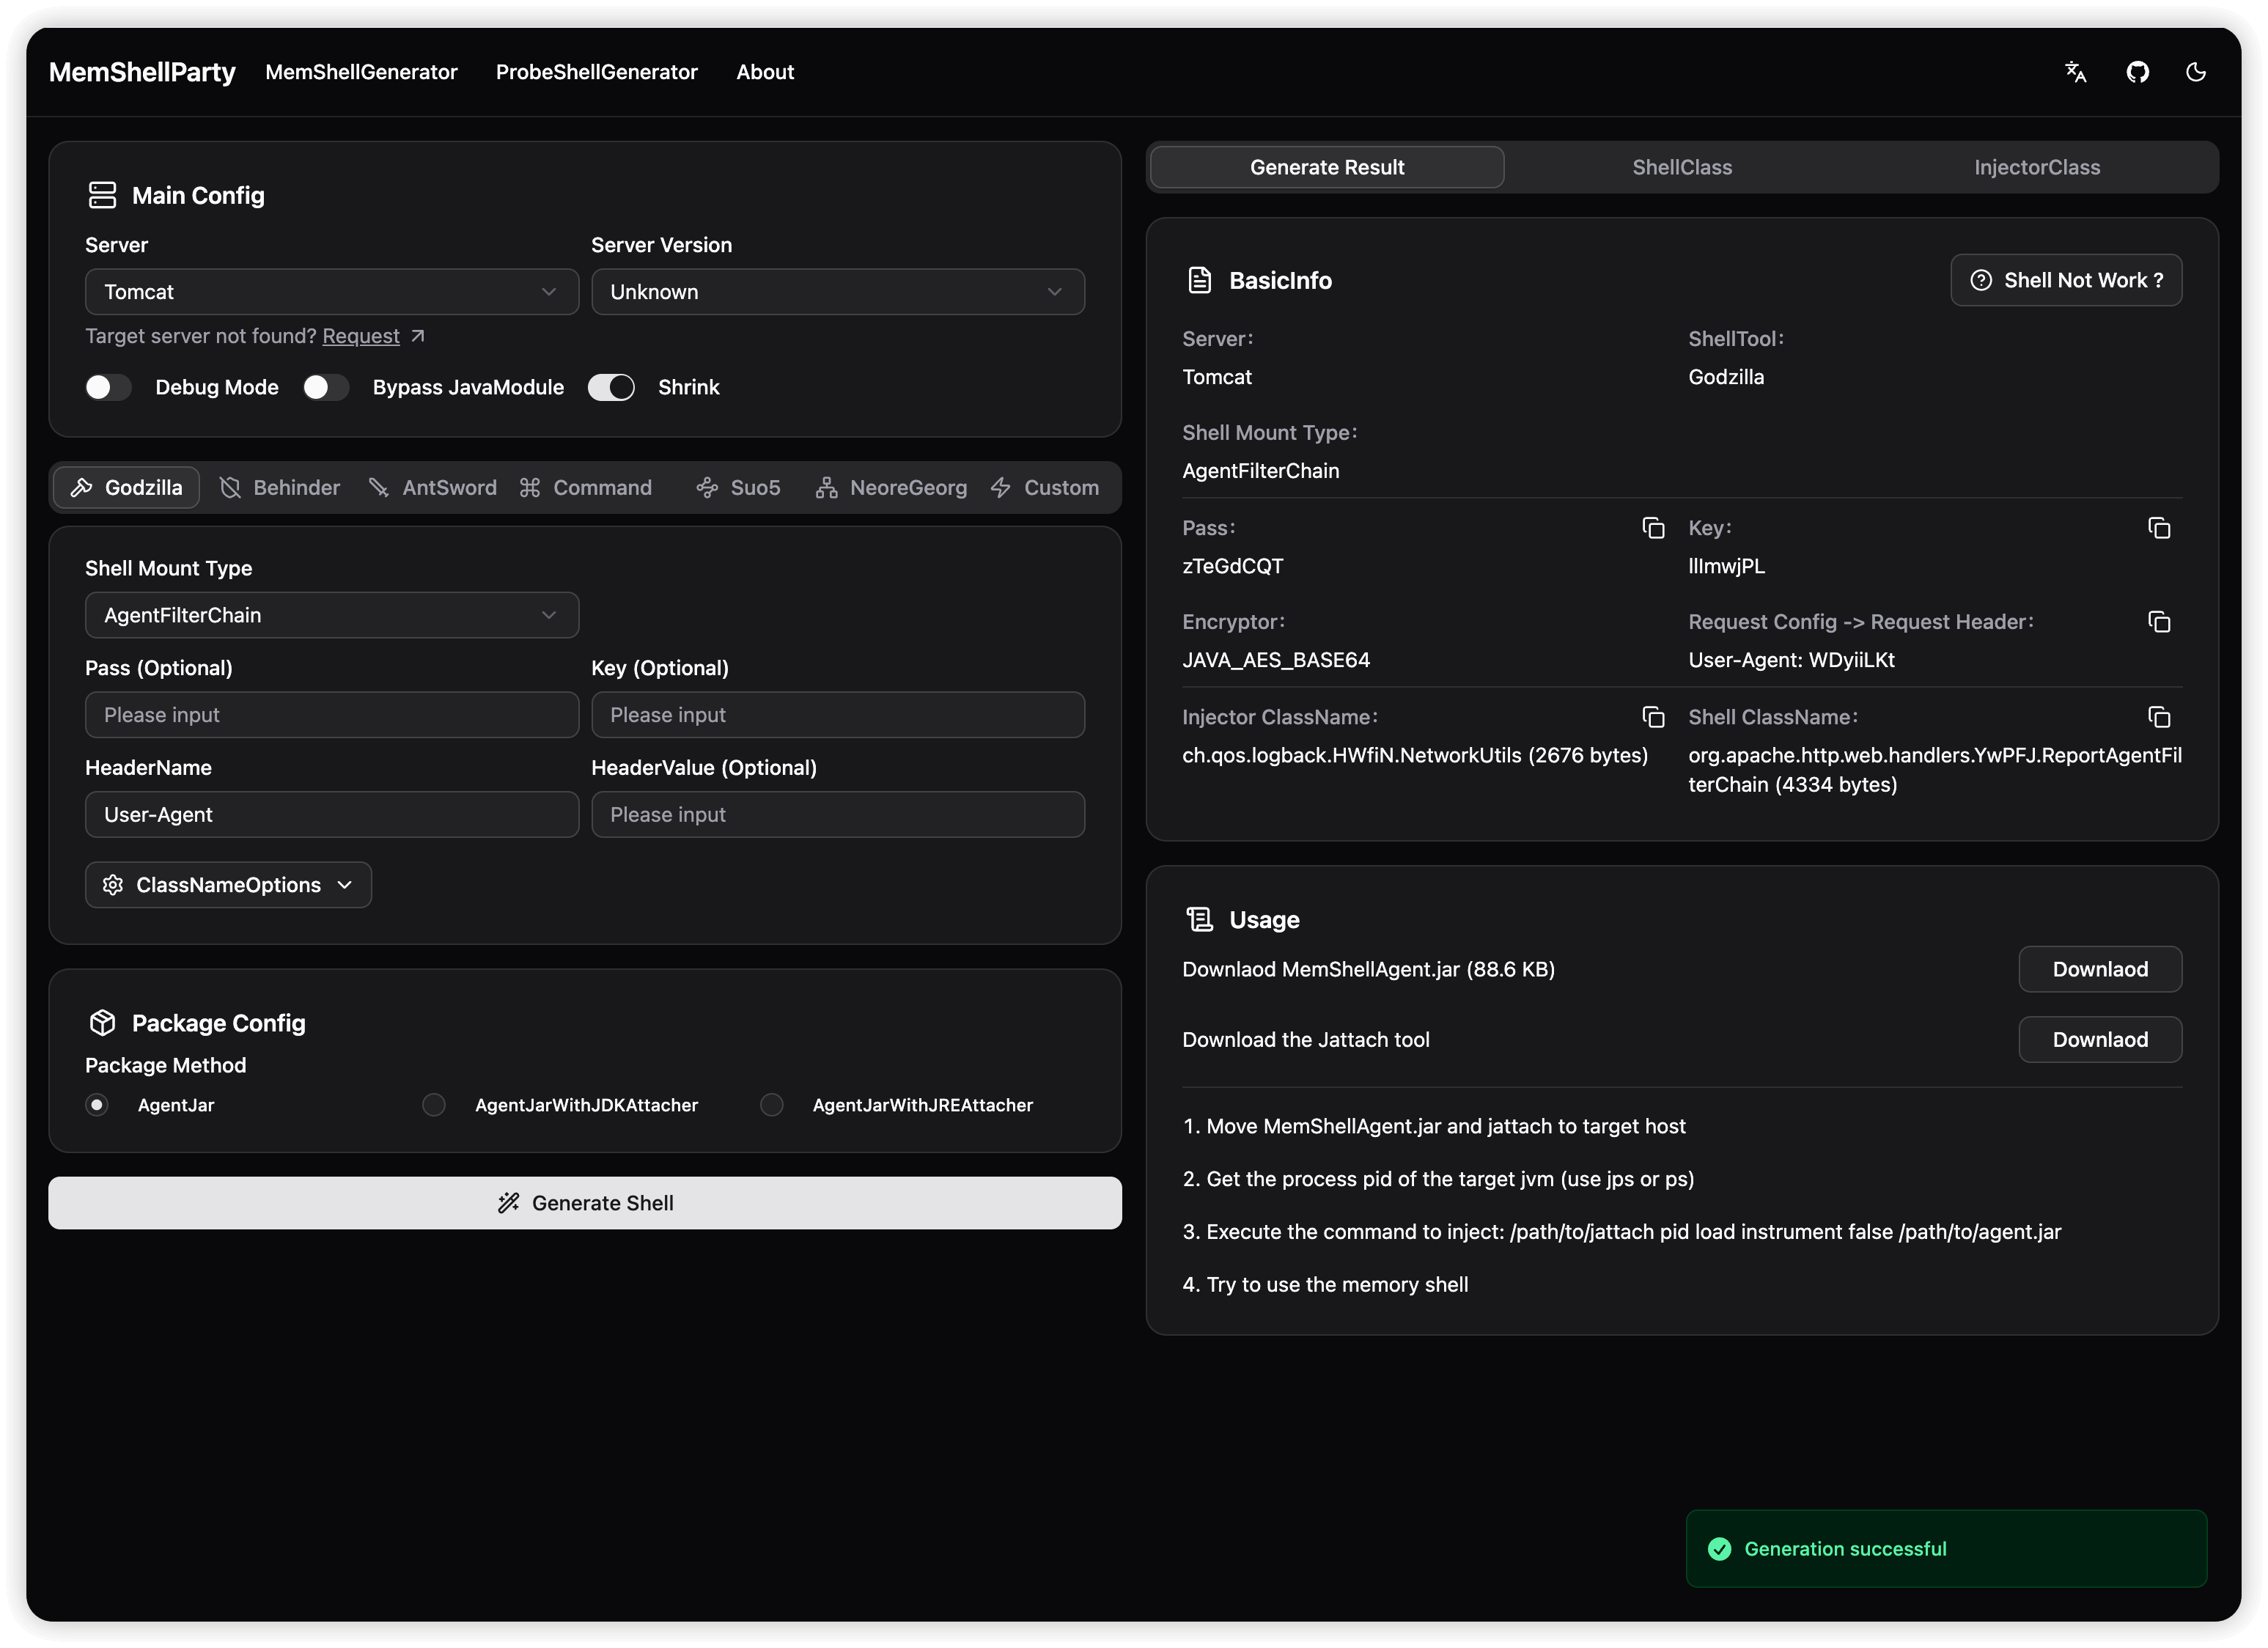 reajason/memshellparty
一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率
 x0rz/eqgrp
Decrypted content of eqgrp-auction-file.tar.xz
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 watchtowrlabs/watchtowr-vs-citrix-netscaler-preauth-rce-cve-2026-8452
CVE-2026-8452 PreAuth RCE
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 bishopfox/joro
A collaborative web exploitation framework.
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
 0xsha/cve-2026-6307
Google Chrome CVE-2026-6307 PoC
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
 devploit/put2win
Script to automate PUT HTTP method exploitation to get shell
 pimps/cve-2019-2725
WebLogic Insecure Deserialization - CVE-2019-2725 payload builder & exploit
 drac0nids/cve-2017-8570
## 在kali中自动化生成cve-2017-8570的恶意ppsx文件和配置msf监听
 kal1gh0st/cve-2021-40444_cab_archives
Custom CAB template generator for CVE-2021-40444, crafting malicious cabinet archives to exploit Windows MSHTML remote code execution via crafted…
 orangepirate/cve-2018-9948-9958-exp
a exp for cve-2018-9948/9958 , current shellcode called win-calc
 paulsery/cve-2021-30632
m-y-mo: https://github.com/github/securitylab/tree/main/SecurityExploits/Chrome/v8/CVE-2021-30632