metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode

Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)

Go package that aids in binary analysis and exploitation

SysWhispers on Steroids - AV/EDR evasion via direct system calls.

EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…

MCP Server for Metasploit

UNIX-like reverse engineering framework and command-line toolset.

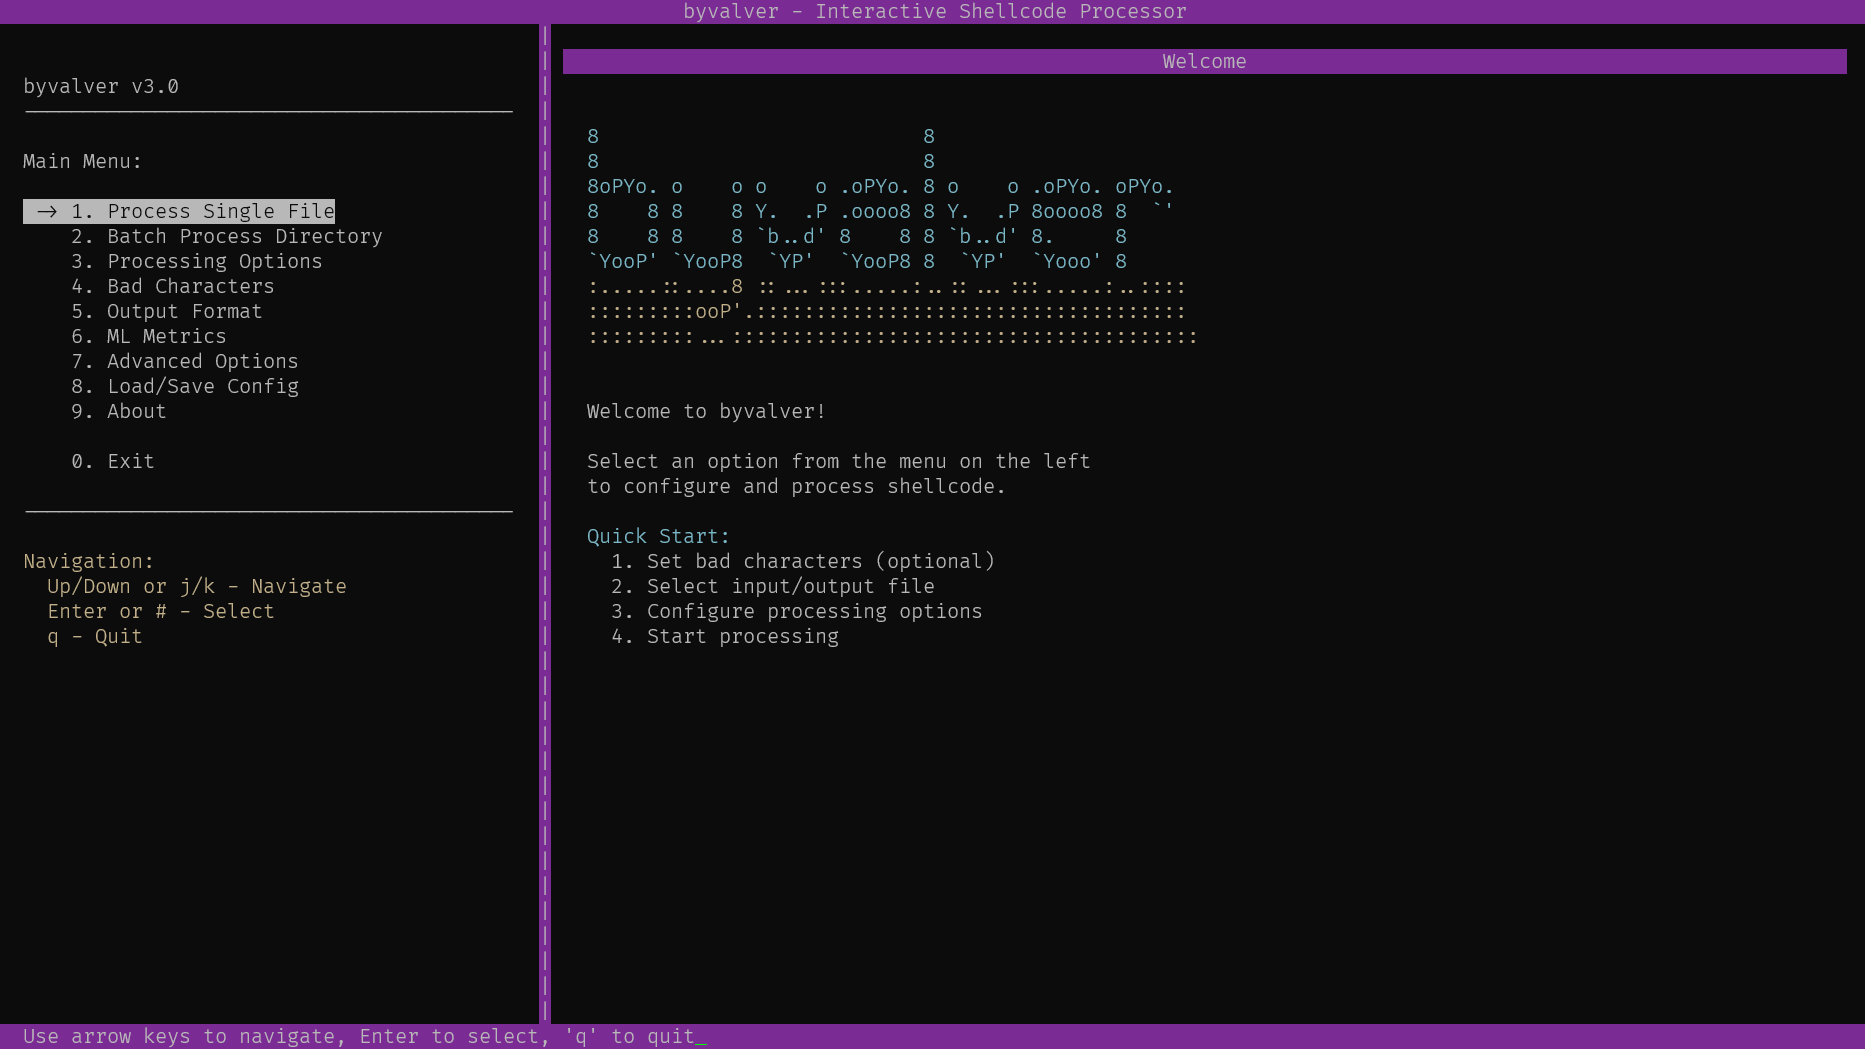
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities

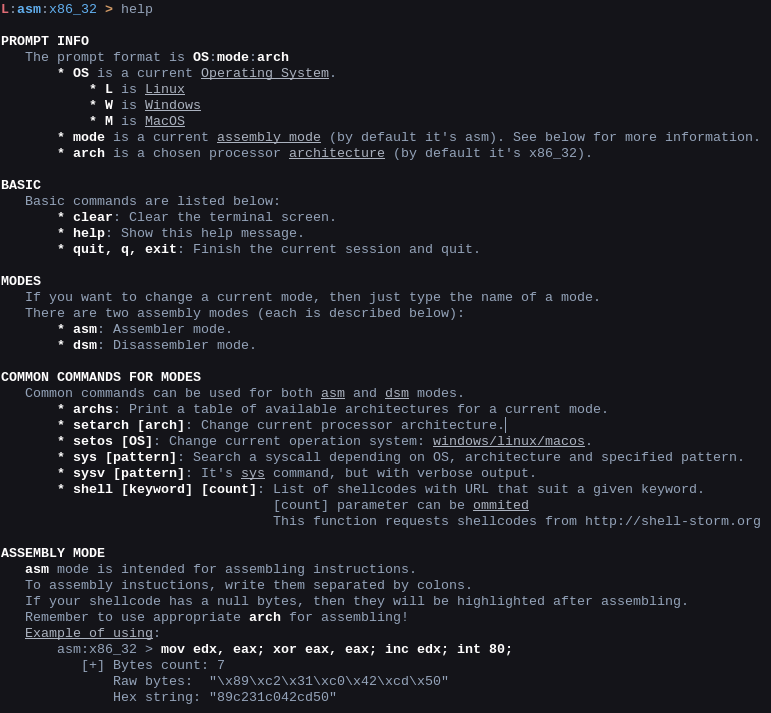
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes

Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment

The Havoc Framework

Shellcode injection using the Windows Debugging API

Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).

Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.