
windows-x86-shellcode-poc
 nataliadiak/windows-x86-shellcode-poc
Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
binary-exploitationeducationpayload-development+3
8
nataliadiak/windows-x86-shellcode-pocWindows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
 pelock/simple-polymorphic-engine-spe32
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 0xhossam/killer
Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
 sysdream/hershell
Hershell is a simple TCP reverse shell written in Go.
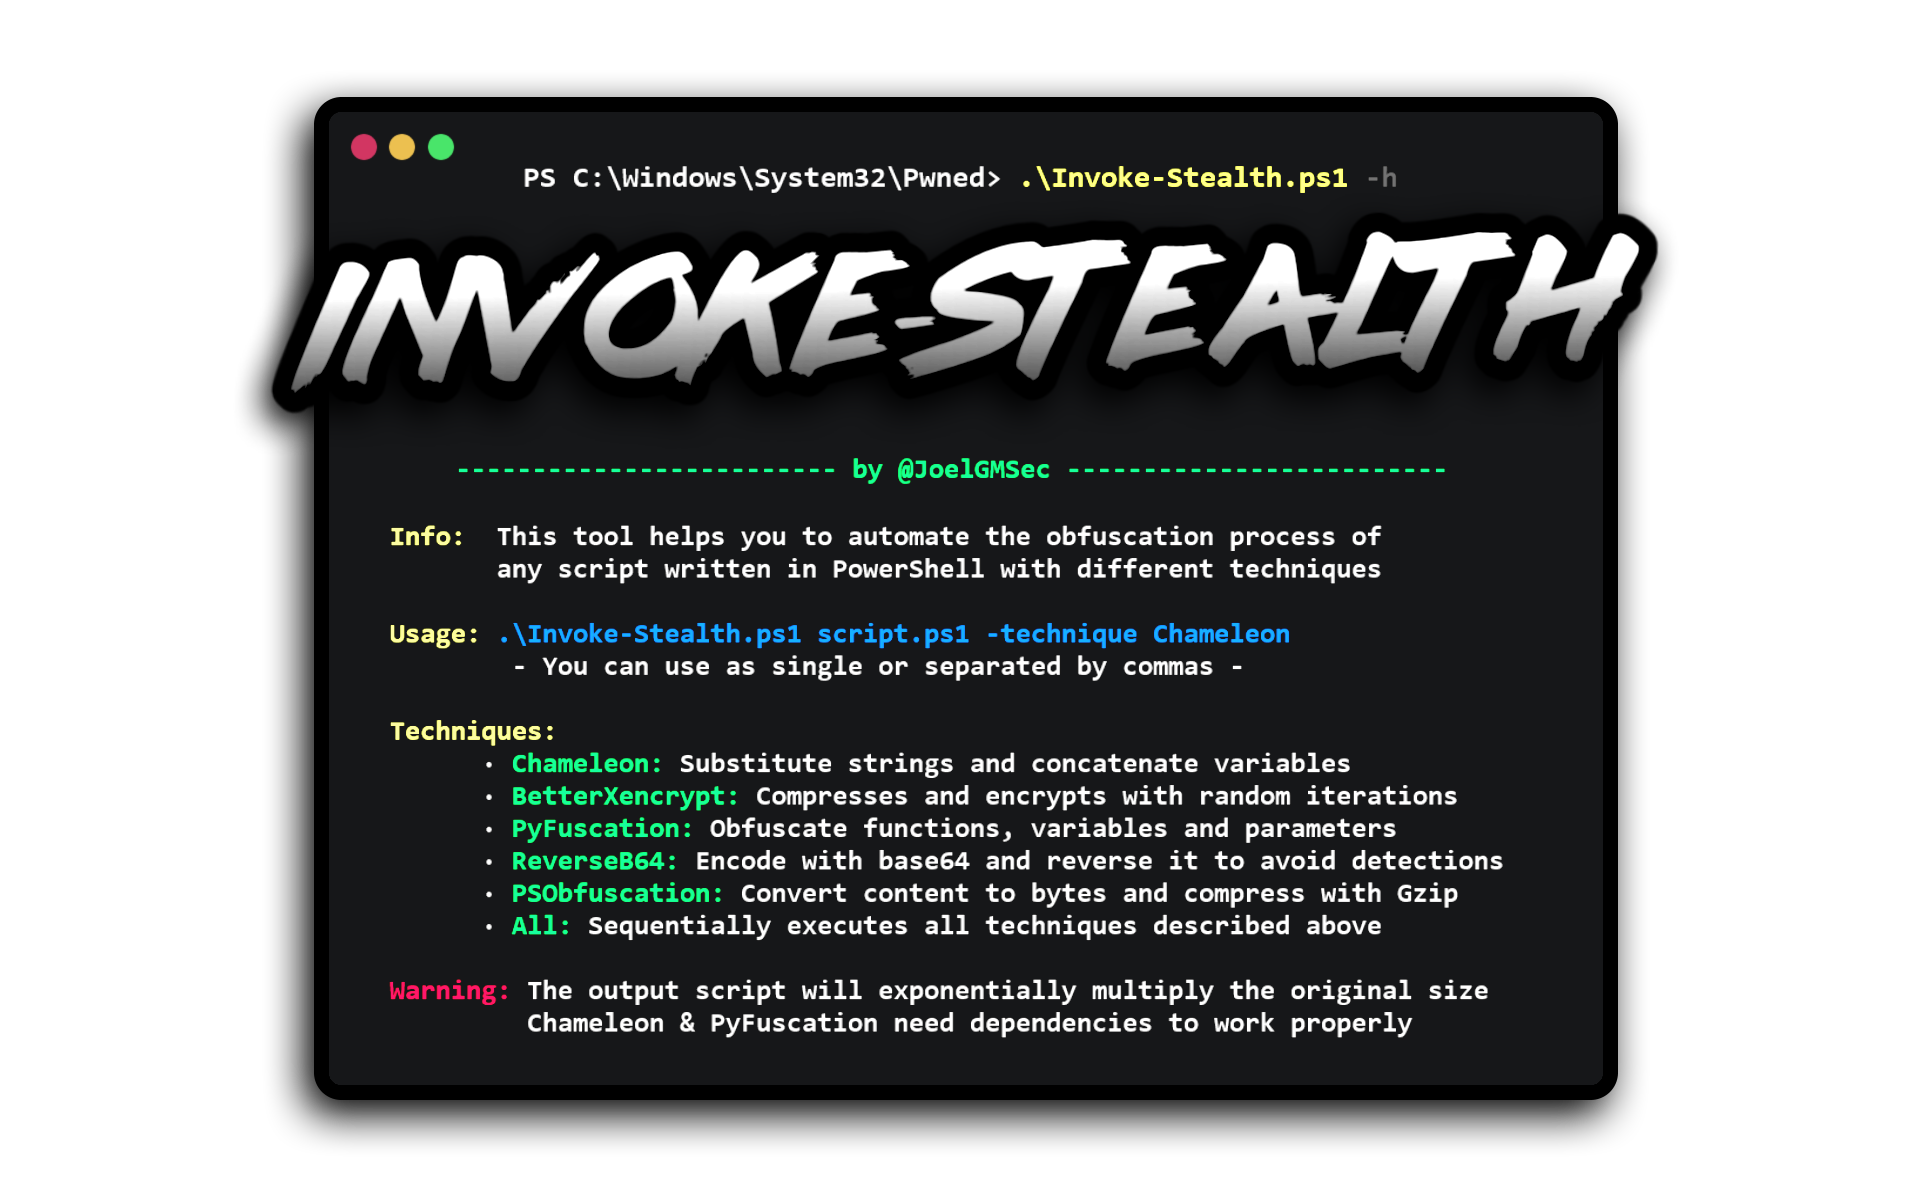 joelgmsec/invoke-stealth
Simple & Powerful PowerShell Script Obfuscator
 tokyoneon/armor
Armor is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners.
 plackyhacker/shellcode-encryptor
A simple shell code encryptor/decryptor/executor to bypass anti virus.
 saadahla/shellcode-hide
This repo contains : simple shellcode Loader , Encoders (base64 - custom - UUID - IPv4 - MAC), Encryptors (AES), Fileless Loader (Winhttp, socket)
 soledad208/cve-2018-10933
CVE-2018-10933 very simple POC
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 aniqfakhrul/sharperner
Simple executable generator with encrypted shellcode.
 hatriot/shellme
simple shellcode generator
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 enkomio/brokenflow
A simple PoC to invoke an encrypted shellcode by using an hidden call
 nbaertsch/nimvoke
Indirect syscalls + DInvoke made simple.
 dump-guy/sc2pe
Simple dotnet Native AOT app that uses AsmResolver to convert shellcode to PE