
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
863 results
BadKernel preview

BadKernel

GitHubsecmob/badkernel

Full exploit of CVE-2016-6754(BadKernel) and slide of SyScan360 2016

binary-exploitationexploitationpayload-development+3
1519 years ago
tools preview

tools

GitHubnullsecuritynet/tools

Curated collection of security tools, exploits, proof-of-concept code, shellcodes, and scripts for penetration testing and educational offensive…
curated-resourceseducationexploitation+5
7220 days ago
ROP_ROCKET preview

ROP_ROCKET

GitHubbw3ll/rop_rocket

ROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…
binary-exploitationexploitationexploit-frameworks+4
17311 months ago
Project-Onyx preview

Project-Onyx

GitHubx-3306/project-onyx

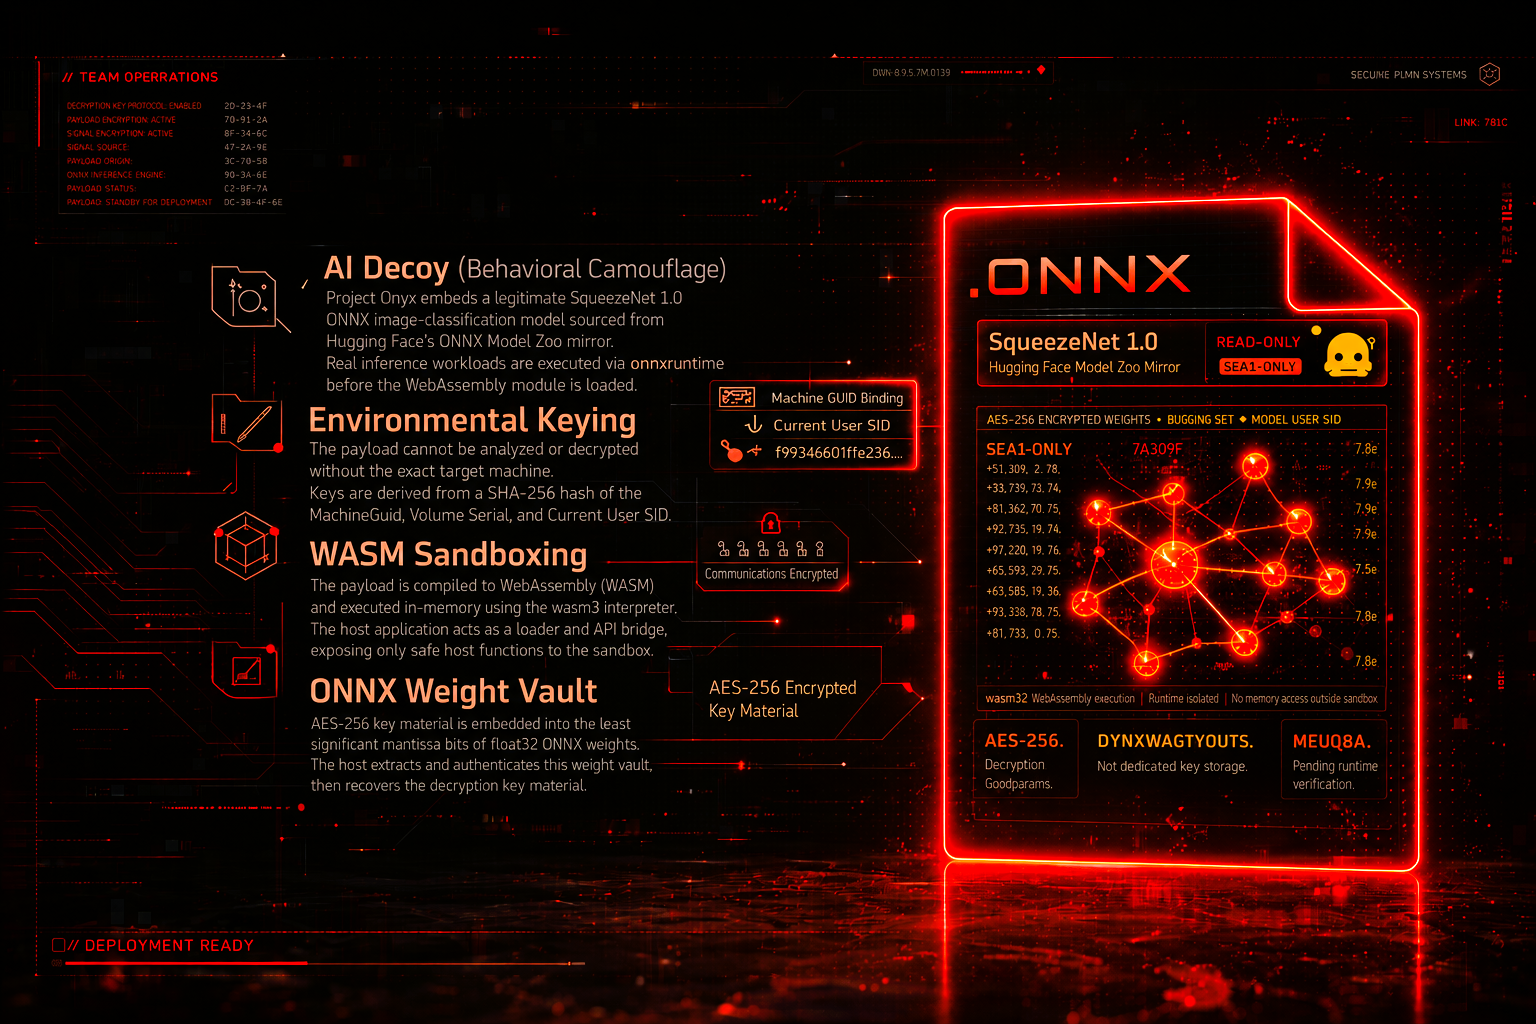
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…

ai-securitycommand-and-controlcryptography+6
1151 month ago
TinyLoad preview

TinyLoad

GitHubiamsopotatoe-coder/tinyload

Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
1802 months ago
DuplexSpyCS preview

DuplexSpyCS

GitHubiss4cf0ng/duplexspycs

An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
command-and-controleducationpayload-development+5
2178 months ago
ICMP-Ghost-A-Fileless-x64-Assembly-C2-Agent preview

ICMP-Ghost-A-Fileless-x64-Assembly-C2-Agent

GitHubjm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent

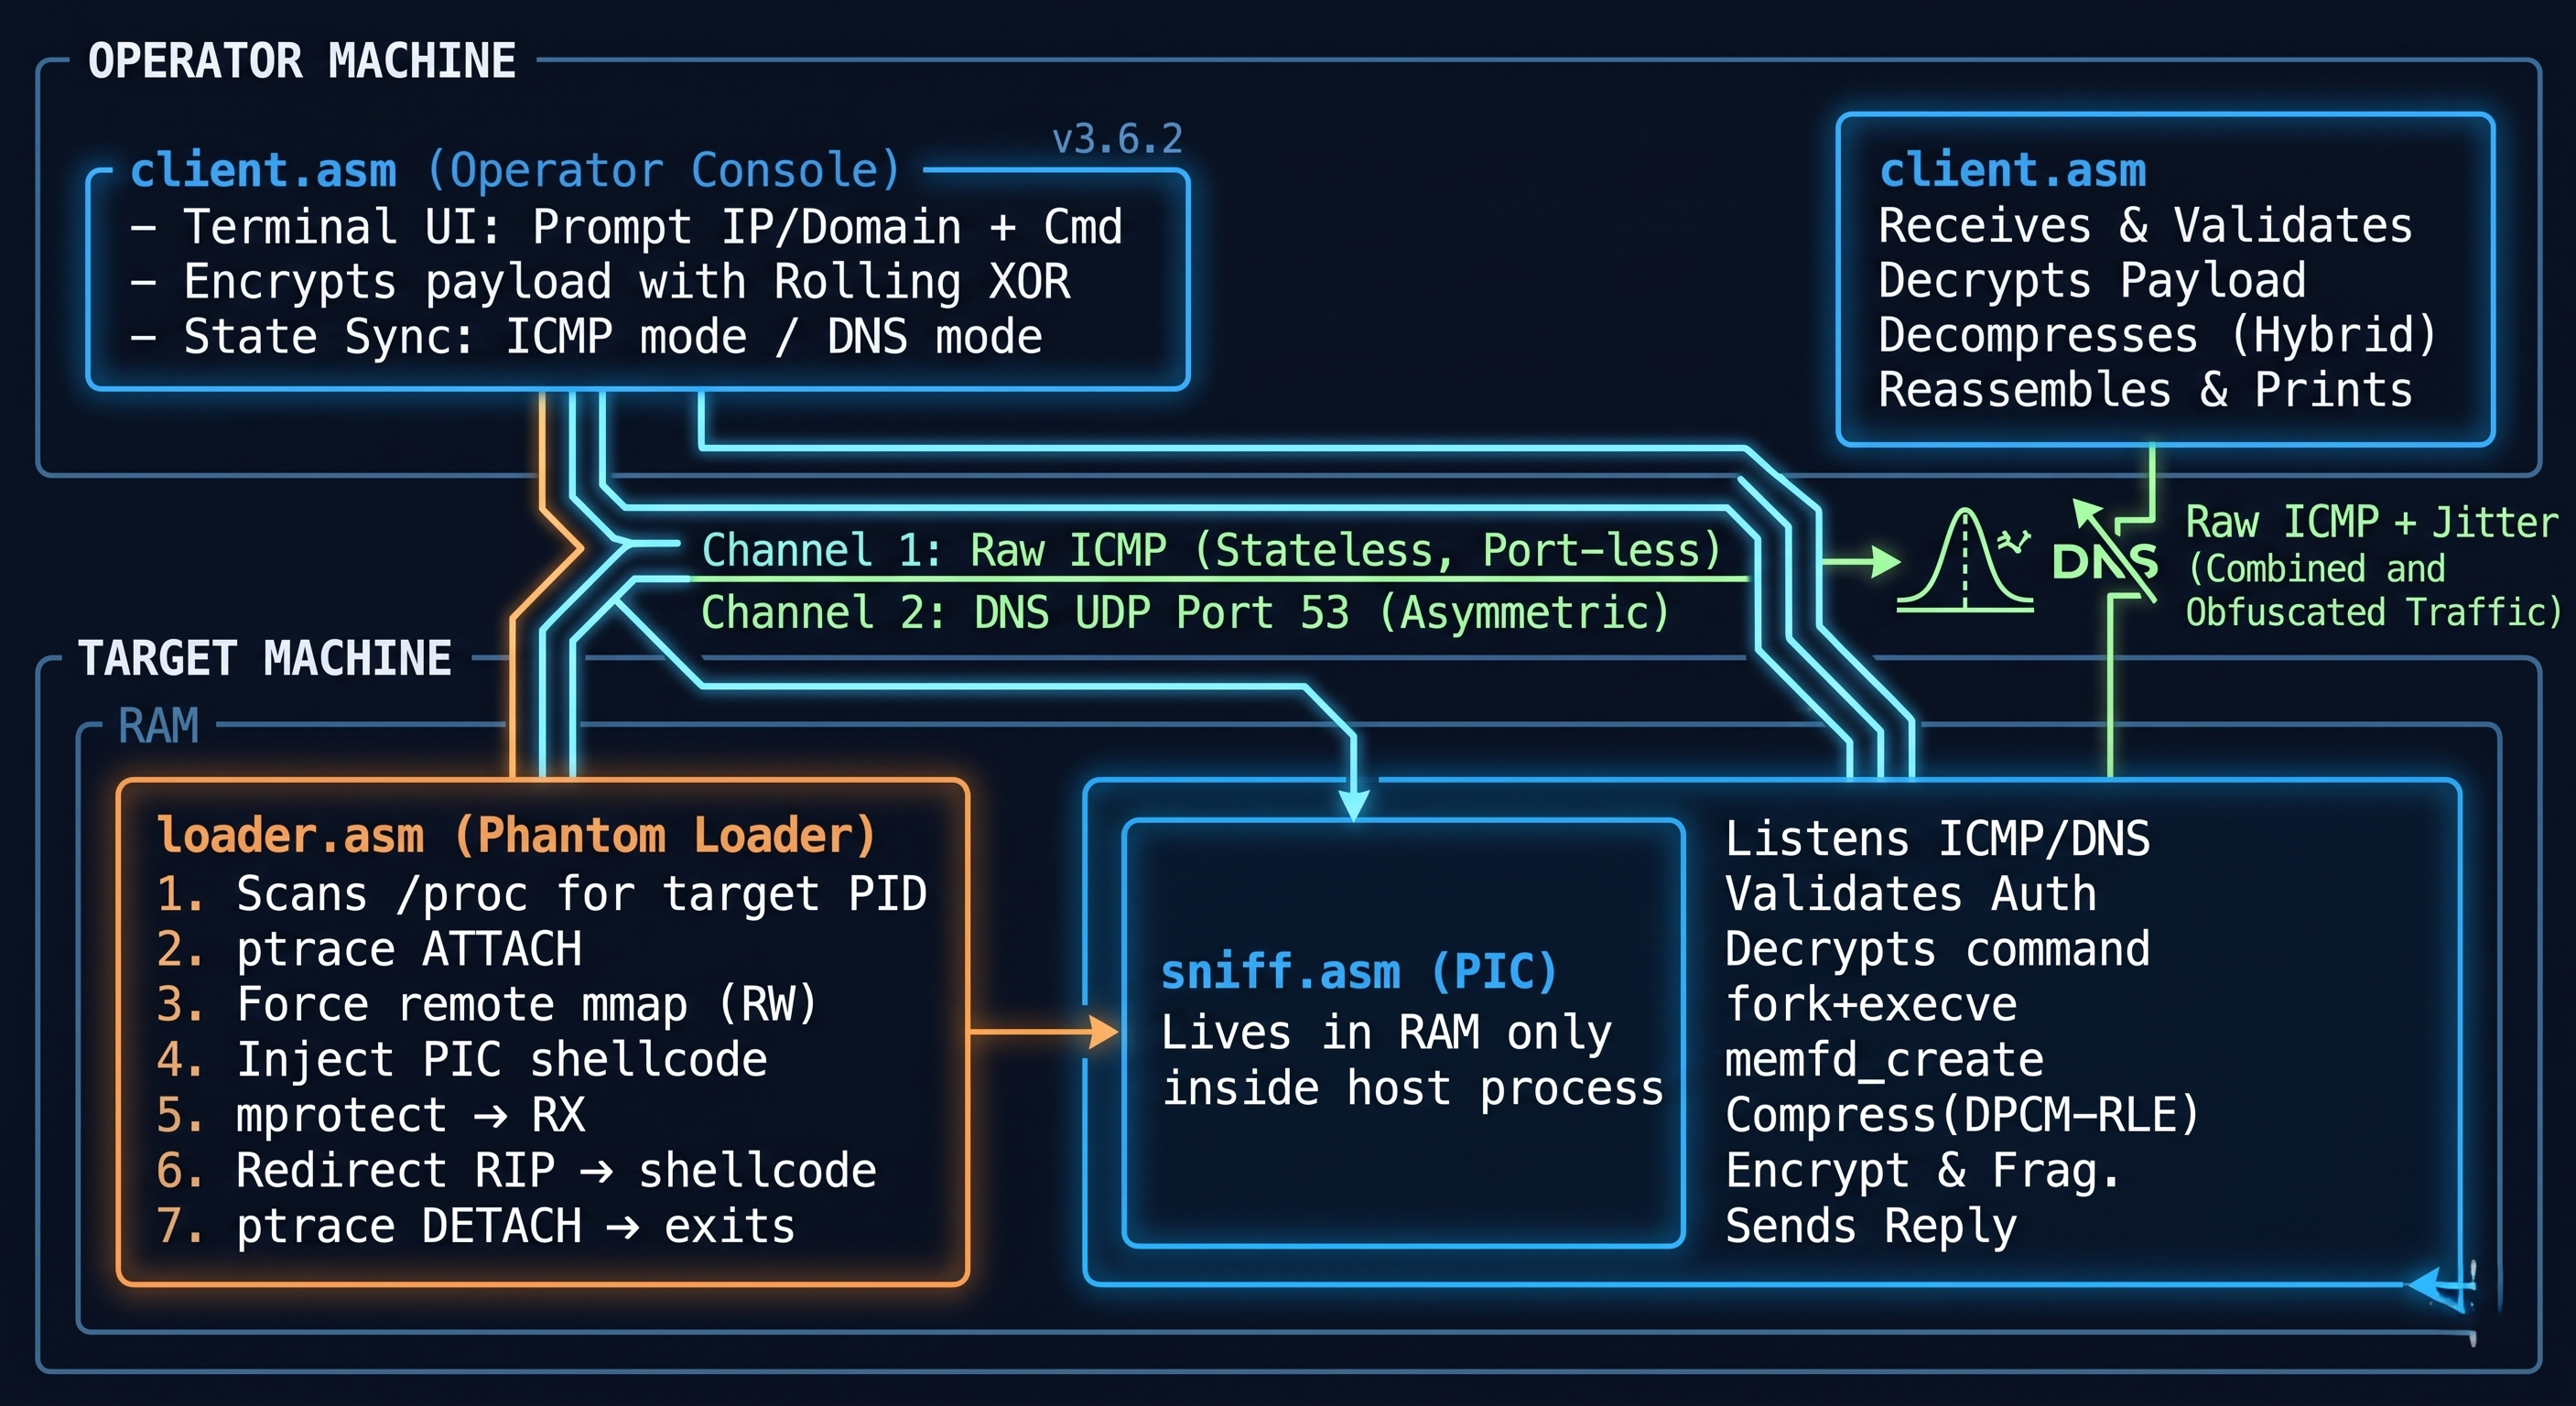
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…
command-and-controlexploit-frameworksids-ips-evasion+5
881 month ago
hackEmbedded preview

hackEmbedded

GitHubdoudoudedi/hackembedded

This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices

command-and-controlembedded-systems-securityencryption-decryption-tools+8
2073 months ago
ntqueueapcthreadex-ntdll-gadget-injection preview

ntqueueapcthreadex-ntdll-gadget-injection

GitHublloydlabs/ntqueueapcthreadex-ntdll-gadget-injection

This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
adversarial-attackids-ips-evasionpayload-development+3
2663 years ago
SynthAPT preview

SynthAPT

GitHubacedef/synthapt

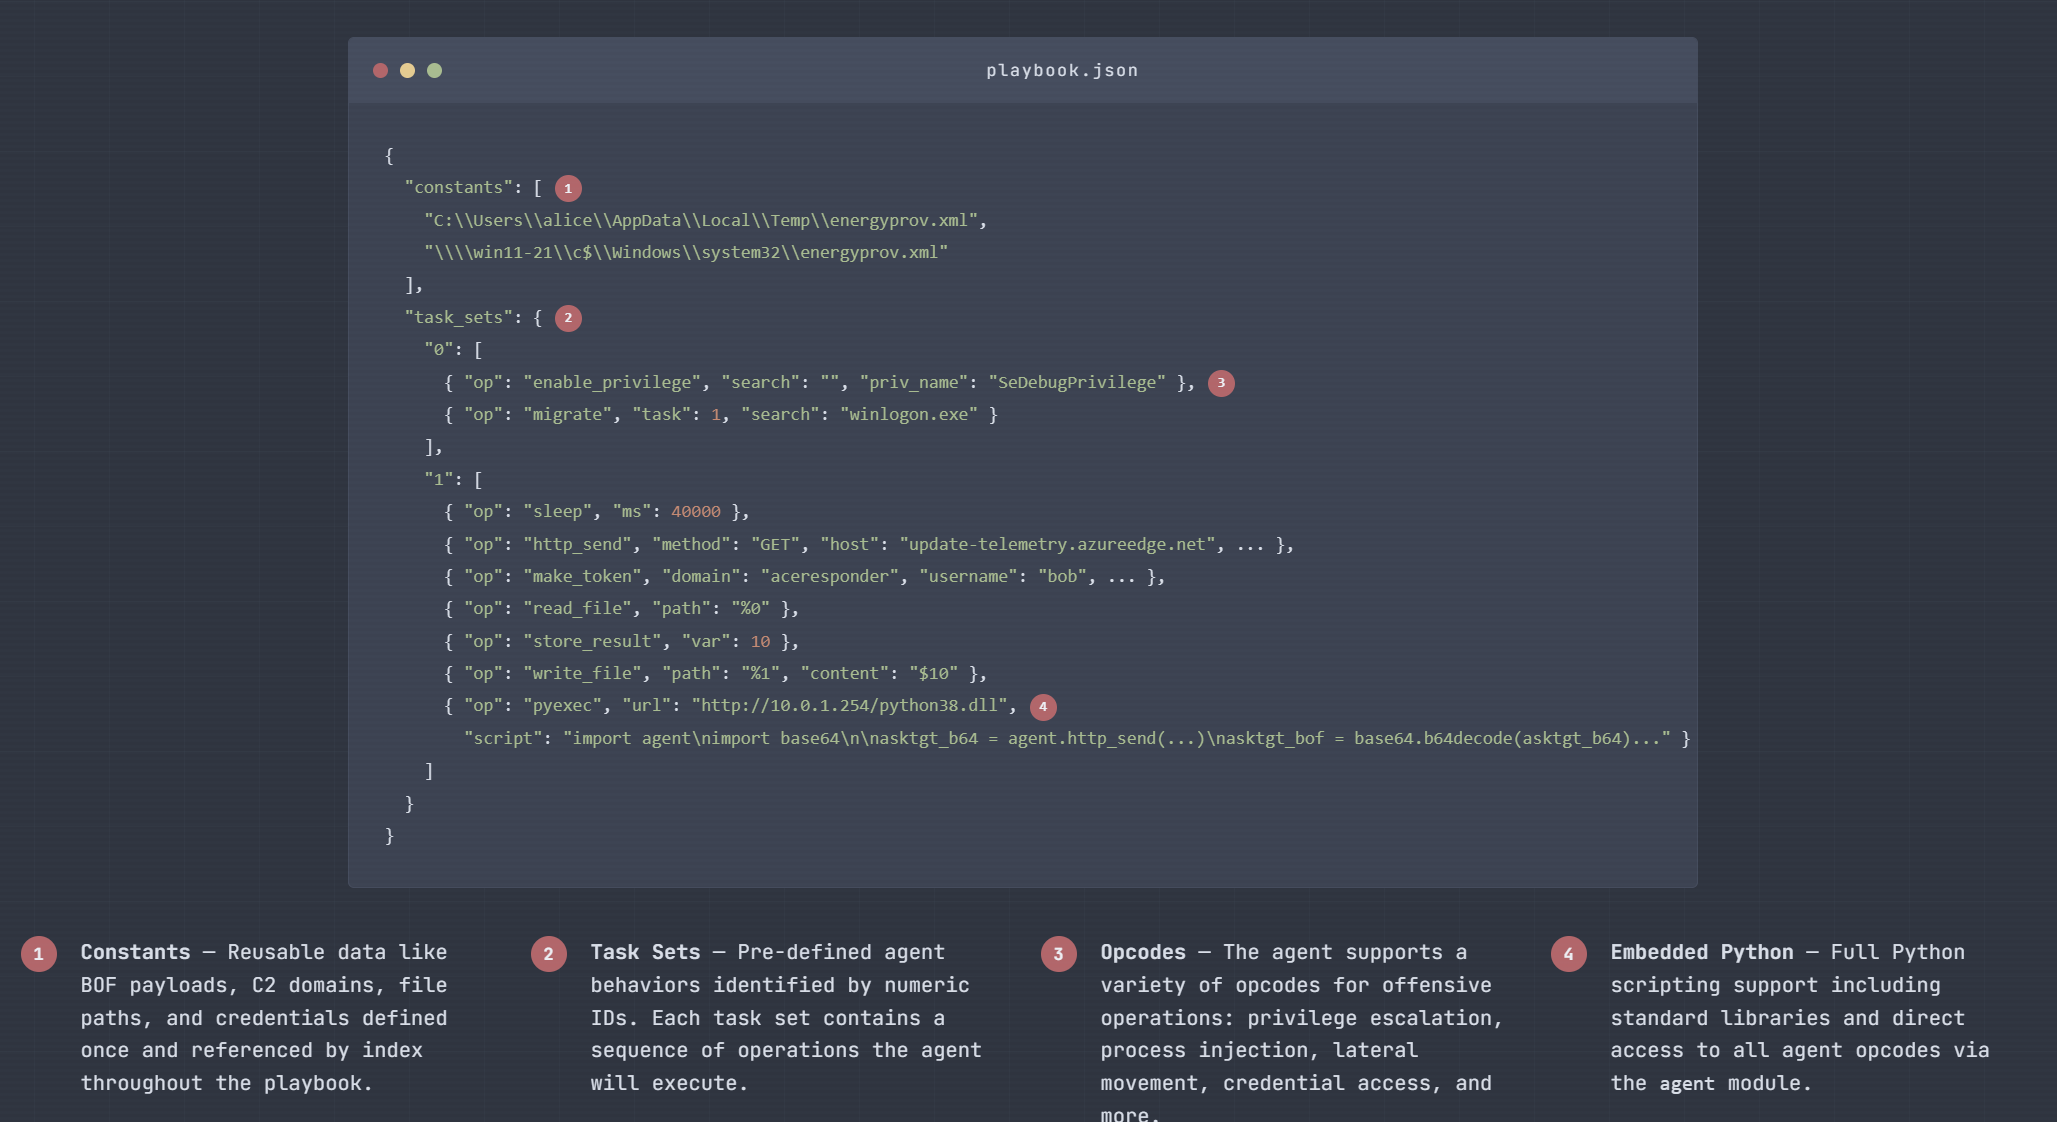
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
adversarial-attackai-securitycommand-and-control+8
2316 months ago
Simple-Polymorphic-Engine-SPE32 preview

Simple-Polymorphic-Engine-SPE32

GitHubpelock/simple-polymorphic-engine-spe32

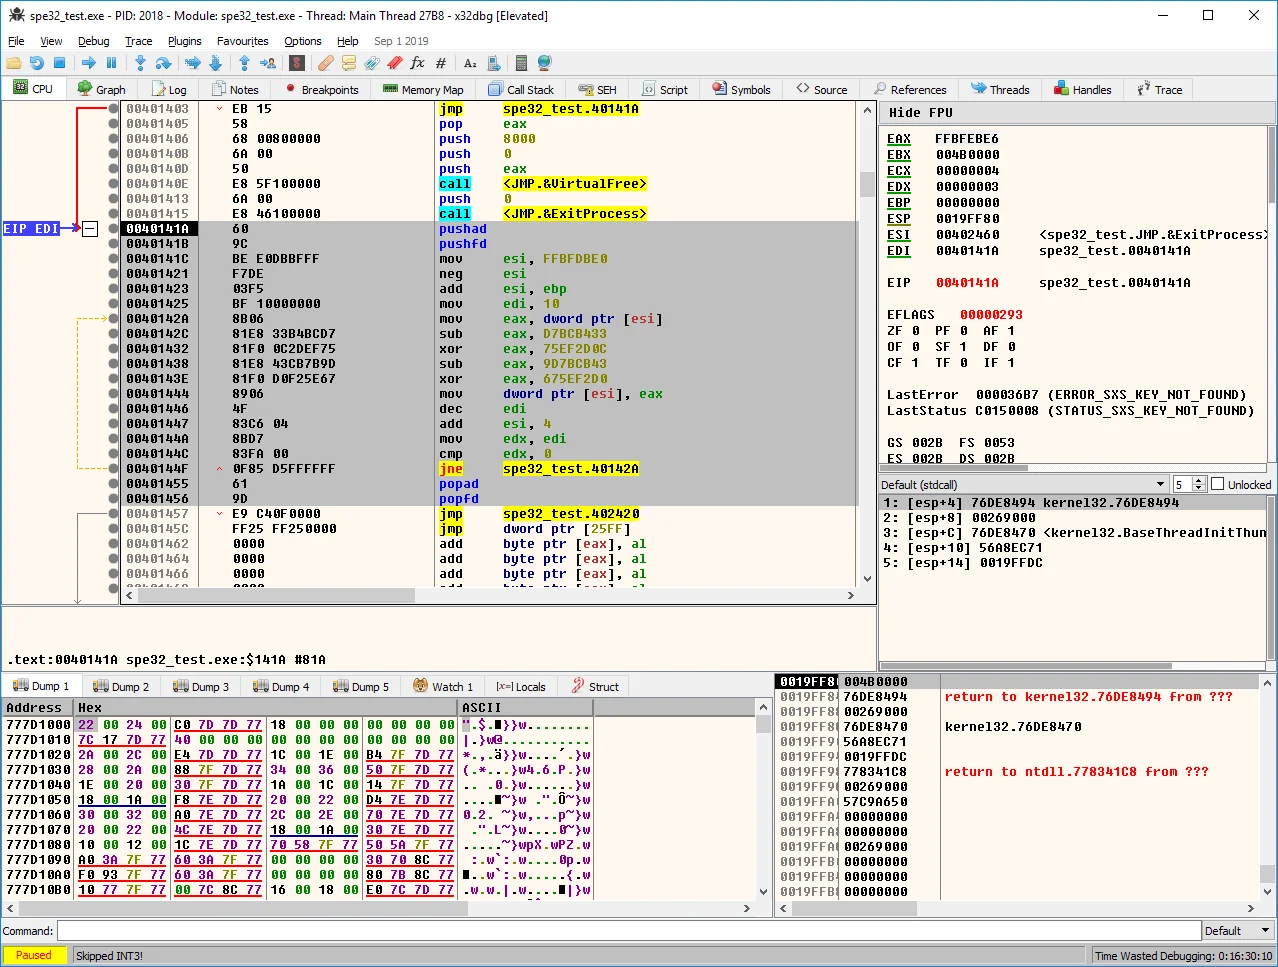
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…
encryption-decryption-toolsmalware-analysisreverse-engineering+1
1603 years ago
dropengine preview

dropengine

GitHubs0lst1c3/dropengine

DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…

defensive-toolsexploit-frameworkspayload-development+5
2125 years ago
RustyWater-ShellCode-Dropper preview

RustyWater-ShellCode-Dropper

GitHubs3n4t0r-0x0/rustywater-shellcode-dropper

RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
binary-exploitationcommand-and-controlexploitation+9
1043 months ago
Phantom-Evasion-Loader preview

Phantom-Evasion-Loader

GitHubjm00nj/phantom-evasion-loader

x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…

binary-exploitationcommand-and-controleducation+6
1103 months ago
ByteCaster preview

ByteCaster

GitHubprint3m/bytecaster

Swiss Army Knife for payload encryption, obfuscation, and conversion to byte arrays – all in a single command (14 output formats supported)! ☢️
encryption-decryption-toolspayload-developmentred-teaming+1
2298 months ago
CVE-2024-6387 preview

CVE-2024-6387

GitHubl0n3m4n/cve-2024-6387

PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit)

exploitationnetwork-securitypayload-development+6
1132 years ago
sploit preview

sploit

GitHubzznop/sploit

Go package that aids in binary analysis and exploitation
binary-analysisbinary-exploitationctf+6
1805 years ago
asminject preview

asminject

GitHubbishopfox/asminject

Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…

container-escapepayload-developmentpenetration-testing+2
1484 years ago
Previous1…456…48Next