
CVE-2023-4911
 guffre/cve-2023-4911
Python-based proof-of-concept exploit for CVE-2023-4911 (Looney Tunables) targeting glibc dynamic loader's parse_tunables() for local privilege…
binary-exploitationexploitationpayload-development+3
guffre/cve-2023-4911Python-based proof-of-concept exploit for CVE-2023-4911 (Looney Tunables) targeting glibc dynamic loader's parse_tunables() for local privilege…
 nobodyatall648/cve-2009-0182
CVE-2009-0182 VUPlayer2.49_LocalBufferOverflow
 0vercl0k/cve-2019-9810
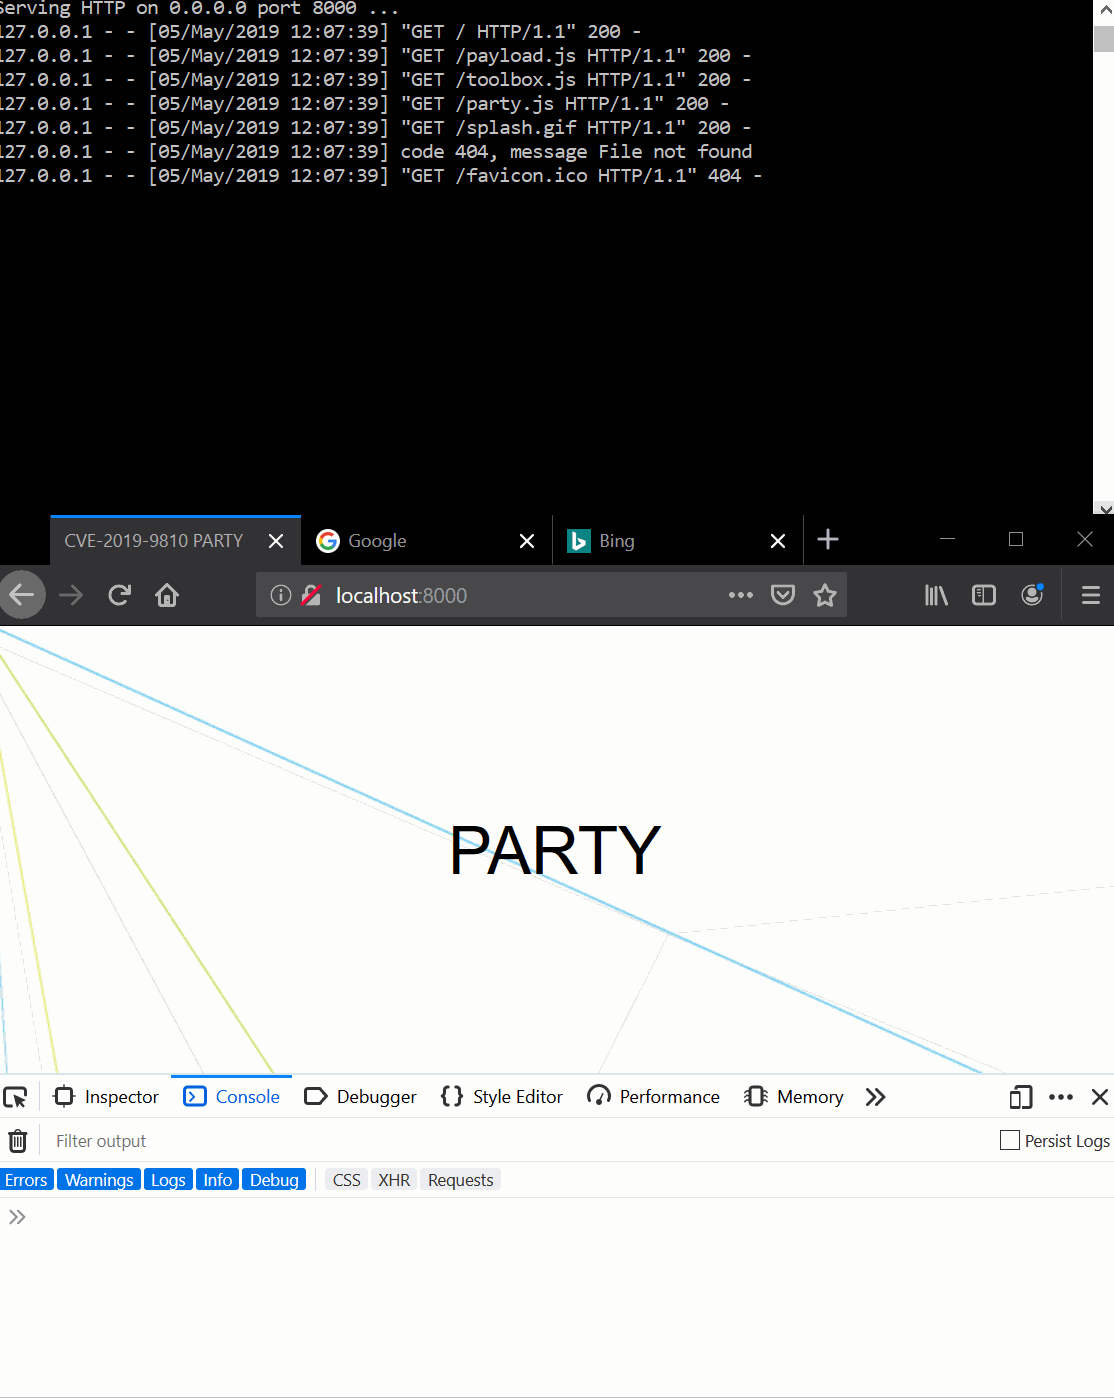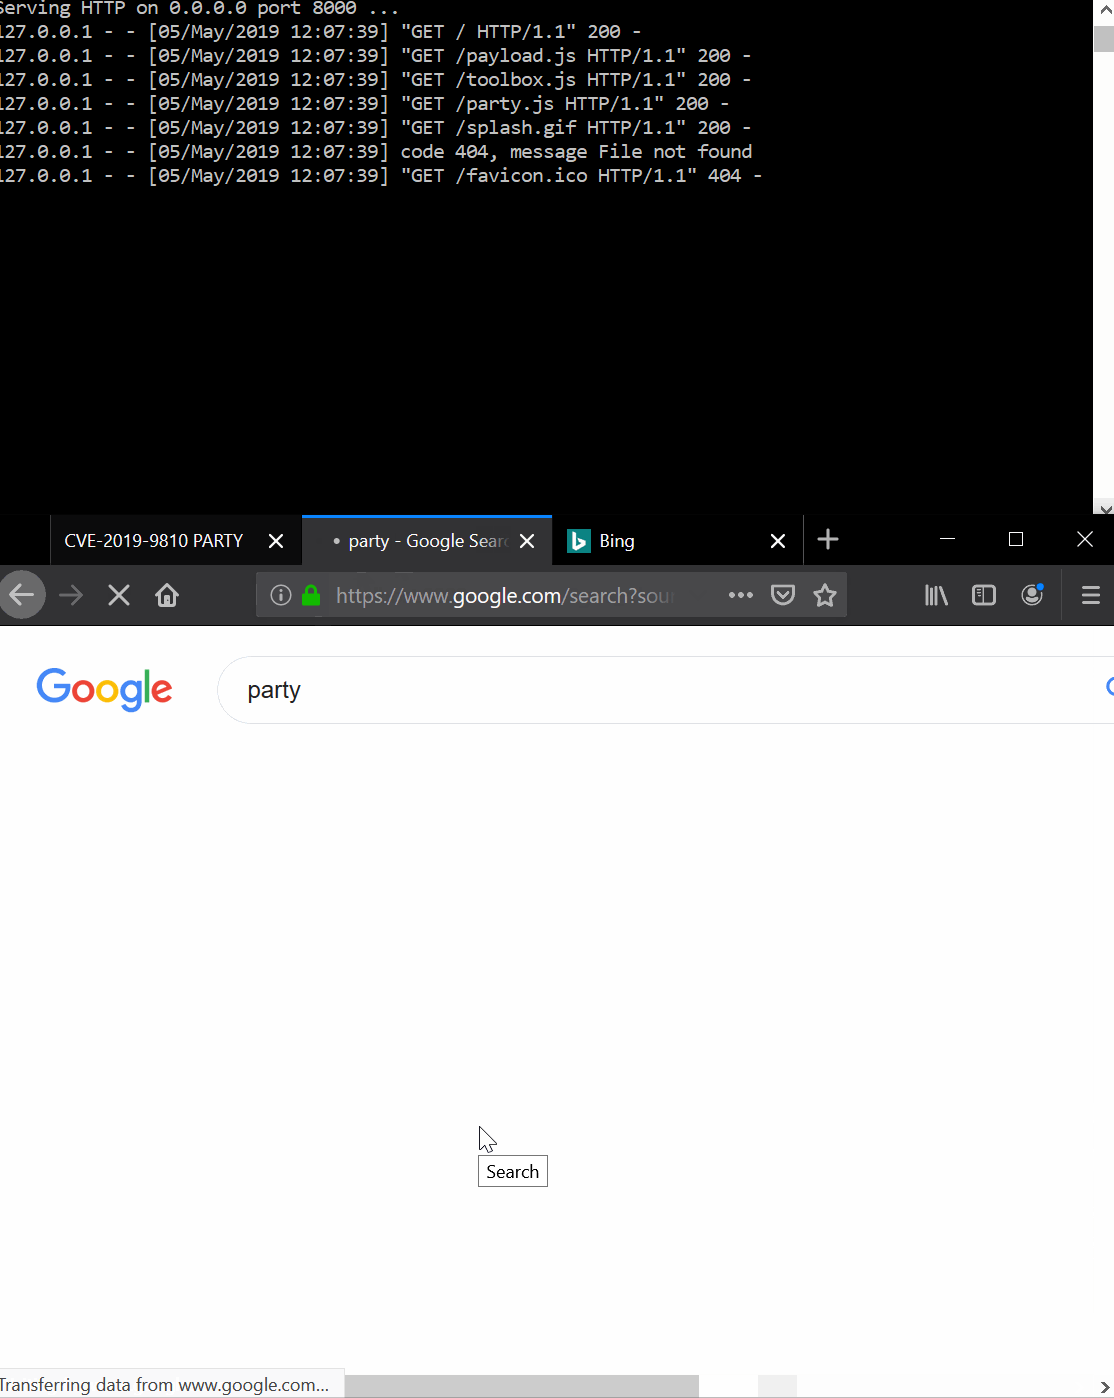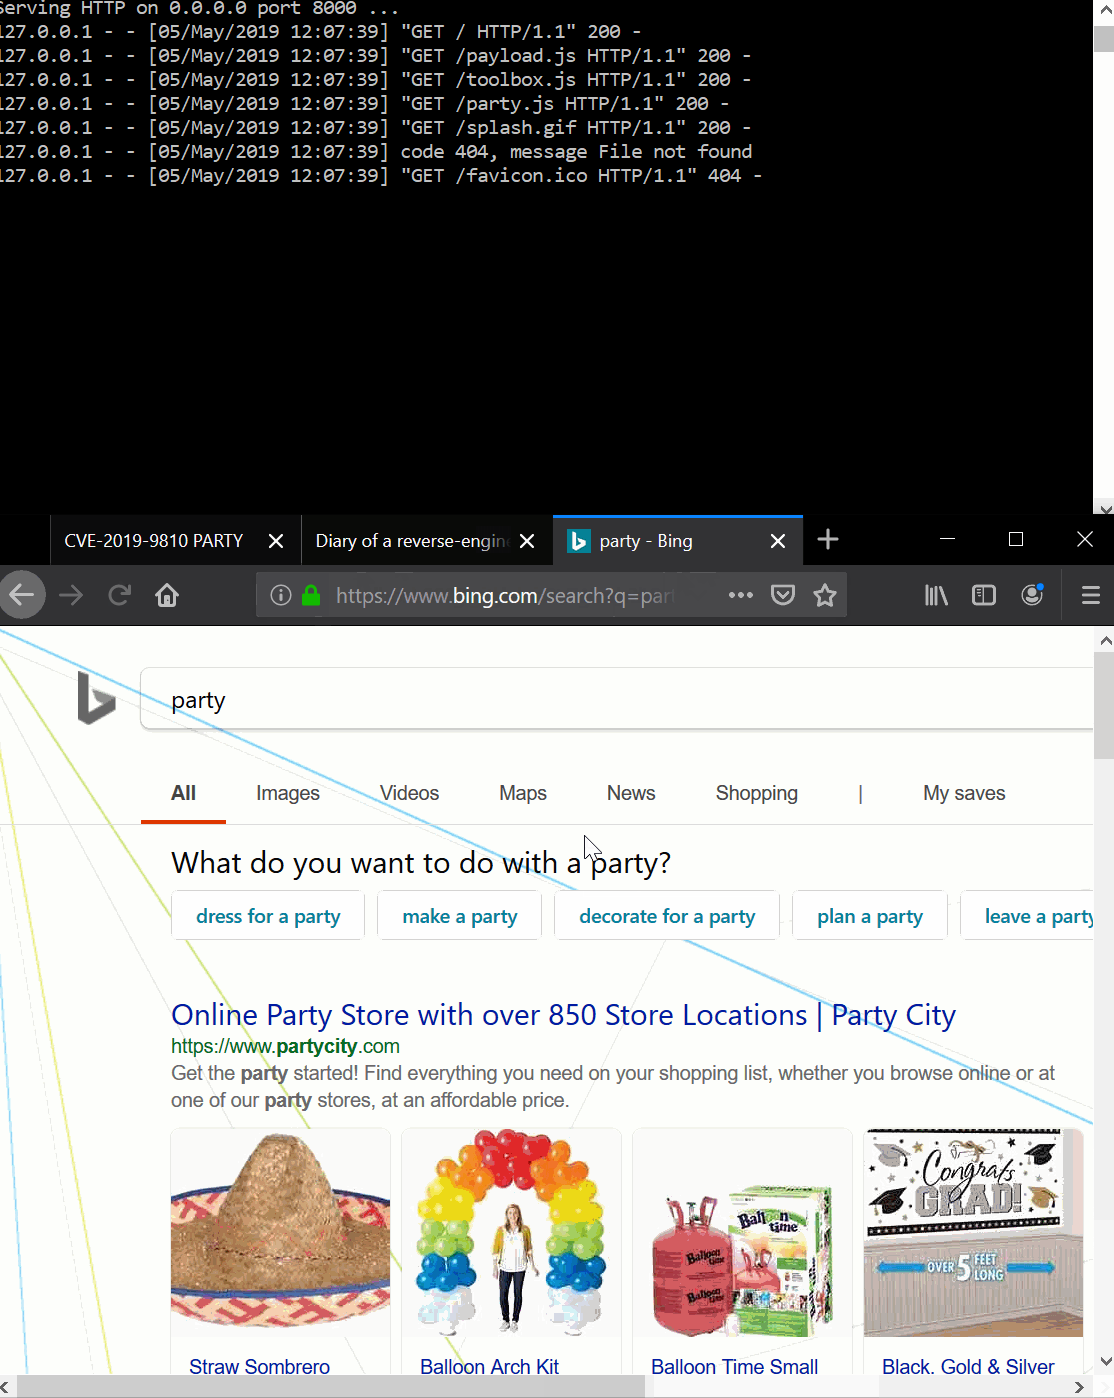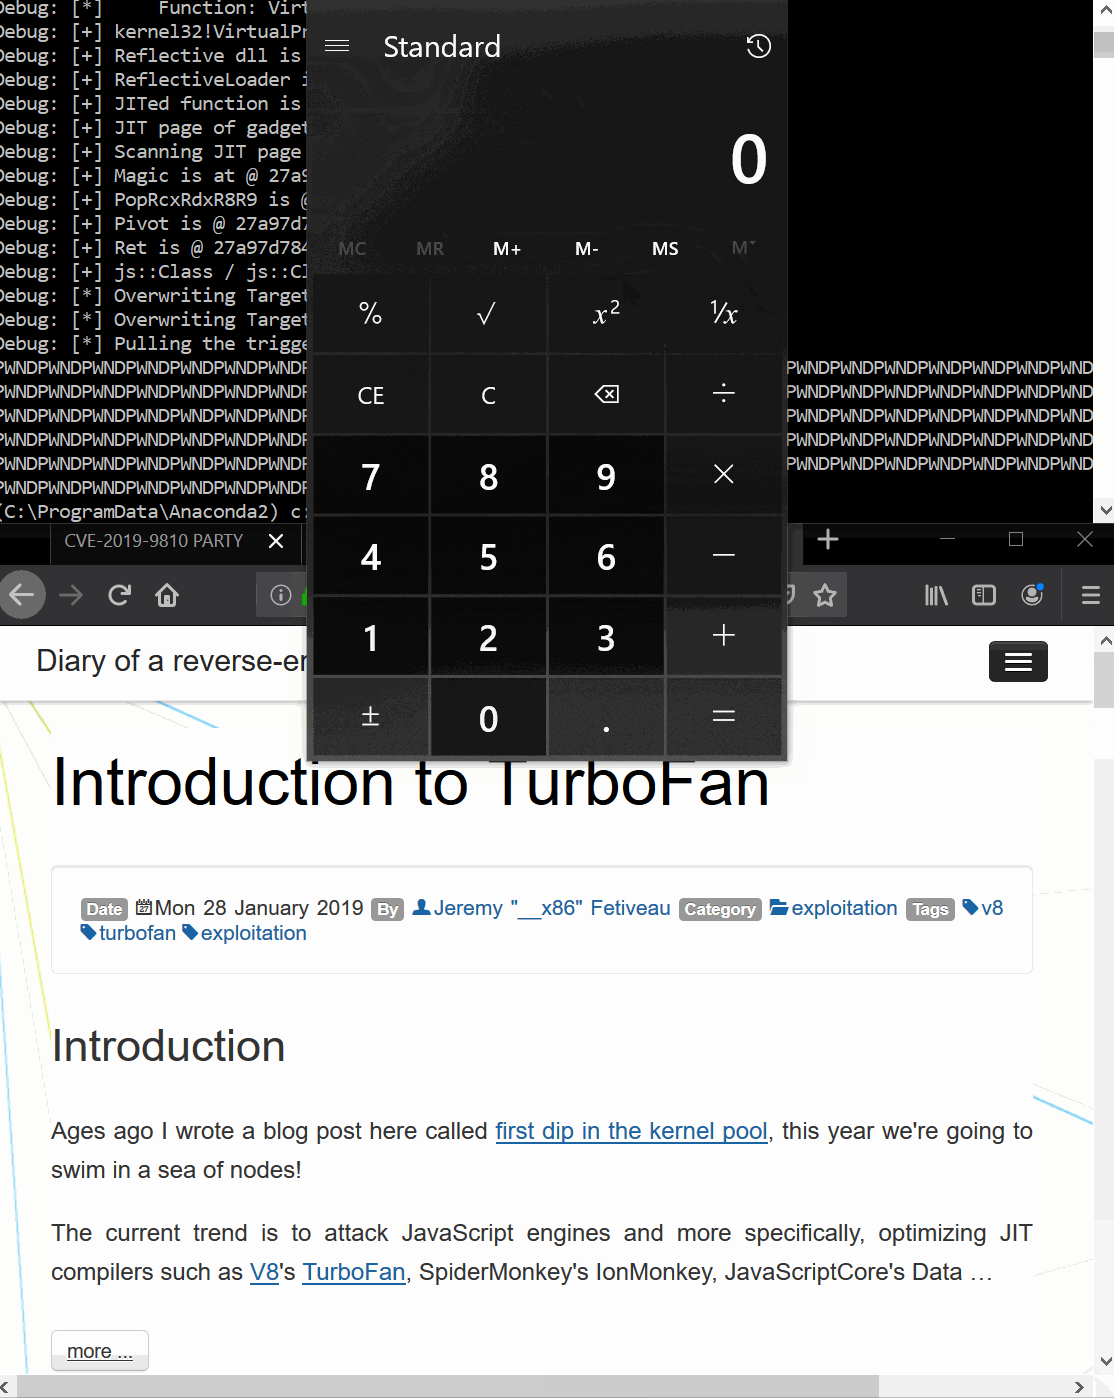
Exploit for CVE-2019-9810 Firefox on Windows 64-bit.
 hfiref0x/kdu
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
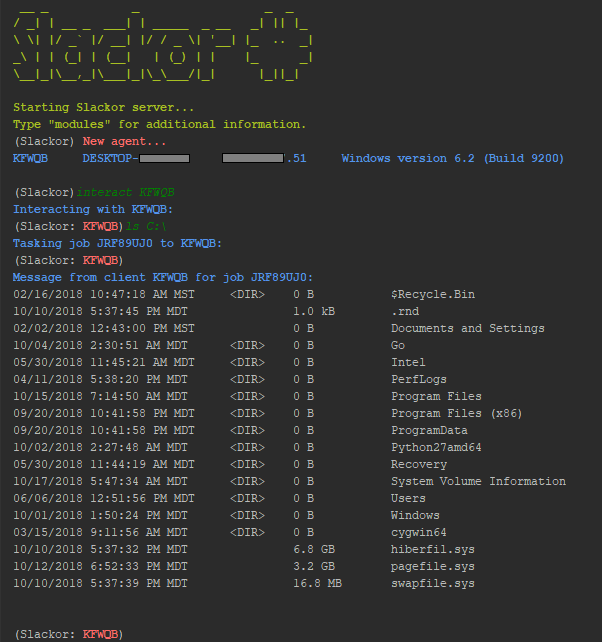 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
 machine1337/gmailc2
A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions
 peterferrie/win-exec-calc-shellcode
A small, null-free Windows shellcode that executes calc.exe (x86/x64, all OS/SPs)
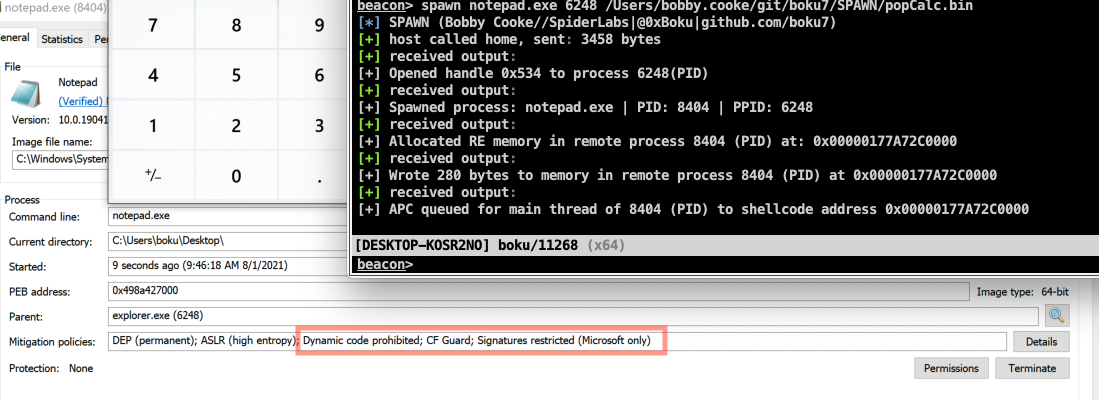 boku7/spawn
Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 abedalqaderswedan1/aswcrypter
An Bash&Python Script For Generating Payloads that Bypasses All Antivirus so far [FUD]
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
 senzee1984/micr0_shell
micr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.
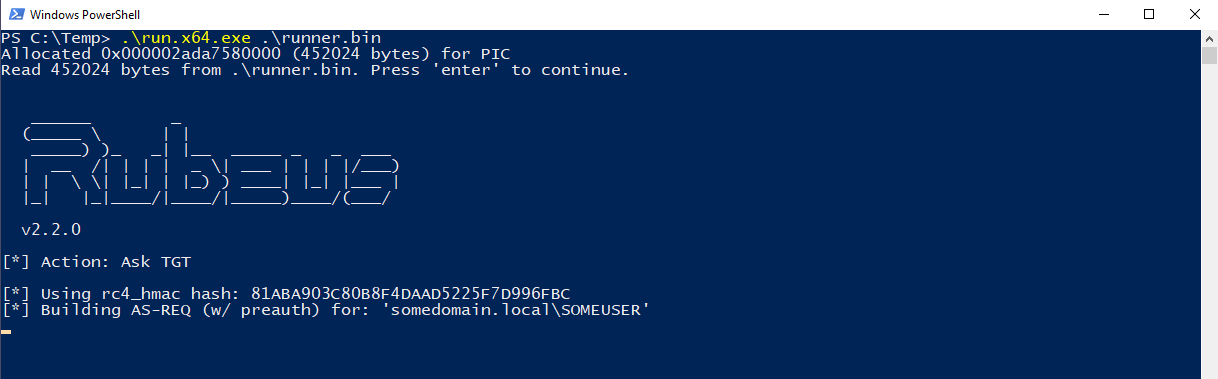 ofasgard/execute-assembly-pico
A PICO for Crystal Palace that implements CLR hosting to execute a .NET assembly in memory.
 bohops/dynamicdotnet
A collection of various and sundry code snippets that leverage .NET dynamic tradecraft
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
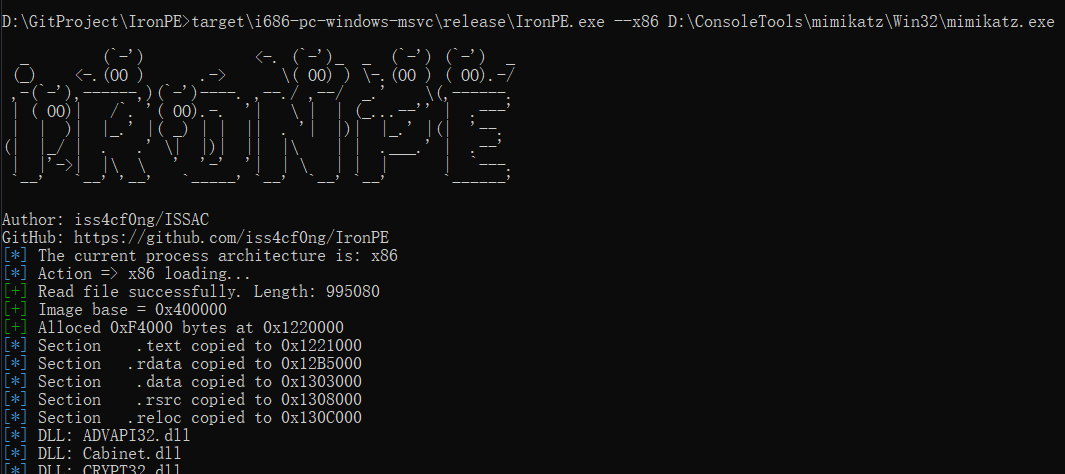 iss4cf0ng/ironpe
Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
 nirvanaon/now
NØW is a word-based shellcode encoding and obfuscation tool that transforms raw shellcode bytes into natural-looking English prose.
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…