

CVE-2023-38035-MobileIron-RCE
 mind2hex/cve-2023-38035-mobileiron-rce
Script to exploit CVE-2023-38035
exploitationpenetration-testingreconnaissance+3
1
mind2hex/cve-2023-38035-mobileiron-rceScript to exploit CVE-2023-38035
 cylancevulnresearch/reflectivedllrefresher
Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.
 redcode-labs/citadel
Collection of pentesting scripts
 zhzyker/exphub
Exphub[漏洞利用脚本库] 包括Webloigc、Struts2、Tomcat、Nexus、Solr、Jboss、Drupal的漏洞利用脚本,最新添加CVE-2020-14882、CVE-2020-11444、CVE-2020-10204、CVE-2020-10199、CVE-2020-1938…
 sensepost/ruler
A tool to abuse Exchange services
 wireghoul/htshells
Self contained htaccess shells and attacks
 bignerd95/chimay-red
Working POC of Mikrotik exploit from Vault 7 CIA Leaks
 plackyhacker/shellcode-encryptor
A simple shell code encryptor/decryptor/executor to bypass anti virus.
 smaash/quasibot
complex webshell manager, quasi-http botnet.
 barriuso/smbghost_automateexploitation
SMBGhost (CVE-2020-0796) Automate Exploitation and Detection
 d7ead/mkpivm
Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
 aniqfakhrul/sharperner
Simple executable generator with encrypted shellcode.
 cookiengineer/actual-php2shell
:robot: (Vibecoded prototype) NO, There is an easy way to exploit this vulnerability!
 c0ntextomy/c0ntextomy
CVE-2020-9992 - A design flaw in MobileDevice.framework/Xcode and iOS/iPadOS/tvOS Development Tools allows an attacker in the same network to gain…
 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
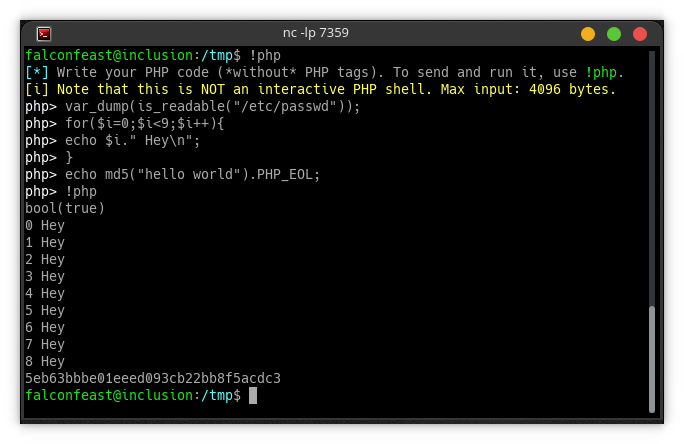 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…