
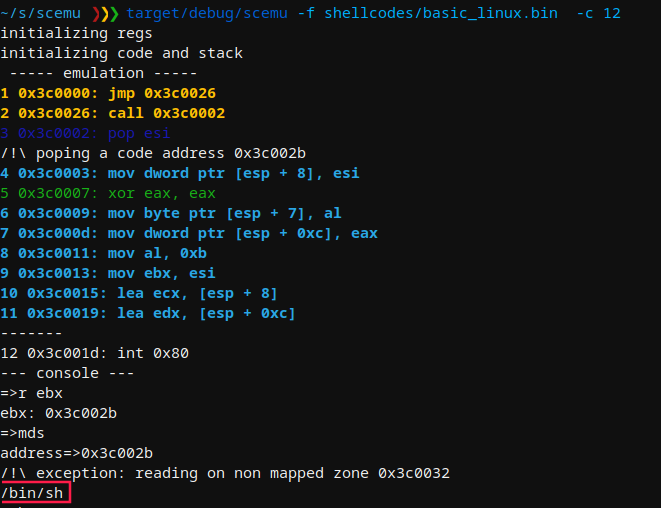
mwemu
 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
binary-analysisexploit-frameworksmalware-analysis+2
315
mwemuorg/mwemuPure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 chvancooten/nimpackt-v1
Nim-based assembly packer and shellcode loader for opsec & profit
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
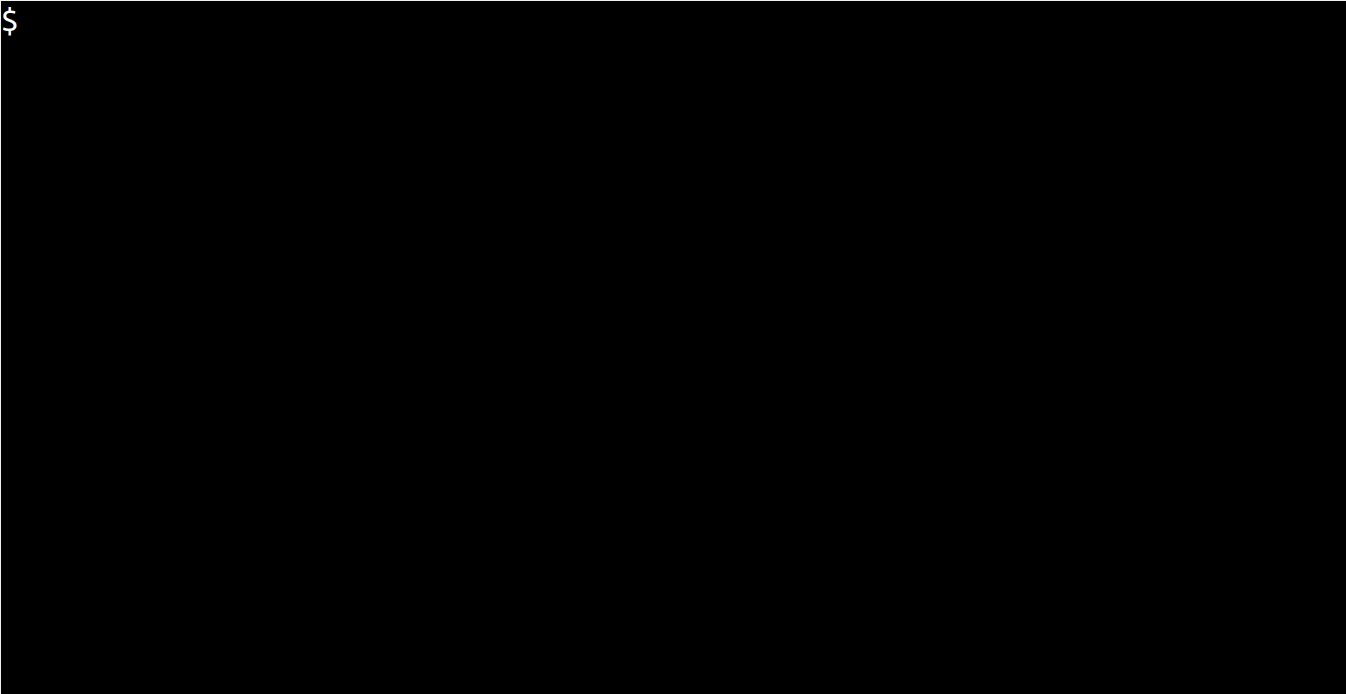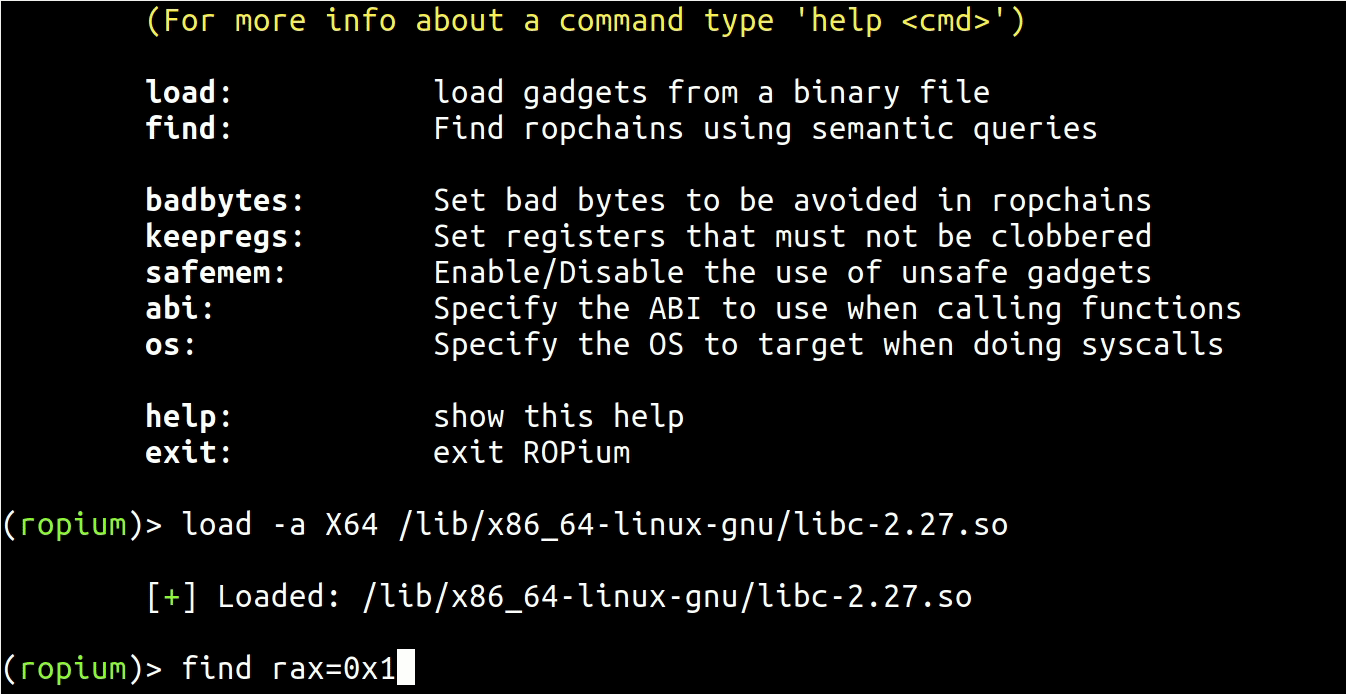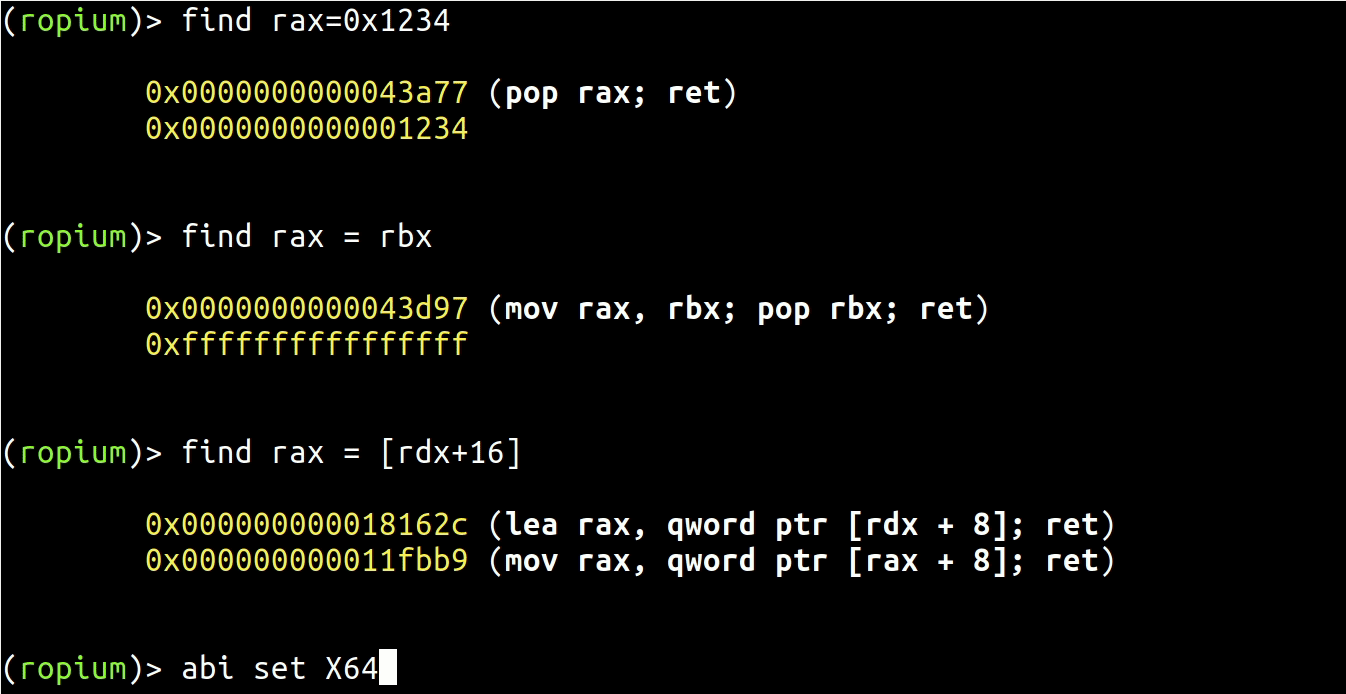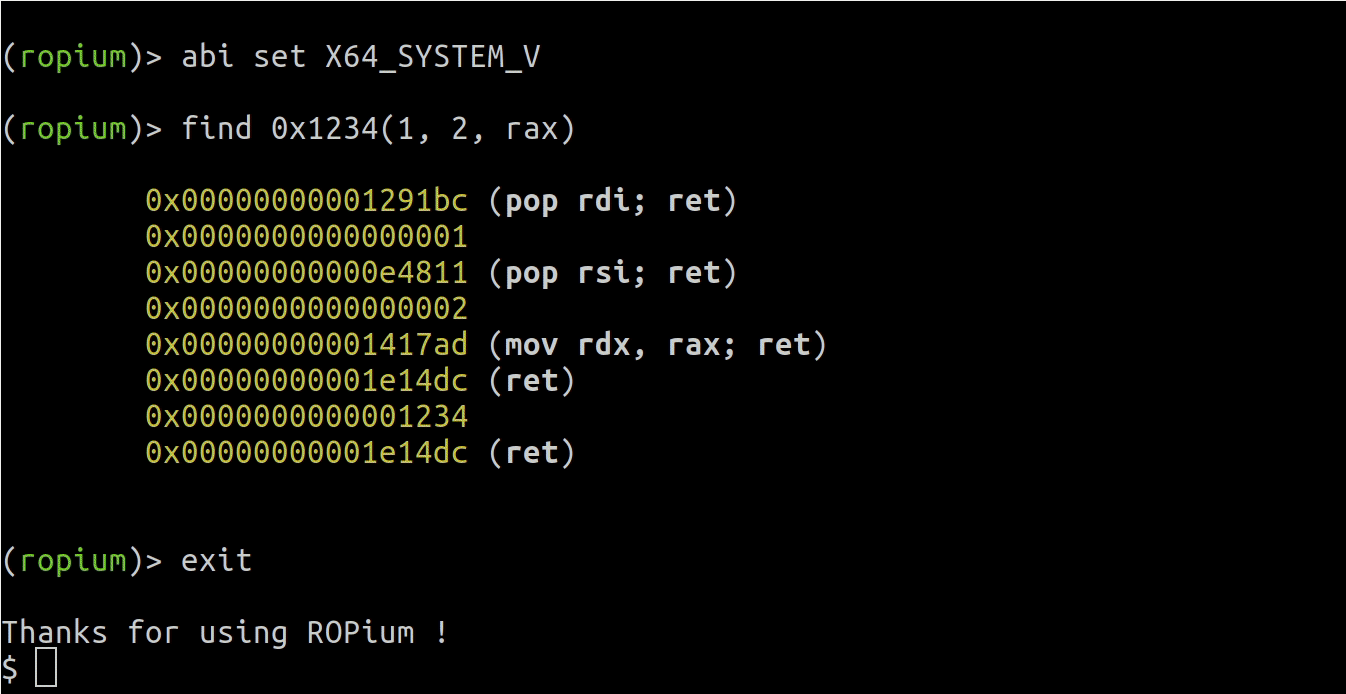 boyan-milanov/ropium
Automated ROP chain builder that extracts and analyzes gadgets from binaries using semantic queries, supporting X86/X64 architectures with a Python…
 b4rtik/redpeanut
RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.
 cryptolok/aslray
Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
 inf0secrabbit/badassmacros
C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.
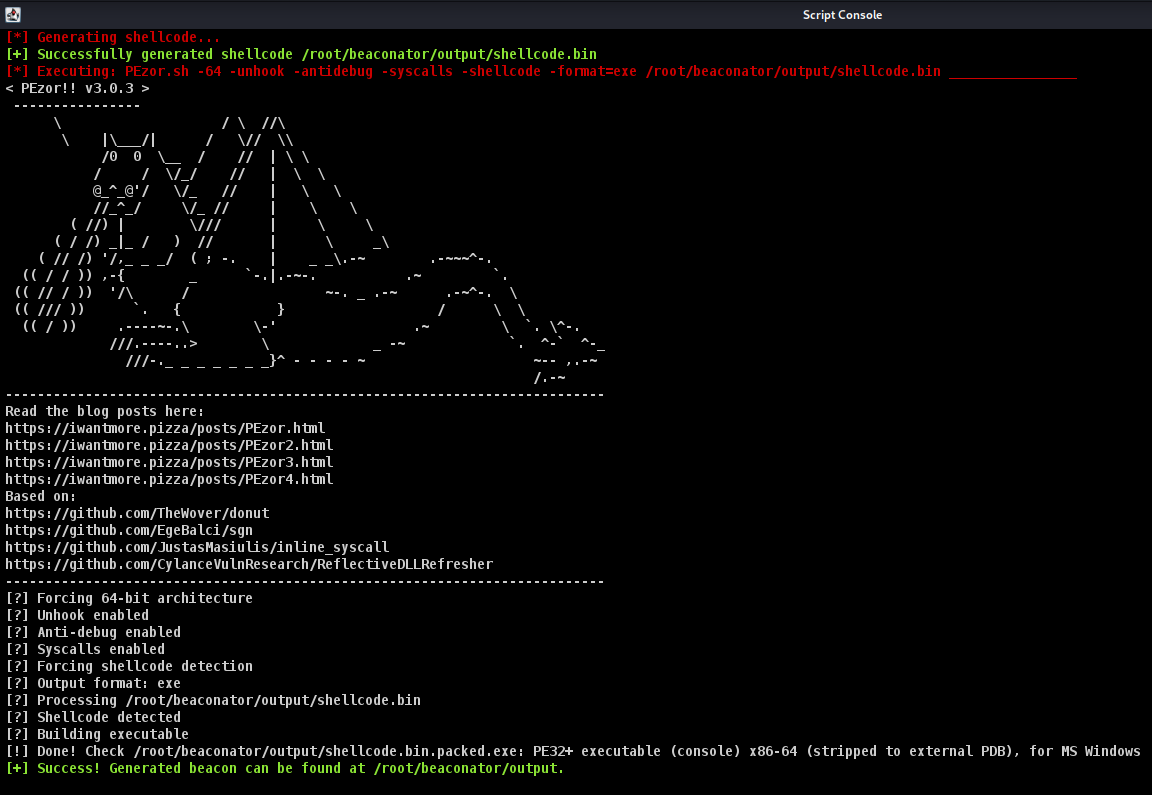 capt-meelo/beaconator
A beacon generator using Cobalt Strike and a variety of tools.
 risksense-ops/cve-2016-6366
Public repository for improvements to the EXTRABACON exploit
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
 wetw0rk/exploit-development
CVE-2020-8012, CVE-2016-10709, CVE-2017-17099, CVE-2017-18047, CVE-2019-1003000, CVE-2018-1999002
 codextf2/customc2channeltemplate
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
 rsmudge/cve-2020-0796-bof
Cobalt Strike Beacon Object File implementing CVE-2020-0796 SMBGhost local privilege escalation with dual weaponization paths for token theft and…
 codextf2/cobaltstrike_bofloader
open source port/reimplementation of the Cobalt Strike BOF Loader as is
 qmadev/crabloader
Rust-based User-Defined Reflective Loader for Cobalt Strike payloads. Avoids RWX memory pages for OPSEC safety. Includes an extractor tool for loader…