
phantom-frida
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
android-securitybinary-analysisdynamic-analysis-sandboxing+7
360
theqmaks/phantom-fridaBuild anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
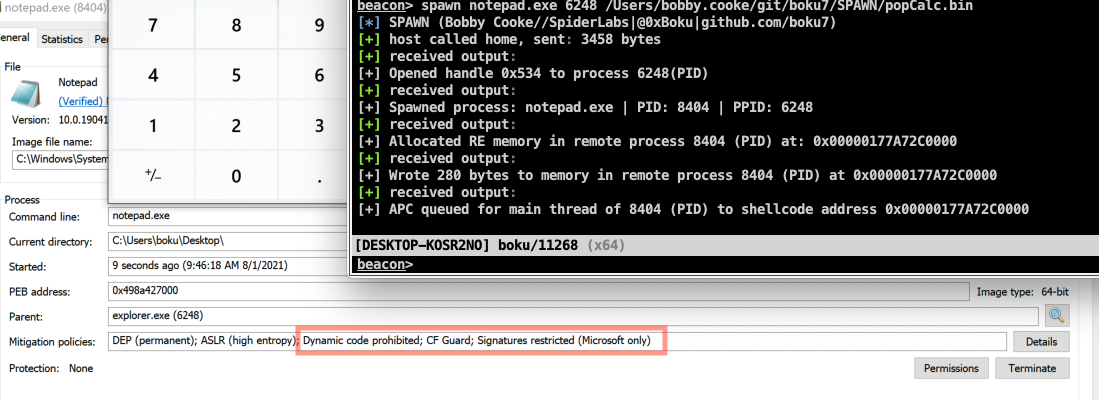 boku7/spawn
Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…
 noperator/cve-2019-18935
RCE exploit for a .NET JSON deserialization vulnerability in Telerik UI for ASP.NET AJAX.
 yzddmr6/java-shellcode-loader
基于Java实现的Shellcode加载器
 tarlogicsecurity/chankro
Herramienta para evadir disable_functions y open_basedir
 varbaek/xsser
From XSS to RCE 2.75 - Black Hat Europe Arsenal 2017 + Extras
 inf0secrabbit/badassmacros
C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
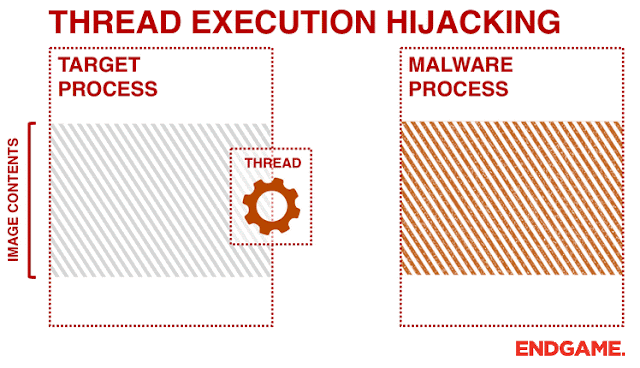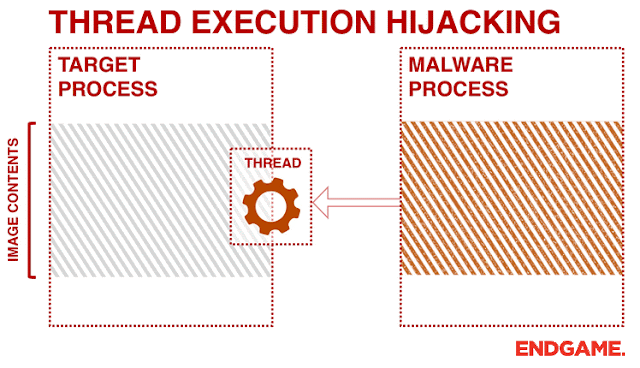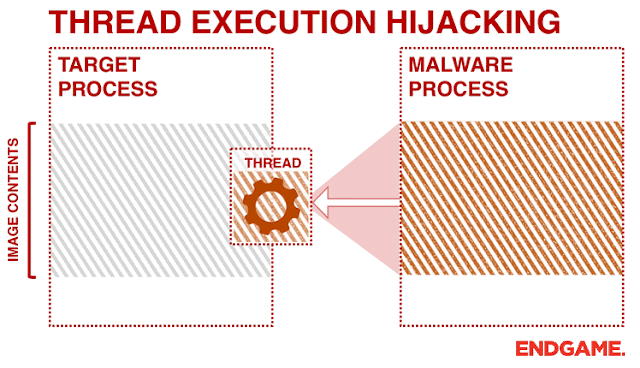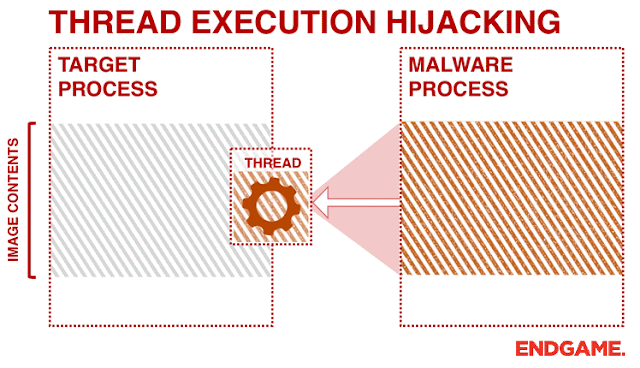 josh0xa/threadfire
PoC Thread Execution Hijacking for Win32 Code Injection
 l0n3m4n/cve-2024-6387
PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit)
 ofasgard/execute-assembly-pico
A PICO for Crystal Palace that implements CLR hosting to execute a .NET assembly in memory.
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 wetw0rk/exploit-development
CVE-2020-8012, CVE-2016-10709, CVE-2017-17099, CVE-2017-18047, CVE-2019-1003000, CVE-2018-1999002
 hood3drob1n/cve-2016-3714
ImaegMagick Code Execution (CVE-2016-3714)
 coolboy4me/cve-2019-0708_bluekeep_rce
it works on xp (all version sp2 sp3)

 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…