libpeconv
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
binary-analysismalware-analysismemory-forensics+4
1.4k
hasherezade/libpeconvCustom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 wireghoul/htshells
Self contained htaccess shells and attacks
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
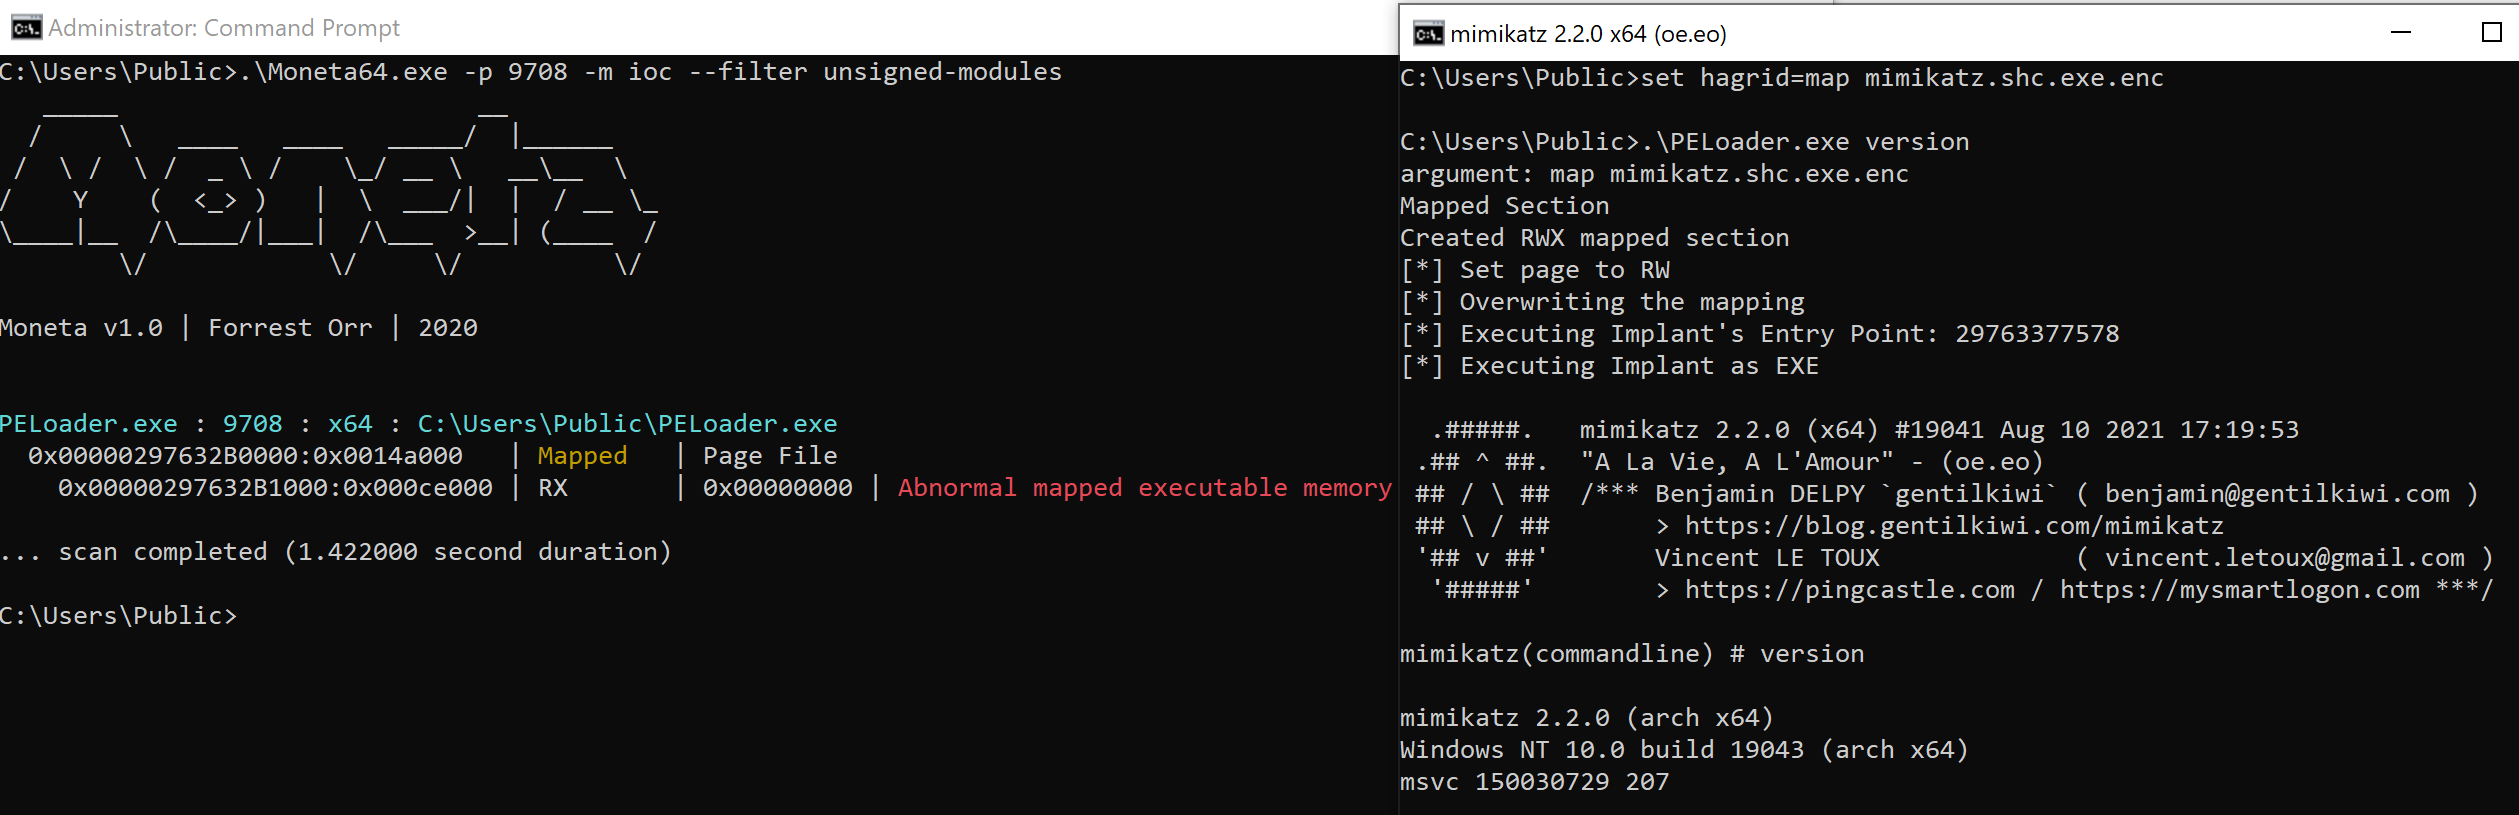 hagrid29/peloader
PE loader with various shellcode injection techniques
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby

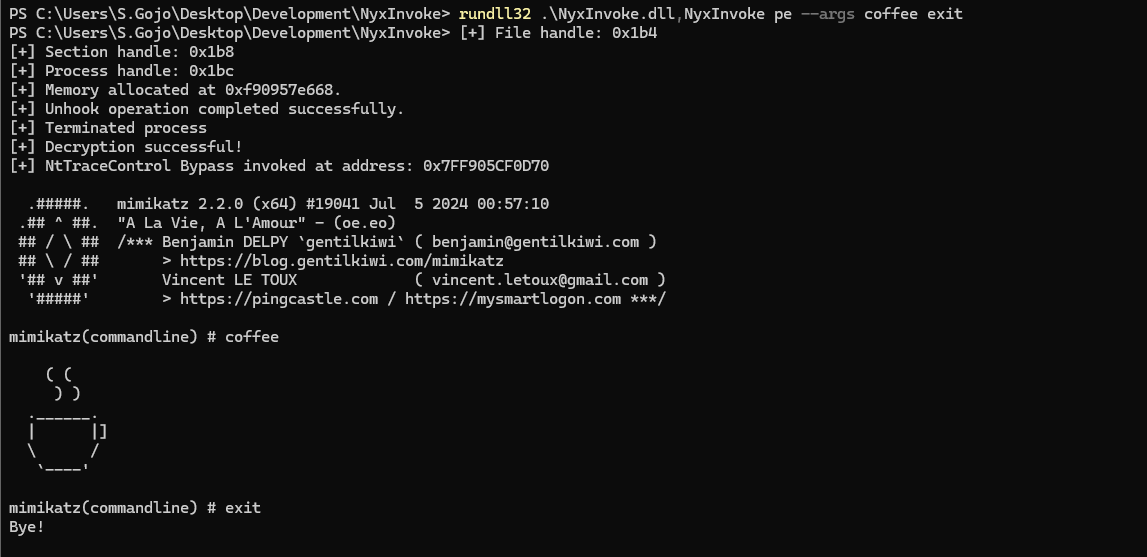 blacksnufkin/nyxinvoke
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
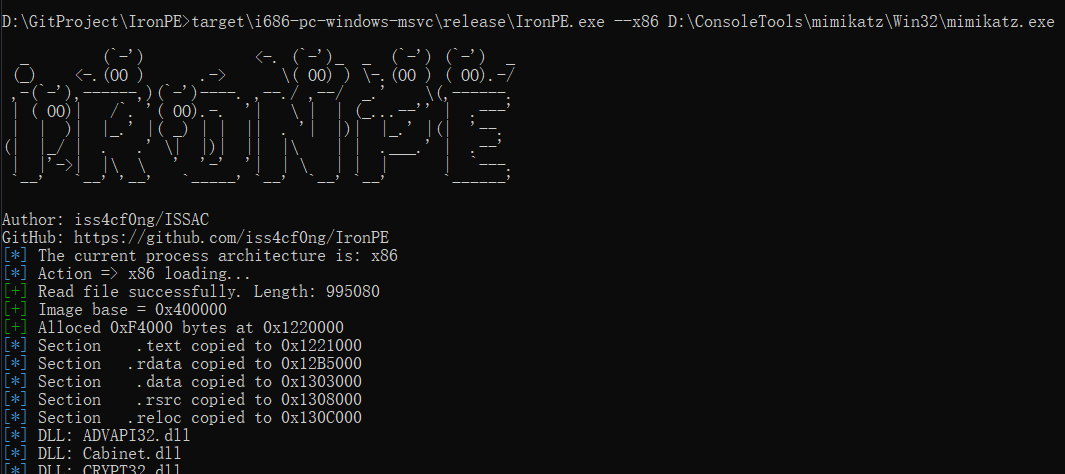 iss4cf0ng/ironpe
Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
 synacktiv/canon-mf644
Exploit and firmware analysis toolkit for Canon MF644 printer vulnerabilities, including Python exploits, ARM shellcode, and IDA Pro loader scripts…
 spiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-
Analysis for stage1 shellcode loader from hacking
 x3rx3ssec/cve-2023-5360
Royal Elementor Addons - Unauthenticated Remote Code Execution