
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
87 results
venom preview

venom

GitHubr00t-3xp10it/venom

venom - C2 shellcode generator/compiler/handler

command-and-controlexploit-frameworkspayload-development+5
2.0k5 years ago
BokuLoader preview

BokuLoader

GitHubboku7/bokuloader

A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
binary-analysisexploit-frameworkspayload-development+3
1.4k2 years ago
mortar preview

mortar

GitHub0xsp-srd/mortar

evasion technique to defeat and divert detection and prevention of security products (AV/EDR/XDR)

exploit-frameworksids-ips-evasionpayload-generation+2
1.5k2 years ago
Shoggoth preview

Shoggoth

GitHubfrkngksl/shoggoth

Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
binary-analysisexploit-frameworkspayload-generation+2
8057 months ago
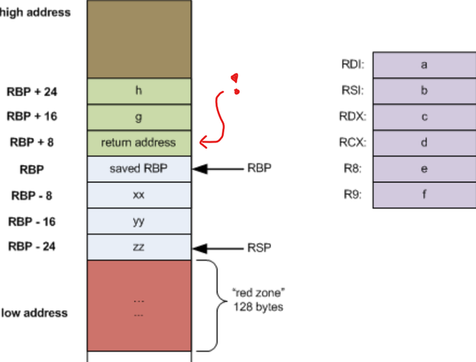
ThreadStackSpoofer preview

ThreadStackSpoofer

GitHubmgeeky/threadstackspoofer

Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
exploit-frameworksmalware-analysismemory-forensics+4
1.2k4 years ago
Medusa preview

Medusa

GitHubmythicagents/medusa

Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
command-and-controlexploit-frameworkslateral-movement+8
20811 days ago
Obfusk8 preview

Obfusk8

GitHubx86byte/obfusk8

Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries

cryptographyexploit-frameworkspayload-development+4
7934 months ago
Cooolis-ms preview

Cooolis-ms

GitHubrvn0xsy/cooolis-ms

Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
command-and-controlexploit-frameworksids-ips-evasion+7
9282 years ago
CobaltStrike-Toolset preview

CobaltStrike-Toolset

GitHubqax-a-team/cobaltstrike-toolset

Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
command-and-controlexploit-frameworkslateral-movement+8
5907 years ago
mwemu preview

mwemu

GitHubmwemuorg/mwemu

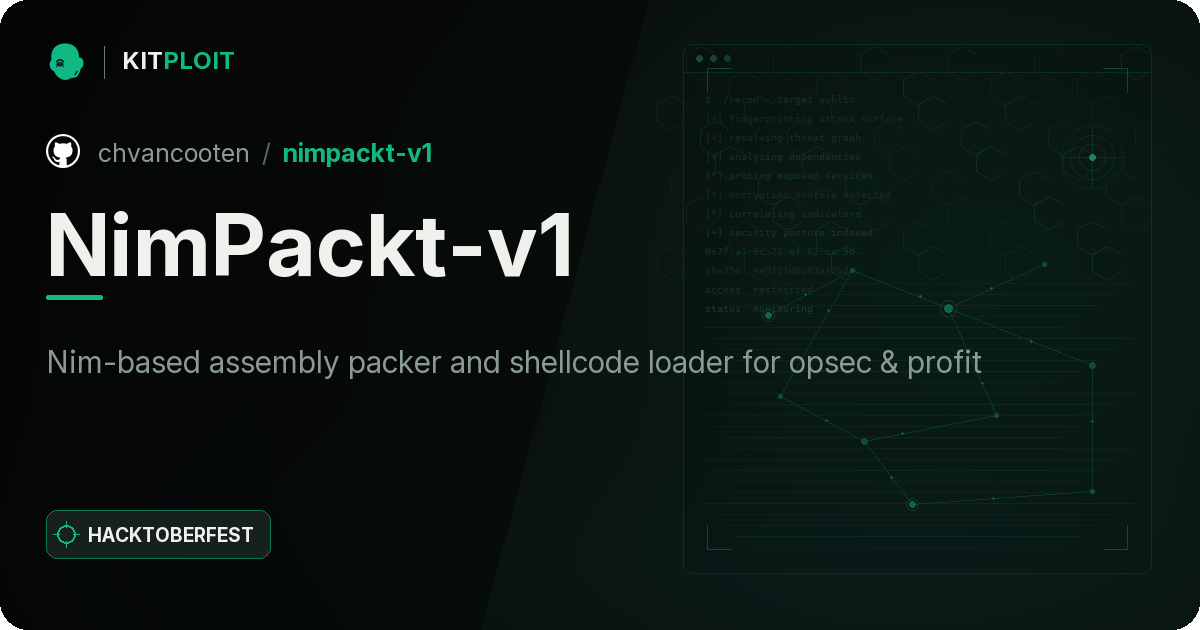
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
binary-analysisexploit-frameworksmalware-analysis+2
3132 days ago
NimPackt-v1 preview

NimPackt-v1

GitHubchvancooten/nimpackt-v1

Nim-based assembly packer and shellcode loader for opsec & profit

binary-exploitationexploit-frameworkspayload-generation+3
4873 years ago
RedPeanut preview

RedPeanut

GitHubb4rtik/redpeanut

RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.

command-and-controlexploit-frameworkspayload-generation+7
3306 years ago
BadAssMacros preview

BadAssMacros

GitHubinf0secrabbit/badassmacros

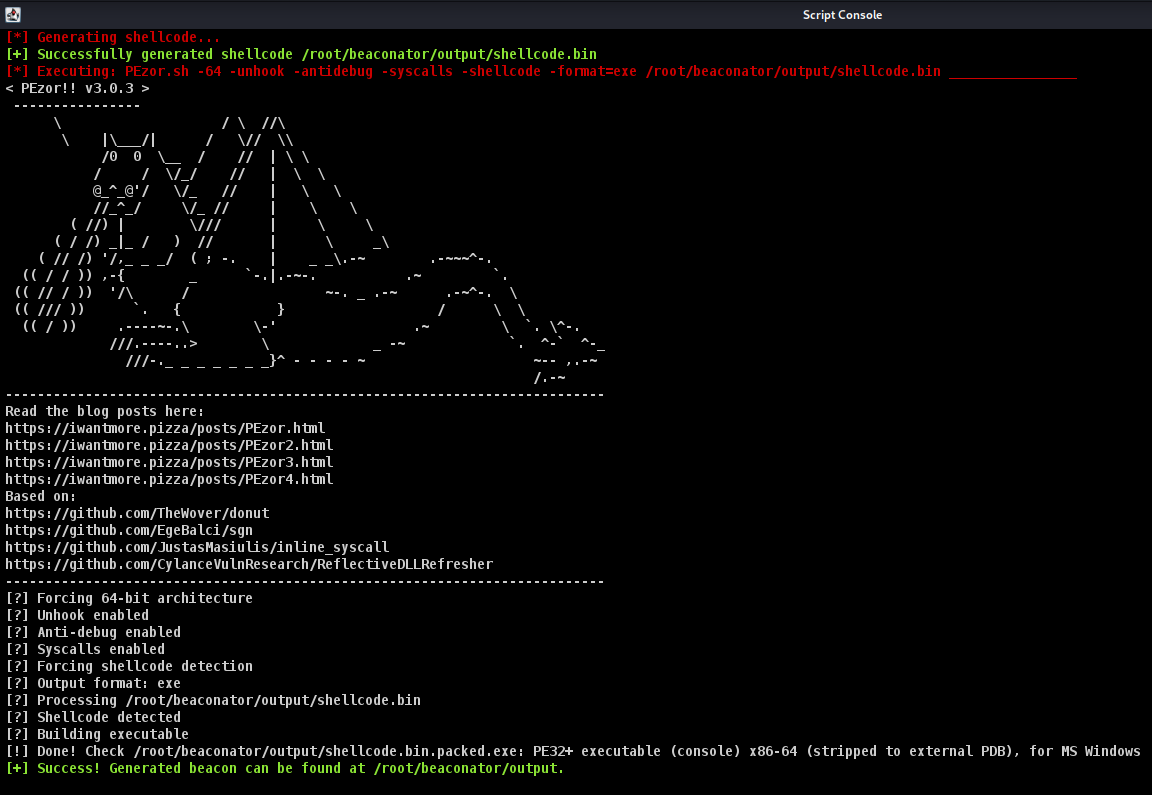
C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.
exploit-frameworkspayload-generationred-teaming+1
4445 years ago
Beaconator preview

Beaconator

GitHubcapt-meelo/beaconator

A beacon generator using Cobalt Strike and a variety of tools.
command-and-controlexploit-frameworkspayload-generation+2
4465 years ago
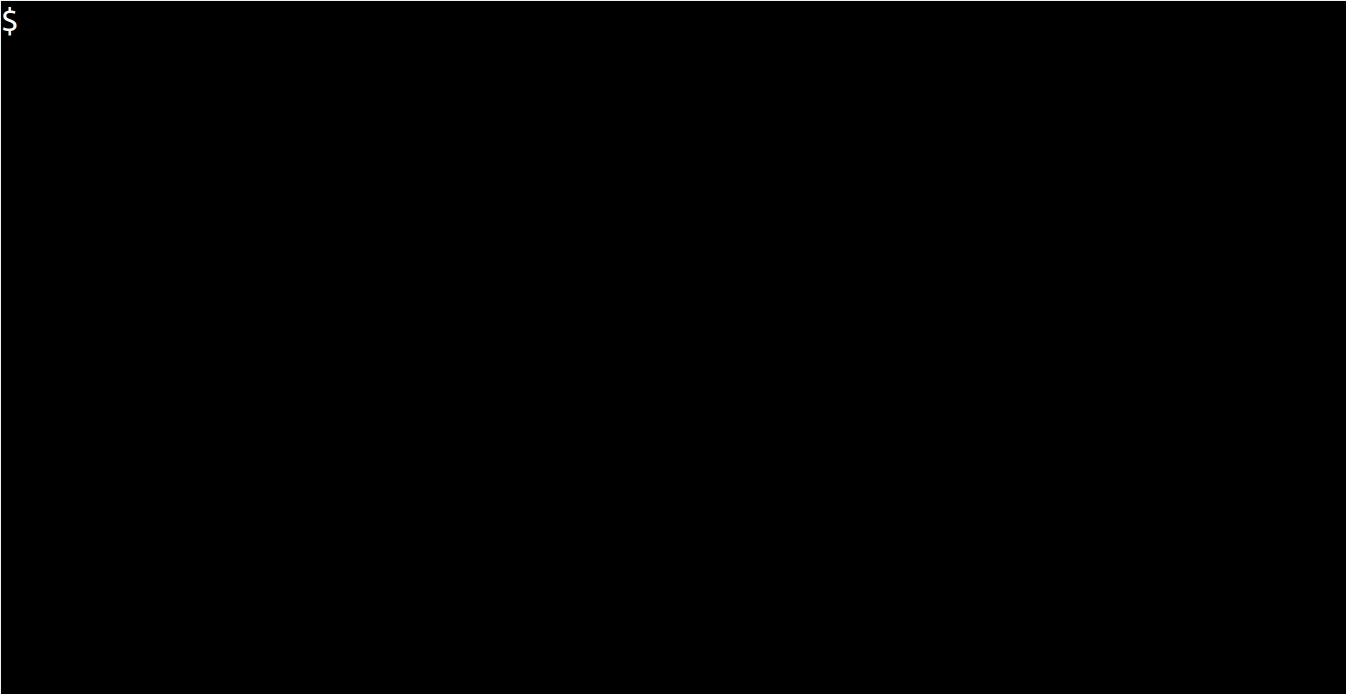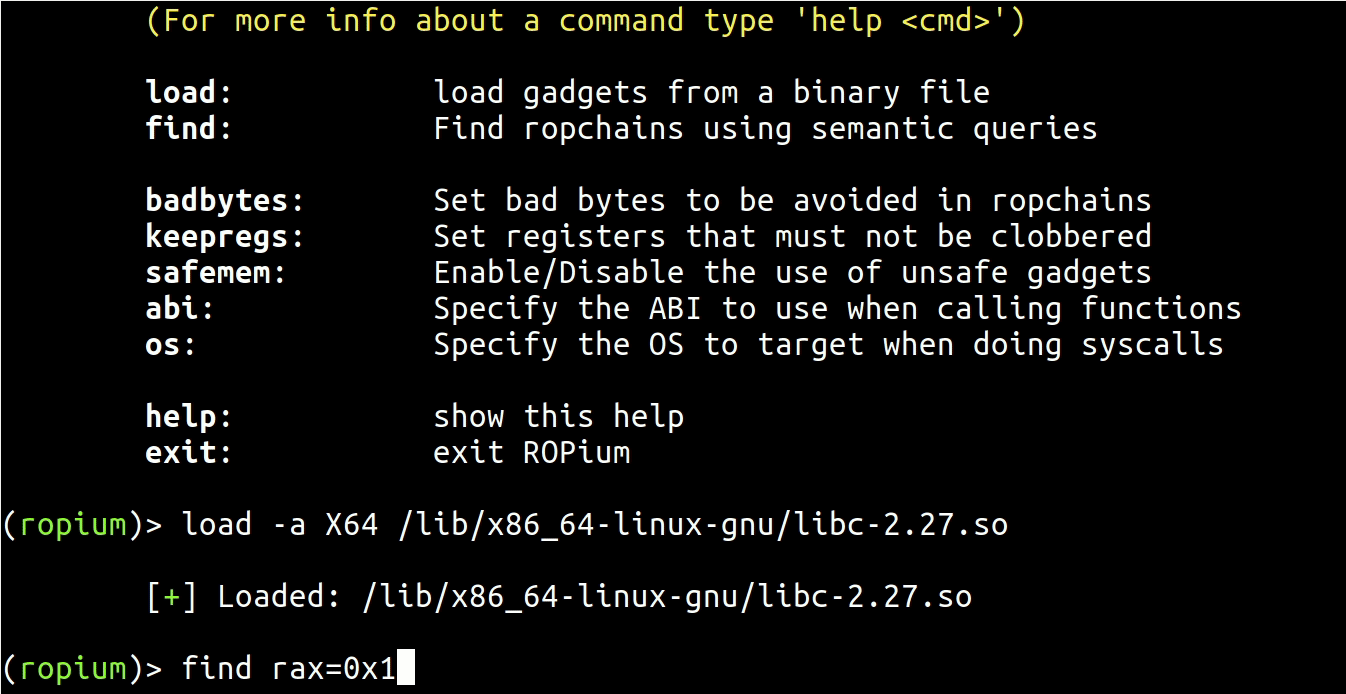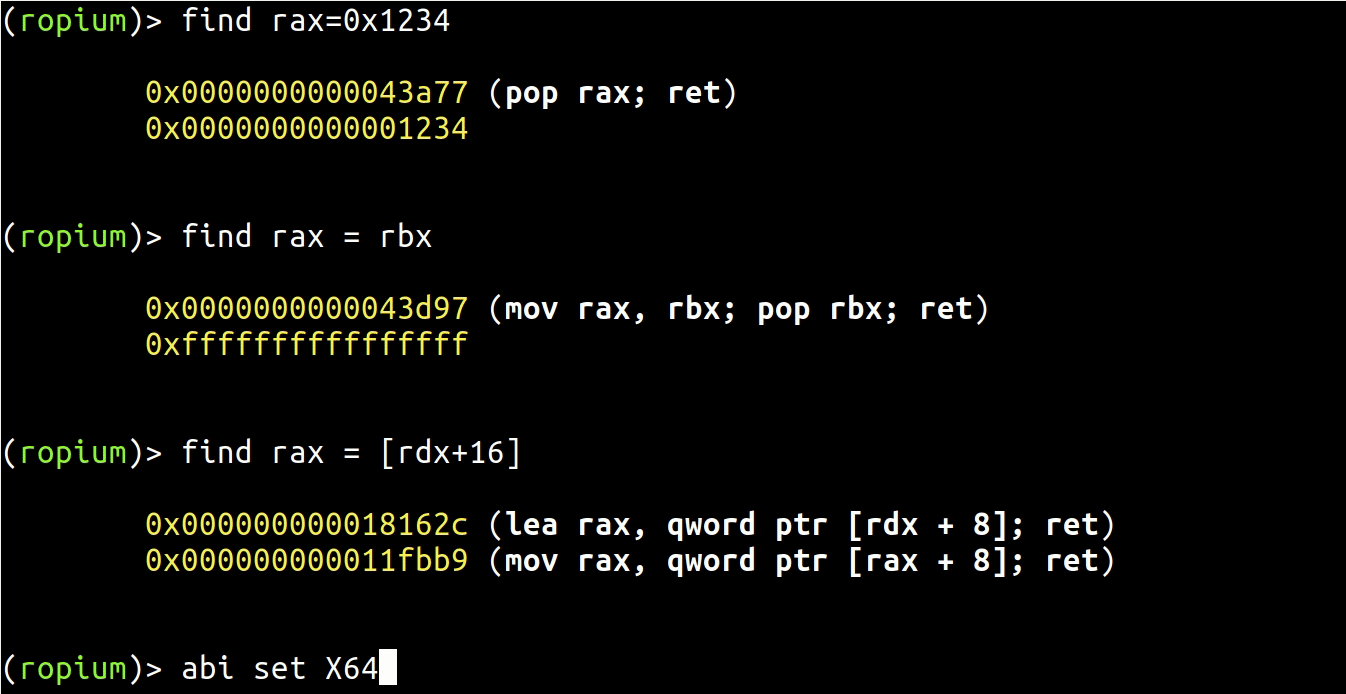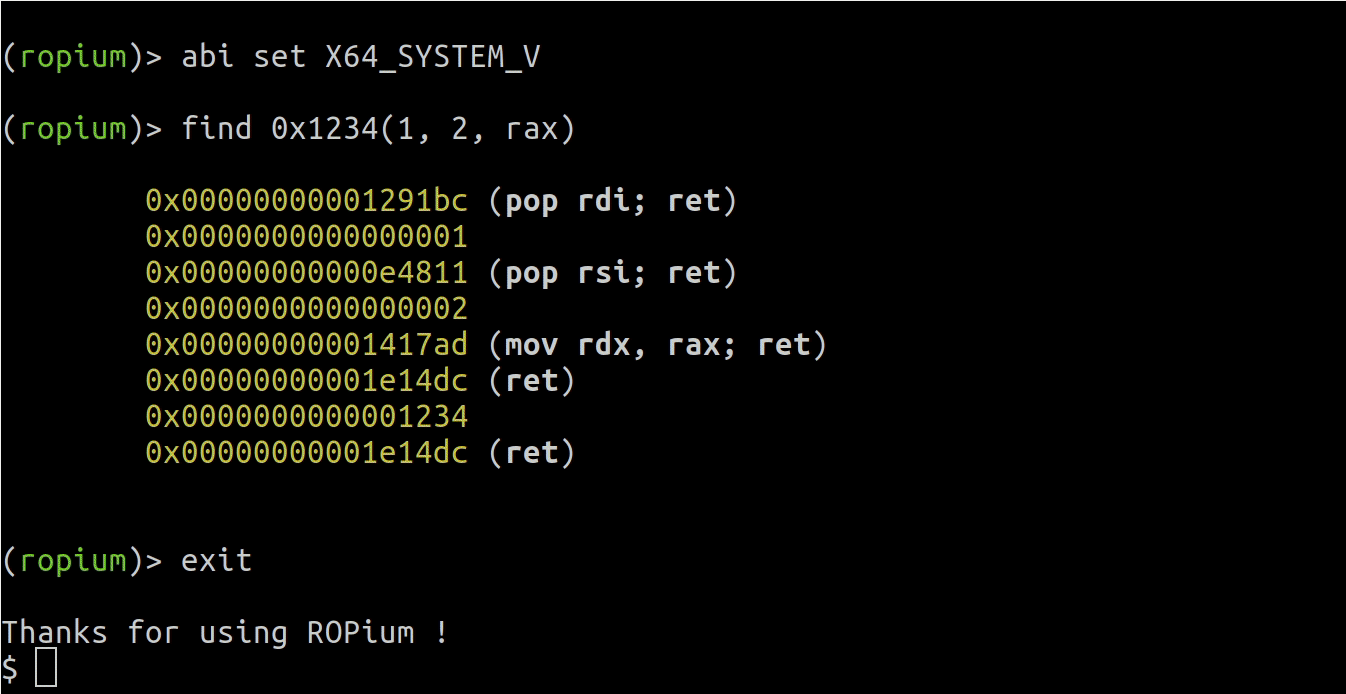
ropium preview

ropium

GitHubboyan-milanov/ropium

Automated ROP chain builder that extracts and analyzes gadgets from binaries using semantic queries, supporting X86/X64 architectures with a Python…

binary-exploitationexploit-frameworkspayload-development+2
4024 years ago
TeamsImplant preview

TeamsImplant

GitHuballevon412/teamsimplant

Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
command-and-controlexploit-frameworkspayload-development+5
2084 years ago
EvilVM preview

EvilVM

GitHubjephthai/evilvm

Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…

command-and-controlexploit-frameworkspayload-development+7
2095 years ago
Cobaltstrike_BOFLoader preview

Cobaltstrike_BOFLoader

GitHubcodextf2/cobaltstrike_bofloader

open source port/reimplementation of the Cobalt Strike BOF Loader as is

binary-exploitationexploit-frameworkspayload-development+3
7428 days ago
Previous12345Next