
patching
 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
binary-analysisbinary-exploitationdebuggers+8
gaasedelen/patchingAn Interactive Binary Patching Plugin for IDA Pro
 capt-meelo/lazzzy
Shellcode loader demonstrating multiple execution techniques including direct syscalls, IAT evasion, encrypted payloads, PPID spoofing, and code…
 machine1337/gmailc2
A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions
 hagrid29/peloader
PE loader with various shellcode injection techniques
 d7ead/mkpivm
Generate polymorphic, position-independent virtual machines (PIVMs) from arbitrary x86/x64 shellcode.
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 kleiton0x00/shelltropy
A technique of hiding malicious shellcode via Shannon encoding.
 senzee1984/inflativeloading
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
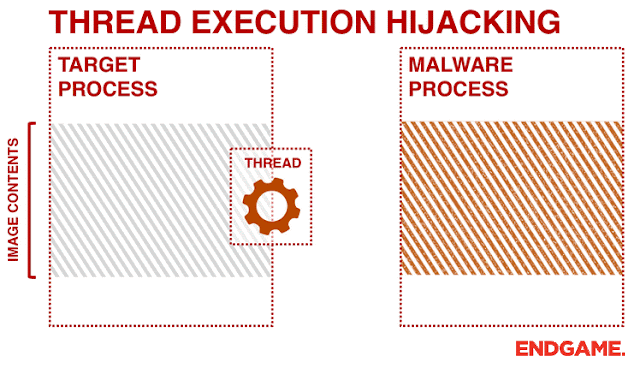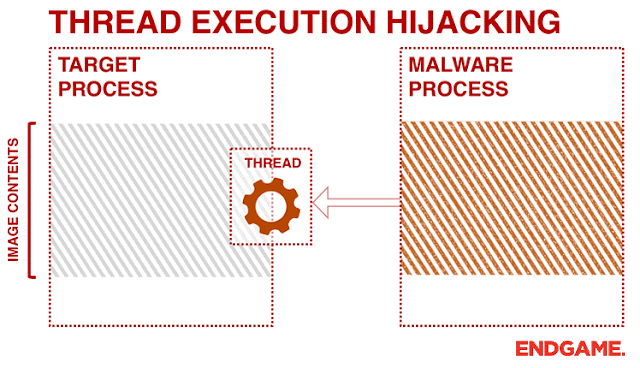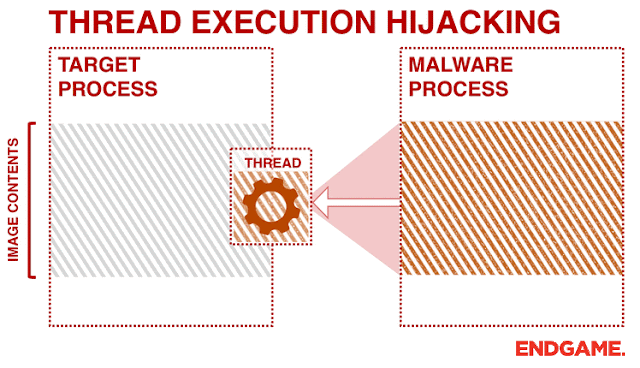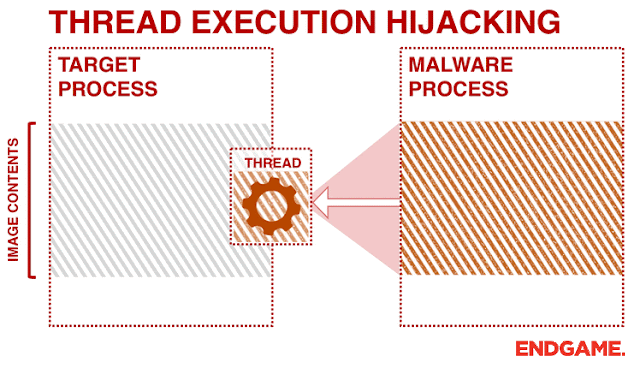 josh0xa/threadfire
PoC Thread Execution Hijacking for Win32 Code Injection
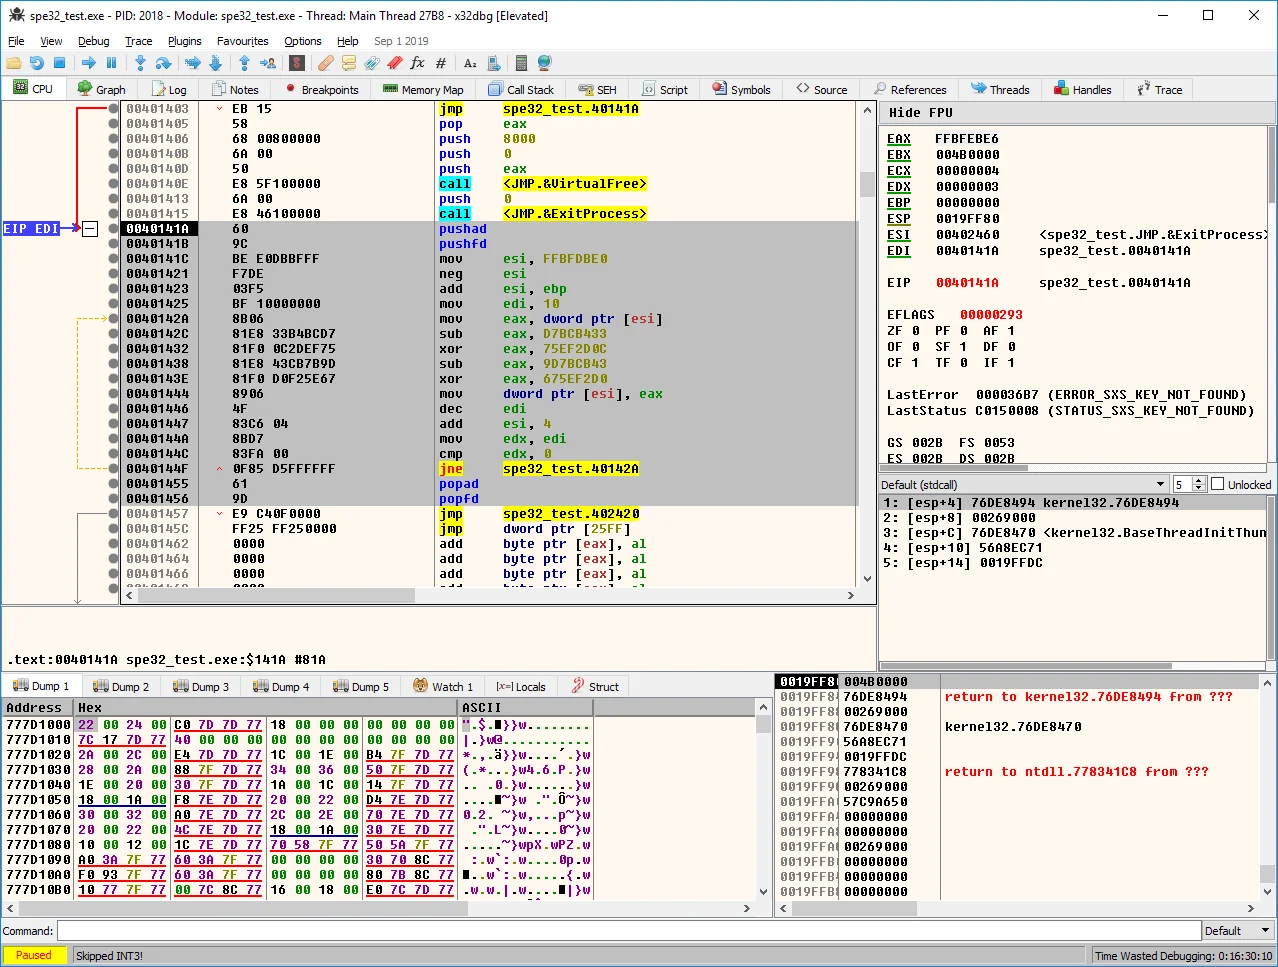 pelock/simple-polymorphic-engine-spe32
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…
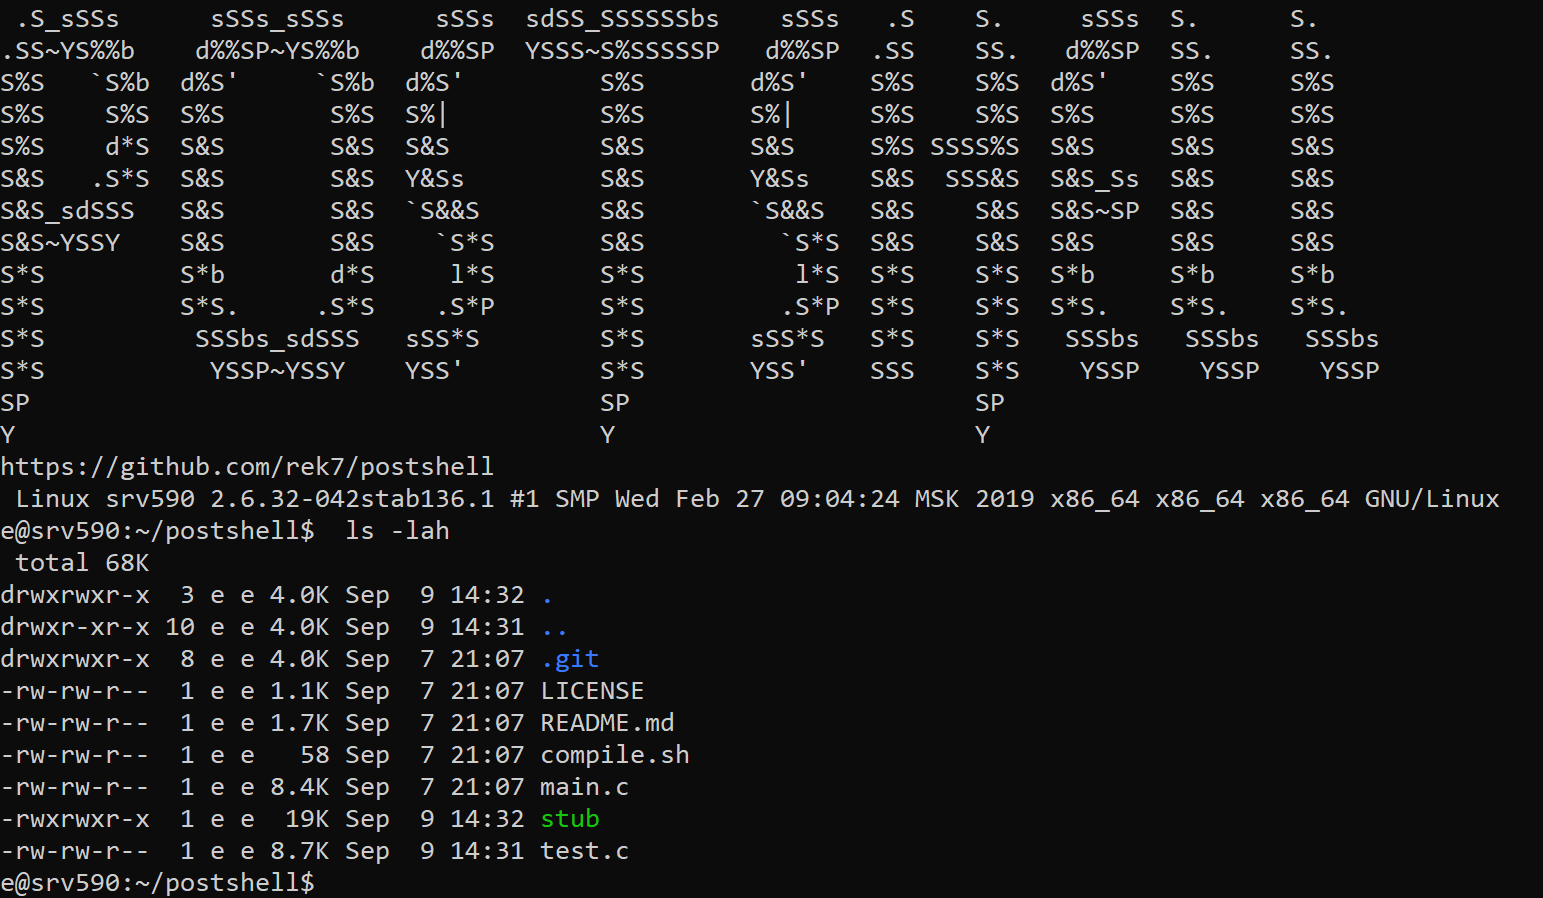 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
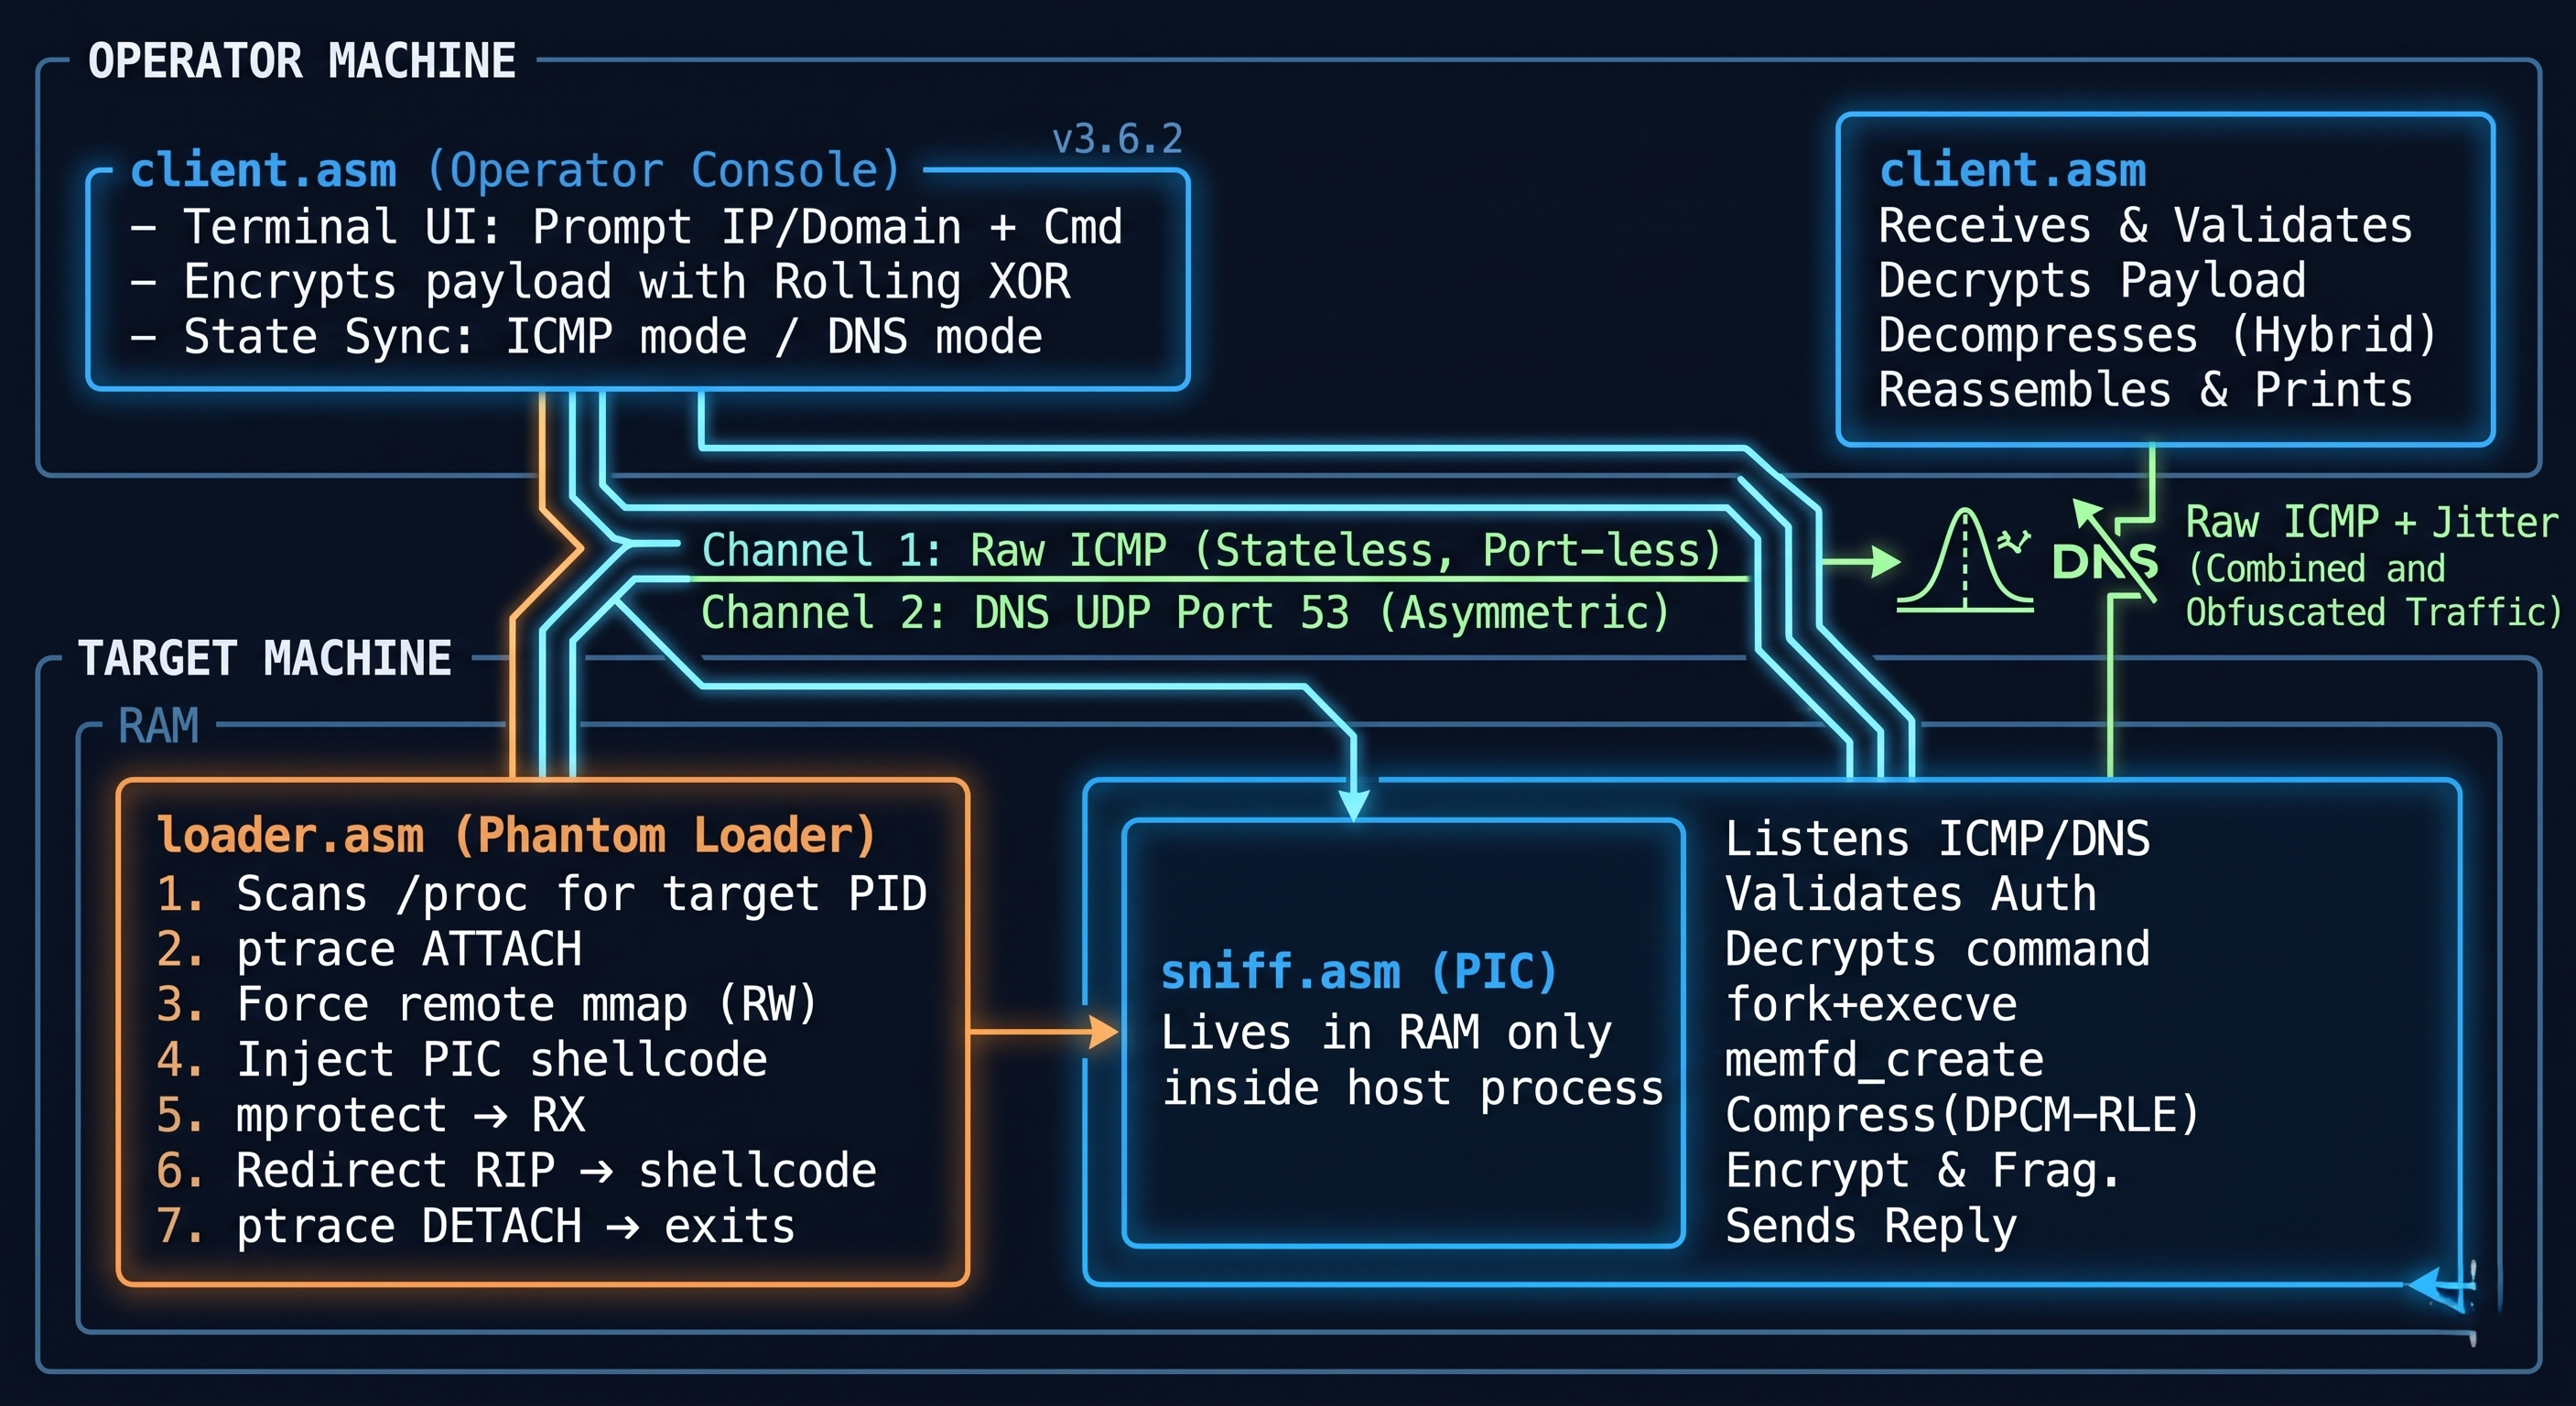 jm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…
 buzzer-re/shinigami
A dynamic unpacking tool
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 melardev/xeytanwxcpp-rat
Work in Progress. RAT written in C++ using wxWidgets
 cecio/xenoboxx
Hardware Sandbox Toolkit
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 zardus/ctf-tools
Some setup scripts for security research tools.