

CuiRi
 nydubh3/cuiri
一款红队专用免杀木马生成器,基于shellcode生成绕过所有杀软的木马。
command-and-controlexploitationids-ips-evasion+7
nydubh3/cuiri一款红队专用免杀木马生成器,基于shellcode生成绕过所有杀软的木马。
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
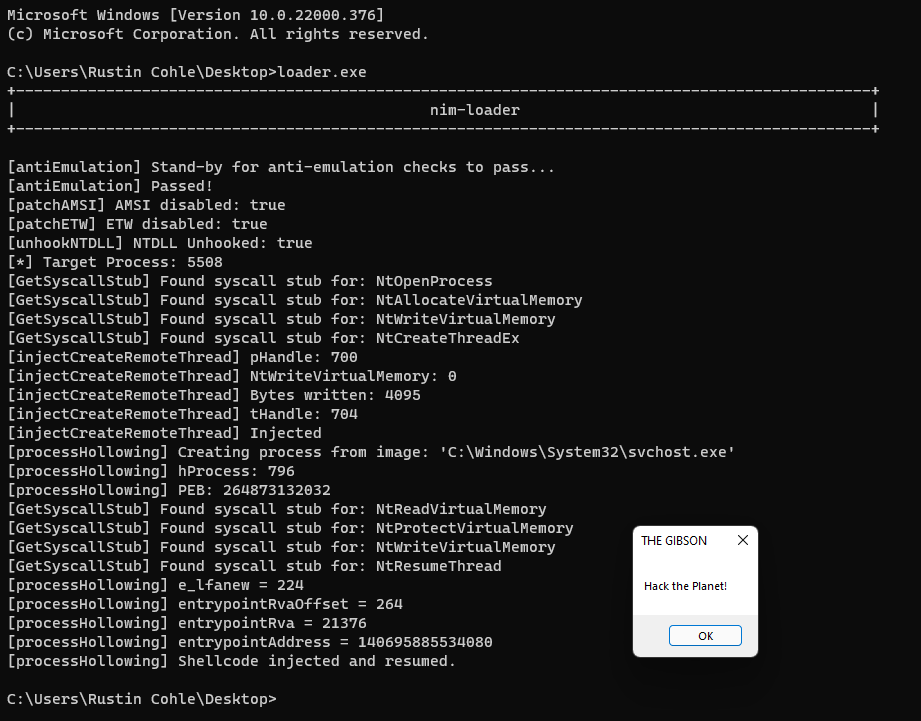 adamsvoboda/nim-loader
WIP shellcode loader in nim with EDR evasion techniques
 zznop/sploit
Go package that aids in binary analysis and exploitation
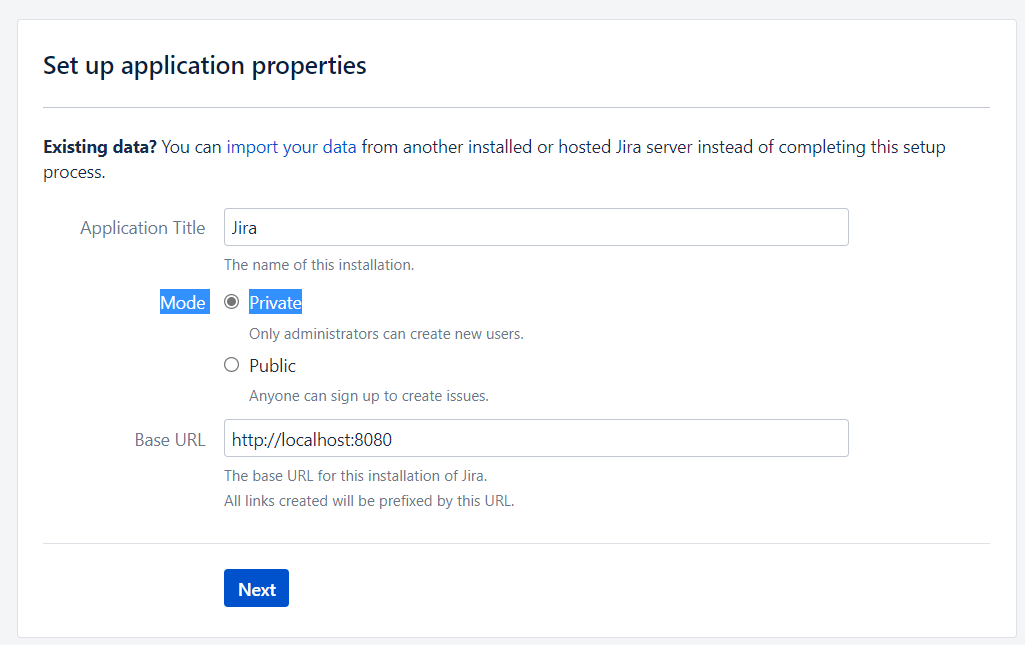 petrusviet/cve-2019-11581
Atlassian Jira unauthen template injection
 d0rb/logofail-poc
This is a hypothetical demonstration of the process involved in exploiting LogoFail, it theoretically includes the necessary steps.
 0xcl/cve-2016-7190
ChakraCore exploitation techniques
 gelukcrab/react-server-components-rce
React Server Components 远程代码执行漏洞(CVE-2025-55182)
 bootsareme/copyfail-deconstructed
Easy-to-understand version of CVE-2026-31431
 yanoshercohen/react2shell_cve-2025-55182
React2Shell (CVE-2025-55182) Exploit
 blackjuker2/cve-2019-0232
Apache Tomcat CGI Servlet RCE (Windows)
 sadisticnight/poc-cve-2025-62222
Proof-of-concept demonstrating remote code execution via prompt injection in GitHub Copilot Chat, using a crafted Python file to trigger a…
 themalwareguardian/cve-2025-34096
SEH-based buffer overflow in Easy File Sharing Web Server 7.2, reachable through the password recovery endpoint.
 innocentx0/cve-2015-6967-exploit
CVE-2015-6967 PoC Exploit