
 codextf2/cobaltstrike_bofloader
open source port/reimplementation of the Cobalt Strike BOF Loader as is
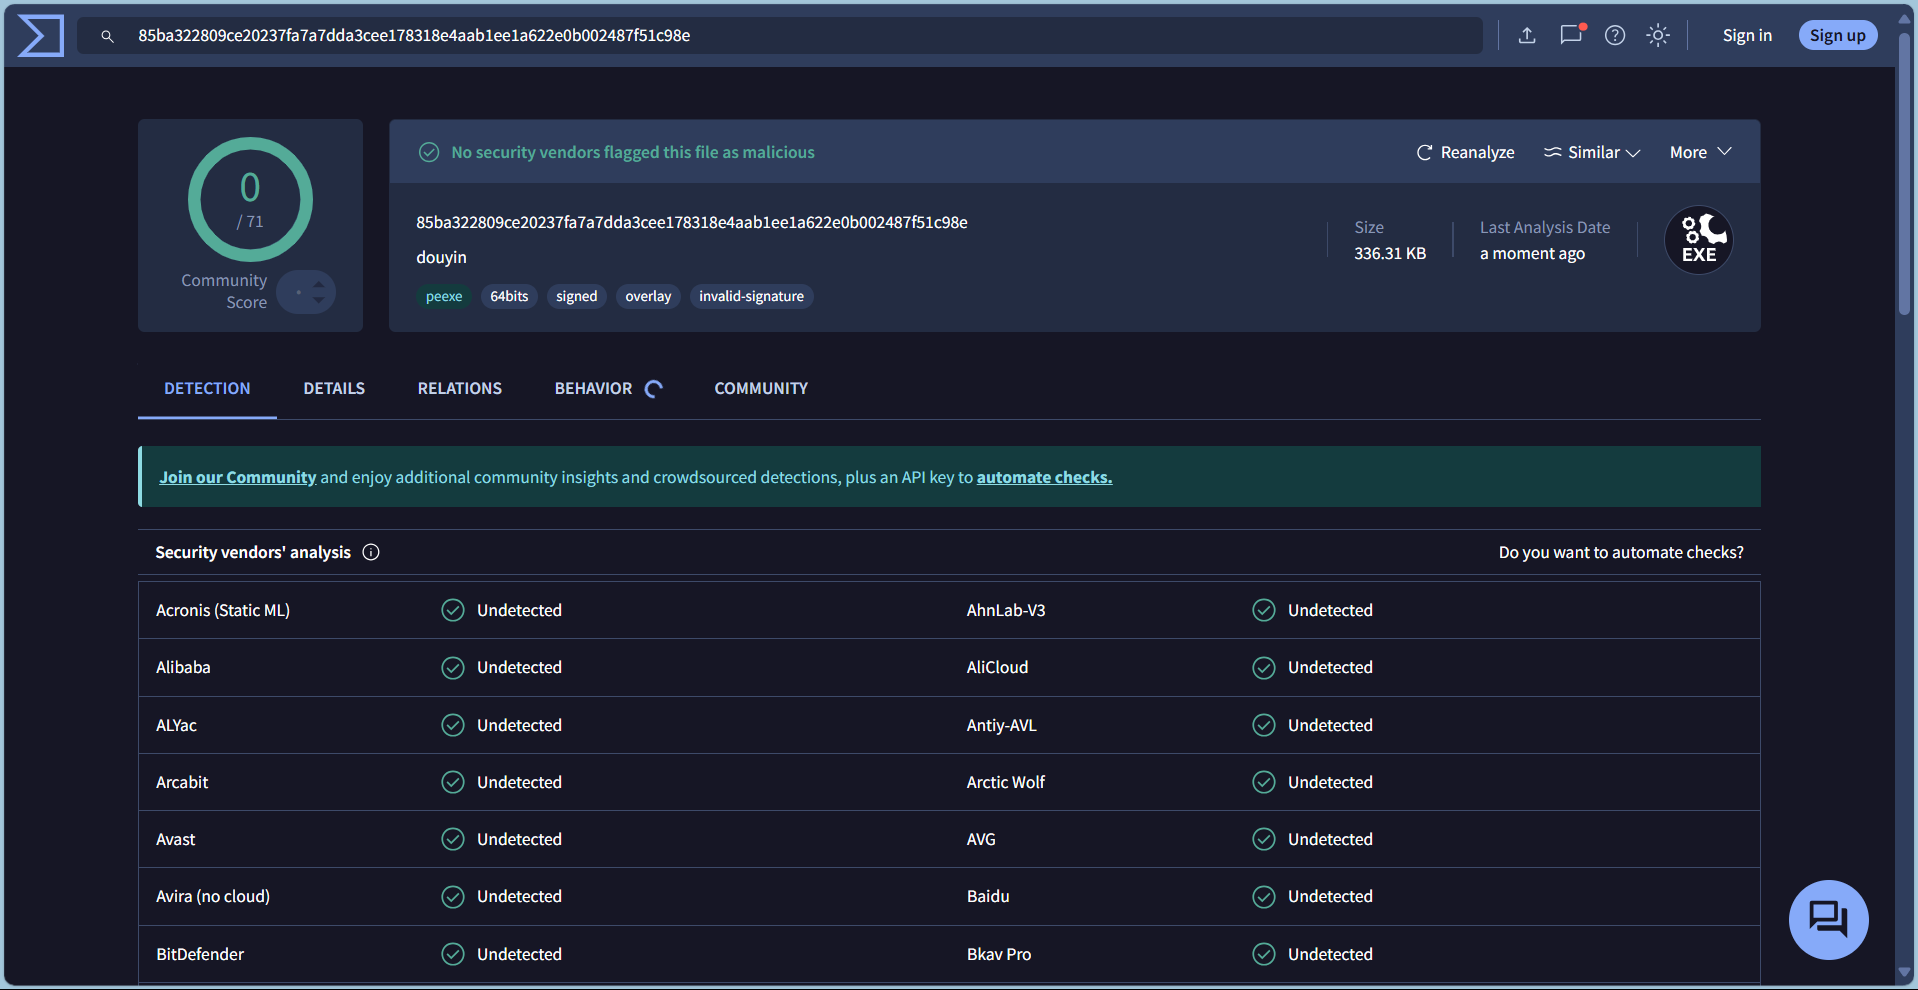 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
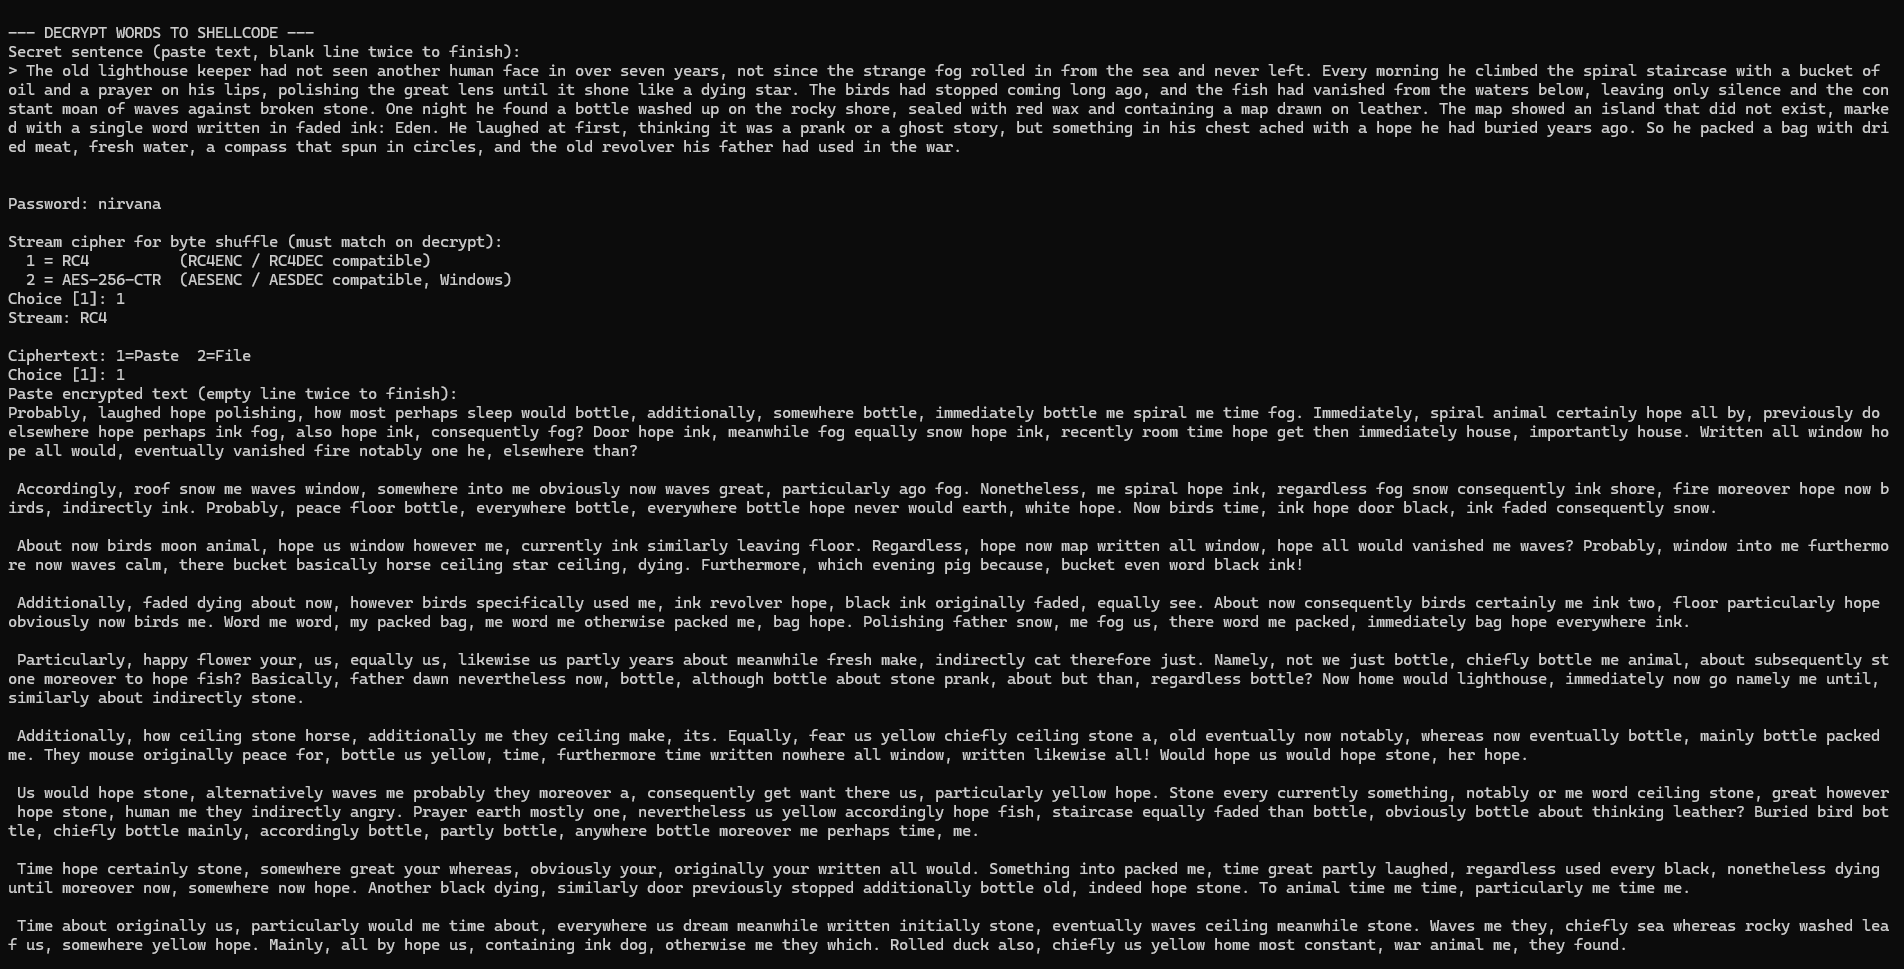 nirvanaon/now
NØW is a word-based shellcode encoding and obfuscation tool that transforms raw shellcode bytes into natural-looking English prose.
 sk4r4b/ntdll-reconstruction
A technique that mixes NTDLL unhooking and hellsgate gate varients
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
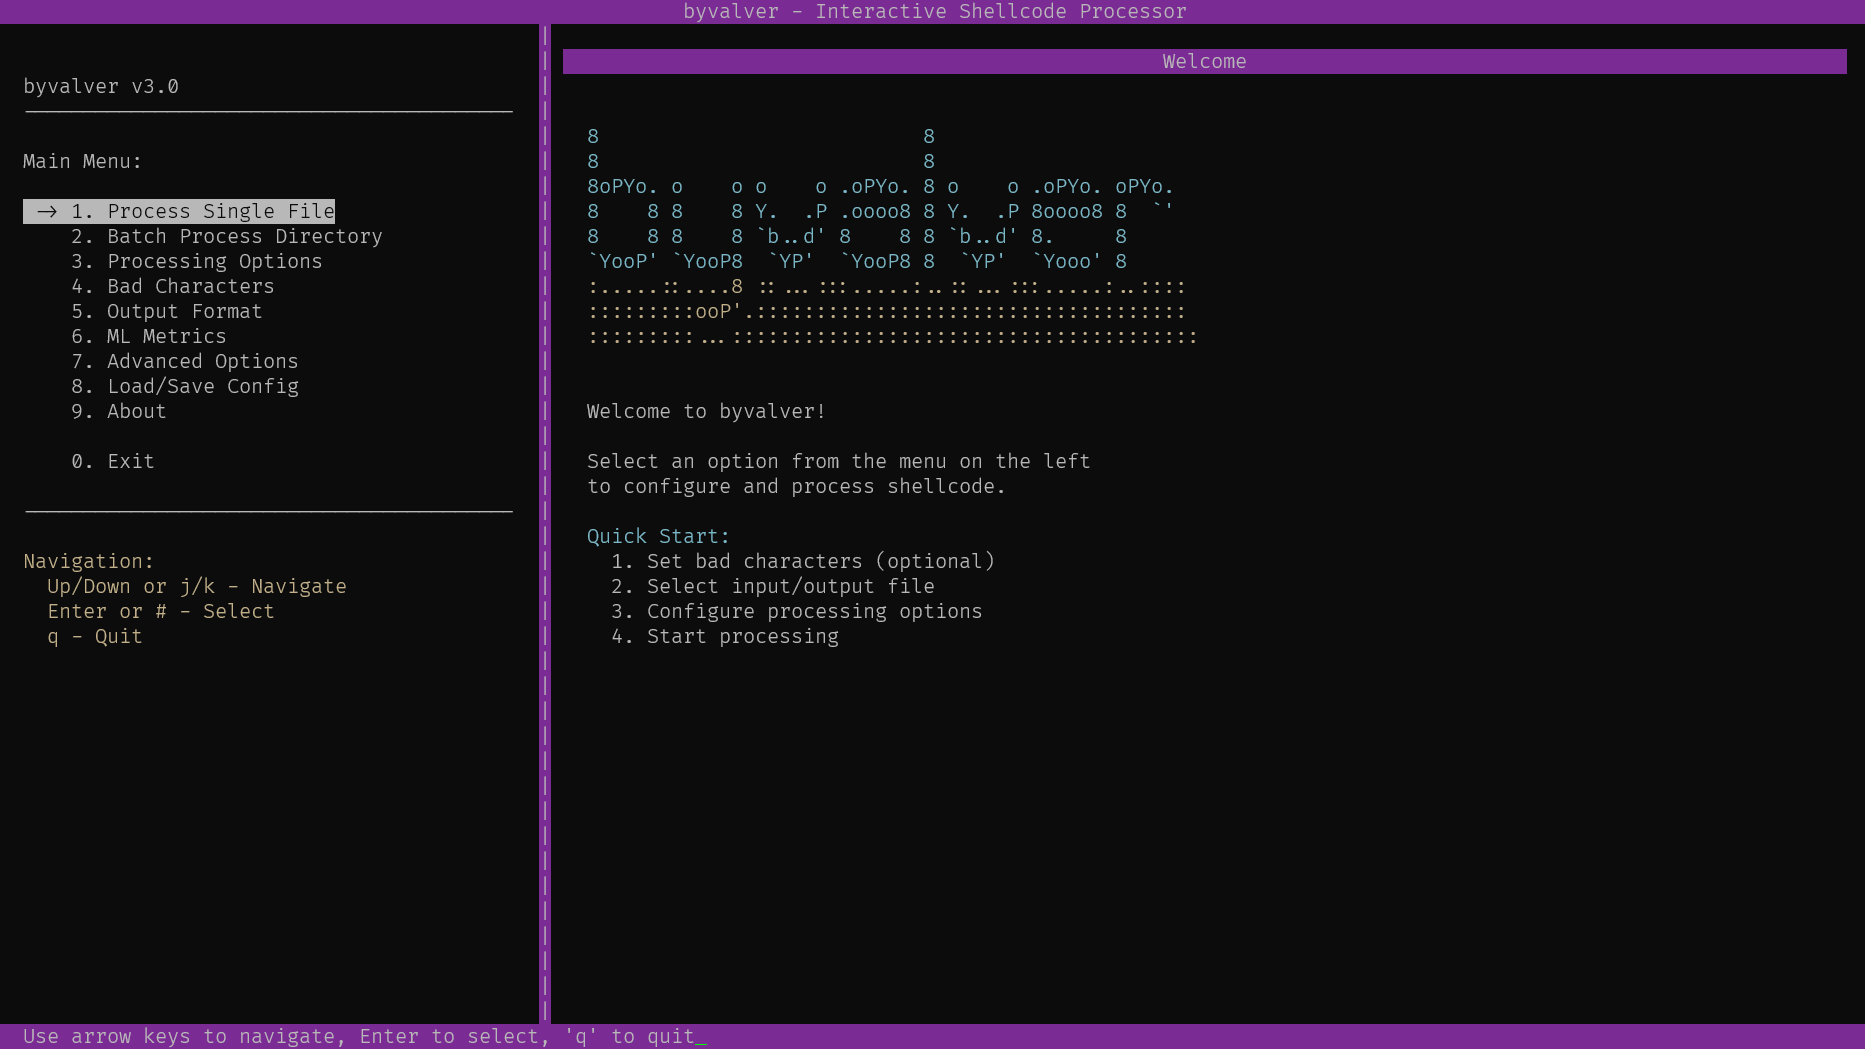 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
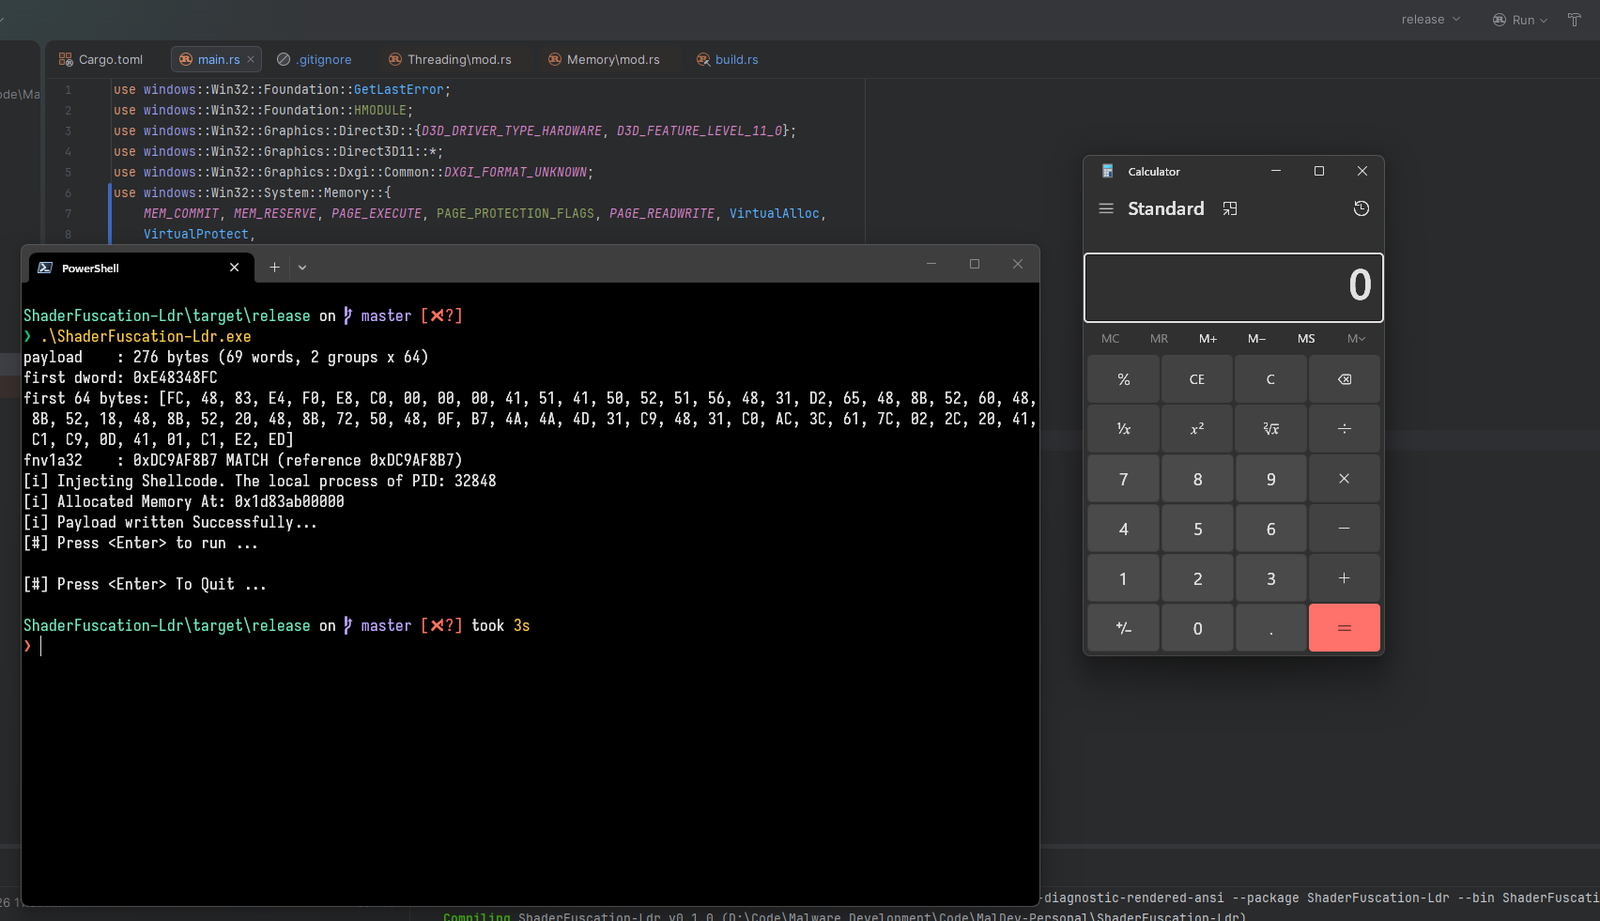 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 ps1337/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
 sneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter
Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.
 sneakynachos/cve-2026-87575-cve-2026-87606-cve-2026-87491-and-cve-2026-85046.-escape-the-v8-carcass.
Chained Chrome V8 renderer escape proof-of-concept exploiting four CVEs: Float64Array corruption, Wasm overwrite, popup navigation retargeting, and…
 gmh5225/memory-relocalloc
C proof-of-concept that locates code caves in the .reloc section of mapped DLLs to allocate and execute small shellcode, replacing typical memory…
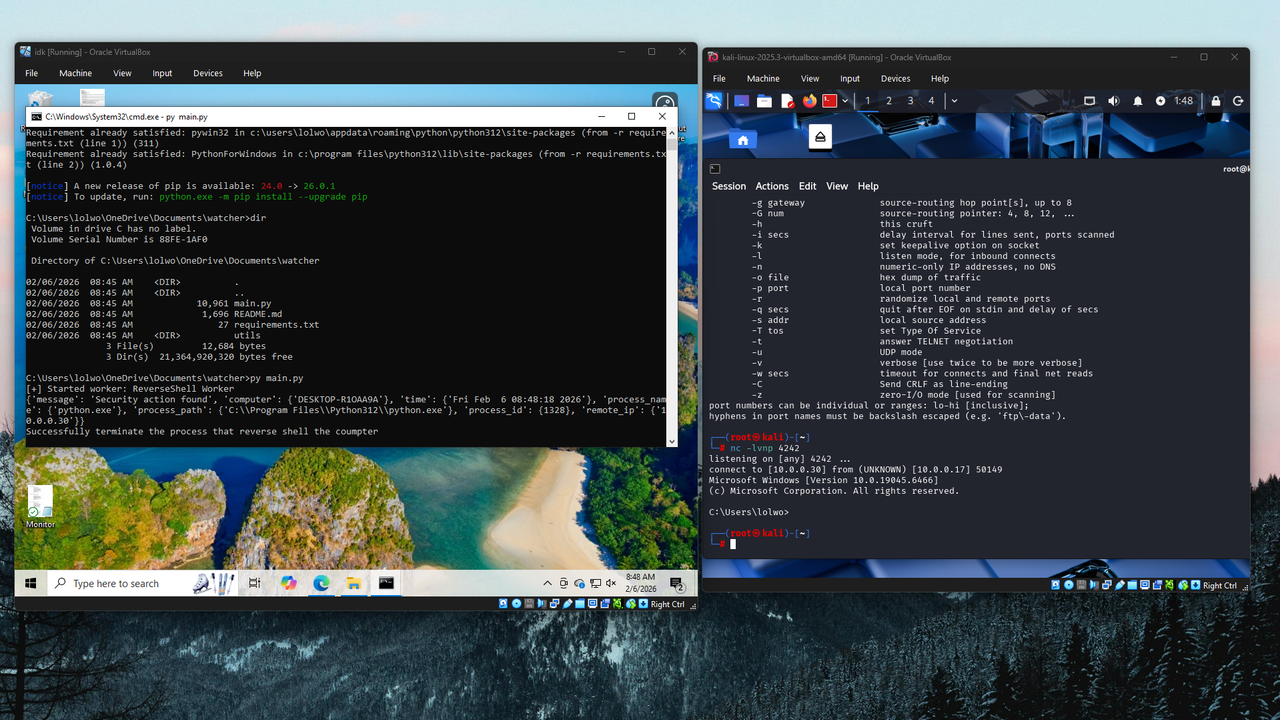 themoonsir/watcher
Detection reverse shell and kill it before trying shell.