Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-87575-CVE-2026-87606-CVE-2026-87491-and-CVE-2026-85046.-Escape-the-v8-carcass. — Chained Chrome V8 renderer escape proof-of-concept exploiting four CVEs: Float64Array corruption, Wasm overwrite, popup navigation retargeting, and activation misattribution. | Kitploit
Tools/GitHubGitHub/sneakynachos/cve-2026-87575-cve-2026-87606-cve-2026-87491-and-cve-2026-85046.-escape-the-v8-carcass.
Vulnerability AnalysisExploitationReverse EngineeringShellcodeWeb Application ExploitationPapers & ResearchPayload DevelopmentBinary Exploitation
GitHub
sneakynachos/cve-2026-87575-cve-2026-87606-cve-2026-87491-and-cve-2026-85046.-escape-the-v8-carcass.

CVE-2026-87575-CVE-2026-87606-CVE-2026-87491-and-CVE-2026-85046.-Escape-the-v8-carcass.

Chained Chrome V8 renderer escape proof-of-concept exploiting four CVEs: Float64Array corruption, Wasm overwrite, popup navigation retargeting, and activation misattribution.

View Repository
51111 days agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2026-85046 + CVE-2026-87491 + CVE-2026-87606 + CVE-2026-87575

Talk about a giant pain to sneak a path out of the renderer.

550 mg of caffiene and going up and down chrome CVE's all night, you too can bounce out of the renderer.

  • CVE-2026-85046 corrupts a Float64Array for V8-cage read/write.
  • CVE-2026-87491 overwrites compiled Wasm and runs native renderer code.
  • CVE-2026-87606 retargets a navigation to the sandboxed popup.
  • The popup receives one real user click.
  • CVE-2026-87575 misattributes that activation to the navigation.
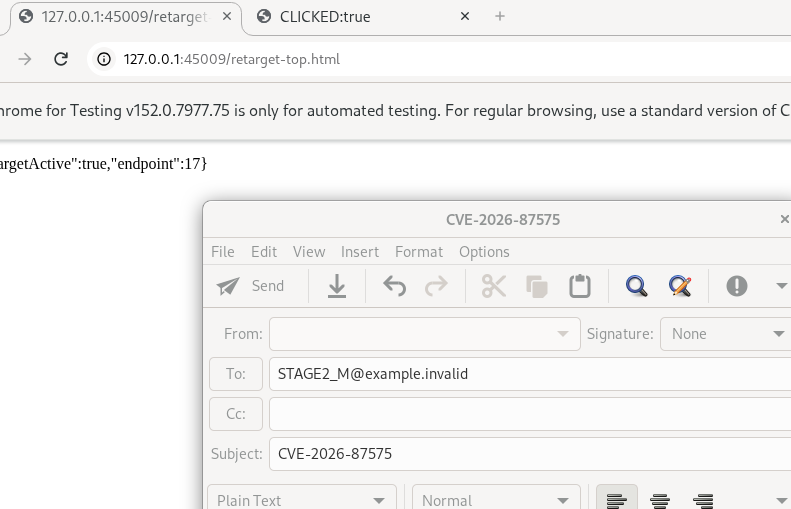
  • Chrome launches the existing Evolution mail handler outside the renderer.

Other notes:

  • V8 has quite a bit of a shaky runtime and likes to move up and down
  • The cage can info disclose itself at times because of the slide (Spectre style side watching via js)
  • The renderer is the renderer once you pop out, standard stare around and look for jumps
  • Just look for misaligned permissions and sort of just roll out depending on target

Chipset:

  • PKU chips can increase the chance of runway and create RWX pages, otherise you'd have to modify the runway
Pasted Graphic 71
root@kitploit:~
python3 run.py vulnerable
python3 run.py fixed --attempts 1
image

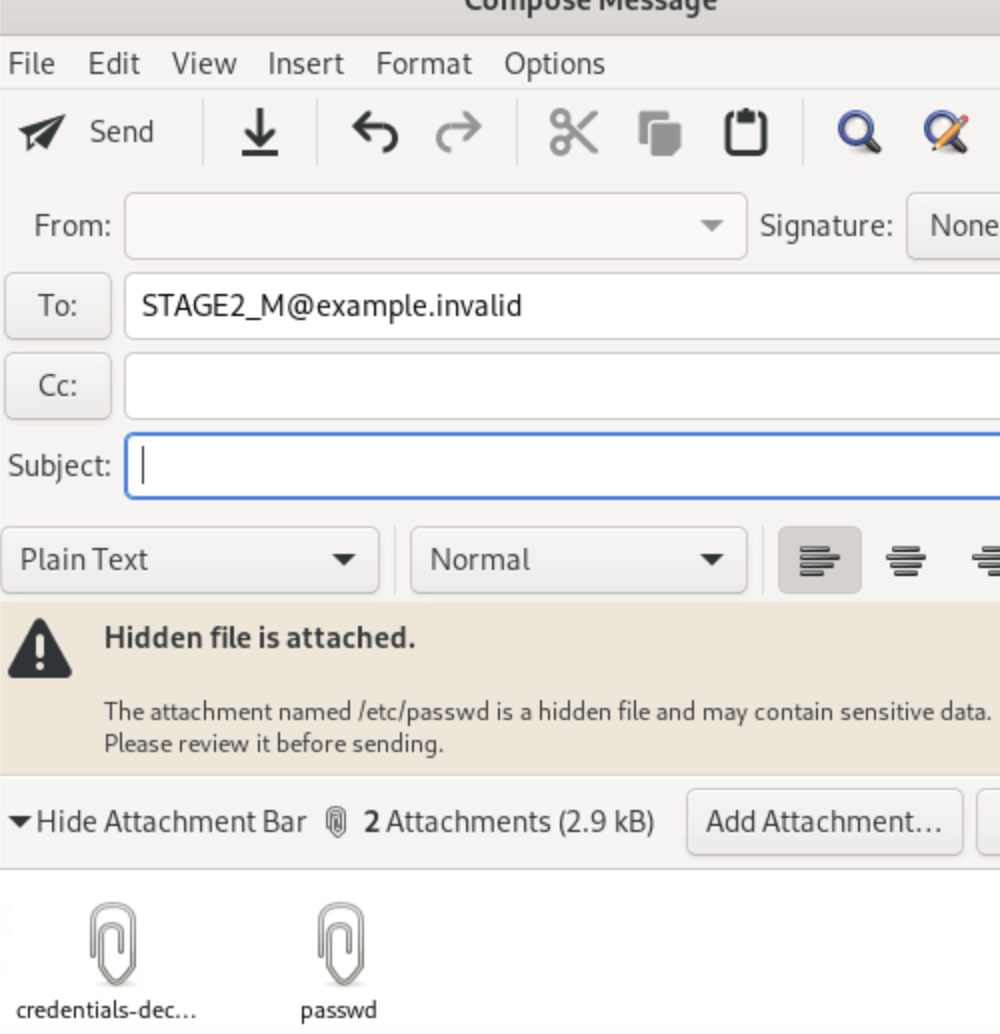
Also there's a 0-day in Evolution and you can just add files to email to yourself

image
Download Tool