metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Interactive Ruby shell for authorized CVE-2025-55182 (react2shell) testing

Automated RCE exploit for WordPress WPCode Lite v2.3.5. Executes 6-step exploitation chain via XML-RPC bypass with 8 built-in PHP payloads, including…

CVE-2024-6387 POC (Currently being edited)

An automated exploit for CVE-2026-0073 (Android ADB TLS Auth Bypass). Features a built-in mDNS/Zeroconf scanner to instantly discover randomized…

An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…

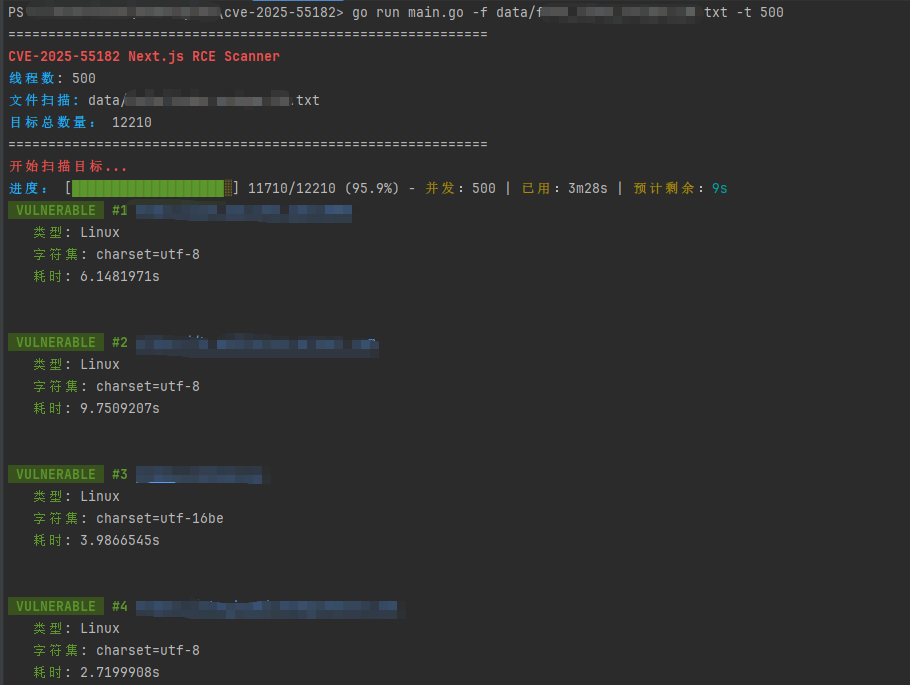
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…

Exploit for CVE-2024-23897 in Jenkins, enabling file read and remote code execution via crafted requests. Includes Docker setup and Groovy scripts…

Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.

Automated exploit tool targeting CVE-2024-52010 for penetration testing and vulnerability validation.

Exploit scripts for CVE-2021-41773 (Apache 2.4.49) enabling path traversal and remote code execution via CGI, including a reverse shell payload.

CVE-2024-10914 Shell Exploit

A simple tool to interact with web shells and command injection vulnerabilities

PoC code for vulnerability in webmod v0.48. Originally written in 2007, assigned CVE-2007-1260.

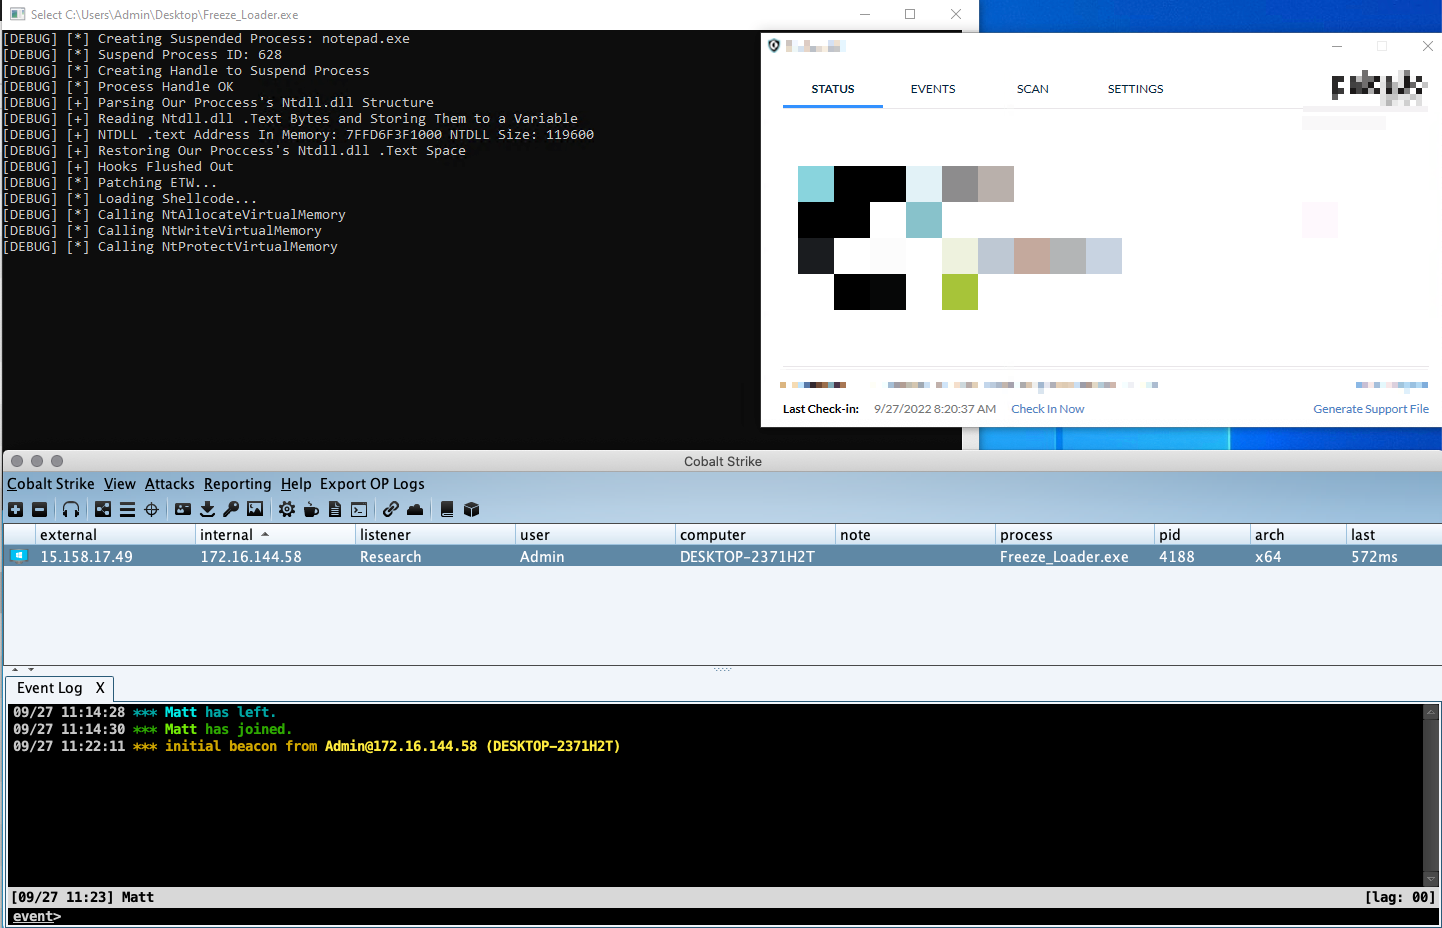
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods

SambaCry (CVE-2017-7494) exploit for Samba | bind shell without Metasploit

OpenSMTPD version 6.6.2 remote code execution exploit

C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.